xian-tech-wallet-cli 0.2.1__py3-none-any.whl
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- xian_tech_wallet_cli-0.2.1.dist-info/METADATA +145 -0
- xian_tech_wallet_cli-0.2.1.dist-info/RECORD +29 -0
- xian_tech_wallet_cli-0.2.1.dist-info/WHEEL +5 -0
- xian_tech_wallet_cli-0.2.1.dist-info/entry_points.txt +2 -0
- xian_tech_wallet_cli-0.2.1.dist-info/licenses/LICENSE +21 -0
- xian_tech_wallet_cli-0.2.1.dist-info/top_level.txt +1 -0
- xian_wallet_cli/__init__.py +0 -0
- xian_wallet_cli/accounts_cli.py +148 -0
- xian_wallet_cli/activity.py +120 -0
- xian_wallet_cli/agent_cli.py +418 -0
- xian_wallet_cli/chain.py +306 -0
- xian_wallet_cli/chain_apps.py +291 -0
- xian_wallet_cli/cli.py +424 -0
- xian_wallet_cli/dashboard.py +213 -0
- xian_wallet_cli/domain.py +259 -0
- xian_wallet_cli/files.py +63 -0
- xian_wallet_cli/payments.py +278 -0
- xian_wallet_cli/permissions.py +173 -0
- xian_wallet_cli/presentation.py +203 -0
- xian_wallet_cli/profiles.py +157 -0
- xian_wallet_cli/shielded.py +329 -0
- xian_wallet_cli/state.py +84 -0
- xian_wallet_cli/telegram.py +121 -0
- xian_wallet_cli/vault.py +115 -0
- xian_wallet_cli/walletconnect/bridge.mjs +199 -0
- xian_wallet_cli/walletconnect/package-lock.json +1044 -0
- xian_wallet_cli/walletconnect/package.json +10 -0
- xian_wallet_cli/walletconnect/policy.mjs +37 -0
- xian_wallet_cli/walletconnect_cli.py +106 -0
|
@@ -0,0 +1,145 @@
|
|
|
1
|
+
Metadata-Version: 2.4
|
|
2
|
+
Name: xian-tech-wallet-cli
|
|
3
|
+
Version: 0.2.1
|
|
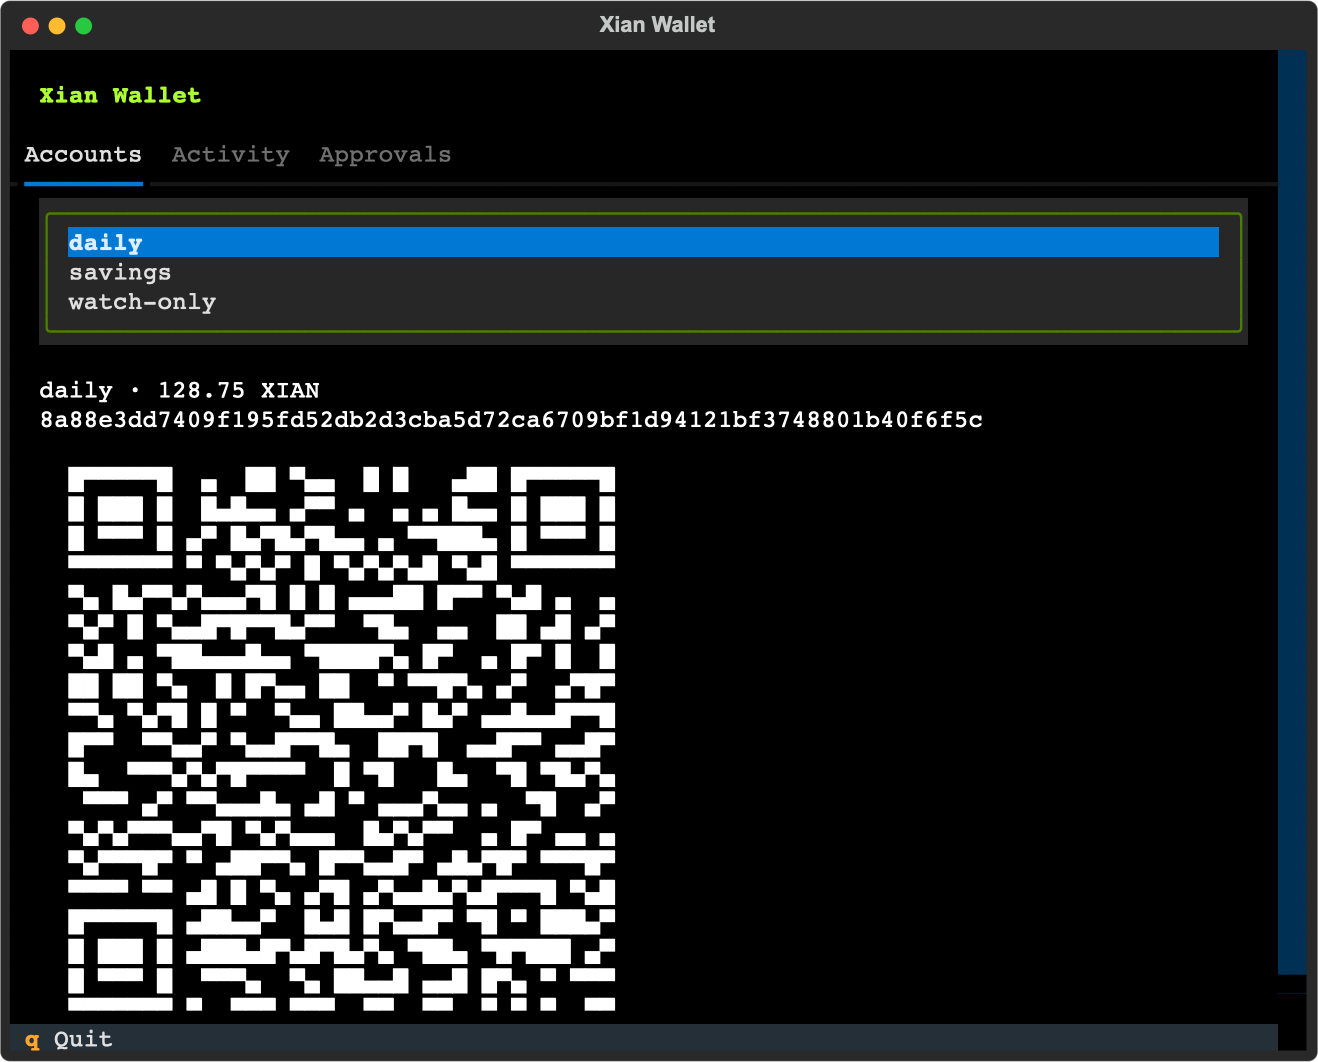
4
|
+
Summary: Xian wallet for terminals and agents
|
|
5
|
+
License-Expression: MIT
|
|
6
|
+
Project-URL: Homepage, https://github.com/xian-technology/xian-wallet-cli
|
|
7
|
+
Project-URL: Documentation, https://docs.xian.technology/tools/xian-wallet-cli
|
|
8
|
+
Project-URL: Issues, https://github.com/xian-technology/xian-wallet-cli/issues
|
|
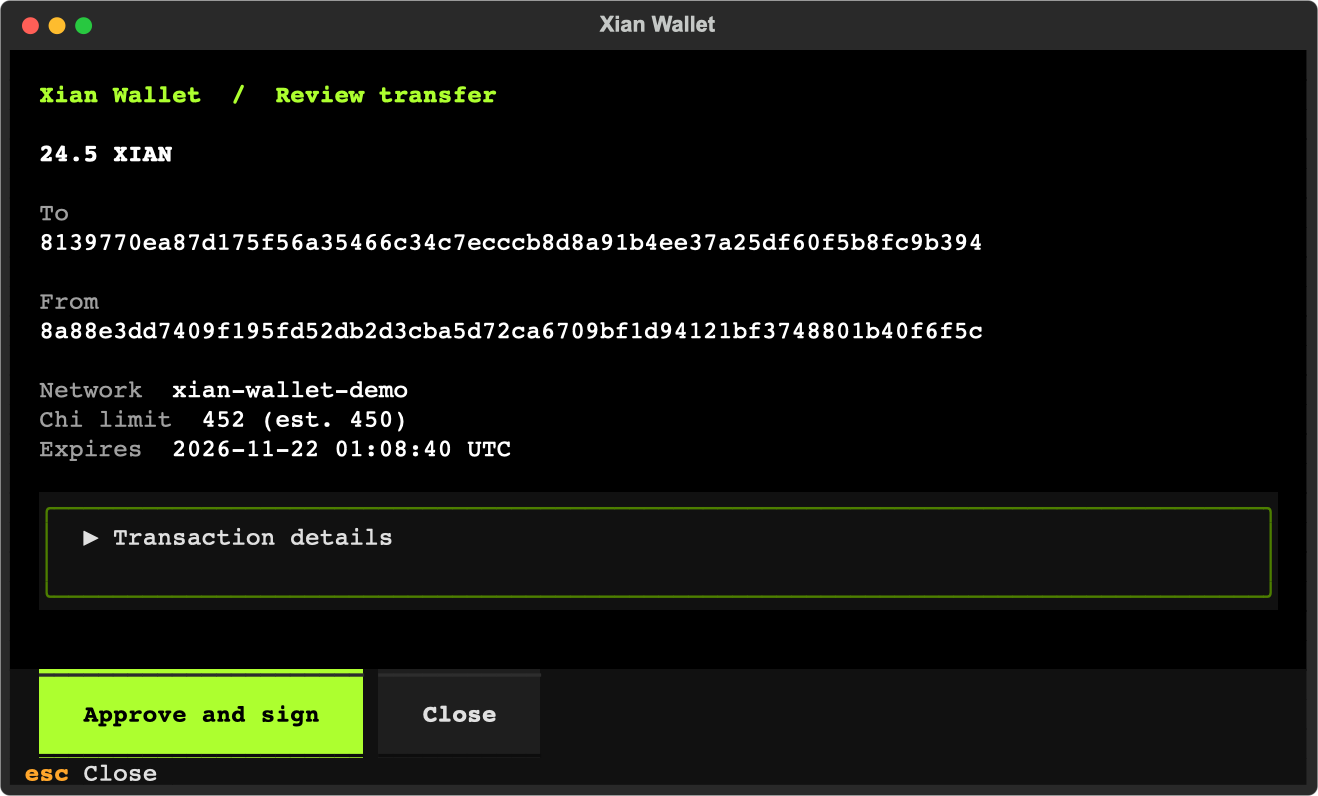
9
|
+
Requires-Python: <3.15,>=3.14
|
|
10
|
+
Description-Content-Type: text/markdown
|
|
11
|
+
License-File: LICENSE
|
|
12
|
+
Requires-Dist: aiohttp<4,>=3.13.5
|
|
13
|
+
Requires-Dist: pydantic<3,>=2.12
|
|
14
|
+
Requires-Dist: pynacl<2,>=1.6
|
|
15
|
+
Requires-Dist: qrcode<9,>=8
|
|
16
|
+
Requires-Dist: rich<16,>=14
|
|
17
|
+
Requires-Dist: textual<9,>=6
|
|
18
|
+
Requires-Dist: typer<1,>=0.26
|
|
19
|
+
Requires-Dist: xian-tech-py[hd]<0.6,>=0.5.3
|
|
20
|
+
Requires-Dist: xian-tech-runtime-types<0.2,>=0.1.6
|
|
21
|
+
Requires-Dist: yarl<2,>=1.20
|
|
22
|
+
Provides-Extra: shielded
|
|
23
|
+
Requires-Dist: xian-tech-zk<0.3,>=0.2.1; extra == "shielded"
|
|
24
|
+
Dynamic: license-file
|
|
25
|
+
|
|
26
|
+
# Xian Wallet CLI
|
|
27
|
+
|
|
28
|
+
`xian-wallet` is a terminal wallet for Xian. It combines named accounts,
|
|
29
|
+
encrypted recovery backups, portfolio and activity views, and transaction
|
|
30
|
+
approval for people and agents. The CLI, Textual interface, and signer service
|
|
31
|
+
use the same Xian SDK transaction format.
|
|
32
|
+
|
|
33
|
+
## Install
|
|
34
|
+
|
|
35
|
+
Use Python 3.14 and uv on macOS or Linux.
|
|
36
|
+
|
|
37
|
+
```sh
|
|
38
|
+
uv tool install xian-tech-wallet-cli
|
|
39
|
+
xian-wallet --help
|
|
40
|
+
```
|
|
41
|
+
|
|
42
|
+
For shielded notes, install with `uv tool install 'xian-tech-wallet-cli[shielded]'`.
|
|
43
|
+
If uv reports that its executable directory is outside `PATH`, run
|
|
44
|
+
`uv tool update-shell` and open a fresh terminal.
|
|
45
|
+
|
|
46
|
+
Control the state directory with `--home` or `XIAN_WALLET_HOME`. It defaults
|
|
47
|
+
to `$XDG_STATE_HOME/xian-wallet` or `~/.local/state/xian-wallet`.
|
|
48
|
+
|
|
49
|
+
## Accounts and networks
|
|
50
|
+
|
|
51
|
+
```sh
|
|
52
|
+
xian-wallet account create primary
|
|
53
|
+
xian-wallet account backup primary --out primary.backup.json
|
|
54
|
+
xian-wallet receive primary --qr
|
|
55
|
+
xian-wallet ui
|
|
56
|
+
```
|
|
57
|
+
|
|
58
|
+
|
|
59
|
+
|
|
60
|
+
Use `account restore NAME --mnemonic-file FILE --index INDEX` for the same
|
|
61
|
+
mnemonic-derived address as the browser and mobile wallets. Use
|
|
62
|
+
`account import-key NAME --key-file FILE` for a previously generated raw
|
|
63
|
+
Ed25519 key, `account derive SOURCE NAME --index INDEX` for another account
|
|
64
|
+
from the same recovery phrase, and `account watch NAME ADDRESS` for a public
|
|
65
|
+
address. `account restore-backup FILE` verifies an encrypted CLI backup before
|
|
66
|
+
restoring it. `account export-recovery NAME --out FILE` writes the mnemonic
|
|
67
|
+
to an owner-only file for offline storage.
|
|
68
|
+
|
|
69
|
+
The vault unlocks only for each sensitive operation and prompts for its
|
|
70
|
+
password locally. Trusted signer processes can use `--password-file` for
|
|
71
|
+
an explicitly provisioned owner-only file. Use a separate OS identity or
|
|
72
|
+
host for a signer that serves agents.
|
|
73
|
+
|
|
74
|
+
The default RPC is `http://127.0.0.1:26657`. For a saved network, obtain the
|
|
75
|
+
chain ID and first-block hash from a trusted source. Add it with
|
|
76
|
+
`network add NAME URL --chain-id ID --first-block-hash HASH`, then select it
|
|
77
|
+
with `network use NAME` or the global `--network NAME` option. Named profiles
|
|
78
|
+
allow explicit HTTPS RPCs. The node must be synced and serve block 1.
|
|
79
|
+
|
|
80
|
+
## Review and send
|
|
81
|
+
|
|
82
|
+
```sh
|
|
83
|
+
xian-wallet contact add recipient "$RECIPIENT_ADDRESS"
|
|
84
|
+
xian-wallet prepare --from primary --to recipient --amount 1.25 --out proposal.json
|
|
85
|
+
xian-wallet approve proposal.json --account primary --out approval.json --textual
|
|
86
|
+
xian-wallet submit proposal.json --approval approval.json
|
|
87
|
+
```
|
|
88
|
+
|
|
89
|
+
|
|
90
|
+
|
|
91
|
+
Use `--token CONTRACT` for a fungible token. `token watch NAME CONTRACT`
|
|
92
|
+
adds a token to `portfolio ACCOUNT`. `activity` reads the local approval and
|
|
93
|
+
receipt journal. `incoming ACCOUNT --token CONTRACT` scans a page of
|
|
94
|
+
BDS-indexed transfers. Use the returned `next_offset` to keep scanning if a
|
|
95
|
+
page lacks matches.
|
|
96
|
+
|
|
97
|
+
Use `call CONTRACT FUNCTION --args ARGS.json` for read-only simulation.
|
|
98
|
+
Use `prepare-call` to prepare a typed write. Generic fractional values use
|
|
99
|
+
`{"__fixed__":"1.25"}`. The simulator and signing flow share the exact
|
|
100
|
+
payload. `dex`, `nft`, `message`, `x402`, `shielded`, and `walletconnect`
|
|
101
|
+
provide the product-specific workflows in the [wallet guide](https://github.com/xian-technology/xian-wallet-cli/blob/main/docs/WALLET.md).
|
|
102
|
+
|
|
103
|
+
## Agent approvals
|
|
104
|
+
|
|
105
|
+
The agent prepares a proposal and submits it to the trusted signer with
|
|
106
|
+
`agent request`. The owner reviews it using the Textual inbox or a configured
|
|
107
|
+
Telegram bot. The agent then uses `agent fetch` to obtain the signed approval
|
|
108
|
+
and submits it with `submit`. Use `grant` to opt into autonomous, revocable
|
|
109
|
+
transfers within an account, network, asset, recipient, amount, chi budget,
|
|
110
|
+
and expiry. The agent needs the signer socket or an SSH socket forward and
|
|
111
|
+
the relevant bearer credential. [Signer setup and examples](https://github.com/xian-technology/xian-wallet-cli/blob/main/docs/WALLET.md#agent-approvals)
|
|
112
|
+
|
|
113
|
+
Put `--json` before the command for one `xian-wallet-cli/v1` result on stdout.
|
|
114
|
+
Amounts are decimal strings. Normal usage errors go to stderr.
|
|
115
|
+
|
|
116
|
+
| Exit | Meaning |
|
|
117
|
+
| --- | --- |
|
|
118
|
+
| 0 | Command succeeded, or transfer committed successfully |
|
|
119
|
+
| 1 | Admission rejection, failed execution, or failed verification |
|
|
120
|
+
| 2 | Command, input, approval, file, or RPC error |
|
|
121
|
+
| 3 | Final outcome is pending or unknown |
|
|
122
|
+
|
|
123
|
+
After interruption, use `receipt TX_HASH` or retry the same proposal and
|
|
124
|
+
approval. The wallet only signs competing same-nonce proposals through an
|
|
125
|
+
explicit owner replacement. Keep the original hash available until one of
|
|
126
|
+
the competing transactions is finalized.
|
|
127
|
+
|
|
128
|
+
## Validation
|
|
129
|
+
|
|
130
|
+
From a source checkout, use `uv run xian-wallet --help` to run the CLI.
|
|
131
|
+
|
|
132
|
+
```sh
|
|
133
|
+
uv run --extra shielded ruff check
|
|
134
|
+
uv run --extra shielded ruff format --check
|
|
135
|
+
uv run --extra shielded pytest
|
|
136
|
+
node --test tests/walletconnect.test.mjs
|
|
137
|
+
```
|
|
138
|
+
|
|
139
|
+
## Related Docs
|
|
140
|
+
|
|
141
|
+
- [Wallet guide](https://github.com/xian-technology/xian-wallet-cli/blob/main/docs/WALLET.md)
|
|
142
|
+
- [Architecture](https://github.com/xian-technology/xian-wallet-cli/blob/main/docs/ARCHITECTURE.md)
|
|
143
|
+
- [Backlog](https://github.com/xian-technology/xian-wallet-cli/blob/main/docs/BACKLOG.md)
|
|
144
|
+
- [Xian Python SDK](https://github.com/xian-technology/xian-py)
|
|
145
|
+
- [Agent wallet skill](https://github.com/xian-technology/xian-ai-skills/blob/main/xian-wallet-cli-skill/SKILL.md)
|
|
@@ -0,0 +1,29 @@
|
|
|
1
|
+
xian_tech_wallet_cli-0.2.1.dist-info/licenses/LICENSE,sha256=ycJzcyO5tlkhVb1zK81VNraUqPctocDvv2dxHl91KBA,1072
|
|
2
|
+
xian_wallet_cli/__init__.py,sha256=47DEQpj8HBSa-_TImW-5JCeuQeRkm5NMpJWZG3hSuFU,0
|
|
3
|
+
xian_wallet_cli/accounts_cli.py,sha256=0rApMpp8xp-dd3vIyRqdaUHj_Waty8v1GVBXp_kobbk,5549
|
|
4
|
+
xian_wallet_cli/activity.py,sha256=AjjUbPU4K0QxVVzEN0hgE8XzGIdmeQgT12dEHAIF5TI,4285
|
|
5
|
+
xian_wallet_cli/agent_cli.py,sha256=K43QCfMDmqKIgZsPEwBWUaZ0MHjWmrLSm0el8whYRGY,15599
|
|
6
|
+
xian_wallet_cli/chain.py,sha256=N2fgcw4XRP7Pt8QU_oIeqqZfVXCnk-d4xDit1s0iUbs,11750
|
|
7
|
+
xian_wallet_cli/chain_apps.py,sha256=QnwYVjrGPN7djh2nFxVa1MR-3sK_oix7MekCxAFyj6o,9918
|
|
8
|
+
xian_wallet_cli/cli.py,sha256=A4Qy8o8JtTyLYS2WewHM4nwzZS4GEb3lzkkUDtp5gfc,15458
|
|
9
|
+
xian_wallet_cli/dashboard.py,sha256=Xq1ORvoW8UOyGrnw3oUTOgxhzIThQl440JZiLvMepqo,8549
|
|
10
|
+
xian_wallet_cli/domain.py,sha256=76Z_URjKvljf3fxE9hUW5eXL9Ac7EjWOFLPWtwkI-kw,8518
|
|
11
|
+
xian_wallet_cli/files.py,sha256=apQ_9pij7m5UGodht0qUks1APvkaNwBiGOqoaAwnz8Q,2235
|
|
12
|
+
xian_wallet_cli/payments.py,sha256=76_vNfk5SWWUJMOhEyEirLWvzZRp-QvrBfv5_rVVzbI,10609
|
|
13
|
+
xian_wallet_cli/permissions.py,sha256=huarBmwlWSiLP6XryOk7ZfB-j1gE5fB0222EUXW45S0,6365
|
|
14
|
+
xian_wallet_cli/presentation.py,sha256=J-lnc1bRlXoWeV1hdH3gQjcsNzukGvDeAo2uqheEgpY,7498
|
|
15
|
+
xian_wallet_cli/profiles.py,sha256=Mb4isfbsjK6fN4KYuqfzplPQ9ZnXKK3mKByrLwYtH8c,4936
|
|
16
|
+
xian_wallet_cli/shielded.py,sha256=2rF7rDr9VCpgeGhKBZK-iEiHvapFEER-ZnxoeHkqKyQ,12259
|
|
17
|
+
xian_wallet_cli/state.py,sha256=VJswNYPbSwbOzWGfshjNKO6UQpoZQXLY_mAB0qLUbF8,3348
|
|
18
|
+
xian_wallet_cli/telegram.py,sha256=E-LYCwL6iNN1zZTjRgIC1A6eakCx434Onkduvrds0us,4686
|
|
19
|
+
xian_wallet_cli/vault.py,sha256=0SOQ9xFuZKCrgd8dtZl3IZTdm54KmUE3Nk6kh4pCw78,4266
|
|
20
|
+
xian_wallet_cli/walletconnect_cli.py,sha256=Tjs1tf-DHEIf6_52bWaStwJGyXBbFEogLmuqyhm-lFs,4013
|
|
21
|
+
xian_wallet_cli/walletconnect/bridge.mjs,sha256=CABKoAgnJoOFOyzKwHN37Z5gZBbfskJlSGgycGa6-7Y,8282
|
|
22
|
+
xian_wallet_cli/walletconnect/package-lock.json,sha256=MkECtciItoo8rwsAGicI-m6jagf9N_m_Rbk7L-POeeM,39372
|
|
23
|
+
xian_wallet_cli/walletconnect/package.json,sha256=Idce5QYKKrQwJeJaIraCpiIZh3tmS1irrc0oXOB06zY,212
|
|
24
|
+
xian_wallet_cli/walletconnect/policy.mjs,sha256=bLVbEYc9uly-u8T5DXlASma1uJzavQQMd7HEOD4WKhA,1812
|
|
25
|
+
xian_tech_wallet_cli-0.2.1.dist-info/METADATA,sha256=EuXP5qk2jUjY5y7fYf3kvdy95bF38bog4h20fHid4WQ,6520
|
|
26
|
+
xian_tech_wallet_cli-0.2.1.dist-info/WHEEL,sha256=mOdXR9C3wMVov7cSY8PY-XCzo3SmmWCHvGQr5csJoao,91
|
|
27
|
+
xian_tech_wallet_cli-0.2.1.dist-info/entry_points.txt,sha256=E5p0zxjMawzSFN31ZuwltaBX2b04UdUU1vN7uUonJLg,56
|
|
28
|
+
xian_tech_wallet_cli-0.2.1.dist-info/top_level.txt,sha256=JHt4cTz1nItrF1LPkfjxVDZsRFKNMkEHUQgCQbO36pQ,16
|
|
29
|
+
xian_tech_wallet_cli-0.2.1.dist-info/RECORD,,
|
|
@@ -0,0 +1,21 @@
|
|
|
1
|
+
MIT License
|
|
2
|
+
|
|
3
|
+
Copyright (c) 2026 Xian Technology
|
|
4
|
+
|
|
5
|
+
Permission is hereby granted, free of charge, to any person obtaining a copy
|
|
6
|
+
of this software and associated documentation files (the "Software"), to deal
|
|
7
|
+
in the Software without restriction, including without limitation the rights
|
|
8
|
+
to use, copy, modify, merge, publish, distribute, sublicense, and/or sell
|
|
9
|
+
copies of the Software, and to permit persons to whom the Software is
|
|
10
|
+
furnished to do so, subject to the following conditions:
|
|
11
|
+
|
|
12
|
+
The above copyright notice and this permission notice shall be included in all
|
|
13
|
+
copies or substantial portions of the Software.
|
|
14
|
+
|
|
15
|
+
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR
|
|
16
|
+
IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY,
|
|
17
|
+
FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE
|
|
18
|
+
AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER
|
|
19
|
+
LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM,
|
|
20
|
+
OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE
|
|
21
|
+
SOFTWARE.
|
|
@@ -0,0 +1 @@
|
|
|
1
|
+
xian_wallet_cli
|
|
File without changes
|
|
@@ -0,0 +1,148 @@
|
|
|
1
|
+
"""Account management and the receive workflow."""
|
|
2
|
+
|
|
3
|
+
import io
|
|
4
|
+
import sys
|
|
5
|
+
from pathlib import Path
|
|
6
|
+
from typing import Annotated
|
|
7
|
+
|
|
8
|
+
import qrcode
|
|
9
|
+
import typer
|
|
10
|
+
from rich.console import Console
|
|
11
|
+
|
|
12
|
+
from .domain import WalletError
|
|
13
|
+
from .files import load_document, write_new
|
|
14
|
+
from .vault import Account, AccountBackup, new_mnemonic, seal_account, secret_file
|
|
15
|
+
|
|
16
|
+
accounts = typer.Typer(no_args_is_help=True, help="Create, restore, back up or watch accounts.")
|
|
17
|
+
PasswordFile = Annotated[Path | None, typer.Option(help="Owner-only password file for the signer.")]
|
|
18
|
+
Index = Annotated[int, typer.Option(min=0, max=2**32 - 1)]
|
|
19
|
+
|
|
20
|
+
|
|
21
|
+
def password_for(ctx: typer.Context, path: Path | None, *, confirm: bool = False) -> str:
|
|
22
|
+
if path is not None:
|
|
23
|
+
return secret_file(path, "password")
|
|
24
|
+
if ctx.obj.as_json or not (sys.stdin.isatty() and sys.stderr.isatty()):
|
|
25
|
+
raise WalletError("password_required", "Use an owner-only password file in headless mode.")
|
|
26
|
+
return typer.prompt("Vault password", hide_input=True, confirmation_prompt=confirm, err=True)
|
|
27
|
+
|
|
28
|
+
|
|
29
|
+
def save_account(ctx: typer.Context, backup: AccountBackup) -> None:
|
|
30
|
+
ctx.obj.store.add("account", backup.account.name, backup)
|
|
31
|
+
ctx.obj.emit(backup.account.model_dump())
|
|
32
|
+
|
|
33
|
+
|
|
34
|
+
@accounts.command()
|
|
35
|
+
def create(ctx: typer.Context, name: str, password_file: PasswordFile = None) -> None:
|
|
36
|
+
"""Create an encrypted mnemonic account."""
|
|
37
|
+
password = password_for(ctx, password_file, confirm=True)
|
|
38
|
+
save_account(ctx, seal_account(name, "mnemonic", new_mnemonic(), password, index=0))
|
|
39
|
+
|
|
40
|
+
|
|
41
|
+
@accounts.command()
|
|
42
|
+
def restore(
|
|
43
|
+
ctx: typer.Context,
|
|
44
|
+
name: str,
|
|
45
|
+
mnemonic_file: Annotated[Path, typer.Option(help="Owner-only BIP39 recovery phrase file.")],
|
|
46
|
+
password_file: PasswordFile = None,
|
|
47
|
+
index: Index = 0,
|
|
48
|
+
) -> None:
|
|
49
|
+
"""Restore the same indexed address as the browser and mobile wallets."""
|
|
50
|
+
password = password_for(ctx, password_file, confirm=True)
|
|
51
|
+
phrase = secret_file(mnemonic_file, "recovery phrase")
|
|
52
|
+
save_account(
|
|
53
|
+
ctx, seal_account(name, "mnemonic", " ".join(phrase.split()), password, index=index)
|
|
54
|
+
)
|
|
55
|
+
|
|
56
|
+
|
|
57
|
+
@accounts.command("import-key")
|
|
58
|
+
def import_key(
|
|
59
|
+
ctx: typer.Context,
|
|
60
|
+
name: str,
|
|
61
|
+
key_file: Annotated[Path, typer.Option()],
|
|
62
|
+
password_file: PasswordFile = None,
|
|
63
|
+
) -> None:
|
|
64
|
+
"""Move an existing Ed25519 key into the encrypted vault."""
|
|
65
|
+
password = password_for(ctx, password_file, confirm=True)
|
|
66
|
+
save_account(
|
|
67
|
+
ctx,
|
|
68
|
+
seal_account(name, "private_key", secret_file(key_file, "private-key").strip(), password),
|
|
69
|
+
)
|
|
70
|
+
|
|
71
|
+
|
|
72
|
+
@accounts.command()
|
|
73
|
+
def derive(
|
|
74
|
+
ctx: typer.Context,
|
|
75
|
+
source: str,
|
|
76
|
+
name: str,
|
|
77
|
+
index: Annotated[int, typer.Option(min=0, max=2**32 - 1)],
|
|
78
|
+
password_file: PasswordFile = None,
|
|
79
|
+
) -> None:
|
|
80
|
+
"""Add another account from the same recovery phrase."""
|
|
81
|
+
original = ctx.obj.store.read("account", source, AccountBackup)
|
|
82
|
+
if original.account.kind != "mnemonic":
|
|
83
|
+
raise WalletError("mnemonic_required", "Choose an account backed by a recovery phrase.")
|
|
84
|
+
password = password_for(ctx, password_file)
|
|
85
|
+
save_account(
|
|
86
|
+
ctx, seal_account(name, "mnemonic", original.secret_text(password), password, index=index)
|
|
87
|
+
)
|
|
88
|
+
|
|
89
|
+
|
|
90
|
+
@accounts.command()
|
|
91
|
+
def watch(ctx: typer.Context, name: str, address: str) -> None:
|
|
92
|
+
"""Add a public address without a signing key."""
|
|
93
|
+
save_account(
|
|
94
|
+
ctx, AccountBackup(account=Account(name=name, address=address.lower(), kind="watch"))
|
|
95
|
+
)
|
|
96
|
+
|
|
97
|
+
|
|
98
|
+
@accounts.command("list")
|
|
99
|
+
def list_accounts(ctx: typer.Context) -> None:
|
|
100
|
+
"""List local account names and public addresses."""
|
|
101
|
+
rows = ctx.obj.store.entries("account", AccountBackup)
|
|
102
|
+
ctx.obj.emit({"accounts": [entry.account.model_dump() for entry in rows]})
|
|
103
|
+
|
|
104
|
+
|
|
105
|
+
@accounts.command()
|
|
106
|
+
def backup(ctx: typer.Context, name: str, out: Annotated[Path, typer.Option()]) -> None:
|
|
107
|
+
"""Write an encrypted account backup."""
|
|
108
|
+
entry = ctx.obj.store.read("account", name, AccountBackup)
|
|
109
|
+
write_new(out, entry.model_dump_json(indent=2) + "\n")
|
|
110
|
+
ctx.obj.emit({"account": name, "backup_file": str(out)})
|
|
111
|
+
|
|
112
|
+
|
|
113
|
+
@accounts.command()
|
|
114
|
+
def restore_backup(
|
|
115
|
+
ctx: typer.Context, backup_file: Path, password_file: PasswordFile = None
|
|
116
|
+
) -> None:
|
|
117
|
+
"""Verify and restore a previously encrypted CLI backup."""
|
|
118
|
+
entry = load_document(backup_file, AccountBackup)
|
|
119
|
+
if entry.account.kind != "watch":
|
|
120
|
+
entry.unlock(password_for(ctx, password_file))
|
|
121
|
+
save_account(ctx, entry)
|
|
122
|
+
|
|
123
|
+
|
|
124
|
+
@accounts.command()
|
|
125
|
+
def export_recovery(
|
|
126
|
+
ctx: typer.Context,
|
|
127
|
+
name: str,
|
|
128
|
+
out: Annotated[Path, typer.Option()],
|
|
129
|
+
password_file: PasswordFile = None,
|
|
130
|
+
) -> None:
|
|
131
|
+
"""Write the mnemonic to an owner-only file for offline recovery."""
|
|
132
|
+
entry = ctx.obj.store.read("account", name, AccountBackup)
|
|
133
|
+
if entry.account.kind != "mnemonic":
|
|
134
|
+
raise WalletError("mnemonic_required", "Choose an account backed by a recovery phrase.")
|
|
135
|
+
write_new(out, entry.secret_text(password_for(ctx, password_file)) + "\n")
|
|
136
|
+
ctx.obj.emit({"account": name, "recovery_file": str(out)})
|
|
137
|
+
|
|
138
|
+
|
|
139
|
+
def receive(ctx: typer.Context, name: str, qr: bool = False) -> None:
|
|
140
|
+
"""Show a public account address and optionally render its QR code."""
|
|
141
|
+
entry = ctx.obj.store.read("account", name, AccountBackup)
|
|
142
|
+
ctx.obj.emit(entry.account.model_dump())
|
|
143
|
+
if qr and not ctx.obj.as_json:
|
|
144
|
+
graphic = qrcode.QRCode(border=2)
|
|
145
|
+
graphic.add_data(entry.account.address)
|
|
146
|
+
output = io.StringIO()
|
|
147
|
+
graphic.print_ascii(out=output, tty=False)
|
|
148
|
+
Console().print(output.getvalue(), markup=False, highlight=False)
|
|
@@ -0,0 +1,120 @@
|
|
|
1
|
+
"""Persistent signing reservations and outgoing transaction receipts."""
|
|
2
|
+
|
|
3
|
+
import sqlite3
|
|
4
|
+
from typing import Literal
|
|
5
|
+
|
|
6
|
+
from .chain import Finality, now
|
|
7
|
+
from .domain import Address, Approval, Digest, Document, Network, Proposal, WalletError, sign_plan
|
|
8
|
+
from .state import Store
|
|
9
|
+
|
|
10
|
+
|
|
11
|
+
class Activity(Document):
|
|
12
|
+
network: Network
|
|
13
|
+
tx_hash: Digest
|
|
14
|
+
proposal_id: Digest
|
|
15
|
+
sender: Address
|
|
16
|
+
contract: str
|
|
17
|
+
function: str
|
|
18
|
+
timestamp: int
|
|
19
|
+
status: Literal["approved", "completed", "failed", "pending", "rejected"] = "approved"
|
|
20
|
+
height: int | None = None
|
|
21
|
+
chi_used: int | None = None
|
|
22
|
+
|
|
23
|
+
|
|
24
|
+
def activity_key(network: Network, tx_hash: str) -> str:
|
|
25
|
+
return f"{network.chain_id}/{network.first_block_hash}/{tx_hash}"
|
|
26
|
+
|
|
27
|
+
|
|
28
|
+
def nonce_key(plan: Proposal) -> str:
|
|
29
|
+
return activity_key(plan.network, f"{plan.sender}/{plan.nonce}")
|
|
30
|
+
|
|
31
|
+
|
|
32
|
+
def sign_once(
|
|
33
|
+
db: sqlite3.Connection, plan: Proposal, wallet, *, replaces: str | None = None
|
|
34
|
+
) -> Approval:
|
|
35
|
+
if wallet.public_key != plan.sender:
|
|
36
|
+
raise WalletError("wrong_signer", "The signing key does not match the sender.")
|
|
37
|
+
row = db.execute(
|
|
38
|
+
"SELECT data FROM records WHERE namespace='signed-nonce' AND name=?", (nonce_key(plan),)
|
|
39
|
+
).fetchone()
|
|
40
|
+
prior = Approval.model_validate_json(row[0]) if row else None
|
|
41
|
+
if prior and prior.proposal_id == plan.proposal_id:
|
|
42
|
+
plan.require_unexpired(now())
|
|
43
|
+
return prior
|
|
44
|
+
if prior and replaces is None:
|
|
45
|
+
raise WalletError(
|
|
46
|
+
"nonce_already_signed", "This account already signed another proposal for that nonce."
|
|
47
|
+
)
|
|
48
|
+
if replaces is not None and (prior is None or prior.tx_hash != replaces):
|
|
49
|
+
raise WalletError(
|
|
50
|
+
"replacement_mismatch", "The nonce is not reserved by the specified hash."
|
|
51
|
+
)
|
|
52
|
+
signed = sign_plan(plan, wallet, now())
|
|
53
|
+
db.execute(
|
|
54
|
+
"INSERT OR REPLACE INTO records VALUES ('signed-nonce', ?, ?)",
|
|
55
|
+
(nonce_key(plan), signed.model_dump_json()),
|
|
56
|
+
)
|
|
57
|
+
return signed
|
|
58
|
+
|
|
59
|
+
|
|
60
|
+
def reserve_signing(
|
|
61
|
+
store: Store, plan: Proposal, wallet, *, replaces: str | None = None
|
|
62
|
+
) -> Approval:
|
|
63
|
+
with store.transaction(write=True) as db:
|
|
64
|
+
return sign_once(db, plan, wallet, replaces=replaces)
|
|
65
|
+
|
|
66
|
+
|
|
67
|
+
class Journal:
|
|
68
|
+
def __init__(self, store: Store):
|
|
69
|
+
self.store = store
|
|
70
|
+
|
|
71
|
+
def record(self, plan: Proposal, approval: Approval) -> None:
|
|
72
|
+
entry = Activity(
|
|
73
|
+
network=plan.network,
|
|
74
|
+
tx_hash=approval.tx_hash,
|
|
75
|
+
proposal_id=plan.proposal_id,
|
|
76
|
+
sender=plan.sender,
|
|
77
|
+
contract=plan.payload["contract"],
|
|
78
|
+
function=plan.payload["function"],
|
|
79
|
+
timestamp=now(),
|
|
80
|
+
)
|
|
81
|
+
with self.store.transaction(write=True) as db:
|
|
82
|
+
db.execute(
|
|
83
|
+
"INSERT OR IGNORE INTO records VALUES ('activity', ?, ?)",
|
|
84
|
+
(activity_key(plan.network, approval.tx_hash), entry.model_dump_json()),
|
|
85
|
+
)
|
|
86
|
+
|
|
87
|
+
def update(self, network: Network, receipt: Finality) -> None:
|
|
88
|
+
key = activity_key(network, receipt.tx_hash)
|
|
89
|
+
with self.store.transaction(write=True) as db:
|
|
90
|
+
row = db.execute(
|
|
91
|
+
"SELECT data FROM records WHERE namespace='activity' AND name=?", (key,)
|
|
92
|
+
).fetchone()
|
|
93
|
+
if row is None:
|
|
94
|
+
return
|
|
95
|
+
previous = Activity.model_validate_json(row[0])
|
|
96
|
+
if previous.status in ("completed", "failed"):
|
|
97
|
+
return
|
|
98
|
+
updated = previous.model_copy(update=receipt.model_dump(exclude={"message"}))
|
|
99
|
+
db.execute(
|
|
100
|
+
"UPDATE records SET data=? WHERE namespace='activity' AND name=?",
|
|
101
|
+
(updated.model_dump_json(), key),
|
|
102
|
+
)
|
|
103
|
+
|
|
104
|
+
|
|
105
|
+
async def refresh_activity(node, store: Store, address: str | None = None) -> None:
|
|
106
|
+
network = await node.identity()
|
|
107
|
+
journal = Journal(store)
|
|
108
|
+
entries = sorted(
|
|
109
|
+
store.entries("activity", Activity), key=lambda item: item.timestamp, reverse=True
|
|
110
|
+
)
|
|
111
|
+
open_entries = [
|
|
112
|
+
row
|
|
113
|
+
for row in entries
|
|
114
|
+
if row.network == network
|
|
115
|
+
and address in (None, row.sender)
|
|
116
|
+
and row.status in ("approved", "pending", "rejected")
|
|
117
|
+
]
|
|
118
|
+
for row in open_entries[:50]:
|
|
119
|
+
if result := await node.lookup(row.tx_hash):
|
|
120
|
+
journal.update(network, result)
|