sovlens 0.3.1__py3-none-any.whl
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- sovlens/__init__.py +1 -0
- sovlens/catalog.py +107 -0
- sovlens/cli.py +97 -0
- sovlens/data/esc_services.json +345 -0
- sovlens/deps.py +171 -0
- sovlens/inventory.py +119 -0
- sovlens/report.py +102 -0
- sovlens/runner.py +54 -0
- sovlens-0.3.1.dist-info/METADATA +132 -0
- sovlens-0.3.1.dist-info/RECORD +14 -0
- sovlens-0.3.1.dist-info/WHEEL +5 -0
- sovlens-0.3.1.dist-info/entry_points.txt +2 -0
- sovlens-0.3.1.dist-info/licenses/LICENSE +179 -0
- sovlens-0.3.1.dist-info/top_level.txt +1 -0
sovlens/__init__.py
ADDED
|
@@ -0,0 +1 @@
|
|
|
1
|
+
__version__ = "0.3.1"
|
sovlens/catalog.py
ADDED
|
@@ -0,0 +1,107 @@
|
|
|
1
|
+
"""Which services exist in the target partition.
|
|
2
|
+
|
|
3
|
+
Sources, in order:
|
|
4
|
+
1. Manual overrides (catalog/overrides.json).
|
|
5
|
+
2. The service list of the AWS European Sovereign Cloud User Guide (catalog/esc_services.json).
|
|
6
|
+
Widely used services that the guide does not cover are reported as "wait".
|
|
7
|
+
3. The endpoint data shipped with botocore. It misses partition-wide services such as IAM,
|
|
8
|
+
Organizations and Route 53, so it is only a fallback.
|
|
9
|
+
Anything else is reported as "verify", never as a hard "no".
|
|
10
|
+
"""
|
|
11
|
+
from __future__ import annotations
|
|
12
|
+
|
|
13
|
+
import json
|
|
14
|
+
from pathlib import Path
|
|
15
|
+
|
|
16
|
+
import botocore
|
|
17
|
+
import botocore.session
|
|
18
|
+
|
|
19
|
+
TARGET_PARTITION = "aws-eusc"
|
|
20
|
+
|
|
21
|
+
# Services that are operated outside a single regional endpoint in the
|
|
22
|
+
# commercial partition. Their presence always deserves a manual look.
|
|
23
|
+
GLOBAL_SERVICES = {"cloudfront", "route53", "globalaccelerator", "shield", "waf"}
|
|
24
|
+
ESC_SERVICES = Path(__file__).resolve().parent / "data" / "esc_services.json"
|
|
25
|
+
|
|
26
|
+
|
|
27
|
+
class Catalog:
|
|
28
|
+
def __init__(self, target_region: str, overrides_path: Path | None = None):
|
|
29
|
+
self.target_region = target_region
|
|
30
|
+
self.botocore_version = botocore.__version__
|
|
31
|
+
self._session = botocore.session.get_session()
|
|
32
|
+
self._available: set[str] = set()
|
|
33
|
+
self._known: set[str] = set()
|
|
34
|
+
self._build()
|
|
35
|
+
guide = json.loads(ESC_SERVICES.read_text())
|
|
36
|
+
self.guide_source, self.guide_checked = guide["source"], guide["checked"]
|
|
37
|
+
self.guide_available = {n for names in guide["services"].values() for n in names}
|
|
38
|
+
self.guide_missing = dict(guide["not_listed"])
|
|
39
|
+
self.guide_notes = dict(guide.get("notes", {}))
|
|
40
|
+
self.override_available: set[str] = set()
|
|
41
|
+
self.override_unavailable: set[str] = set()
|
|
42
|
+
if overrides_path and overrides_path.exists():
|
|
43
|
+
data = json.loads(overrides_path.read_text())
|
|
44
|
+
self.override_available = set(data.get("available", []))
|
|
45
|
+
self.override_unavailable = set(data.get("unavailable", []))
|
|
46
|
+
|
|
47
|
+
def _namespaces(self, service_name: str) -> set[str]:
|
|
48
|
+
"""ARN namespaces a botocore service can appear under."""
|
|
49
|
+
names = {service_name}
|
|
50
|
+
try:
|
|
51
|
+
meta = self._session.get_service_model(service_name).metadata
|
|
52
|
+
except Exception:
|
|
53
|
+
return names
|
|
54
|
+
for key in ("signingName", "endpointPrefix"):
|
|
55
|
+
if meta.get(key):
|
|
56
|
+
names.add(meta[key])
|
|
57
|
+
return names
|
|
58
|
+
|
|
59
|
+
def _build(self) -> None:
|
|
60
|
+
for svc in self._session.get_available_services():
|
|
61
|
+
names = self._namespaces(svc)
|
|
62
|
+
self._known |= names
|
|
63
|
+
regions = self._session.get_available_regions(
|
|
64
|
+
svc, partition_name=TARGET_PARTITION
|
|
65
|
+
)
|
|
66
|
+
if self.target_region in regions:
|
|
67
|
+
self._available |= names
|
|
68
|
+
|
|
69
|
+
def known(self, namespace: str) -> bool:
|
|
70
|
+
return (namespace in self._known or namespace in GLOBAL_SERVICES
|
|
71
|
+
or namespace in self.guide_available or namespace in self.guide_missing
|
|
72
|
+
or namespace in self.override_available or namespace in self.override_unavailable)
|
|
73
|
+
|
|
74
|
+
def status(self, namespace: str) -> str:
|
|
75
|
+
"""Return 'ready', 'wait' or 'verify' for an ARN service namespace."""
|
|
76
|
+
if namespace in self.override_unavailable:
|
|
77
|
+
return "wait"
|
|
78
|
+
if namespace in self.override_available:
|
|
79
|
+
return "ready"
|
|
80
|
+
if namespace in self.guide_available:
|
|
81
|
+
return "ready"
|
|
82
|
+
if namespace in self.guide_missing:
|
|
83
|
+
return "wait"
|
|
84
|
+
if namespace in GLOBAL_SERVICES:
|
|
85
|
+
return "verify"
|
|
86
|
+
if namespace in self._available:
|
|
87
|
+
return "ready"
|
|
88
|
+
return "verify"
|
|
89
|
+
|
|
90
|
+
def reason(self, namespace: str) -> str:
|
|
91
|
+
if namespace in self.override_unavailable:
|
|
92
|
+
return "Marked unavailable in catalog overrides"
|
|
93
|
+
if namespace in self.override_available:
|
|
94
|
+
return "Marked available in catalog overrides"
|
|
95
|
+
if namespace in self.guide_available:
|
|
96
|
+
return f"Listed in the AWS European Sovereign Cloud User Guide (checked {self.guide_checked})"
|
|
97
|
+
if namespace in self.guide_missing:
|
|
98
|
+
note = self.guide_notes.get(namespace, "Check AWS Capabilities by Region for the roadmap.")
|
|
99
|
+
return (f"{self.guide_missing[namespace]} is not in the AWS European Sovereign Cloud User Guide "
|
|
100
|
+
f"(checked {self.guide_checked}) or the SDK endpoint data. {note}")
|
|
101
|
+
if namespace in GLOBAL_SERVICES:
|
|
102
|
+
return "Global or edge service: check how it is offered in the target partition"
|
|
103
|
+
if namespace in self._available:
|
|
104
|
+
return f"Endpoint listed for {self.target_region}"
|
|
105
|
+
if namespace in self._known:
|
|
106
|
+
return f"No endpoint listed for {self.target_region} in botocore {self.botocore_version}: verify against AWS Capabilities by Region"
|
|
107
|
+
return "Service not recognised: verify manually"
|
sovlens/cli.py
ADDED
|
@@ -0,0 +1,97 @@
|
|
|
1
|
+
"""sovlens scan: read-only readiness check for the AWS European Sovereign Cloud."""
|
|
2
|
+
from __future__ import annotations
|
|
3
|
+
|
|
4
|
+
import argparse
|
|
5
|
+
import json
|
|
6
|
+
import sys
|
|
7
|
+
from pathlib import Path
|
|
8
|
+
|
|
9
|
+
import boto3
|
|
10
|
+
from botocore.exceptions import BotoCoreError, ClientError
|
|
11
|
+
|
|
12
|
+
from . import __version__, deps, inventory, report, runner
|
|
13
|
+
from .catalog import Catalog
|
|
14
|
+
|
|
15
|
+
try: # Sovlens Pro is a separate, licensed package
|
|
16
|
+
import sovlens_pro as _pro
|
|
17
|
+
except ImportError:
|
|
18
|
+
_pro = None
|
|
19
|
+
|
|
20
|
+
|
|
21
|
+
def run_scan(session, target: str, regions: list[str] | None, overrides: Path | None,
|
|
22
|
+
iac: Path | None = None) -> dict:
|
|
23
|
+
runner.say("Checking credentials")
|
|
24
|
+
account_id = runner.client(session, "sts").get_caller_identity()["Account"]
|
|
25
|
+
regions = regions or inventory.enabled_regions(session)
|
|
26
|
+
runner.say(f"Account {account_id}, {len(regions)} regions")
|
|
27
|
+
catalog = Catalog(target, overrides)
|
|
28
|
+
usage, w1 = inventory.collect(session, regions)
|
|
29
|
+
if _pro is not None:
|
|
30
|
+
return _pro.run(session, account_id, target, catalog, usage, w1, regions=regions, iac=iac)
|
|
31
|
+
summary, w2, _org = deps.scan(session, account_id)
|
|
32
|
+
return report.build(account_id, target, catalog, usage, summary, w1 + w2)
|
|
33
|
+
|
|
34
|
+
|
|
35
|
+
def main(argv: list[str] | None = None) -> int:
|
|
36
|
+
parser = argparse.ArgumentParser(prog="sovlens", description=__doc__)
|
|
37
|
+
parser.add_argument("--version", action="version", version=__version__)
|
|
38
|
+
sub = parser.add_subparsers(dest="command", required=True)
|
|
39
|
+
scan = sub.add_parser("scan", help="scan the current account (read-only)")
|
|
40
|
+
scan.add_argument("--profile", help="AWS CLI profile to use")
|
|
41
|
+
scan.add_argument("--regions", help="comma-separated regions to scan (default: all enabled)")
|
|
42
|
+
scan.add_argument("--target", default="eusc-de-east-1", help="target ESC region")
|
|
43
|
+
scan.add_argument("--iac", help="folder with Terraform or CloudFormation code to check (Sovlens Pro)")
|
|
44
|
+
scan.add_argument("--report", choices=["html", "json", "both"], default="both")
|
|
45
|
+
scan.add_argument("--out", default="sovlens-report", help="output file name without extension")
|
|
46
|
+
scan.add_argument("--quiet", action="store_true", help="no progress output")
|
|
47
|
+
scan.add_argument("--overrides", default="catalog/overrides.json", help="catalog overrides file")
|
|
48
|
+
args = parser.parse_args(argv)
|
|
49
|
+
|
|
50
|
+
runner.set_quiet(args.quiet)
|
|
51
|
+
iac = Path(args.iac) if args.iac else None
|
|
52
|
+
if iac is not None and _pro is None:
|
|
53
|
+
print("Note: --iac is part of Sovlens Pro (https://sovlens.dev). Skipping the code check.")
|
|
54
|
+
iac = None
|
|
55
|
+
elif iac is not None and not iac.is_dir():
|
|
56
|
+
print(f"Error: --iac folder not found: {iac}", file=sys.stderr)
|
|
57
|
+
return 2
|
|
58
|
+
|
|
59
|
+
try:
|
|
60
|
+
session = boto3.Session(profile_name=args.profile) if args.profile else boto3.Session()
|
|
61
|
+
regions = [r.strip() for r in args.regions.split(",")] if args.regions else None
|
|
62
|
+
result = run_scan(session, args.target, regions, Path(args.overrides), iac)
|
|
63
|
+
except BotoCoreError as exc:
|
|
64
|
+
print(f"Error: could not use your AWS credentials: {exc}", file=sys.stderr)
|
|
65
|
+
print("If you signed in with 'aws login', run: pip install \"botocore[crt]\"", file=sys.stderr)
|
|
66
|
+
return 1
|
|
67
|
+
except ClientError as exc:
|
|
68
|
+
print(f"Error: AWS rejected the request: {exc}", file=sys.stderr)
|
|
69
|
+
return 1
|
|
70
|
+
|
|
71
|
+
runner.say("Writing report")
|
|
72
|
+
written = []
|
|
73
|
+
if args.report in ("json", "both"):
|
|
74
|
+
Path(f"{args.out}.json").write_text(json.dumps(result, indent=2))
|
|
75
|
+
written.append(f"{args.out}.json")
|
|
76
|
+
if args.report in ("html", "both"):
|
|
77
|
+
page = _pro.to_html(result) if _pro is not None else report.to_html(result)
|
|
78
|
+
Path(f"{args.out}.html").write_text(page)
|
|
79
|
+
written.append(f"{args.out}.html")
|
|
80
|
+
|
|
81
|
+
s = result["summary"]
|
|
82
|
+
print(f"Account {result['account_id']} -> {result['target_region']}")
|
|
83
|
+
print(f" Services ready: {s['ready']}")
|
|
84
|
+
print(f" To verify: {s['verify']}")
|
|
85
|
+
print(f" Must wait: {s['wait']}")
|
|
86
|
+
print(f" Dependencies outside your control: {s['outside_control']}")
|
|
87
|
+
print(f" All cross-partition dependencies: {s['dependencies']}")
|
|
88
|
+
if result["warnings"]:
|
|
89
|
+
print(f" Warnings: {len(result['warnings'])} (see report)")
|
|
90
|
+
if _pro is None:
|
|
91
|
+
print(" Sovlens Pro lists each one with a fix: https://sovlens.dev")
|
|
92
|
+
print("Report: " + ", ".join(written))
|
|
93
|
+
return 0
|
|
94
|
+
|
|
95
|
+
|
|
96
|
+
if __name__ == "__main__":
|
|
97
|
+
sys.exit(main())
|
|
@@ -0,0 +1,345 @@
|
|
|
1
|
+
{
|
|
2
|
+
"_comment": "Services documented in the AWS European Sovereign Cloud User Guide, mapped to ARN service namespaces. 'not_listed' holds widely used services that the guide does not cover and the SDK endpoint data does not list either.",
|
|
3
|
+
"source": "https://docs.aws.eu/esc/latest/userguide/services.html",
|
|
4
|
+
"checked": "2026-11-17",
|
|
5
|
+
"services": {
|
|
6
|
+
"AWS Account Management": [
|
|
7
|
+
"account"
|
|
8
|
+
],
|
|
9
|
+
"Amazon API Gateway": [
|
|
10
|
+
"apigateway",
|
|
11
|
+
"execute-api"
|
|
12
|
+
],
|
|
13
|
+
"AWS AppConfig": [
|
|
14
|
+
"appconfig"
|
|
15
|
+
],
|
|
16
|
+
"Application Auto Scaling": [
|
|
17
|
+
"application-autoscaling"
|
|
18
|
+
],
|
|
19
|
+
"AWS ARC - Zonal Shift": [
|
|
20
|
+
"arc-zonal-shift"
|
|
21
|
+
],
|
|
22
|
+
"AWS Artifact": [
|
|
23
|
+
"artifact"
|
|
24
|
+
],
|
|
25
|
+
"Amazon Athena": [
|
|
26
|
+
"athena"
|
|
27
|
+
],
|
|
28
|
+
"AWS Backup": [
|
|
29
|
+
"backup"
|
|
30
|
+
],
|
|
31
|
+
"AWS Batch": [
|
|
32
|
+
"batch"
|
|
33
|
+
],
|
|
34
|
+
"Amazon Bedrock": [
|
|
35
|
+
"bedrock"
|
|
36
|
+
],
|
|
37
|
+
"AWS Billing and Cost Management": [
|
|
38
|
+
"billing",
|
|
39
|
+
"ce",
|
|
40
|
+
"budgets",
|
|
41
|
+
"cur"
|
|
42
|
+
],
|
|
43
|
+
"AWS CDK": [],
|
|
44
|
+
"AWS Certificate Manager": [
|
|
45
|
+
"acm"
|
|
46
|
+
],
|
|
47
|
+
"AWS Cloud Map": [
|
|
48
|
+
"servicediscovery"
|
|
49
|
+
],
|
|
50
|
+
"AWS CloudFormation": [
|
|
51
|
+
"cloudformation"
|
|
52
|
+
],
|
|
53
|
+
"AWS CloudTrail": [
|
|
54
|
+
"cloudtrail"
|
|
55
|
+
],
|
|
56
|
+
"Amazon CloudWatch": [
|
|
57
|
+
"cloudwatch"
|
|
58
|
+
],
|
|
59
|
+
"Amazon CloudWatch Logs": [
|
|
60
|
+
"logs"
|
|
61
|
+
],
|
|
62
|
+
"AWS CodeBuild": [
|
|
63
|
+
"codebuild"
|
|
64
|
+
],
|
|
65
|
+
"AWS CodeDeploy": [
|
|
66
|
+
"codedeploy"
|
|
67
|
+
],
|
|
68
|
+
"AWS CodePipeline": [
|
|
69
|
+
"codepipeline"
|
|
70
|
+
],
|
|
71
|
+
"Amazon Cognito": [
|
|
72
|
+
"cognito-idp",
|
|
73
|
+
"cognito-identity"
|
|
74
|
+
],
|
|
75
|
+
"AWS Compute Optimizer": [
|
|
76
|
+
"compute-optimizer"
|
|
77
|
+
],
|
|
78
|
+
"AWS Config": [
|
|
79
|
+
"config"
|
|
80
|
+
],
|
|
81
|
+
"AWS Control Tower": [
|
|
82
|
+
"controltower"
|
|
83
|
+
],
|
|
84
|
+
"Amazon Data Firehose": [
|
|
85
|
+
"firehose"
|
|
86
|
+
],
|
|
87
|
+
"AWS Database Migration Service": [
|
|
88
|
+
"dms"
|
|
89
|
+
],
|
|
90
|
+
"AWS DataSync": [
|
|
91
|
+
"datasync"
|
|
92
|
+
],
|
|
93
|
+
"AWS Direct Connect": [
|
|
94
|
+
"directconnect"
|
|
95
|
+
],
|
|
96
|
+
"AWS Directory Service": [
|
|
97
|
+
"ds"
|
|
98
|
+
],
|
|
99
|
+
"Amazon DocumentDB": [
|
|
100
|
+
"docdb"
|
|
101
|
+
],
|
|
102
|
+
"Amazon DynamoDB": [
|
|
103
|
+
"dynamodb"
|
|
104
|
+
],
|
|
105
|
+
"Amazon EBS": [
|
|
106
|
+
"ebs"
|
|
107
|
+
],
|
|
108
|
+
"Amazon EC2": [
|
|
109
|
+
"ec2"
|
|
110
|
+
],
|
|
111
|
+
"Amazon EC2 Auto Scaling": [
|
|
112
|
+
"autoscaling"
|
|
113
|
+
],
|
|
114
|
+
"EC2 Image Builder": [
|
|
115
|
+
"imagebuilder"
|
|
116
|
+
],
|
|
117
|
+
"Amazon ECR": [
|
|
118
|
+
"ecr"
|
|
119
|
+
],
|
|
120
|
+
"Amazon ECS": [
|
|
121
|
+
"ecs"
|
|
122
|
+
],
|
|
123
|
+
"Amazon EFS": [
|
|
124
|
+
"elasticfilesystem"
|
|
125
|
+
],
|
|
126
|
+
"Amazon EKS": [
|
|
127
|
+
"eks"
|
|
128
|
+
],
|
|
129
|
+
"Elastic Disaster Recovery": [
|
|
130
|
+
"drs"
|
|
131
|
+
],
|
|
132
|
+
"Elastic Load Balancing": [
|
|
133
|
+
"elasticloadbalancing"
|
|
134
|
+
],
|
|
135
|
+
"Amazon ElastiCache": [
|
|
136
|
+
"elasticache"
|
|
137
|
+
],
|
|
138
|
+
"Amazon EMR": [
|
|
139
|
+
"elasticmapreduce"
|
|
140
|
+
],
|
|
141
|
+
"Amazon End User Messaging": [
|
|
142
|
+
"sms-voice"
|
|
143
|
+
],
|
|
144
|
+
"Amazon EventBridge": [
|
|
145
|
+
"events"
|
|
146
|
+
],
|
|
147
|
+
"Amazon FSx": [
|
|
148
|
+
"fsx"
|
|
149
|
+
],
|
|
150
|
+
"AWS Glue": [
|
|
151
|
+
"glue"
|
|
152
|
+
],
|
|
153
|
+
"Amazon GuardDuty": [
|
|
154
|
+
"guardduty"
|
|
155
|
+
],
|
|
156
|
+
"AWS Health": [
|
|
157
|
+
"health"
|
|
158
|
+
],
|
|
159
|
+
"AWS IAM Identity Center": [
|
|
160
|
+
"sso",
|
|
161
|
+
"identitystore"
|
|
162
|
+
],
|
|
163
|
+
"IAM Roles Anywhere": [
|
|
164
|
+
"rolesanywhere"
|
|
165
|
+
],
|
|
166
|
+
"AWS Identity and Access Management": [
|
|
167
|
+
"iam",
|
|
168
|
+
"sts",
|
|
169
|
+
"access-analyzer"
|
|
170
|
+
],
|
|
171
|
+
"Amazon Kinesis Data Streams": [
|
|
172
|
+
"kinesis"
|
|
173
|
+
],
|
|
174
|
+
"AWS KMS": [
|
|
175
|
+
"kms"
|
|
176
|
+
],
|
|
177
|
+
"AWS Lake Formation": [
|
|
178
|
+
"lakeformation"
|
|
179
|
+
],
|
|
180
|
+
"AWS Lambda": [
|
|
181
|
+
"lambda"
|
|
182
|
+
],
|
|
183
|
+
"AWS License Manager": [
|
|
184
|
+
"license-manager"
|
|
185
|
+
],
|
|
186
|
+
"Amazon Linux": [],
|
|
187
|
+
"Amazon Managed Service for Apache Flink": [
|
|
188
|
+
"kinesisanalytics"
|
|
189
|
+
],
|
|
190
|
+
"Amazon Managed Service for Prometheus": [
|
|
191
|
+
"aps"
|
|
192
|
+
],
|
|
193
|
+
"Amazon MQ": [
|
|
194
|
+
"mq"
|
|
195
|
+
],
|
|
196
|
+
"Amazon Managed Streaming for Apache Kafka": [
|
|
197
|
+
"kafka"
|
|
198
|
+
],
|
|
199
|
+
"AWS Management Console": [],
|
|
200
|
+
"AWS Marketplace": [
|
|
201
|
+
"aws-marketplace"
|
|
202
|
+
],
|
|
203
|
+
"Neptune": [
|
|
204
|
+
"neptune-db"
|
|
205
|
+
],
|
|
206
|
+
"AWS Network Firewall": [
|
|
207
|
+
"network-firewall"
|
|
208
|
+
],
|
|
209
|
+
"Amazon OpenSearch Service": [
|
|
210
|
+
"es"
|
|
211
|
+
],
|
|
212
|
+
"AWS Organizations": [
|
|
213
|
+
"organizations"
|
|
214
|
+
],
|
|
215
|
+
"Amazon Polly": [
|
|
216
|
+
"polly"
|
|
217
|
+
],
|
|
218
|
+
"AWS Private Certificate Authority": [
|
|
219
|
+
"acm-pca"
|
|
220
|
+
],
|
|
221
|
+
"Amazon RDS": [
|
|
222
|
+
"rds"
|
|
223
|
+
],
|
|
224
|
+
"Amazon Redshift": [
|
|
225
|
+
"redshift"
|
|
226
|
+
],
|
|
227
|
+
"AWS Resource Access Manager": [
|
|
228
|
+
"ram"
|
|
229
|
+
],
|
|
230
|
+
"AWS Resource Groups": [
|
|
231
|
+
"resource-groups",
|
|
232
|
+
"tag"
|
|
233
|
+
],
|
|
234
|
+
"Amazon Route 53": [
|
|
235
|
+
"route53"
|
|
236
|
+
],
|
|
237
|
+
"Amazon S3": [
|
|
238
|
+
"s3"
|
|
239
|
+
],
|
|
240
|
+
"Amazon SageMaker AI": [
|
|
241
|
+
"sagemaker"
|
|
242
|
+
],
|
|
243
|
+
"AWS Secrets Manager": [
|
|
244
|
+
"secretsmanager"
|
|
245
|
+
],
|
|
246
|
+
"AWS Security Hub CSPM": [
|
|
247
|
+
"securityhub"
|
|
248
|
+
],
|
|
249
|
+
"Service Quotas": [
|
|
250
|
+
"servicequotas"
|
|
251
|
+
],
|
|
252
|
+
"Amazon SES": [
|
|
253
|
+
"ses"
|
|
254
|
+
],
|
|
255
|
+
"AWS Shield": [
|
|
256
|
+
"shield"
|
|
257
|
+
],
|
|
258
|
+
"AWS Signer": [
|
|
259
|
+
"signer"
|
|
260
|
+
],
|
|
261
|
+
"Amazon SNS": [
|
|
262
|
+
"sns"
|
|
263
|
+
],
|
|
264
|
+
"Amazon SQS": [
|
|
265
|
+
"sqs"
|
|
266
|
+
],
|
|
267
|
+
"AWS Step Functions": [
|
|
268
|
+
"states"
|
|
269
|
+
],
|
|
270
|
+
"AWS Storage Gateway": [
|
|
271
|
+
"storagegateway"
|
|
272
|
+
],
|
|
273
|
+
"AWS Support": [
|
|
274
|
+
"support"
|
|
275
|
+
],
|
|
276
|
+
"Amazon SWF": [
|
|
277
|
+
"swf"
|
|
278
|
+
],
|
|
279
|
+
"AWS Systems Manager": [
|
|
280
|
+
"ssm"
|
|
281
|
+
],
|
|
282
|
+
"Amazon Transcribe": [
|
|
283
|
+
"transcribe"
|
|
284
|
+
],
|
|
285
|
+
"AWS Transfer Family": [
|
|
286
|
+
"transfer"
|
|
287
|
+
],
|
|
288
|
+
"AWS Transit Gateway": [
|
|
289
|
+
"ec2"
|
|
290
|
+
],
|
|
291
|
+
"AWS Trusted Advisor": [
|
|
292
|
+
"trustedadvisor"
|
|
293
|
+
],
|
|
294
|
+
"AWS User Notifications": [
|
|
295
|
+
"notifications"
|
|
296
|
+
],
|
|
297
|
+
"AWS User Notifications Contacts": [
|
|
298
|
+
"notifications-contacts"
|
|
299
|
+
],
|
|
300
|
+
"Amazon Verified Permissions": [
|
|
301
|
+
"verifiedpermissions"
|
|
302
|
+
],
|
|
303
|
+
"Amazon VPC": [
|
|
304
|
+
"ec2"
|
|
305
|
+
],
|
|
306
|
+
"AWS Virtual Private Network": [
|
|
307
|
+
"ec2"
|
|
308
|
+
],
|
|
309
|
+
"AWS WAF": [
|
|
310
|
+
"wafv2"
|
|
311
|
+
],
|
|
312
|
+
"AWS X-Ray": [
|
|
313
|
+
"xray"
|
|
314
|
+
]
|
|
315
|
+
},
|
|
316
|
+
"not_listed": {
|
|
317
|
+
"cloudfront": "Amazon CloudFront",
|
|
318
|
+
"globalaccelerator": "AWS Global Accelerator",
|
|
319
|
+
"appsync": "AWS AppSync",
|
|
320
|
+
"amplify": "AWS Amplify",
|
|
321
|
+
"quicksight": "Amazon QuickSight",
|
|
322
|
+
"connect": "Amazon Connect",
|
|
323
|
+
"workspaces": "Amazon WorkSpaces",
|
|
324
|
+
"comprehend": "Amazon Comprehend",
|
|
325
|
+
"textract": "Amazon Textract",
|
|
326
|
+
"rekognition": "Amazon Rekognition",
|
|
327
|
+
"translate": "Amazon Translate",
|
|
328
|
+
"memorydb": "Amazon MemoryDB",
|
|
329
|
+
"timestream": "Amazon Timestream",
|
|
330
|
+
"codecommit": "AWS CodeCommit",
|
|
331
|
+
"codeartifact": "AWS CodeArtifact",
|
|
332
|
+
"lightsail": "Amazon Lightsail",
|
|
333
|
+
"apprunner": "AWS App Runner",
|
|
334
|
+
"elasticbeanstalk": "AWS Elastic Beanstalk",
|
|
335
|
+
"inspector2": "Amazon Inspector",
|
|
336
|
+
"macie2": "Amazon Macie",
|
|
337
|
+
"fms": "AWS Firewall Manager"
|
|
338
|
+
},
|
|
339
|
+
"notes": {
|
|
340
|
+
"cloudfront": "AWS said in November 2025 that it expects CloudFront in the ESC by the end of 2026."
|
|
341
|
+
},
|
|
342
|
+
"notes_sources": {
|
|
343
|
+
"cloudfront": "https://aws.amazon.com/blogs/security/announcing-initial-services-available-in-the-aws-european-sovereign-cloud-backed-by-the-full-power-of-aws"
|
|
344
|
+
}
|
|
345
|
+
}
|
sovlens/deps.py
ADDED
|
@@ -0,0 +1,171 @@
|
|
|
1
|
+
"""Dependencies that cross the partition boundary.
|
|
2
|
+
|
|
3
|
+
The AWS European Sovereign Cloud is a separate partition. Roles, policies and
|
|
4
|
+
connections that point at accounts or services in the commercial partition
|
|
5
|
+
will not work from there, whether the resources were built with Terraform,
|
|
6
|
+
CloudFormation or the console.
|
|
7
|
+
|
|
8
|
+
This module holds the shared helpers and the checks of the free edition, which
|
|
9
|
+
reports counts only. Sovlens Pro adds resource policies, replication, network
|
|
10
|
+
links, Lambda layers and infrastructure-as-code checks, with resource names and
|
|
11
|
+
fixes.
|
|
12
|
+
"""
|
|
13
|
+
from __future__ import annotations
|
|
14
|
+
|
|
15
|
+
import re
|
|
16
|
+
|
|
17
|
+
from botocore.exceptions import BotoCoreError, ClientError
|
|
18
|
+
|
|
19
|
+
from . import runner
|
|
20
|
+
|
|
21
|
+
ACCOUNT_RE = re.compile(r"(?<!\d)(\d{12})(?!\d)")
|
|
22
|
+
|
|
23
|
+
# Groups shown in reports, in this order.
|
|
24
|
+
GROUPS = {
|
|
25
|
+
"outside_control": "Outside your control",
|
|
26
|
+
"rebuild": "Rebuild in the sovereign cloud",
|
|
27
|
+
"code": "Code to change",
|
|
28
|
+
}
|
|
29
|
+
|
|
30
|
+
KINDS = {
|
|
31
|
+
"third_party_trust": ("outside_control", "Third-party integration (role with ExternalId)"),
|
|
32
|
+
"external_trust": ("outside_control", "Role trusted by an account outside your organization"),
|
|
33
|
+
"external_resource_policy": ("outside_control", "Resource policy grants an outside account"),
|
|
34
|
+
"cross_account_replication": ("outside_control", "S3 replication to another account"),
|
|
35
|
+
"external_layer": ("outside_control", "Lambda layer from another account"),
|
|
36
|
+
"external_network": ("outside_control", "Network link to another account"),
|
|
37
|
+
"org_trust": ("rebuild", "Role trusted by another account in your organization"),
|
|
38
|
+
"org_membership": ("rebuild", "Account belongs to an AWS Organization"),
|
|
39
|
+
"identity_provider": ("rebuild", "SAML or OIDC identity provider"),
|
|
40
|
+
"private_link": ("rebuild", "Direct Connect or VPN connection"),
|
|
41
|
+
"hardcoded_arn": ("code", "Hardcoded arn:aws: in infrastructure code"),
|
|
42
|
+
}
|
|
43
|
+
|
|
44
|
+
|
|
45
|
+
def as_list(value):
|
|
46
|
+
if value is None:
|
|
47
|
+
return []
|
|
48
|
+
return value if isinstance(value, list) else [value]
|
|
49
|
+
|
|
50
|
+
|
|
51
|
+
class OrgContext:
|
|
52
|
+
"""Which accounts count as 'yours'."""
|
|
53
|
+
|
|
54
|
+
def __init__(self, session, account_id: str):
|
|
55
|
+
self.account_id = account_id
|
|
56
|
+
self.accounts: set[str] = {account_id}
|
|
57
|
+
self.in_org = False
|
|
58
|
+
self.complete = True
|
|
59
|
+
self.warnings: list[str] = []
|
|
60
|
+
try:
|
|
61
|
+
org = runner.client(session, "organizations").describe_organization()["Organization"]
|
|
62
|
+
self.in_org = True
|
|
63
|
+
self.accounts.add(org["MasterAccountId"])
|
|
64
|
+
except (ClientError, BotoCoreError):
|
|
65
|
+
return
|
|
66
|
+
try:
|
|
67
|
+
client = runner.client(session, "organizations")
|
|
68
|
+
for page in client.get_paginator("list_accounts").paginate():
|
|
69
|
+
self.accounts |= {a["Id"] for a in page["Accounts"]}
|
|
70
|
+
except (ClientError, BotoCoreError):
|
|
71
|
+
self.complete = False
|
|
72
|
+
self.warnings.append(
|
|
73
|
+
"Organization accounts could not be listed. Run from the management account "
|
|
74
|
+
"to tell your own accounts from external ones."
|
|
75
|
+
)
|
|
76
|
+
|
|
77
|
+
def is_own(self, account: str) -> bool:
|
|
78
|
+
return account in self.accounts
|
|
79
|
+
|
|
80
|
+
|
|
81
|
+
def principal_accounts(principal) -> list[str]:
|
|
82
|
+
"""12-digit account IDs named in an IAM principal block. '*' is returned as '*'."""
|
|
83
|
+
if principal == "*":
|
|
84
|
+
return ["*"]
|
|
85
|
+
if not isinstance(principal, dict):
|
|
86
|
+
return []
|
|
87
|
+
found = []
|
|
88
|
+
for p in as_list(principal.get("AWS")):
|
|
89
|
+
if p == "*":
|
|
90
|
+
found.append("*")
|
|
91
|
+
continue
|
|
92
|
+
m = ACCOUNT_RE.search(str(p))
|
|
93
|
+
if m:
|
|
94
|
+
found.append(m.group(1))
|
|
95
|
+
return found
|
|
96
|
+
|
|
97
|
+
|
|
98
|
+
def has_external_id(statement: dict) -> bool:
|
|
99
|
+
cond = statement.get("Condition") or {}
|
|
100
|
+
for operator in cond.values():
|
|
101
|
+
if isinstance(operator, dict) and any(k.lower() == "sts:externalid" for k in operator):
|
|
102
|
+
return True
|
|
103
|
+
return False
|
|
104
|
+
|
|
105
|
+
|
|
106
|
+
def role_trust_findings(session, org: OrgContext) -> tuple[list[dict], list[str]]:
|
|
107
|
+
"""One finding per (role, trusted account). Used by both editions."""
|
|
108
|
+
findings: list[dict] = []
|
|
109
|
+
warnings: list[str] = []
|
|
110
|
+
try:
|
|
111
|
+
iam = runner.client(session, "iam")
|
|
112
|
+
for page in iam.get_paginator("list_roles").paginate():
|
|
113
|
+
for role in page["Roles"]:
|
|
114
|
+
if role.get("Path", "").startswith("/aws-service-role/"):
|
|
115
|
+
continue
|
|
116
|
+
doc = role.get("AssumeRolePolicyDocument") or {}
|
|
117
|
+
for stmt in as_list(doc.get("Statement")):
|
|
118
|
+
if stmt.get("Effect") != "Allow":
|
|
119
|
+
continue
|
|
120
|
+
for account in principal_accounts(stmt.get("Principal")):
|
|
121
|
+
if account == org.account_id:
|
|
122
|
+
continue
|
|
123
|
+
if has_external_id(stmt):
|
|
124
|
+
kind = "third_party_trust"
|
|
125
|
+
elif account != "*" and org.is_own(account):
|
|
126
|
+
kind = "org_trust"
|
|
127
|
+
else:
|
|
128
|
+
kind = "external_trust"
|
|
129
|
+
findings.append({"kind": kind, "resource": f"role/{role['RoleName']}",
|
|
130
|
+
"detail": f"trusts {account}"})
|
|
131
|
+
except (ClientError, BotoCoreError) as exc:
|
|
132
|
+
warnings.append(f"IAM roles skipped: {type(exc).__name__}")
|
|
133
|
+
return findings, warnings
|
|
134
|
+
|
|
135
|
+
|
|
136
|
+
def identity_findings(session, org: OrgContext) -> tuple[list[dict], list[str]]:
|
|
137
|
+
findings: list[dict] = []
|
|
138
|
+
warnings: list[str] = []
|
|
139
|
+
if org.in_org:
|
|
140
|
+
findings.append({"kind": "org_membership", "resource": "account",
|
|
141
|
+
"detail": "member of an AWS Organization"})
|
|
142
|
+
try:
|
|
143
|
+
iam = runner.client(session, "iam")
|
|
144
|
+
for p in iam.list_saml_providers().get("SAMLProviderList", []):
|
|
145
|
+
findings.append({"kind": "identity_provider", "resource": p["Arn"].split(":", 5)[-1],
|
|
146
|
+
"detail": "SAML provider"})
|
|
147
|
+
for p in iam.list_open_id_connect_providers().get("OpenIDConnectProviderList", []):
|
|
148
|
+
findings.append({"kind": "identity_provider", "resource": p["Arn"].split(":", 5)[-1],
|
|
149
|
+
"detail": "OIDC provider"})
|
|
150
|
+
except (ClientError, BotoCoreError) as exc:
|
|
151
|
+
warnings.append(f"identity providers skipped: {type(exc).__name__}")
|
|
152
|
+
return findings, warnings
|
|
153
|
+
|
|
154
|
+
|
|
155
|
+
def summarize(findings: list[dict]) -> list[dict]:
|
|
156
|
+
"""Counts per kind, without resource names. The free edition only keeps this."""
|
|
157
|
+
counts: dict[str, int] = {}
|
|
158
|
+
for f in findings:
|
|
159
|
+
counts[f["kind"]] = counts.get(f["kind"], 0) + 1
|
|
160
|
+
order = list(KINDS)
|
|
161
|
+
return [{"kind": k, "group": KINDS[k][0], "count": counts[k]}
|
|
162
|
+
for k in sorted(counts, key=order.index)]
|
|
163
|
+
|
|
164
|
+
|
|
165
|
+
def scan(session, account_id: str) -> tuple[list[dict], list[str], OrgContext]:
|
|
166
|
+
"""Free edition: counts of role trust and identity dependencies."""
|
|
167
|
+
runner.say("Dependencies: organization, roles and identity providers")
|
|
168
|
+
org = OrgContext(session, account_id)
|
|
169
|
+
trust, w1 = role_trust_findings(session, org)
|
|
170
|
+
ident, w2 = identity_findings(session, org)
|
|
171
|
+
return summarize(trust + ident), org.warnings + w1 + w2, org
|
sovlens/inventory.py
ADDED
|
@@ -0,0 +1,119 @@
|
|
|
1
|
+
"""Read-only inventory of the services an account actually uses."""
|
|
2
|
+
from __future__ import annotations
|
|
3
|
+
|
|
4
|
+
from collections import defaultdict
|
|
5
|
+
|
|
6
|
+
from botocore.exceptions import BotoCoreError, ClientError
|
|
7
|
+
|
|
8
|
+
from . import runner
|
|
9
|
+
|
|
10
|
+
# (client name, ARN namespace, paginator/operation, result key, global?)
|
|
11
|
+
PROBES = [
|
|
12
|
+
("cloudfront", "cloudfront", "list_distributions", "DistributionList.Items", True),
|
|
13
|
+
("route53", "route53", "list_hosted_zones", "HostedZones", True),
|
|
14
|
+
("lambda", "lambda", "list_functions", "Functions", False),
|
|
15
|
+
("rds", "rds", "describe_db_instances", "DBInstances", False),
|
|
16
|
+
("dynamodb", "dynamodb", "list_tables", "TableNames", False),
|
|
17
|
+
("ecs", "ecs", "list_clusters", "clusterArns", False),
|
|
18
|
+
("eks", "eks", "list_clusters", "clusters", False),
|
|
19
|
+
("sqs", "sqs", "list_queues", "QueueUrls", False),
|
|
20
|
+
("sns", "sns", "list_topics", "Topics", False),
|
|
21
|
+
("ecr", "ecr", "describe_repositories", "repositories", False),
|
|
22
|
+
]
|
|
23
|
+
|
|
24
|
+
|
|
25
|
+
def _dig(data: dict, dotted: str):
|
|
26
|
+
for part in dotted.split("."):
|
|
27
|
+
data = (data or {}).get(part)
|
|
28
|
+
return data or []
|
|
29
|
+
|
|
30
|
+
|
|
31
|
+
def enabled_regions(session) -> list[str]:
|
|
32
|
+
try:
|
|
33
|
+
ec2 = runner.client(session, "ec2")
|
|
34
|
+
return sorted(r["RegionName"] for r in ec2.describe_regions()["Regions"])
|
|
35
|
+
except (ClientError, BotoCoreError):
|
|
36
|
+
return [session.region_name] if session.region_name else []
|
|
37
|
+
|
|
38
|
+
|
|
39
|
+
def _count(client, op: str, key: str) -> int:
|
|
40
|
+
if client.can_paginate(op):
|
|
41
|
+
return sum(len(_dig(p, key)) for p in client.get_paginator(op).paginate())
|
|
42
|
+
return len(_dig(getattr(client, op)(), key))
|
|
43
|
+
|
|
44
|
+
|
|
45
|
+
def _scan_region(session, region: str, probes) -> tuple[dict, dict, list[str]]:
|
|
46
|
+
tagged: dict[str, int] = defaultdict(int)
|
|
47
|
+
probed: dict[str, int] = {}
|
|
48
|
+
warnings: list[str] = []
|
|
49
|
+
try:
|
|
50
|
+
client = runner.client(session, "resourcegroupstaggingapi", region)
|
|
51
|
+
for page in client.get_paginator("get_resources").paginate():
|
|
52
|
+
for res in page.get("ResourceTagMappingList", []):
|
|
53
|
+
parts = res["ResourceARN"].split(":")
|
|
54
|
+
if len(parts) > 2 and parts[2]:
|
|
55
|
+
tagged[parts[2]] += 1
|
|
56
|
+
except (ClientError, BotoCoreError) as exc:
|
|
57
|
+
warnings.append(f"tagging API skipped in {region}: {type(exc).__name__}")
|
|
58
|
+
for client_name, ns, op, key in probes:
|
|
59
|
+
try:
|
|
60
|
+
n = _count(runner.client(session, client_name, region), op, key)
|
|
61
|
+
except (ClientError, BotoCoreError) as exc:
|
|
62
|
+
warnings.append(f"{client_name}:{op} skipped in {region}: {type(exc).__name__}")
|
|
63
|
+
continue
|
|
64
|
+
if n:
|
|
65
|
+
probed[ns] = n
|
|
66
|
+
return dict(tagged), probed, warnings
|
|
67
|
+
|
|
68
|
+
|
|
69
|
+
def collect(session, regions: list[str]) -> tuple[dict, list[str]]:
|
|
70
|
+
"""Return ({namespace: {"count": n, "regions": [...]}}, warnings)."""
|
|
71
|
+
usage: dict = defaultdict(lambda: {"count": 0, "regions": set()})
|
|
72
|
+
warnings: list[str] = []
|
|
73
|
+
regional = [(c, ns, op, key) for c, ns, op, key, is_global in PROBES if not is_global]
|
|
74
|
+
global_probes = [(c, ns, op, key) for c, ns, op, key, is_global in PROBES if is_global]
|
|
75
|
+
|
|
76
|
+
results = runner.for_regions(regions, lambda r: _scan_region(session, r, regional), "Inventory")
|
|
77
|
+
probe_totals: dict[str, int] = defaultdict(int)
|
|
78
|
+
for region, (tagged, probed, warn) in zip(regions, results):
|
|
79
|
+
warnings += warn
|
|
80
|
+
for ns, n in tagged.items():
|
|
81
|
+
usage[ns]["count"] += n
|
|
82
|
+
usage[ns]["regions"].add(region)
|
|
83
|
+
for ns, n in probed.items():
|
|
84
|
+
probe_totals[ns] += n
|
|
85
|
+
usage[ns]["regions"].add(region)
|
|
86
|
+
|
|
87
|
+
runner.say("Inventory: global services and S3")
|
|
88
|
+
for client_name, ns, op, key in global_probes:
|
|
89
|
+
try:
|
|
90
|
+
n = _count(runner.client(session, client_name, regions[0] if regions else None), op, key)
|
|
91
|
+
except (ClientError, BotoCoreError) as exc:
|
|
92
|
+
warnings.append(f"{client_name}:{op} skipped: {type(exc).__name__}")
|
|
93
|
+
continue
|
|
94
|
+
if n:
|
|
95
|
+
probe_totals[ns] += n
|
|
96
|
+
usage[ns]["regions"].add("global")
|
|
97
|
+
|
|
98
|
+
# S3 buckets are regional even though the API is global.
|
|
99
|
+
try:
|
|
100
|
+
s3 = runner.client(session, "s3")
|
|
101
|
+
buckets = [b for page in s3.get_paginator("list_buckets").paginate() for b in page.get("Buckets", [])]
|
|
102
|
+
for b in buckets:
|
|
103
|
+
region = b.get("BucketRegion")
|
|
104
|
+
if not region:
|
|
105
|
+
try:
|
|
106
|
+
region = s3.get_bucket_location(Bucket=b["Name"]).get("LocationConstraint") or "us-east-1"
|
|
107
|
+
except (ClientError, BotoCoreError):
|
|
108
|
+
region = "unknown"
|
|
109
|
+
usage["s3"]["regions"].add(region)
|
|
110
|
+
if buckets:
|
|
111
|
+
probe_totals["s3"] = len(buckets)
|
|
112
|
+
except (ClientError, BotoCoreError) as exc:
|
|
113
|
+
warnings.append(f"s3:list_buckets skipped: {type(exc).__name__}")
|
|
114
|
+
|
|
115
|
+
# Probes are exact counts; prefer them over tag-based counts for the same service.
|
|
116
|
+
for ns, n in probe_totals.items():
|
|
117
|
+
usage[ns]["count"] = max(usage[ns]["count"], n)
|
|
118
|
+
|
|
119
|
+
return {k: {"count": v["count"], "regions": sorted(v["regions"])} for k, v in usage.items()}, warnings
|
sovlens/report.py
ADDED
|
@@ -0,0 +1,102 @@
|
|
|
1
|
+
"""Turn scan results into JSON and a self-contained HTML report."""
|
|
2
|
+
from __future__ import annotations
|
|
3
|
+
|
|
4
|
+
import html
|
|
5
|
+
from datetime import datetime, timezone
|
|
6
|
+
|
|
7
|
+
from .deps import GROUPS, KINDS
|
|
8
|
+
|
|
9
|
+
LABEL = {"ready": "Ready", "verify": "Verify", "wait": "Wait"}
|
|
10
|
+
COLOR = {"ready": "#4ADE9B", "verify": "#F5C04A", "wait": "#FF8A80"}
|
|
11
|
+
PRO_NOTE = ("Sovlens Pro lists every affected resource with a fix, names the vendor behind each outside account "
|
|
12
|
+
"with its ESC status, and adds resource policies, S3 replication, network links, Lambda layers and "
|
|
13
|
+
"infrastructure-as-code checks: https://sovlens.dev")
|
|
14
|
+
|
|
15
|
+
|
|
16
|
+
def build(account_id, target, catalog, usage, deps_summary, warnings, edition="free", deps=None) -> dict:
|
|
17
|
+
services, unknown = [], []
|
|
18
|
+
for ns in sorted(usage):
|
|
19
|
+
if not catalog.known(ns):
|
|
20
|
+
unknown.append({"namespace": ns, "resources": usage[ns]["count"], "regions": usage[ns]["regions"]})
|
|
21
|
+
continue
|
|
22
|
+
services.append({
|
|
23
|
+
"service": ns,
|
|
24
|
+
"resources": usage[ns]["count"],
|
|
25
|
+
"regions": usage[ns]["regions"],
|
|
26
|
+
"status": catalog.status(ns),
|
|
27
|
+
"reason": catalog.reason(ns),
|
|
28
|
+
})
|
|
29
|
+
order = {"wait": 0, "verify": 1, "ready": 2}
|
|
30
|
+
services.sort(key=lambda s: (order[s["status"]], s["service"]))
|
|
31
|
+
summary = {k: sum(1 for s in services if s["status"] == k) for k in ("ready", "verify", "wait")}
|
|
32
|
+
summary["dependencies"] = sum(d["count"] for d in deps_summary)
|
|
33
|
+
summary["outside_control"] = sum(d["count"] for d in deps_summary if d["group"] == "outside_control")
|
|
34
|
+
result = {
|
|
35
|
+
"tool": "sovlens",
|
|
36
|
+
"edition": edition,
|
|
37
|
+
"generated_at": datetime.now(timezone.utc).isoformat(timespec="seconds"),
|
|
38
|
+
"account_id": account_id,
|
|
39
|
+
"target_region": target,
|
|
40
|
+
"catalog_source": f"ESC User Guide ({catalog.guide_checked}) + botocore {catalog.botocore_version} endpoint data + overrides",
|
|
41
|
+
"summary": summary,
|
|
42
|
+
"services": services,
|
|
43
|
+
"unrecognised": unknown,
|
|
44
|
+
"dependencies_summary": deps_summary,
|
|
45
|
+
"warnings": warnings,
|
|
46
|
+
"disclaimer": "Technical readiness only. Not legal or compliance advice. Verify 'Verify' items against AWS Capabilities by Region.",
|
|
47
|
+
}
|
|
48
|
+
if deps is not None:
|
|
49
|
+
result["dependencies"] = deps
|
|
50
|
+
return result
|
|
51
|
+
|
|
52
|
+
|
|
53
|
+
def dependencies_section(r: dict) -> str:
|
|
54
|
+
"""Free edition: counts per kind. Sovlens Pro replaces this section."""
|
|
55
|
+
e = html.escape
|
|
56
|
+
rows = "".join(
|
|
57
|
+
f"<tr><td>{e(GROUPS[d['group']])}</td><td>{e(KINDS[d['kind']][1])}</td><td>{d['count']}</td></tr>"
|
|
58
|
+
for d in r["dependencies_summary"]
|
|
59
|
+
) or "<tr><td colspan='3'>Nothing found.</td></tr>"
|
|
60
|
+
return ("<h2>Cross-partition dependencies</h2><div class='wrap'><table>"
|
|
61
|
+
"<tr><th>Group</th><th>What</th><th>Count</th></tr>"
|
|
62
|
+
f"{rows}</table></div><p class='meta' style='margin-top:10px'>{e(PRO_NOTE)}</p>")
|
|
63
|
+
|
|
64
|
+
|
|
65
|
+
def to_html(r: dict, deps_html: str | None = None) -> str:
|
|
66
|
+
e = html.escape
|
|
67
|
+
tiles = "".join(
|
|
68
|
+
f"<div class='tile'><b style='color:{c}'>{r['summary'][k]}</b><span>{e(t)}</span></div>"
|
|
69
|
+
for k, t, c in [("ready", "Services ready", COLOR["ready"]), ("verify", "To verify", COLOR["verify"]),
|
|
70
|
+
("wait", "Must wait", COLOR["wait"]),
|
|
71
|
+
("outside_control", "Dependencies outside your control", "#AFC2FF")]
|
|
72
|
+
)
|
|
73
|
+
rows = "".join(
|
|
74
|
+
f"<tr><td style='white-space:nowrap'><code>{e(s['service'])}</code></td><td>{s['resources']}</td>"
|
|
75
|
+
f"<td>{'<br>'.join(f'<span style=white-space:nowrap>{e(r)}</span>' for r in s['regions'])}</td>"
|
|
76
|
+
f"<td><span class='pill' style='color:{COLOR[s['status']]}'>{LABEL[s['status']]}</span></td><td>{e(s['reason'])}</td></tr>"
|
|
77
|
+
for s in r["services"]
|
|
78
|
+
) or "<tr><td colspan='5'>No resources found.</td></tr>"
|
|
79
|
+
unknown = ""
|
|
80
|
+
if r["unrecognised"]:
|
|
81
|
+
items = ", ".join(f"<code>{e(u['namespace'])}</code> ({u['resources']})" for u in r["unrecognised"])
|
|
82
|
+
unknown = f"<p class='meta' style='margin-top:10px'>Other tagged resource types, not assessed: {items}</p>"
|
|
83
|
+
warn = "".join(f"<li>{e(w)}</li>" for w in r["warnings"]) or "<li>None</li>"
|
|
84
|
+
deps = deps_html if deps_html is not None else dependencies_section(r)
|
|
85
|
+
return f"""<!doctype html><html lang="en"><head><meta charset="utf-8">
|
|
86
|
+
<meta name="viewport" content="width=device-width,initial-scale=1"><title>Sovlens report {e(r['account_id'])}</title>
|
|
87
|
+
<style>body{{margin:0;background:#0E1116;color:#E8EAF0;font:15px/1.55 system-ui,sans-serif}}
|
|
88
|
+
main{{max-width:1100px;margin:0 auto;padding:40px 20px}}h1{{font-size:28px;margin:0 0 4px}}h2{{font-size:19px;margin:36px 0 12px}}
|
|
89
|
+
p.meta{{color:#9AA3B2;margin:0 0 24px}}.tiles{{display:flex;flex-wrap:wrap;gap:12px}}
|
|
90
|
+
.tile{{flex:1 1 160px;background:#151A22;border:1px solid #262D3A;border-radius:12px;padding:14px 16px}}
|
|
91
|
+
.tile b{{display:block;font-size:30px;line-height:1.1}}.tile span{{color:#B4BCCA;font-size:13px}}
|
|
92
|
+
.wrap{{overflow-x:auto;border:1px solid #262D3A;border-radius:12px}}table{{border-collapse:collapse;width:100%;min-width:720px}}
|
|
93
|
+
th,td{{text-align:left;padding:10px 12px;border-bottom:1px solid #222937;vertical-align:top}}th{{color:#9AA3B2;font-size:12px;text-transform:uppercase;letter-spacing:.05em}}
|
|
94
|
+
code{{font:13px ui-monospace,monospace;word-break:break-all}}.pill{{font-weight:600}}li{{color:#B4BCCA}}footer{{color:#8A93A3;font-size:13px;margin-top:32px}}</style></head>
|
|
95
|
+
<body><main><h1>ESC readiness report</h1>
|
|
96
|
+
<p class="meta">Account {e(r['account_id'])} → {e(r['target_region'])} · {e(r['generated_at'])} · {e(r['catalog_source'])}</p>
|
|
97
|
+
<div class="tiles">{tiles}</div>
|
|
98
|
+
<h2>Services in use</h2><div class="wrap"><table><tr><th>Service</th><th>Resources</th><th>Regions</th><th>Status</th><th>Why</th></tr>{rows}</table></div>
|
|
99
|
+
{unknown}
|
|
100
|
+
{deps}
|
|
101
|
+
<h2>Scan warnings</h2><ul>{warn}</ul>
|
|
102
|
+
<footer>{e(r['disclaimer'])} Sovlens is not affiliated with Amazon Web Services.</footer></main></body></html>"""
|
sovlens/runner.py
ADDED
|
@@ -0,0 +1,54 @@
|
|
|
1
|
+
"""Shared plumbing: fast-failing AWS clients, parallel regions and progress output."""
|
|
2
|
+
from __future__ import annotations
|
|
3
|
+
|
|
4
|
+
import sys
|
|
5
|
+
import threading
|
|
6
|
+
import time
|
|
7
|
+
from concurrent.futures import ThreadPoolExecutor, as_completed
|
|
8
|
+
|
|
9
|
+
from botocore.config import Config
|
|
10
|
+
|
|
11
|
+
# Fail fast: a region without a service endpoint should not stall the scan.
|
|
12
|
+
CONFIG = Config(connect_timeout=5, read_timeout=20, retries={"max_attempts": 3, "mode": "standard"})
|
|
13
|
+
MAX_WORKERS = 8
|
|
14
|
+
|
|
15
|
+
_lock = threading.Lock()
|
|
16
|
+
_quiet = False
|
|
17
|
+
_start = time.monotonic()
|
|
18
|
+
|
|
19
|
+
|
|
20
|
+
def set_quiet(value: bool) -> None:
|
|
21
|
+
global _quiet
|
|
22
|
+
_quiet = value
|
|
23
|
+
|
|
24
|
+
|
|
25
|
+
def client(session, name: str, region: str | None = None):
|
|
26
|
+
# boto3 sessions are not thread-safe when creating clients; clients themselves are.
|
|
27
|
+
with _lock:
|
|
28
|
+
return session.client(name, region_name=region, config=CONFIG)
|
|
29
|
+
|
|
30
|
+
|
|
31
|
+
def say(message: str) -> None:
|
|
32
|
+
if _quiet:
|
|
33
|
+
return
|
|
34
|
+
elapsed = int(time.monotonic() - _start)
|
|
35
|
+
with _lock:
|
|
36
|
+
print(f"[{elapsed // 60:02d}:{elapsed % 60:02d}] {message}", file=sys.stderr, flush=True)
|
|
37
|
+
|
|
38
|
+
|
|
39
|
+
def for_regions(regions: list[str], fn, what: str) -> list:
|
|
40
|
+
"""Run fn(region) for every region in parallel and report progress. Returns results in region order."""
|
|
41
|
+
results: dict[str, object] = {}
|
|
42
|
+
total = len(regions)
|
|
43
|
+
if not total:
|
|
44
|
+
return []
|
|
45
|
+
say(f"{what}: 0/{total} regions")
|
|
46
|
+
done = 0
|
|
47
|
+
with ThreadPoolExecutor(max_workers=min(MAX_WORKERS, total)) as pool:
|
|
48
|
+
futures = {pool.submit(fn, r): r for r in regions}
|
|
49
|
+
for fut in as_completed(futures):
|
|
50
|
+
results[futures[fut]] = fut.result()
|
|
51
|
+
done += 1
|
|
52
|
+
if done == total or done % 4 == 0:
|
|
53
|
+
say(f"{what}: {done}/{total} regions")
|
|
54
|
+
return [results[r] for r in regions]
|
|
@@ -0,0 +1,132 @@
|
|
|
1
|
+
Metadata-Version: 2.4
|
|
2
|
+
Name: sovlens
|
|
3
|
+
Version: 0.3.1
|
|
4
|
+
Summary: Read-only readiness scanner for the AWS European Sovereign Cloud
|
|
5
|
+
Author-email: Sovlens <hello@sovlens.dev>
|
|
6
|
+
License: Apache-2.0
|
|
7
|
+
Project-URL: Homepage, https://sovlens.dev
|
|
8
|
+
Project-URL: Source, https://github.com/sovlens/sovlens
|
|
9
|
+
Project-URL: Issues, https://github.com/sovlens/sovlens/issues
|
|
10
|
+
Project-URL: ESC services list, https://sovlens.dev/esc-services
|
|
11
|
+
Keywords: aws,european sovereign cloud,aws-eusc,eusc-de-east-1,migration,sovereignty,cli
|
|
12
|
+
Classifier: Development Status :: 4 - Beta
|
|
13
|
+
Classifier: Environment :: Console
|
|
14
|
+
Classifier: Intended Audience :: System Administrators
|
|
15
|
+
Classifier: License :: OSI Approved :: Apache Software License
|
|
16
|
+
Classifier: Operating System :: OS Independent
|
|
17
|
+
Classifier: Programming Language :: Python :: 3
|
|
18
|
+
Classifier: Topic :: System :: Systems Administration
|
|
19
|
+
Requires-Python: >=3.10
|
|
20
|
+
Description-Content-Type: text/markdown
|
|
21
|
+
License-File: LICENSE
|
|
22
|
+
Requires-Dist: boto3[crt]>=1.40
|
|
23
|
+
Provides-Extra: dev
|
|
24
|
+
Requires-Dist: pytest; extra == "dev"
|
|
25
|
+
Requires-Dist: moto[all]; extra == "dev"
|
|
26
|
+
Dynamic: license-file
|
|
27
|
+
|
|
28
|
+
# Sovlens
|
|
29
|
+
|
|
30
|
+
[](https://github.com/sovlens/sovlens/actions/workflows/test.yml)
|
|
31
|
+
[](LICENSE)
|
|
32
|
+
|
|
33
|
+
**What in this AWS account will not move to the AWS European Sovereign Cloud as-is?**
|
|
34
|
+
|
|
35
|
+
The AWS European Sovereign Cloud (ESC) is a separate partition, `aws-eusc`, with its own region (`eusc-de-east-1`), accounts and IAM. Moving there is not a region switch: some services are missing, and anything that trusts or talks to another account stops working at the partition boundary.
|
|
36
|
+
|
|
37
|
+
Sovlens is a read-only CLI that scans one AWS account and tells you:
|
|
38
|
+
|
|
39
|
+
- **Which services you use** and whether each one is available in the ESC: Ready, Verify or Wait.
|
|
40
|
+
- **How many dependencies cross the partition boundary**, however the infrastructure was built (Terraform, CloudFormation or the console):
|
|
41
|
+
- roles trusted by third-party vendors (roles with an ExternalId) and by accounts outside your organization,
|
|
42
|
+
- roles trusted by other accounts in your organization,
|
|
43
|
+
- membership in an AWS Organization,
|
|
44
|
+
- SAML and OIDC identity providers.
|
|
45
|
+
|
|
46
|
+
It writes a local HTML and JSON report. Nothing leaves your machine.
|
|
47
|
+
|
|
48
|
+
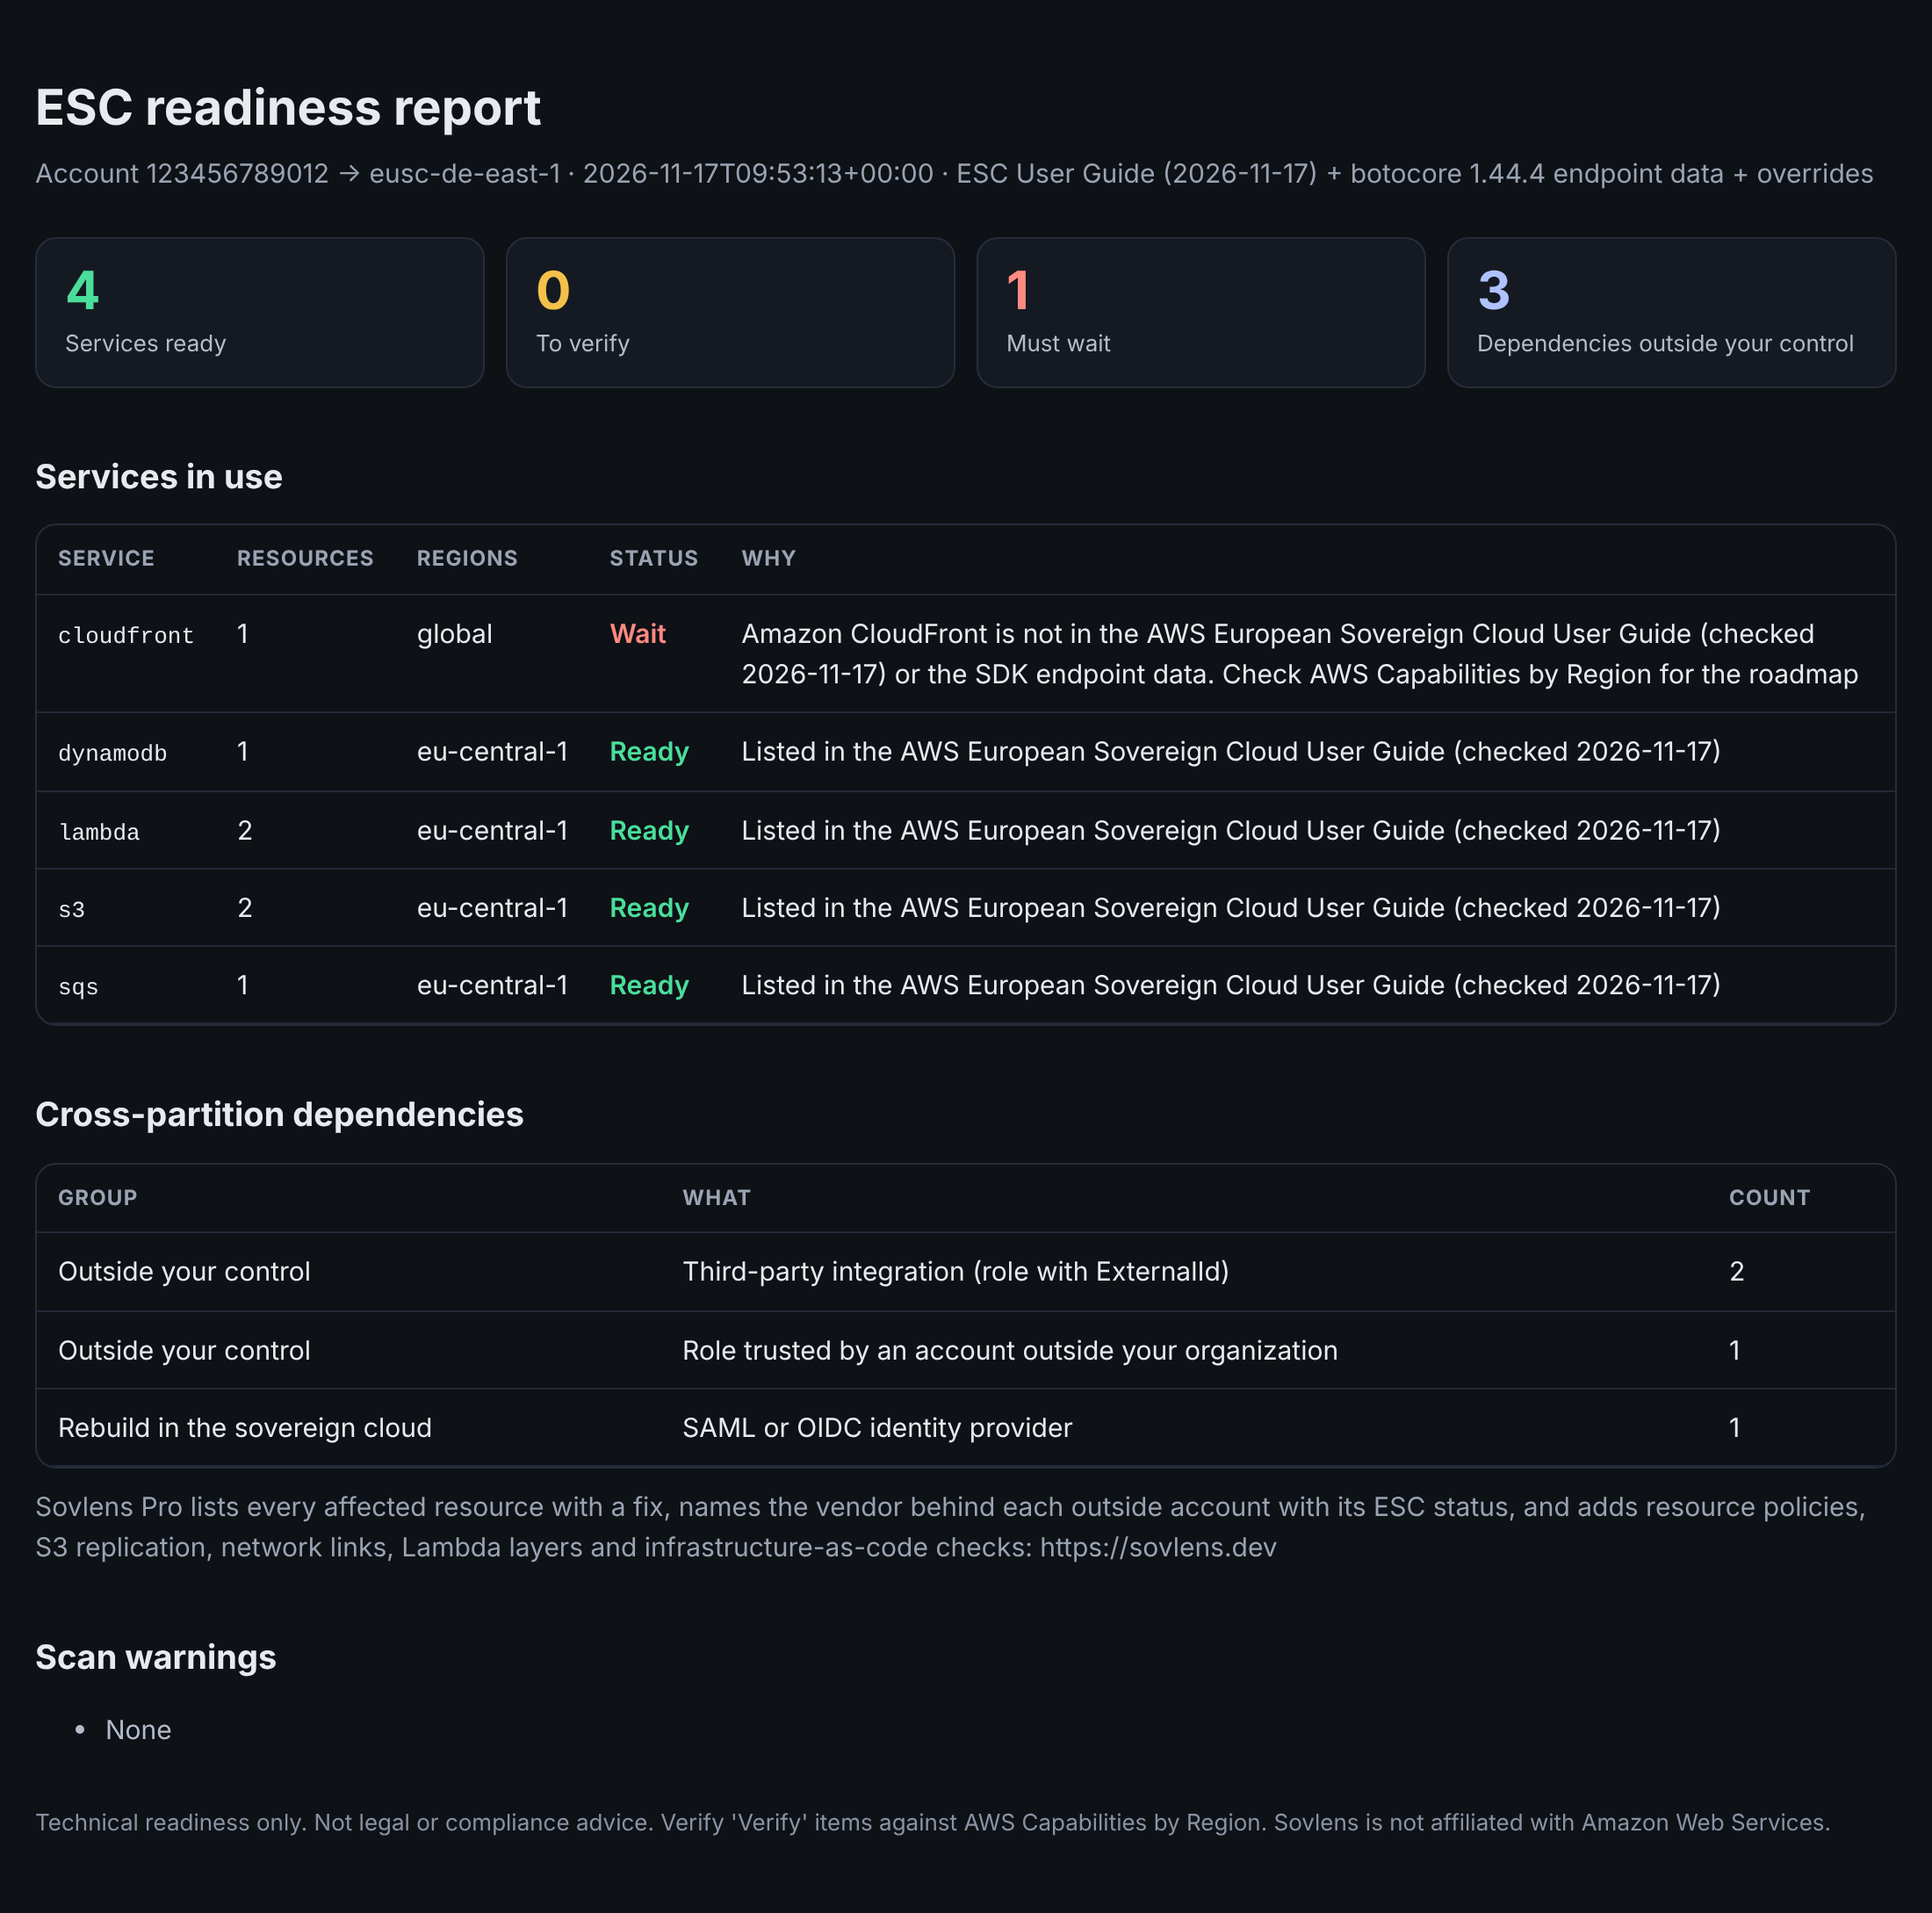
|
|
49
|
+
|
|
50
|
+
*Sample report from a test account.*
|
|
51
|
+
|
|
52
|
+
## Quick start
|
|
53
|
+
|
|
54
|
+
Requires Python 3.10 or newer and AWS credentials with read-only access.
|
|
55
|
+
|
|
56
|
+
```sh
|
|
57
|
+
pipx install sovlens # or: pip install sovlens
|
|
58
|
+
sovlens scan --profile my-profile
|
|
59
|
+
open sovlens-report.html
|
|
60
|
+
```
|
|
61
|
+
|
|
62
|
+
From source:
|
|
63
|
+
|
|
64
|
+
```sh
|
|
65
|
+
git clone https://github.com/sovlens/sovlens && cd sovlens
|
|
66
|
+
python3 -m venv .venv && source .venv/bin/activate
|
|
67
|
+
pip install .
|
|
68
|
+
```
|
|
69
|
+
|
|
70
|
+
| Option | Meaning |
|
|
71
|
+
| --- | --- |
|
|
72
|
+
| `--profile` | AWS profile to use |
|
|
73
|
+
| `--regions eu-central-1,eu-west-1` | Regions to scan (default: all enabled regions, scanned in parallel) |
|
|
74
|
+
| `--target eusc-de-east-1` | Target ESC region |
|
|
75
|
+
| `--report html\|json\|both` | Report format (default: both) |
|
|
76
|
+
| `--out name` | Report file name without extension |
|
|
77
|
+
| `--quiet` | No progress output |
|
|
78
|
+
|
|
79
|
+
A scan of all enabled regions usually takes a few minutes.
|
|
80
|
+
|
|
81
|
+
## Permissions
|
|
82
|
+
|
|
83
|
+
Read-only. The minimal policy is in [`iam/sovlens-readonly-policy.json`](iam/sovlens-readonly-policy.json); `ReadOnlyAccess` or `SecurityAudit` also work. Sovlens never calls an API that creates, changes or deletes anything.
|
|
84
|
+
|
|
85
|
+
Run it from an account that can call `organizations:ListAccounts` (the management account or a delegated administrator) so it can tell your own accounts from external ones. Otherwise every other account counts as external, and the report says so.
|
|
86
|
+
|
|
87
|
+
## How the verdicts work
|
|
88
|
+
|
|
89
|
+
| Status | Meaning |
|
|
90
|
+
| --- | --- |
|
|
91
|
+
| **Ready** | Listed in the [ESC User Guide](https://docs.aws.eu/esc/latest/userguide/services.html), or has an ESC endpoint in the AWS SDK. |
|
|
92
|
+
| **Verify** | Not covered by either source. Check AWS Capabilities by Region. |
|
|
93
|
+
| **Wait** | A widely used service that is not in the ESC User Guide and has no ESC endpoint, such as CloudFront. |
|
|
94
|
+
|
|
95
|
+
The service list is in [`src/sovlens/data/esc_services.json`](src/sovlens/data/esc_services.json), with the date it was last checked. It follows the ESC User Guide rather than SDK endpoint data, because the endpoint data in botocore has no entry for partition-wide services such as IAM, Organizations and Route 53. More on that, and the full list, at [sovlens.dev/esc-services](https://sovlens.dev/esc-services).
|
|
96
|
+
|
|
97
|
+
Found a wrong verdict? Open an issue with the "Service availability correction" template and a link to the AWS source.
|
|
98
|
+
|
|
99
|
+
Dependencies are grouped as **Outside your control** (a vendor or another company must act), **Rebuild in the sovereign cloud** (you recreate it in the ESC) and **Code to change** (from your Terraform or CloudFormation files, Pro only).
|
|
100
|
+
|
|
101
|
+
## Free and Pro
|
|
102
|
+
|
|
103
|
+
This repository is the free, open-source edition. [Sovlens Pro](https://sovlens.dev) is a separate add-on: install it next to this package and the same `sovlens scan` command produces the full report.
|
|
104
|
+
|
|
105
|
+
| | Free (this repo) | Pro |
|
|
106
|
+
| --- | --- | --- |
|
|
107
|
+
| Services in use, with verdicts | Yes | Yes |
|
|
108
|
+
| Cross-partition dependencies | Number per type | Every resource, with a fix |
|
|
109
|
+
| Vendor behind each outside account, with its ESC status | No | Yes |
|
|
110
|
+
| Resource policies (S3, KMS, SQS, SNS) | No | Yes |
|
|
111
|
+
| S3 replication, Lambda layers, VPC peering, Transit Gateway, VPN, Direct Connect | No | Yes |
|
|
112
|
+
| Hardcoded `arn:aws:` in Terraform and CloudFormation (`--iac`) | No | Yes |
|
|
113
|
+
| Organization-wide scan, PDF export | No | Planned |
|
|
114
|
+
|
|
115
|
+
## Known limits
|
|
116
|
+
|
|
117
|
+
- Service-level only. Feature-level differences (for example S3 Express One Zone or STS global endpoints) are not checked yet. The ESC User Guide lists them per service.
|
|
118
|
+
- Inventory uses the Resource Groups Tagging API plus direct checks for core services. Resources of other services that were never tagged can be missed.
|
|
119
|
+
- One account per scan.
|
|
120
|
+
|
|
121
|
+
## Development
|
|
122
|
+
|
|
123
|
+
```sh
|
|
124
|
+
pip install -e ".[dev]"
|
|
125
|
+
pytest
|
|
126
|
+
```
|
|
127
|
+
|
|
128
|
+
See [CONTRIBUTING.md](CONTRIBUTING.md). Security issues: [SECURITY.md](SECURITY.md).
|
|
129
|
+
|
|
130
|
+
## License
|
|
131
|
+
|
|
132
|
+
Apache-2.0. Sovlens is independent and not affiliated with, endorsed by or sponsored by Amazon Web Services. It assesses technical readiness only and is not legal or compliance advice.
|
|
@@ -0,0 +1,14 @@
|
|
|
1
|
+
sovlens/__init__.py,sha256=r4xAFihOf72W9TD-lpMi6ntWSTKTP2SlzKP1ytkjRbI,22
|
|
2
|
+
sovlens/catalog.py,sha256=r2vtFYxUs7xG6gk1Q0awCPAfHVm5Vvv5XnL9_uz-Jrc,4936
|
|
3
|
+
sovlens/cli.py,sha256=nv_TcC3Czhf6prpyNJ9KNHCDglqbkpI_UeaXbUzoyNU,4500
|
|
4
|
+
sovlens/deps.py,sha256=LUkM1jhcWEZKJ4c-PIGcQEeFe3QrLdWSu5imIThZ3lk,7148
|
|
5
|
+
sovlens/inventory.py,sha256=hpCH4F62farKcLB90S-Km-0u7xgPj3n9SNX1EnypEEo,5093
|
|
6
|
+
sovlens/report.py,sha256=KAAaSIDxiKlcAxo_nWbmyX61SBZuLOtP7V0Wt6md_qo,6011
|
|
7
|
+
sovlens/runner.py,sha256=H8oDIOvtZ1zjzGV9l3L-FzjoDtTz_-ENYlJcb4nMZWk,1764
|
|
8
|
+
sovlens/data/esc_services.json,sha256=w-v2RVm60Tjy3VHtqpawijOo5v9fZF0kSF_ivz3ocXA,6042
|
|
9
|
+
sovlens-0.3.1.dist-info/licenses/LICENSE,sha256=dd2-WOzsftNq2W-21v4uTE5y8hrLuL_xSTkBEdGoloA,10201
|
|
10
|
+
sovlens-0.3.1.dist-info/METADATA,sha256=q3BIfkrmxKG3FdR2g4t_HS3vwc6fT1hnK-5l2Er3GaU,6393
|
|
11
|
+
sovlens-0.3.1.dist-info/WHEEL,sha256=mOdXR9C3wMVov7cSY8PY-XCzo3SmmWCHvGQr5csJoao,91
|
|
12
|
+
sovlens-0.3.1.dist-info/entry_points.txt,sha256=5WDn_YJK2_Sqi0niPQo9RK8aXJnD3bvgRX3e2lbL_Co,45
|
|
13
|
+
sovlens-0.3.1.dist-info/top_level.txt,sha256=jX1xpQ_GNYMCtbFhlF1PYpV3KWWDrmniExAtu71LrJg,8
|
|
14
|
+
sovlens-0.3.1.dist-info/RECORD,,
|
|
@@ -0,0 +1,179 @@
|
|
|
1
|
+
|
|
2
|
+
Apache License
|
|
3
|
+
Version 2.0, January 2004
|
|
4
|
+
http://www.apache.org/licenses/
|
|
5
|
+
|
|
6
|
+
TERMS AND CONDITIONS FOR USE, REPRODUCTION, AND DISTRIBUTION
|
|
7
|
+
|
|
8
|
+
1. Definitions.
|
|
9
|
+
|
|
10
|
+
"License" shall mean the terms and conditions for use, reproduction,
|
|
11
|
+
and distribution as defined by Sections 1 through 9 of this document.
|
|
12
|
+
|
|
13
|
+
"Licensor" shall mean the copyright owner or entity authorized by
|
|
14
|
+
the copyright owner that is granting the License.
|
|
15
|
+
|
|
16
|
+
"Legal Entity" shall mean the union of the acting entity and all
|
|
17
|
+
other entities that control, are controlled by, or are under common
|
|
18
|
+
control with that entity. For the purposes of this definition,
|
|
19
|
+
"control" means (i) the power, direct or indirect, to cause the
|
|
20
|
+
direction or management of such entity, whether by contract or
|
|
21
|
+
otherwise, or (ii) ownership of fifty percent (50%) or more of the
|
|
22
|
+
outstanding shares, or (iii) beneficial ownership of such entity.
|
|
23
|
+
|
|
24
|
+
"You" (or "Your") shall mean an individual or Legal Entity
|
|
25
|
+
exercising permissions granted by this License.
|
|
26
|
+
|
|
27
|
+
"Source" form shall mean the preferred form for making modifications,
|
|
28
|
+
including but not limited to software source code, documentation
|
|
29
|
+
source, and configuration files.
|
|
30
|
+
|
|
31
|
+
"Object" form shall mean any form resulting from mechanical
|
|
32
|
+
transformation or translation of a Source form, including but
|
|
33
|
+
not limited to compiled object code, generated documentation,
|
|
34
|
+
and conversions to other media types.
|
|
35
|
+
|
|
36
|
+
"Work" shall mean the work of authorship, whether in Source or
|
|
37
|
+
Object form, made available under the License, as indicated by a
|
|
38
|
+
copyright notice that is included in or attached to the work
|
|
39
|
+
(an example is provided in the Appendix below).
|
|
40
|
+
|
|
41
|
+
"Derivative Works" shall mean any work, whether in Source or Object
|
|
42
|
+
form, that is based on (or derived from) the Work and for which the
|
|
43
|
+
editorial revisions, annotations, elaborations, or other modifications
|
|
44
|
+
represent, as a whole, an original work of authorship. For the purposes
|
|
45
|
+
of this License, Derivative Works shall not include works that remain
|
|
46
|
+
separable from, or merely link (or bind by name) to the interfaces of,
|
|
47
|
+
the Work and Derivative Works thereof.
|
|
48
|
+
|
|
49
|
+
"Contribution" shall mean any work of authorship, including
|
|
50
|
+
the original version of the Work and any modifications or additions
|
|
51
|
+
to that Work or Derivative Works thereof, that is intentionally
|
|
52
|
+
submitted to Licensor for inclusion in the Work by the copyright owner
|
|
53
|
+
or by an individual or Legal Entity authorized to submit on behalf of
|
|
54
|
+
the copyright owner. For the purposes of this definition, "submitted"
|
|
55
|
+
means any form of electronic, verbal, or written communication sent
|
|
56
|
+
to the Licensor or its representatives, including but not limited to
|
|
57
|
+
communication on electronic mailing lists, source code control systems,
|
|
58
|
+
and issue tracking systems that are managed by, or on behalf of, the
|
|
59
|
+
Licensor for the purpose of discussing and improving the Work, but
|
|
60
|
+
excluding communication that is conspicuously marked or otherwise
|
|
61
|
+
designated in writing by the copyright owner as "Not a Contribution."
|
|
62
|
+
|
|
63
|
+
"Contributor" shall mean Licensor and any individual or Legal Entity
|
|
64
|
+
on behalf of whom a Contribution has been received by Licensor and
|
|
65
|
+
subsequently incorporated within the Work.
|
|
66
|
+
|
|
67
|
+
2. Grant of Copyright License. Subject to the terms and conditions of
|
|
68
|
+
this License, each Contributor hereby grants to You a perpetual,
|
|
69
|
+
worldwide, non-exclusive, no-charge, royalty-free, irrevocable
|
|
70
|
+
copyright license to reproduce, prepare Derivative Works of,
|
|
71
|
+
publicly display, publicly perform, sublicense, and distribute the
|
|
72
|
+
Work and such Derivative Works in Source or Object form.
|
|
73
|
+
|
|
74
|
+
3. Grant of Patent License. Subject to the terms and conditions of
|
|
75
|
+
this License, each Contributor hereby grants to You a perpetual,
|
|
76
|
+
worldwide, non-exclusive, no-charge, royalty-free, irrevocable
|
|
77
|
+
(except as stated in this section) patent license to make, have made,
|
|
78
|
+
use, offer to sell, sell, import, and otherwise transfer the Work,
|
|
79
|
+
where such license applies only to those patent claims licensable
|
|
80
|
+
by such Contributor that are necessarily infringed by their
|
|
81
|
+
Contribution(s) alone or by combination of their Contribution(s)
|
|
82
|
+
with the Work to which such Contribution(s) was submitted. If You
|
|
83
|
+
institute patent litigation against any entity (including a
|
|
84
|
+
cross-claim or counterclaim in a lawsuit) alleging that the Work
|
|
85
|
+
or a Contribution incorporated within the Work constitutes direct
|
|
86
|
+
or contributory patent infringement, then any patent licenses
|
|
87
|
+
granted to You under this License for that Work shall terminate
|
|
88
|
+
as of the date such litigation is filed.
|
|
89
|
+
|
|
90
|
+
4. Redistribution. You may reproduce and distribute copies of the
|
|
91
|
+
Work or Derivative Works thereof in any medium, with or without
|
|
92
|
+
modifications, and in Source or Object form, provided that You
|
|
93
|
+
meet the following conditions:
|
|
94
|
+
|
|
95
|
+
(a) You must give any other recipients of the Work or
|
|
96
|
+
Derivative Works a copy of this License; and
|
|
97
|
+
|
|
98
|
+
(b) You must cause any modified files to carry prominent notices
|
|
99
|
+
stating that You changed the files; and
|
|
100
|
+
|
|
101
|
+
(c) You must retain, in the Source form of any Derivative Works
|
|
102
|
+
that You distribute, all copyright, patent, trademark, and
|
|
103
|
+
attribution notices from the Source form of the Work,
|
|
104
|
+
excluding those notices that do not pertain to any part of
|
|
105
|
+
the Derivative Works; and
|
|
106
|
+
|
|
107
|
+
(d) If the Work includes a "NOTICE" text file as part of its
|
|
108
|
+
distribution, then any Derivative Works that You distribute must
|
|
109
|
+
include a readable copy of the attribution notices contained
|
|
110
|
+
within such NOTICE file, excluding those notices that do not
|
|
111
|
+
pertain to any part of the Derivative Works, in at least one
|
|
112
|
+
of the following places: within a NOTICE text file distributed
|
|
113
|
+
as part of the Derivative Works; within the Source form or
|
|
114
|
+
documentation, if provided along with the Derivative Works; or,
|
|
115
|
+
within a display generated by the Derivative Works, if and
|
|
116
|
+
wherever such third-party notices normally appear. The contents
|
|
117
|
+
of the NOTICE file are for informational purposes only and
|
|
118
|
+
do not modify the License. You may add Your own attribution
|
|
119
|
+
notices within Derivative Works that You distribute, alongside
|
|
120
|
+
or as an addendum to the NOTICE text from the Work, provided
|
|
121
|
+
that such additional attribution notices cannot be construed
|
|
122
|
+
as modifying the License.
|
|
123
|
+
|
|
124
|
+
You may add Your own copyright statement to Your modifications and
|
|
125
|
+
may provide additional or different license terms and conditions
|
|
126
|
+
for use, reproduction, or distribution of Your modifications, or
|
|
127
|
+
for any such Derivative Works as a whole, provided Your use,
|
|
128
|
+
reproduction, and distribution of the Work otherwise complies with
|
|
129
|
+
the conditions stated in this License.
|
|
130
|
+
|
|
131
|
+
5. Submission of Contributions. Unless You explicitly state otherwise,
|
|
132
|
+
any Contribution intentionally submitted for inclusion in the Work
|
|
133
|
+
by You to the Licensor shall be under the terms and conditions of
|
|
134
|
+
this License, without any additional terms or conditions.
|
|
135
|
+
Notwithstanding the above, nothing herein shall supersede or modify
|
|
136
|
+
the terms of any separate license agreement you may have executed
|
|
137
|
+
with Licensor regarding such Contributions.
|
|
138
|
+
|
|
139
|
+
6. Trademarks. This License does not grant permission to use the trade
|
|
140
|
+
names, trademarks, service marks, or product names of the Licensor,
|
|
141
|
+
except as required for reasonable and customary use in describing the
|
|
142
|
+
origin of the Work and reproducing the content of the NOTICE file.
|
|
143
|
+
|
|
144
|
+
7. Disclaimer of Warranty. Unless required by applicable law or
|
|
145
|
+
agreed to in writing, Licensor provides the Work (and each
|
|
146
|
+
Contributor provides its Contributions) on an "AS IS" BASIS,
|
|
147
|
+
WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or
|
|
148
|
+
implied, including, without limitation, any warranties or conditions
|
|
149
|
+
of TITLE, NON-INFRINGEMENT, MERCHANTABILITY, or FITNESS FOR A
|
|
150
|
+
PARTICULAR PURPOSE. You are solely responsible for determining the
|
|
151
|
+
appropriateness of using or redistributing the Work and assume any
|
|
152
|
+
risks associated with Your exercise of permissions under this License.
|
|
153
|
+
|
|
154
|
+
8. Limitation of Liability. In no event and under no legal theory,
|
|
155
|
+
whether in tort (including negligence), contract, or otherwise,
|
|
156
|
+
unless required by applicable law (such as deliberate and grossly
|
|
157
|
+
negligent acts) or agreed to in writing, shall any Contributor be
|
|
158
|
+
liable to You for damages, including any direct, indirect, special,
|
|
159
|
+
incidental, or consequential damages of any character arising as a
|
|
160
|
+
result of this License or out of the use or inability to use the
|
|
161
|
+
Work (including but not limited to damages for loss of goodwill,
|
|
162
|
+
work stoppage, computer failure or malfunction, or any and all
|
|
163
|
+
other commercial damages or losses), even if such Contributor
|
|
164
|
+
has been advised of the possibility of such damages.
|
|
165
|
+
|
|
166
|
+
9. Accepting Warranty or Additional Liability. While redistributing
|
|
167
|
+
the Work or Derivative Works thereof, You may choose to offer,
|
|
168
|
+
and charge a fee for, acceptance of support, warranty, indemnity,
|
|
169
|
+
or other liability obligations and/or rights consistent with this
|
|
170
|
+
License. However, in accepting such obligations, You may act only
|
|
171
|
+
on Your own behalf and on Your sole responsibility, not on behalf
|
|
172
|
+
of any other Contributor, and only if You agree to indemnify,
|
|
173
|
+
defend, and hold each Contributor harmless for any liability
|
|
174
|
+
incurred by, or claims asserted against, such Contributor by reason
|
|
175
|
+
of your accepting any such warranty or additional liability.
|
|
176
|
+
|
|
177
|
+
END OF TERMS AND CONDITIONS
|
|
178
|
+
|
|
179
|
+
Copyright 2026 Sovlens
|
|
@@ -0,0 +1 @@
|
|
|
1
|
+
sovlens
|