patchsense 0.1.2__py3-none-win_amd64.whl
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- patchsense-0.1.2.data/scripts/patchsense.exe +0 -0
- patchsense-0.1.2.dist-info/METADATA +446 -0
- patchsense-0.1.2.dist-info/RECORD +7 -0
- patchsense-0.1.2.dist-info/WHEEL +4 -0
- patchsense-0.1.2.dist-info/licenses/LICENSE-APACHE +202 -0
- patchsense-0.1.2.dist-info/licenses/LICENSE-MIT +21 -0
- patchsense-0.1.2.dist-info/sboms/patchsense.cyclonedx.json +7410 -0
|
Binary file
|
|
@@ -0,0 +1,446 @@
|
|
|
1
|
+
Metadata-Version: 2.4
|
|
2
|
+
Name: patchsense
|
|
3
|
+
Version: 0.1.2
|
|
4
|
+
Classifier: Environment :: Console
|
|
5
|
+
Classifier: Programming Language :: Rust
|
|
6
|
+
Classifier: Topic :: Security
|
|
7
|
+
License-File: LICENSE-APACHE
|
|
8
|
+
License-File: LICENSE-MIT
|
|
9
|
+
Summary: Prioritize vulnerabilities from lockfiles using OSV, EPSS, and CISA KEV
|
|
10
|
+
Keywords: security,cve,osv,lockfile,dependencies
|
|
11
|
+
Home-Page: https://github.com/Widyasa/patchsense
|
|
12
|
+
Author: Widya Yasa
|
|
13
|
+
License-Expression: MIT OR Apache-2.0
|
|
14
|
+
Requires-Python: >=3.8
|
|
15
|
+
Description-Content-Type: text/markdown; charset=UTF-8; variant=GFM
|
|
16
|
+
Project-URL: Homepage, https://github.com/Widyasa/patchsense
|
|
17
|
+
Project-URL: Repository, https://github.com/Widyasa/patchsense
|
|
18
|
+
|
|
19
|
+
# PatchSense
|
|
20
|
+
|
|
21
|
+
[](https://crates.io/crates/patchsense)
|
|
22
|
+
[](https://github.com/Widyasa/patchsense#license)
|
|
23
|
+
|
|
24
|
+
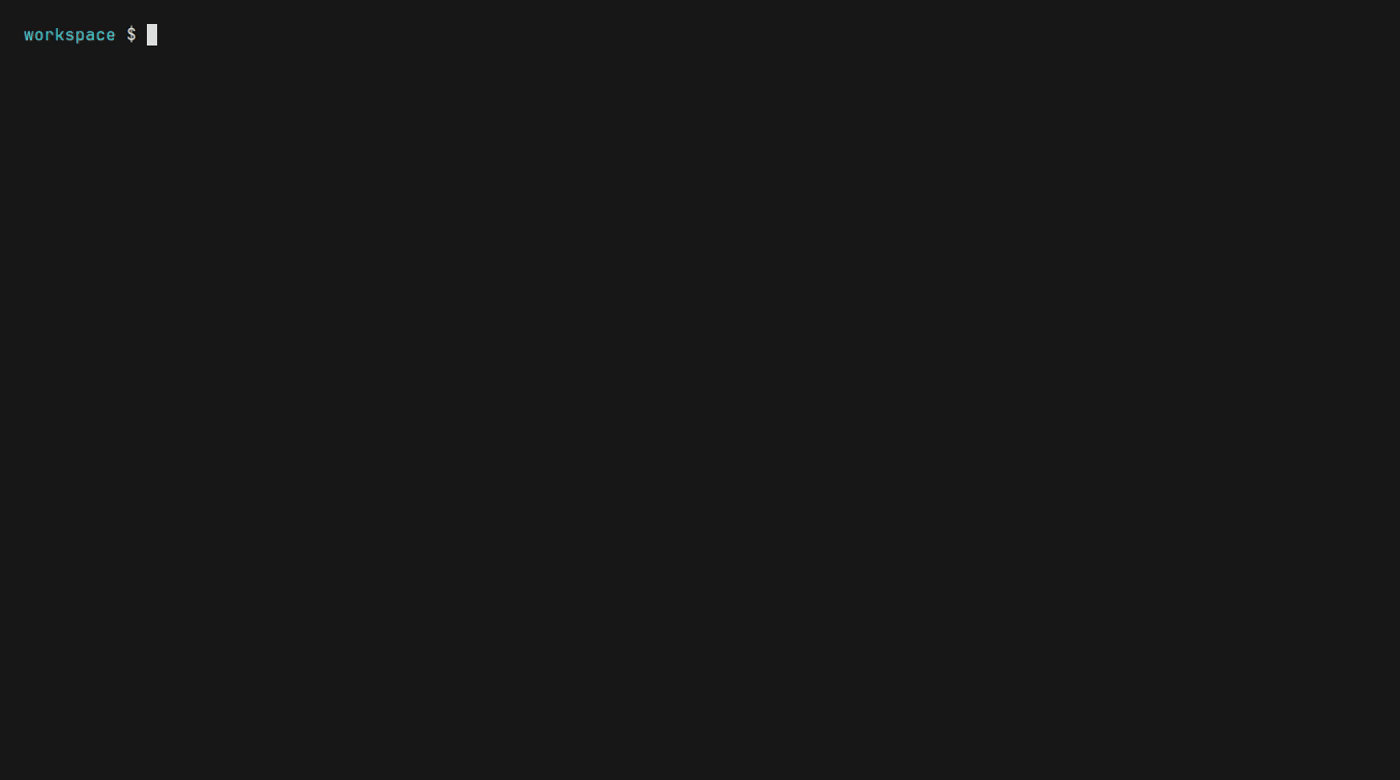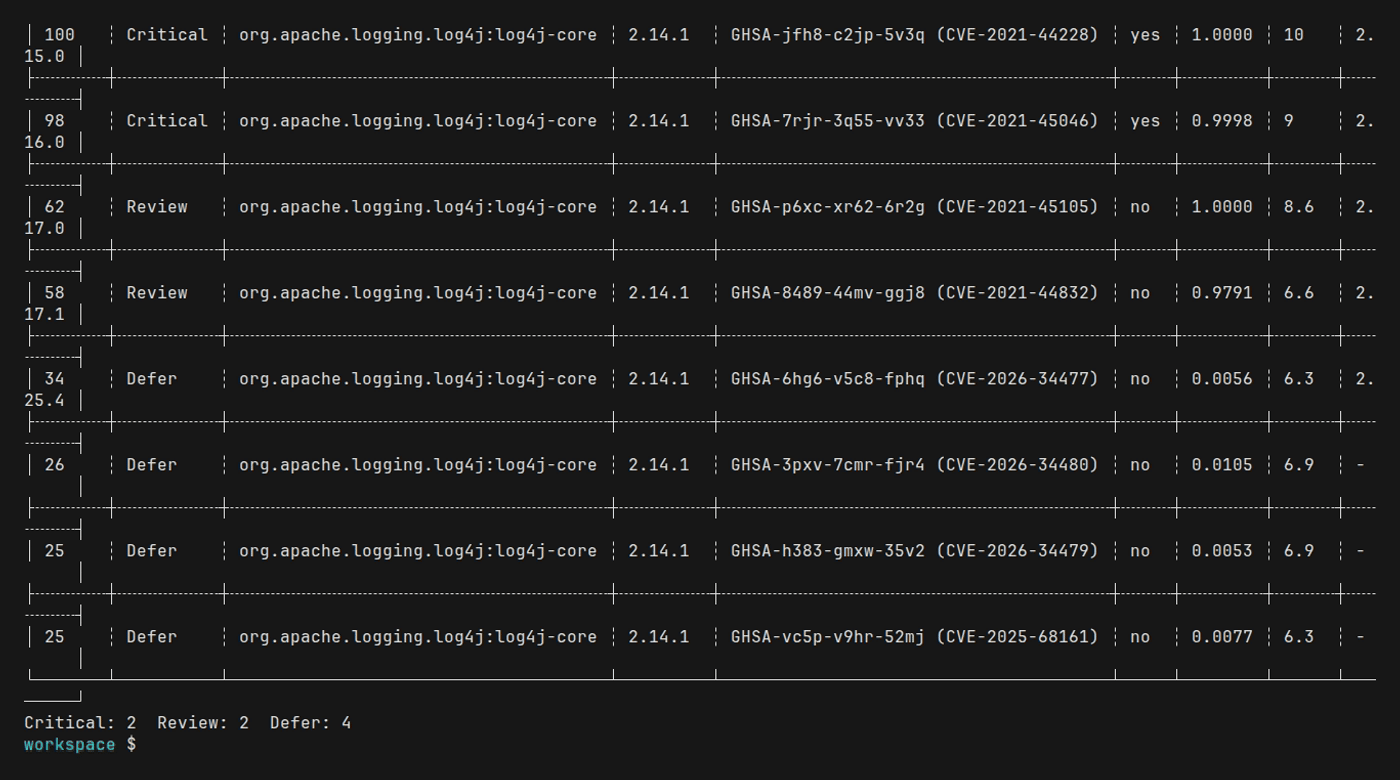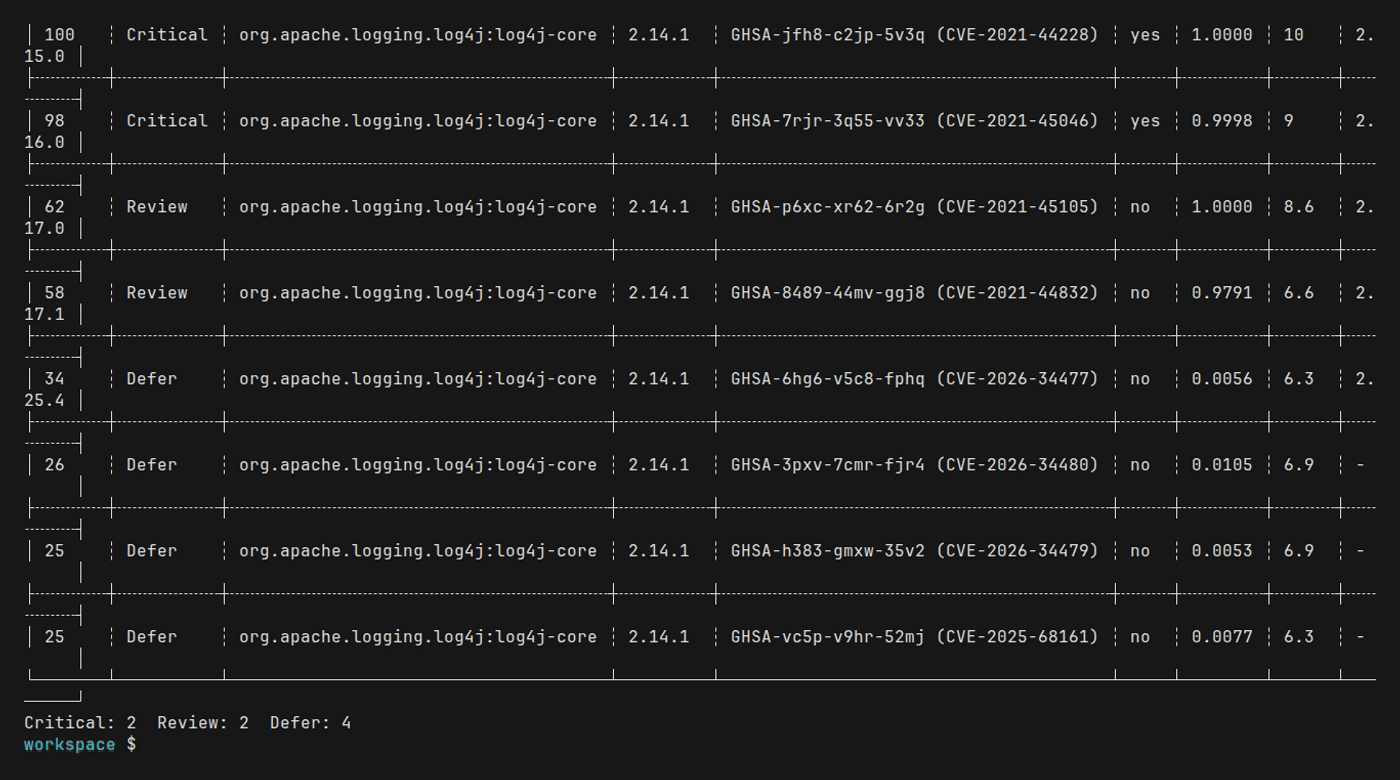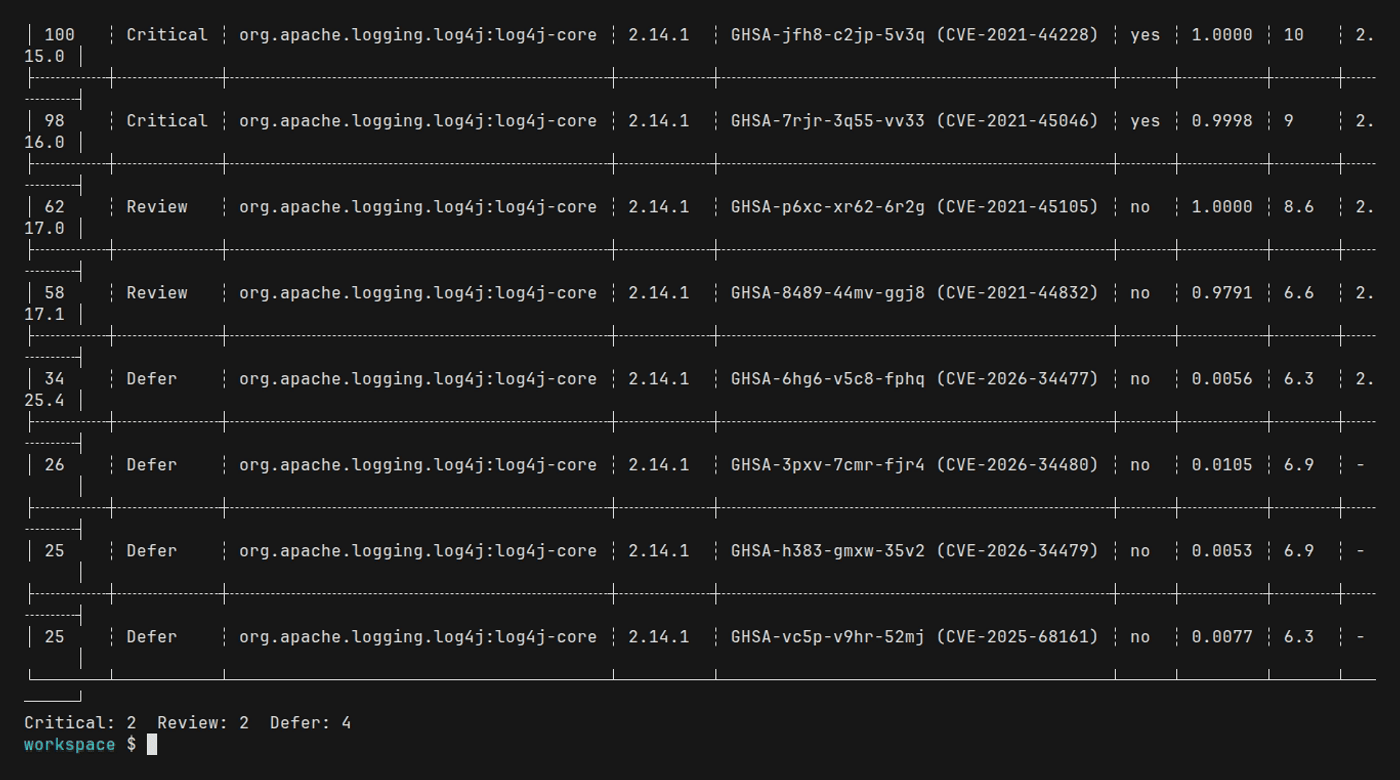
PatchSense reads your lockfiles, looks up every pinned package in [OSV](https://osv.dev), and ranks each advisory from 0 to 100 using CISA KEV (known exploited), FIRST EPSS (exploit probability), CVSS, whether the package is a direct dependency, and whether a fix exists. Instead of a flat list of CVEs you get three tiers, **Critical**, **Review**, and **Defer**, so you know what to patch first. It runs locally, caches data in SQLite, works offline from that cache, writes table, JSON, SARIF, Markdown, and GitLab reports, can post a pull-request or merge-request comment, and ships an MCP server for coding agents.
|
|
25
|
+
|
|
26
|
+
|
|
27
|
+
|
|
28
|
+
## Install
|
|
29
|
+
|
|
30
|
+
### cargo (available now)
|
|
31
|
+
|
|
32
|
+
```bash
|
|
33
|
+
cargo install patchsense --locked
|
|
34
|
+
```
|
|
35
|
+
|
|
36
|
+
This installs the latest `patchsense` release from crates.io. It needs Rust 1.99 or newer (`rust-version` in `Cargo.toml`).
|
|
37
|
+
|
|
38
|
+
From a checkout of this repository:
|
|
39
|
+
|
|
40
|
+
```bash
|
|
41
|
+
cargo build --release -p patchsense
|
|
42
|
+
cargo run -p patchsense -- --version
|
|
43
|
+
```
|
|
44
|
+
|
|
45
|
+
### Prebuilt binaries
|
|
46
|
+
|
|
47
|
+
npm, PyPI, Composer, Go, Homebrew, the shell installer, and Docker install a prebuilt binary from GitHub Release [`v0.1.2`](https://github.com/Widyasa/patchsense/releases/tag/v0.1.2). The npm, PyPI, and Composer commands work once the package is live on that registry.
|
|
48
|
+
|
|
49
|
+
| Channel | Command | Notes |
|
|
50
|
+
|---|---|---|
|
|
51
|
+
| npm | `npm install --save-dev patchsense`, then `npx patchsense scan .` | cargo-dist package, created when the GitHub Release is published. Also `pnpm add -D patchsense && pnpm exec patchsense scan .` and `yarn add -D patchsense && yarn patchsense scan .` |
|
|
52
|
+
| PyPI | `pip install patchsense`, `pipx install patchsense`, or `uv tool install patchsense` | Wheels from [`.github/workflows/pypi.yml`](.github/workflows/pypi.yml): Linux x64 and arm64 (manylinux, glibc), macOS x64 and arm64, Windows x64. Not Alpine. The wheel does not download a GitHub Release |
|
|
53
|
+
| Composer | `composer require --dev widyasa/patchsense`, then `vendor/bin/patchsense scan .` | Root [`composer.json`](composer.json). The first run downloads the release archive and checks sha256 |
|
|
54
|
+
| Go | `go install github.com/Widyasa/patchsense/go/cmd/patchsense@v0.1.2` | [`go/cmd/patchsense`](go/cmd/patchsense) downloads the same archive and checks sha256 |
|
|
55
|
+
| Homebrew | `brew install Widyasa/tap/patchsense` | Formula in [`Widyasa/homebrew-tap`](https://github.com/Widyasa/homebrew-tap) |
|
|
56
|
+
| shell | `curl --proto '=https' --tlsv1.2 -fsSL https://github.com/Widyasa/patchsense/releases/download/v0.1.2/patchsense-installer.sh \| sh` | cargo-dist installer. Checks sha256 before unpacking. Windows: `patchsense-installer.ps1` |
|
|
57
|
+
| Docker | `docker build -t patchsense .`, then `docker run --rm -v "$PWD:/work" -w /work patchsense scan .` | Local image only ([`Dockerfile`](Dockerfile)). Alpine x64, so [`scripts/fetch-release.sh`](scripts/fetch-release.sh) downloads the musl archive. The image is not pushed to a registry |
|
|
58
|
+
|
|
59
|
+
The release archives cover `x86_64-unknown-linux-gnu`, `x86_64-unknown-linux-musl`, `aarch64-unknown-linux-gnu`, `x86_64-apple-darwin`, `aarch64-apple-darwin`, and `x86_64-pc-windows-msvc`. There is no Linux arm64 musl archive and no Windows arm64 archive.
|
|
60
|
+
|
|
61
|
+
Composer, Go, and the Docker entrypoint cache the downloaded binary under `~/.cache/patchsense` (`PATCHSENSE_CACHE_DIR` overrides that directory). `PATCHSENSE_BINARY` points them at a binary you already built and skips the download. `PATCHSENSE_TARGET` overrides target detection. The PyPI wheel and the cargo-dist npm package do not read `PATCHSENSE_BINARY`.
|
|
62
|
+
|
|
63
|
+
Archives are `patchsense-<target>.tar.gz` (Windows included) and are listed with their sha256 in the release `dist-manifest.json` and `sha256.sum`.
|
|
64
|
+
|
|
65
|
+
## Quick start
|
|
66
|
+
|
|
67
|
+
```bash
|
|
68
|
+
patchsense scan . # scan every lockfile under the current directory
|
|
69
|
+
patchsense scan . --fail-on review # exit 1 if any finding is Review or Critical
|
|
70
|
+
patchsense scan . -f json -o report.json # save a JSON report
|
|
71
|
+
patchsense init # write an example patchsense.toml
|
|
72
|
+
patchsense scan . --offline # rescan from the local cache, no network
|
|
73
|
+
```
|
|
74
|
+
|
|
75
|
+
Example output:
|
|
76
|
+
|
|
77
|
+
```text
|
|
78
|
+
┌───────┬──────────┬─────────────────────────────────────┬─────────┬──────────────────────────────────────┬─────┬────────────────────────────┬──────┬────────┐
|
|
79
|
+
│ Score ┆ Tier ┆ Package ┆ Version ┆ Advisory/CVE ┆ KEV ┆ EPSS ┆ CVSS ┆ Fix │
|
|
80
|
+
╞═══════╪══════════╪═════════════════════════════════════╪═════════╪══════════════════════════════════════╪═════╪════════════════════════════╪══════╪════════╡
|
|
81
|
+
│ 100 ┆ Critical ┆ org.apache.logging.log4j:log4j-core ┆ 2.14.1 ┆ GHSA-jfh8-c2jp-5v3q (CVE-2021-44228) ┆ yes ┆ 1.0000 (percentile 1.0000) ┆ 10 ┆ 2.15.0 │
|
|
82
|
+
│ 62 ┆ Review ┆ org.apache.logging.log4j:log4j-core ┆ 2.14.1 ┆ GHSA-p6xc-xr62-6r2g (CVE-2021-45105) ┆ no ┆ 1.0000 (percentile 0.9999) ┆ 8.6 ┆ 2.17.0 │
|
|
83
|
+
│ 34 ┆ Defer ┆ org.apache.logging.log4j:log4j-core ┆ 2.14.1 ┆ GHSA-6hg6-v5c8-fphq (CVE-2026-34477) ┆ no ┆ 0.0056 (percentile 0.4647) ┆ 6.3 ┆ 2.25.4 │
|
|
84
|
+
└───────┴──────────┴─────────────────────────────────────┴─────────┴──────────────────────────────────────┴─────┴────────────────────────────┴──────┴────────┘
|
|
85
|
+
Critical: 2 Review: 2 Defer: 4
|
|
86
|
+
```
|
|
87
|
+
|
|
88
|
+
## Command reference
|
|
89
|
+
|
|
90
|
+
```text
|
|
91
|
+
patchsense <COMMAND>
|
|
92
|
+
|
|
93
|
+
scan Scan lockfiles and print matching advisories
|
|
94
|
+
cache Inspect or delete the local SQLite cache
|
|
95
|
+
init Write an example config, agent instructions, or MCP snippets
|
|
96
|
+
comment Create or update a pull-request comment from a JSON report
|
|
97
|
+
mcp Run the MCP server on stdio
|
|
98
|
+
help Print help for a subcommand
|
|
99
|
+
|
|
100
|
+
-h, --help Print help
|
|
101
|
+
-V, --version Print version
|
|
102
|
+
```
|
|
103
|
+
|
|
104
|
+
### `patchsense scan [OPTIONS] [PATH]`
|
|
105
|
+
|
|
106
|
+
`PATH` is a directory or a single lockfile. Default: the current directory.
|
|
107
|
+
|
|
108
|
+
| Option | Description |
|
|
109
|
+
|---|---|
|
|
110
|
+
| `--ecosystem <LIST>` | Ecosystems to scan, comma-separated (`npm,pypi`). Repeatable. Names: `npm`, `pypi`, `packagist` (or `composer`), `go`, `maven`, `cargo` (or `crates.io`). |
|
|
111
|
+
| `--no-dev` | Skip packages the parser marked as dev dependencies. |
|
|
112
|
+
| `--exclude <GLOB>` | Extra paths to skip. Repeatable. Added to `[scan] exclude`. |
|
|
113
|
+
| `--keep-going` | Continue after a lockfile fails to parse. This is the default. |
|
|
114
|
+
| `--no-keep-going` | Stop at the first lockfile that cannot be read or parsed. |
|
|
115
|
+
| `--fail-on <WHEN>` | Exit 1 when a finding reaches this bar: `critical` (default), `review`, `any`, `never`, or a score `0`–`100`. |
|
|
116
|
+
| `--min-score <N>` | Hide findings below this score in every output. Does not change the exit code. |
|
|
117
|
+
| `-f, --format <FORMAT>` | `table`, `json`, `sarif`, `markdown`, or `gitlab`. Repeatable, paired with `--output` in order. |
|
|
118
|
+
| `-o, --output <FILE>` | Write the paired `--format` to this file instead of stdout. Repeatable. Parent directories are created. |
|
|
119
|
+
| `--no-color` | Plain table. `NO_COLOR` is also honored. |
|
|
120
|
+
| `--offline` | Use only the local cache. No network calls. |
|
|
121
|
+
| `--strict-cache` | With `--offline`, exit 2 when an EPSS row or the KEV catalog is missing or past its TTL. |
|
|
122
|
+
| `--no-cache` | Do not read or write the cache. |
|
|
123
|
+
| `--cache-dir <DIR>` | Directory containing `cache.db`. Overrides `PATCHSENSE_CACHE_DIR`. |
|
|
124
|
+
| `--config <FILE>` | Path to `patchsense.toml`. Overrides discovery and `PATCHSENSE_CONFIG`. |
|
|
125
|
+
| `--explain` | Ask a local coding agent CLI to explain the top findings. |
|
|
126
|
+
| `--agent <AGENT>` | Agent for `--explain`: `auto`, `codex`, `claude`, or `cursor`. |
|
|
127
|
+
| `--explain-top <N>` | Number of findings sent to the agent. Default from `[explain] top` (10). |
|
|
128
|
+
|
|
129
|
+
Writing several reports in one run:
|
|
130
|
+
|
|
131
|
+
```bash
|
|
132
|
+
patchsense scan . --no-color \
|
|
133
|
+
--format json --output patchsense-report.json \
|
|
134
|
+
--format sarif --output patchsense.sarif \
|
|
135
|
+
--format markdown --output patchsense-report.md
|
|
136
|
+
```
|
|
137
|
+
|
|
138
|
+
Rules for pairing: the n-th `--format` goes to the n-th `--output`. At most one format may be left without an `--output` (it goes to stdout). More `--output` values than `--format` values is an error.
|
|
139
|
+
|
|
140
|
+
### `patchsense cache [--cache-dir <DIR>] <info|clear>`
|
|
141
|
+
|
|
142
|
+
| Command | Description |
|
|
143
|
+
|---|---|
|
|
144
|
+
| `cache info` | Print the cache path, schema version, and row counts (`osv_vuln`, `osv_query`, `epss`, `kev`). |
|
|
145
|
+
| `cache clear` | Delete `cache.db`. |
|
|
146
|
+
|
|
147
|
+
`--cache-dir` works before or after the subcommand (`cache info --cache-dir DIR` or `cache --cache-dir DIR info`).
|
|
148
|
+
|
|
149
|
+
### `patchsense init [OPTIONS]`
|
|
150
|
+
|
|
151
|
+
| Option | Description |
|
|
152
|
+
|---|---|
|
|
153
|
+
| *(none)* | Write an example `patchsense.toml` in the current directory. An existing file is kept. |
|
|
154
|
+
| `--force` | Replace an existing `patchsense.toml`. |
|
|
155
|
+
| `--agent [<AGENT>]` | Also write a PatchSense instruction block for `all` (default when no value), `codex` (`AGENTS.md`), `claude` (`CLAUDE.md`), or `cursor` (`.cursor/rules/patchsense.mdc`). The block sits between `<!-- patchsense:start -->` and `<!-- patchsense:end -->` and is updated in place on rerun. |
|
|
156
|
+
| `--print-mcp-config` | Print MCP config snippets for Cursor, Claude Code, and Codex. Writes no files and no `patchsense.toml`. |
|
|
157
|
+
|
|
158
|
+
### `patchsense comment --report <FILE> [OPTIONS]`
|
|
159
|
+
|
|
160
|
+
Posts the Markdown summary of a JSON report as a pull-request comment (GitHub) or merge-request note (GitLab). A hidden `<!-- patchsense-report -->` marker means later runs edit the same comment instead of adding a new one.
|
|
161
|
+
|
|
162
|
+
| Option | Description |
|
|
163
|
+
|---|---|
|
|
164
|
+
| `--report <FILE>` | JSON report from `patchsense scan --format json`. Required. |
|
|
165
|
+
| `--provider <PROVIDER>` | `auto` (default), `github`, or `gitlab`. `auto` picks GitHub when `GITHUB_ACTIONS=true`, GitLab when `GITLAB_CI=true`. |
|
|
166
|
+
| `--top <N>` | Findings in the comment table. Default 20. |
|
|
167
|
+
| `--dry-run` | Print the Markdown and do not call any API. |
|
|
168
|
+
|
|
169
|
+
Environment it reads:
|
|
170
|
+
|
|
171
|
+
- GitHub: `GITHUB_TOKEN` with `pull-requests: write`, `GITHUB_REPOSITORY`, `GITHUB_EVENT_PATH`, optional `GITHUB_API_URL`. The comment is a pull-request conversation comment: `GET` and `POST /repos/{owner}/{repo}/issues/{pull_number}/comments`, and `PATCH /repos/{owner}/{repo}/issues/comments/{comment_id}`. On a pull request, `pull-requests: write` authorizes those calls. `issues: write` is not required.
|
|
172
|
+
- GitLab: `GITLAB_TOKEN` (project access token with `api` scope; `CI_JOB_TOKEN` cannot write notes), `CI_API_V4_URL`, `CI_PROJECT_ID`, `CI_MERGE_REQUEST_IID`.
|
|
173
|
+
|
|
174
|
+
### `patchsense mcp`
|
|
175
|
+
|
|
176
|
+
Runs a Model Context Protocol server on stdio. Tools:
|
|
177
|
+
|
|
178
|
+
| Tool | Parameters | Returns |
|
|
179
|
+
|---|---|---|
|
|
180
|
+
| `list_supported_lockfiles` | none | Lockfile names and their OSV ecosystems |
|
|
181
|
+
| `scan_project` | `path`, `ecosystems`, `min_score`, `include_dev`, `offline` | Top 50 findings plus the full summary |
|
|
182
|
+
| `get_finding` | `id` (GHSA, CVE, or OSV id), `path` | One advisory |
|
|
183
|
+
| `get_fix_plan` | `path`, `tier` (`critical`, `review`, `defer`) | Minimum upgrade covering every advisory on a package |
|
|
184
|
+
| `explain_score` | `id`, `path` | Deterministic score breakdown (no AI call) |
|
|
185
|
+
|
|
186
|
+
`patchsense init --print-mcp-config` prints ready-to-paste snippets, for example Cursor's `.cursor/mcp.json`:
|
|
187
|
+
|
|
188
|
+
```json
|
|
189
|
+
{
|
|
190
|
+
"mcpServers": {
|
|
191
|
+
"patchsense": { "command": "patchsense", "args": ["mcp"] }
|
|
192
|
+
}
|
|
193
|
+
}
|
|
194
|
+
```
|
|
195
|
+
|
|
196
|
+
Claude Code: `claude mcp add --transport stdio patchsense -- patchsense mcp`
|
|
197
|
+
|
|
198
|
+
## How the score works
|
|
199
|
+
|
|
200
|
+
Each finding gets 0–100 points:
|
|
201
|
+
|
|
202
|
+
| Signal | Default weight | Meaning |
|
|
203
|
+
|---|---:|---|
|
|
204
|
+
| KEV | 35 | CVE is in the CISA Known Exploited Vulnerabilities catalog |
|
|
205
|
+
| EPSS | 25 | FIRST exploit probability; full weight at probability 0.10 (`probability` mode) |
|
|
206
|
+
| CVSS | 20 | Highest usable CVSS base score / 10 |
|
|
207
|
+
| Direct | 10 | Package is a direct dependency |
|
|
208
|
+
| Fix available | 10 | OSV lists a fixed version |
|
|
209
|
+
|
|
210
|
+
Tiers: **Critical** ≥ 70, **Review** ≥ 40, otherwise **Defer**. Weights that do not sum to 100 are scaled to 100, with a warning. All of this is configurable.
|
|
211
|
+
|
|
212
|
+
## Configuration
|
|
213
|
+
|
|
214
|
+
PatchSense looks for `patchsense.toml` starting at the scan directory and walking up to the git root. `--config` or `PATCHSENSE_CONFIG` points at a specific file. Precedence: **flag > environment variable > file > built-in default**. Unknown keys are rejected. Every key is optional; this is the full file with defaults:
|
|
215
|
+
|
|
216
|
+
```toml
|
|
217
|
+
schema_version = 1 # only 1 is accepted
|
|
218
|
+
|
|
219
|
+
[scan]
|
|
220
|
+
ecosystems = ["npm", "pypi", "packagist", "go", "maven", "cargo"] # default: all
|
|
221
|
+
exclude = [] # extra glob patterns to skip
|
|
222
|
+
include_dev = true # false = same as --no-dev
|
|
223
|
+
fail_on = "critical" # critical | review | any | never | 0-100
|
|
224
|
+
|
|
225
|
+
[scan.go_imports] # Go import check, see below
|
|
226
|
+
skip_vendor = true # skip directories named vendor
|
|
227
|
+
skip_testdata = true # skip directories named testdata
|
|
228
|
+
skip_tests = true # skip *_test.go
|
|
229
|
+
|
|
230
|
+
[score.weights]
|
|
231
|
+
kev = 35
|
|
232
|
+
epss = 25
|
|
233
|
+
cvss = 20
|
|
234
|
+
direct = 10
|
|
235
|
+
fix_available = 10
|
|
236
|
+
|
|
237
|
+
[score.epss]
|
|
238
|
+
mode = "probability" # probability | percentile
|
|
239
|
+
saturation = 0.10 # probability that earns the full EPSS weight
|
|
240
|
+
|
|
241
|
+
[score.thresholds]
|
|
242
|
+
critical = 70
|
|
243
|
+
review = 40
|
|
244
|
+
|
|
245
|
+
[score.unknown_direct]
|
|
246
|
+
weight_fraction = 1.0 # share of the direct weight when the parser cannot tell
|
|
247
|
+
|
|
248
|
+
[cache]
|
|
249
|
+
ttl_hours_osv = 24 # whole hours
|
|
250
|
+
ttl_hours_epss = 24
|
|
251
|
+
ttl_hours_kev = 24
|
|
252
|
+
strict_cache = false # true = --strict-cache
|
|
253
|
+
|
|
254
|
+
[output]
|
|
255
|
+
top = 20 # rows in the Markdown report
|
|
256
|
+
|
|
257
|
+
[explain]
|
|
258
|
+
agent = "auto" # auto | codex | claude | cursor
|
|
259
|
+
top = 10 # findings sent to the agent
|
|
260
|
+
timeout_secs = 120
|
|
261
|
+
|
|
262
|
+
# Suppress an advisory. Repeat the table for more rules.
|
|
263
|
+
[[ignore]]
|
|
264
|
+
id = "GHSA-xxxx-xxxx-xxxx" # OSV, GHSA, or CVE id (aliases match too)
|
|
265
|
+
reason = "Used only in a build script" # required
|
|
266
|
+
expires = "2027-01-31" # optional, inclusive YYYY-MM-DD
|
|
267
|
+
```
|
|
268
|
+
|
|
269
|
+
Ignored findings are listed under `ignored` in the JSON report. An expired rule is dropped with a warning. `[explain] lang` from older configs is accepted but ignored (output is English only).
|
|
270
|
+
|
|
271
|
+
### Environment variables
|
|
272
|
+
|
|
273
|
+
| Variable | Effect |
|
|
274
|
+
|---|---|
|
|
275
|
+
| `PATCHSENSE_CONFIG` | Config file path (overridden by `--config`) |
|
|
276
|
+
| `PATCHSENSE_CACHE_DIR` | Cache directory (overridden by `--cache-dir`) |
|
|
277
|
+
| `PATCHSENSE_FAIL_ON` | Same values as `--fail-on` |
|
|
278
|
+
| `PATCHSENSE_AGENT` | Same values as `--agent` |
|
|
279
|
+
| `PATCHSENSE_OSV_URL` | OSV API base URL (default `https://api.osv.dev`) |
|
|
280
|
+
| `PATCHSENSE_EPSS_URL` | EPSS API base URL (default `https://api.first.org`) |
|
|
281
|
+
| `PATCHSENSE_KEV_URL` | Full URL of the CISA KEV JSON feed |
|
|
282
|
+
| `NO_COLOR` | Disable table colors |
|
|
283
|
+
|
|
284
|
+
## Output formats
|
|
285
|
+
|
|
286
|
+
| Format | Use |
|
|
287
|
+
|---|---|
|
|
288
|
+
| `table` | Human-readable priority table. Default when stdout is a terminal. |
|
|
289
|
+
| `json` | Full report (`schema_version`, `tool`, `target`, `lockfiles`, `data_sources`, `summary`, `findings`, `ignored`, `warnings`, …). Default when stdout is a pipe or file. Schema: [`schemas/report.v1.json`](schemas/report.v1.json). |
|
|
290
|
+
| `sarif` | SARIF 2.1.0 for GitHub code scanning and other SARIF viewers. |
|
|
291
|
+
| `markdown` | Summary and findings table with per-finding details. This is the PR/MR comment body. |
|
|
292
|
+
| `gitlab` | GitLab Dependency Scanning report (schema 15.2.5). |
|
|
293
|
+
|
|
294
|
+
Warnings (stale cache, parse failures, unsupported lockfiles) go to stderr and are also stored in the JSON and Markdown reports.
|
|
295
|
+
|
|
296
|
+
## Exit codes
|
|
297
|
+
|
|
298
|
+
| Code | Meaning |
|
|
299
|
+
|---|---|
|
|
300
|
+
| `0` | Scan finished and no finding reached the `--fail-on` bar |
|
|
301
|
+
| `1` | At least one finding reached the `--fail-on` bar |
|
|
302
|
+
| `2` | The scan could not run: bad config or flag value, no supported lockfile, unreadable input, every lockfile failed, offline OSV cache missing or expired, `--strict-cache` with missing or expired EPSS/KEV, or a `comment` API error |
|
|
303
|
+
|
|
304
|
+
`--fail-on never` always exits 0 when the scan runs. `--min-score` never changes the exit code.
|
|
305
|
+
|
|
306
|
+
## Offline mode and cache
|
|
307
|
+
|
|
308
|
+
Data is cached in `cache.db`:
|
|
309
|
+
|
|
310
|
+
| OS | Default location |
|
|
311
|
+
|---|---|
|
|
312
|
+
| Linux | `$XDG_CACHE_HOME/patchsense/` or `~/.cache/patchsense/` |
|
|
313
|
+
| macOS | `~/Library/Caches/patchsense/` (or `$XDG_CACHE_HOME/patchsense/` if set) |
|
|
314
|
+
| Windows | `%LOCALAPPDATA%\patchsense\` (or `$XDG_CACHE_HOME/patchsense/` if set) |
|
|
315
|
+
|
|
316
|
+
Online scans reuse rows younger than their TTL and refetch older ones. With `--offline`:
|
|
317
|
+
|
|
318
|
+
- **OSV** results must be in the cache and within `ttl_hours_osv`. A missing or expired row exits 2 and the error says which package and how old. No partial report is printed.
|
|
319
|
+
- **EPSS / KEV**: a missing row is a warning and that signal counts as absent. An expired row is still used, with a warning naming its age, so scores do not drop just because the cache aged.
|
|
320
|
+
- `--strict-cache` (or `[cache] strict_cache = true`) turns missing or expired EPSS/KEV into exit 2.
|
|
321
|
+
|
|
322
|
+
Typical CI pattern: run one online scan to warm the cache, then `--offline` for later runs.
|
|
323
|
+
|
|
324
|
+
```bash
|
|
325
|
+
patchsense scan . # fills the cache
|
|
326
|
+
patchsense scan . --offline # reuses it
|
|
327
|
+
patchsense cache info # see what is stored
|
|
328
|
+
```
|
|
329
|
+
|
|
330
|
+
## CI usage
|
|
331
|
+
|
|
332
|
+
Any CI that has Rust:
|
|
333
|
+
|
|
334
|
+
```bash
|
|
335
|
+
cargo install patchsense --locked
|
|
336
|
+
patchsense scan . --no-color --fail-on critical \
|
|
337
|
+
--format json --output patchsense-report.json \
|
|
338
|
+
--format sarif --output patchsense.sarif
|
|
339
|
+
```
|
|
340
|
+
|
|
341
|
+
GitHub Actions with a PR comment:
|
|
342
|
+
|
|
343
|
+
```yaml
|
|
344
|
+
permissions:
|
|
345
|
+
contents: read
|
|
346
|
+
pull-requests: write
|
|
347
|
+
|
|
348
|
+
jobs:
|
|
349
|
+
scan:
|
|
350
|
+
runs-on: ubuntu-latest
|
|
351
|
+
steps:
|
|
352
|
+
- uses: actions/checkout@v4
|
|
353
|
+
- uses: dtolnay/rust-toolchain@stable
|
|
354
|
+
- run: cargo install patchsense --locked
|
|
355
|
+
- run: patchsense scan . --no-color --format json --output patchsense-report.json
|
|
356
|
+
- if: always() && github.event_name == 'pull_request'
|
|
357
|
+
run: patchsense comment --report patchsense-report.json
|
|
358
|
+
env:
|
|
359
|
+
GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
|
|
360
|
+
```
|
|
361
|
+
|
|
362
|
+
`pull-requests: write` is the permission for that comment. `patchsense comment` writes a pull-request conversation comment through the issue-comment routes above, and GitHub authorizes those routes on a pull request with `pull-requests: write`. `issues: write` is not required.
|
|
363
|
+
|
|
364
|
+
The composite action in [`action.yml`](action.yml) downloads the GitHub Release installer by default (`uses: Widyasa/patchsense@v0`, or pin `version: 0.1.2`). To test an unreleased build instead, build the binary and pass `binary-path`, as [`.github/workflows/self-test.yml`](.github/workflows/self-test.yml) does. The job needs `pull-requests: write` when `comment` is left at its default (`true`), and `security-events: write` when `sarif` is left at its default (`true`):
|
|
365
|
+
|
|
366
|
+
```yaml
|
|
367
|
+
permissions:
|
|
368
|
+
contents: read
|
|
369
|
+
security-events: write
|
|
370
|
+
pull-requests: write
|
|
371
|
+
|
|
372
|
+
jobs:
|
|
373
|
+
patchsense:
|
|
374
|
+
runs-on: ubuntu-latest
|
|
375
|
+
steps:
|
|
376
|
+
- uses: actions/checkout@v4
|
|
377
|
+
- uses: dtolnay/rust-toolchain@stable
|
|
378
|
+
- run: cargo build --release -p patchsense --bin patchsense
|
|
379
|
+
- uses: ./
|
|
380
|
+
with:
|
|
381
|
+
path: .
|
|
382
|
+
fail-on: critical
|
|
383
|
+
binary-path: target/release/patchsense
|
|
384
|
+
```
|
|
385
|
+
|
|
386
|
+
On GitLab, run the same scan with `--format gitlab --output gl-dependency-scanning-report.json` and `patchsense comment --provider gitlab` with a masked `GITLAB_TOKEN`. [`templates/gitlab/patchsense.gitlab-ci.yml`](templates/gitlab/patchsense.gitlab-ci.yml) is the template. Its installer downloads `patchsense-installer.sh` from the GitHub Release (`latest`, or set `PATCHSENSE_VERSION`). Details are in [`docs/gitlab.md`](docs/gitlab.md).
|
|
387
|
+
|
|
388
|
+
## Supported ecosystems and lockfiles
|
|
389
|
+
|
|
390
|
+
| Ecosystem | Files |
|
|
391
|
+
|---|---|
|
|
392
|
+
| npm | `package-lock.json`, `pnpm-lock.yaml`, `yarn.lock` |
|
|
393
|
+
| PyPI | `poetry.lock`, `requirements.txt` |
|
|
394
|
+
| Packagist (PHP) | `composer.lock` |
|
|
395
|
+
| Go | `go.sum` |
|
|
396
|
+
| Maven | `pom.xml` |
|
|
397
|
+
| crates.io | `Cargo.lock` |
|
|
398
|
+
|
|
399
|
+
Details:
|
|
400
|
+
|
|
401
|
+
- Directories named `node_modules`, `vendor`, `target`, `.git`, `.venv`, and `venv` are skipped during discovery.
|
|
402
|
+
- **requirements**: discovery also picks up `requirements-*.txt`, `requirements_*.txt`, `*.requirements.txt`, and any `.txt` inside a `requirements/` directory (case-insensitive). `-r`/`--requirement` and `-c`/`--constraint` includes are followed relative to the including file. A cycle or missing include is a warning; remote includes are skipped with a warning.
|
|
403
|
+
- **Composer**: `platform` constraints such as `php: ^8.3` are skipped; a concrete version such as `php: 8.3.35` is scanned.
|
|
404
|
+
- **Go import check**: when an OSV advisory lists affected import paths, PatchSense checks `.go` files under the scan root. If none of those packages is imported, the finding stays (same score and tier) but gets the note `imported package not seen` (JSON field `import_note`). Subpackages, aliases, dot, and blank imports count. See [`docs/go-import-reachability.md`](docs/go-import-reachability.md).
|
|
405
|
+
- **Not supported**: `bun.lock` / `bun.lockb` (a warning is printed when one is found).
|
|
406
|
+
|
|
407
|
+
## `--explain` (optional AI summary)
|
|
408
|
+
|
|
409
|
+
`patchsense scan . --explain` sends the top findings to a local, read-only coding agent CLI found on `PATH`: `codex`, `claude`, or Cursor's `agent` / `cursor-agent`. With `auto` they are tried in that order. The text is labeled `AI explanation, may be wrong`. A missing agent, a timeout (`[explain] timeout_secs`), or a bad response is only a warning and never changes the exit code.
|
|
410
|
+
|
|
411
|
+
## Troubleshooting / FAQ
|
|
412
|
+
|
|
413
|
+
**`error: no supported lockfile found in .`** — Run from the project root, pass the lockfile path directly, or check that the file is not under a skipped directory or `--exclude` / `[scan] exclude`.
|
|
414
|
+
|
|
415
|
+
**`error: offline cache is missing OSV results …`** — Run one scan without `--offline` first, using the same `--cache-dir` (or `PATCHSENSE_CACHE_DIR`). `--offline` together with `--no-cache` can never succeed.
|
|
416
|
+
|
|
417
|
+
**`offline cache expired …`** — Rerun online, or raise `[cache] ttl_hours_osv`.
|
|
418
|
+
|
|
419
|
+
**`more than one --format would be written to stdout`** — Give every `--format` except one an `--output`.
|
|
420
|
+
|
|
421
|
+
**`failed to parse fail_on`** — Use `critical`, `review`, `any`, `never`, or an integer `0`–`100`.
|
|
422
|
+
|
|
423
|
+
**`unknown field` in the config** — Keys are strict; compare with the configuration reference above.
|
|
424
|
+
|
|
425
|
+
**`could not detect a comment provider`** — Outside GitHub Actions or GitLab CI, pass `--provider github` or `--provider gitlab`, or use `--dry-run` to preview.
|
|
426
|
+
|
|
427
|
+
**A Go finding says `imported package not seen`.** — Your code does not import the vulnerable package of that module. The finding is kept because tests, vendored code, and build tags are not fully analysed; verify before ignoring it with an `[[ignore]]` rule.
|
|
428
|
+
|
|
429
|
+
**Is my code uploaded anywhere?** — No. Only package names and versions are sent to OSV, and CVE ids to EPSS; the KEV catalog is downloaded as a whole. `--offline` makes no network calls.
|
|
430
|
+
|
|
431
|
+
## Links
|
|
432
|
+
|
|
433
|
+
- Changelog: [`CHANGELOG.md`](CHANGELOG.md)
|
|
434
|
+
- Known limitations: [`docs/limitations.md`](docs/limitations.md)
|
|
435
|
+
- Go import check: [`docs/go-import-reachability.md`](docs/go-import-reachability.md)
|
|
436
|
+
- GitLab CI: [`docs/gitlab.md`](docs/gitlab.md)
|
|
437
|
+
- Release checklist: [`docs/release-checklist.md`](docs/release-checklist.md)
|
|
438
|
+
- Contributing: [`CONTRIBUTING.md`](CONTRIBUTING.md)
|
|
439
|
+
- JSON schema: [`schemas/report.v1.json`](schemas/report.v1.json)
|
|
440
|
+
- Issues: <https://github.com/Widyasa/patchsense/issues>
|
|
441
|
+
- Library API docs: <https://docs.rs/patchsense>
|
|
442
|
+
|
|
443
|
+
## License
|
|
444
|
+
|
|
445
|
+
Licensed under either of [MIT](LICENSE-MIT) or [Apache-2.0](LICENSE-APACHE), at your option.
|
|
446
|
+
|
|
@@ -0,0 +1,7 @@
|
|
|
1
|
+
patchsense-0.1.2.data/scripts/patchsense.exe,sha256=80fsctuEBsey6TamnWCQNHq5AcDfqP8_ArWBvJYsB9s,13451264
|
|
2
|
+
patchsense-0.1.2.dist-info/METADATA,sha256=-V8L0JoNYvzlbSDjvAyWpF6Y9bTfkZtmDjDDWtCI0AY,25452
|
|
3
|
+
patchsense-0.1.2.dist-info/WHEEL,sha256=8Aej0W0a6Cz6apA3IzJrTnxLRVLAt-w0Oh8SA3Con_c,94
|
|
4
|
+
patchsense-0.1.2.dist-info/licenses/LICENSE-APACHE,sha256=z8d0m5b2O9McPEK1xHG_dWgUBT6EfBDz6wA0F7xSPTA,11358
|
|
5
|
+
patchsense-0.1.2.dist-info/licenses/LICENSE-MIT,sha256=IFEduqjKmxxZcUTwI0agjB5bbqL0JuNQ7lFG7JTRjoU,1067
|
|
6
|
+
patchsense-0.1.2.dist-info/sboms/patchsense.cyclonedx.json,sha256=yNWC-Mqkn-MRe90cntzy5J_T01RrDGifUaubL12Kpoo,238202
|
|
7
|
+
patchsense-0.1.2.dist-info/RECORD,,
|
|
@@ -0,0 +1,202 @@
|
|
|
1
|
+
|
|
2
|
+
Apache License
|
|
3
|
+
Version 2.0, January 2004
|
|
4
|
+
http://www.apache.org/licenses/
|
|
5
|
+
|
|
6
|
+
TERMS AND CONDITIONS FOR USE, REPRODUCTION, AND DISTRIBUTION
|
|
7
|
+
|
|
8
|
+
1. Definitions.
|
|
9
|
+
|
|
10
|
+
"License" shall mean the terms and conditions for use, reproduction,
|
|
11
|
+
and distribution as defined by Sections 1 through 9 of this document.
|
|
12
|
+
|
|
13
|
+
"Licensor" shall mean the copyright owner or entity authorized by
|
|
14
|
+
the copyright owner that is granting the License.
|
|
15
|
+
|
|
16
|
+
"Legal Entity" shall mean the union of the acting entity and all
|
|
17
|
+
other entities that control, are controlled by, or are under common
|
|
18
|
+
control with that entity. For the purposes of this definition,
|
|
19
|
+
"control" means (i) the power, direct or indirect, to cause the
|
|
20
|
+
direction or management of such entity, whether by contract or
|
|
21
|
+
otherwise, or (ii) ownership of fifty percent (50%) or more of the
|
|
22
|
+
outstanding shares, or (iii) beneficial ownership of such entity.
|
|
23
|
+
|
|
24
|
+
"You" (or "Your") shall mean an individual or Legal Entity
|
|
25
|
+
exercising permissions granted by this License.
|
|
26
|
+
|
|
27
|
+
"Source" form shall mean the preferred form for making modifications,
|
|
28
|
+
including but not limited to software source code, documentation
|
|
29
|
+
source, and configuration files.
|
|
30
|
+
|
|
31
|
+
"Object" form shall mean any form resulting from mechanical
|
|
32
|
+
transformation or translation of a Source form, including but
|
|
33
|
+
not limited to compiled object code, generated documentation,
|
|
34
|
+
and conversions to other media types.
|
|
35
|
+
|
|
36
|
+
"Work" shall mean the work of authorship, whether in Source or
|
|
37
|
+
Object form, made available under the License, as indicated by a
|
|
38
|
+
copyright notice that is included in or attached to the work
|
|
39
|
+
(an example is provided in the Appendix below).
|
|
40
|
+
|
|
41
|
+
"Derivative Works" shall mean any work, whether in Source or Object
|
|
42
|
+
form, that is based on (or derived from) the Work and for which the
|
|
43
|
+
editorial revisions, annotations, elaborations, or other modifications
|
|
44
|
+
represent, as a whole, an original work of authorship. For the purposes
|
|
45
|
+
of this License, Derivative Works shall not include works that remain
|
|
46
|
+
separable from, or merely link (or bind by name) to the interfaces of,
|
|
47
|
+
the Work and Derivative Works thereof.
|
|
48
|
+
|
|
49
|
+
"Contribution" shall mean any work of authorship, including
|
|
50
|
+
the original version of the Work and any modifications or additions
|
|
51
|
+
to that Work or Derivative Works thereof, that is intentionally
|
|
52
|
+
submitted to Licensor for inclusion in the Work by the copyright owner
|
|
53
|
+
or by an individual or Legal Entity authorized to submit on behalf of
|
|
54
|
+
the copyright owner. For the purposes of this definition, "submitted"
|
|
55
|
+
means any form of electronic, verbal, or written communication sent
|
|
56
|
+
to the Licensor or its representatives, including but not limited to
|
|
57
|
+
communication on electronic mailing lists, source code control systems,
|
|
58
|
+
and issue tracking systems that are managed by, or on behalf of, the
|
|
59
|
+
Licensor for the purpose of discussing and improving the Work, but
|
|
60
|
+
excluding communication that is conspicuously marked or otherwise
|
|
61
|
+
designated in writing by the copyright owner as "Not a Contribution."
|
|
62
|
+
|
|
63
|
+
"Contributor" shall mean Licensor and any individual or Legal Entity
|
|
64
|
+
on behalf of whom a Contribution has been received by Licensor and
|
|
65
|
+
subsequently incorporated within the Work.
|
|
66
|
+
|
|
67
|
+
2. Grant of Copyright License. Subject to the terms and conditions of
|
|
68
|
+
this License, each Contributor hereby grants to You a perpetual,
|
|
69
|
+
worldwide, non-exclusive, no-charge, royalty-free, irrevocable
|
|
70
|
+
copyright license to reproduce, prepare Derivative Works of,
|
|
71
|
+
publicly display, publicly perform, sublicense, and distribute the
|
|
72
|
+
Work and such Derivative Works in Source or Object form.
|
|
73
|
+
|
|
74
|
+
3. Grant of Patent License. Subject to the terms and conditions of
|
|
75
|
+
this License, each Contributor hereby grants to You a perpetual,
|
|
76
|
+
worldwide, non-exclusive, no-charge, royalty-free, irrevocable
|
|
77
|
+
(except as stated in this section) patent license to make, have made,
|
|
78
|
+
use, offer to sell, sell, import, and otherwise transfer the Work,
|
|
79
|
+
where such license applies only to those patent claims licensable
|
|
80
|
+
by such Contributor that are necessarily infringed by their
|
|
81
|
+
Contribution(s) alone or by combination of their Contribution(s)
|
|
82
|
+
with the Work to which such Contribution(s) was submitted. If You
|
|
83
|
+
institute patent litigation against any entity (including a
|
|
84
|
+
cross-claim or counterclaim in a lawsuit) alleging that the Work
|
|
85
|
+
or a Contribution incorporated within the Work constitutes direct
|
|
86
|
+
or contributory patent infringement, then any patent licenses
|
|
87
|
+
granted to You under this License for that Work shall terminate
|
|
88
|
+
as of the date such litigation is filed.
|
|
89
|
+
|
|
90
|
+
4. Redistribution. You may reproduce and distribute copies of the
|
|
91
|
+
Work or Derivative Works thereof in any medium, with or without
|
|
92
|
+
modifications, and in Source or Object form, provided that You
|
|
93
|
+
meet the following conditions:
|
|
94
|
+
|
|
95
|
+
(a) You must give any other recipients of the Work or
|
|
96
|
+
Derivative Works a copy of this License; and
|
|
97
|
+
|
|
98
|
+
(b) You must cause any modified files to carry prominent notices
|
|
99
|
+
stating that You changed the files; and
|
|
100
|
+
|
|
101
|
+
(c) You must retain, in the Source form of any Derivative Works
|
|
102
|
+
that You distribute, all copyright, patent, trademark, and
|
|
103
|
+
attribution notices from the Source form of the Work,
|
|
104
|
+
excluding those notices that do not pertain to any part of
|
|
105
|
+
the Derivative Works; and
|
|
106
|
+
|
|
107
|
+
(d) If the Work includes a "NOTICE" text file as part of its
|
|
108
|
+
distribution, then any Derivative Works that You distribute must
|
|
109
|
+
include a readable copy of the attribution notices contained
|
|
110
|
+
within such NOTICE file, excluding those notices that do not
|
|
111
|
+
pertain to any part of the Derivative Works, in at least one
|
|
112
|
+
of the following places: within a NOTICE text file distributed
|
|
113
|
+
as part of the Derivative Works; within the Source form or
|
|
114
|
+
documentation, if provided along with the Derivative Works; or,
|
|
115
|
+
within a display generated by the Derivative Works, if and
|
|
116
|
+
wherever such third-party notices normally appear. The contents
|
|
117
|
+
of the NOTICE file are for informational purposes only and
|
|
118
|
+
do not modify the License. You may add Your own attribution
|
|
119
|
+
notices within Derivative Works that You distribute, alongside
|
|
120
|
+
or as an addendum to the NOTICE text from the Work, provided
|
|
121
|
+
that such additional attribution notices cannot be construed
|
|
122
|
+
as modifying the License.
|
|
123
|
+
|
|
124
|
+
You may add Your own copyright statement to Your modifications and
|
|
125
|
+
may provide additional or different license terms and conditions
|
|
126
|
+
for use, reproduction, or distribution of Your modifications, or
|
|
127
|
+
for any such Derivative Works as a whole, provided Your use,
|
|
128
|
+
reproduction, and distribution of the Work otherwise complies with
|
|
129
|
+
the conditions stated in this License.
|
|
130
|
+
|
|
131
|
+
5. Submission of Contributions. Unless You explicitly state otherwise,
|
|
132
|
+
any Contribution intentionally submitted for inclusion in the Work
|
|
133
|
+
by You to the Licensor shall be under the terms and conditions of
|
|
134
|
+
this License, without any additional terms or conditions.
|
|
135
|
+
Notwithstanding the above, nothing herein shall supersede or modify
|
|
136
|
+
the terms of any separate license agreement you may have executed
|
|
137
|
+
with Licensor regarding such Contributions.
|
|
138
|
+
|
|
139
|
+
6. Trademarks. This License does not grant permission to use the trade
|
|
140
|
+
names, trademarks, service marks, or product names of the Licensor,
|
|
141
|
+
except as required for reasonable and customary use in describing the
|
|
142
|
+
origin of the Work and reproducing the content of the NOTICE file.
|
|
143
|
+
|
|
144
|
+
7. Disclaimer of Warranty. Unless required by applicable law or
|
|
145
|
+
agreed to in writing, Licensor provides the Work (and each
|
|
146
|
+
Contributor provides its Contributions) on an "AS IS" BASIS,
|
|
147
|
+
WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or
|
|
148
|
+
implied, including, without limitation, any warranties or conditions
|
|
149
|
+
of TITLE, NON-INFRINGEMENT, MERCHANTABILITY, or FITNESS FOR A
|
|
150
|
+
PARTICULAR PURPOSE. You are solely responsible for determining the
|
|
151
|
+
appropriateness of using or redistributing the Work and assume any
|
|
152
|
+
risks associated with Your exercise of permissions under this License.
|
|
153
|
+
|
|
154
|
+
8. Limitation of Liability. In no event and under no legal theory,
|
|
155
|
+
whether in tort (including negligence), contract, or otherwise,
|
|
156
|
+
unless required by applicable law (such as deliberate and grossly
|
|
157
|
+
negligent acts) or agreed to in writing, shall any Contributor be
|
|
158
|
+
liable to You for damages, including any direct, indirect, special,
|
|
159
|
+
incidental, or consequential damages of any character arising as a
|
|
160
|
+
result of this License or out of the use or inability to use the
|
|
161
|
+
Work (including but not limited to damages for loss of goodwill,
|
|
162
|
+
work stoppage, computer failure or malfunction, or any and all
|
|
163
|
+
other commercial damages or losses), even if such Contributor
|
|
164
|
+
has been advised of the possibility of such damages.
|
|
165
|
+
|
|
166
|
+
9. Accepting Warranty or Additional Liability. While redistributing
|
|
167
|
+
the Work or Derivative Works thereof, You may choose to offer,
|
|
168
|
+
and charge a fee for, acceptance of support, warranty, indemnity,
|
|
169
|
+
or other liability obligations and/or rights consistent with this
|
|
170
|
+
License. However, in accepting such obligations, You may act only
|
|
171
|
+
on Your own behalf and on Your sole responsibility, not on behalf
|
|
172
|
+
of any other Contributor, and only if You agree to indemnify,
|
|
173
|
+
defend, and hold each Contributor harmless for any liability
|
|
174
|
+
incurred by, or claims asserted against, such Contributor by reason
|
|
175
|
+
of your accepting any such warranty or additional liability.
|
|
176
|
+
|
|
177
|
+
END OF TERMS AND CONDITIONS
|
|
178
|
+
|
|
179
|
+
APPENDIX: How to apply the Apache License to your work.
|
|
180
|
+
|
|
181
|
+
To apply the Apache License to your work, attach the following
|
|
182
|
+
boilerplate notice, with the fields enclosed by brackets "[]"
|
|
183
|
+
replaced with your own identifying information. (Don't include
|
|
184
|
+
the brackets!) The text should be enclosed in the appropriate
|
|
185
|
+
comment syntax for the file format. We also recommend that a
|
|
186
|
+
file or class name and description of purpose be included on the
|
|
187
|
+
same "printed page" as the copyright notice for easier
|
|
188
|
+
identification within third-party archives.
|
|
189
|
+
|
|
190
|
+
Copyright [yyyy] [name of copyright owner]
|
|
191
|
+
|
|
192
|
+
Licensed under the Apache License, Version 2.0 (the "License");
|
|
193
|
+
you may not use this file except in compliance with the License.
|
|
194
|
+
You may obtain a copy of the License at
|
|
195
|
+
|
|
196
|
+
http://www.apache.org/licenses/LICENSE-2.0
|
|
197
|
+
|
|
198
|
+
Unless required by applicable law or agreed to in writing, software
|
|
199
|
+
distributed under the License is distributed on an "AS IS" BASIS,
|
|
200
|
+
WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied.
|
|
201
|
+
See the License for the specific language governing permissions and
|
|
202
|
+
limitations under the License.
|