dsh-mcp-connector 0.2.112 → 0.2.113
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/CHANGELOG.md +8 -0
- package/README.en.md +2 -2
- package/README.md +2 -2
- package/docs/USER-GUIDE.md +15 -0
- package/docs/screenshots/01-market-overview.jpg +0 -0
- package/docs/screenshots/02-connector-detail.jpg +0 -0
- package/docs/screenshots/03-tool-discovery.jpg +0 -0
- package/docs/screenshots/04-json-import.jpg +0 -0
- package/docs/screenshots/05-unified-tool-search.png +0 -0
- package/docs/screenshots/06-tool-parameters.png +0 -0
- package/docs/screenshots/07-connection-diagnostics.png +0 -0
- package/docs/screenshots/08-ten-recommendations.jpg +0 -0
- package/docs/screenshots/README.md +1 -1
- package/docs/screenshots/assets.json +20 -20
- package/docs/screenshots/en/01-market-overview.jpg +0 -0
- package/docs/screenshots/en/02-connector-detail.jpg +0 -0
- package/docs/screenshots/en/03-tool-discovery.jpg +0 -0
- package/docs/screenshots/en/04-json-import.jpg +0 -0
- package/docs/screenshots/en/05-unified-tool-search.png +0 -0
- package/docs/screenshots/en/06-tool-parameters.png +0 -0
- package/docs/screenshots/en/07-connection-diagnostics.png +0 -0
- package/docs/screenshots/en/08-ten-recommendations.jpg +0 -0
- package/docs/screenshots/en/assets.json +20 -20
- package/docs/screenshots/en/demo.gif +0 -0
- package/docs/tutorials/FIRST-SUCCESS-SCENARIOS.md +1 -1
- package/lib/connection-editor.js +1 -1
- package/lib/connectors/json-connector.js +2 -0
- package/lib/connectors/manual-connector.js +4 -3
- package/lib/connectors/oauth-connector.js +4 -1
- package/lib/custom-oauth.js +52 -0
- package/lib/i18n/locales/en/host.js +12 -0
- package/lib/index.js +68 -13
- package/lib/oauth.js +7 -4
- package/lib/schema.js +4 -0
- package/lib/status-events.js +1 -0
- package/lib/tools.js +1 -1
- package/lib/web.js +2 -0
- package/package.json +1 -1
- package/ui/index.html +31 -8
package/CHANGELOG.md
CHANGED
|
@@ -1,5 +1,13 @@
|
|
|
1
1
|
# Changelog
|
|
2
2
|
|
|
3
|
+
## 0.2.113 - 2026-11-18
|
|
4
|
+
|
|
5
|
+
- 自定义 URL 与标准 mcpServers JSON 导入自动检测 HTTP 401 的 OAuth 认证需求;保存待授权配置后,可在已安装页逐项进行身份验证,无需市场卡片 URL。
|
|
6
|
+
- 复用 PKCE、动态客户端注册、本机凭据存储和刷新机制;首次工具同步成功后才启用,取消和失败保留待授权配置,阻止重复授权及同名覆盖。
|
|
7
|
+
- 自定义 OAuth 仅绑定所填资源,保持项目范围和按需注入设置;显式凭据、stdio、403 与网络故障不触发自动授权。
|
|
8
|
+
- Add OAuth discovery and explicit authentication for custom HTTP URLs and standard MCP JSON imports. Pending drafts survive restart; successful startup is required before enabling tools.
|
|
9
|
+
- Keep credentials local and resource-scoped; retain project scope, cancellation and existing explicit-credential behavior.
|
|
10
|
+
|
|
3
11
|
## 0.2.112 - 2026-11-18
|
|
4
12
|
|
|
5
13
|
- 提高运行时依赖的最低版本至 Undici 6.29.1 和 Zod 4.6.6,覆盖相关拒绝服务漏洞的修复。CI 使用 Zod 4.6.6 验证最低版本兼容性(#262)。
|
package/README.en.md
CHANGED
|
@@ -163,7 +163,7 @@ As of 2026-11-17, the public Registry publishes 118 connector descriptors. After
|
|
|
163
163
|
| Connection diagnostics and last-success cache | |
|
|
164
164
|
| 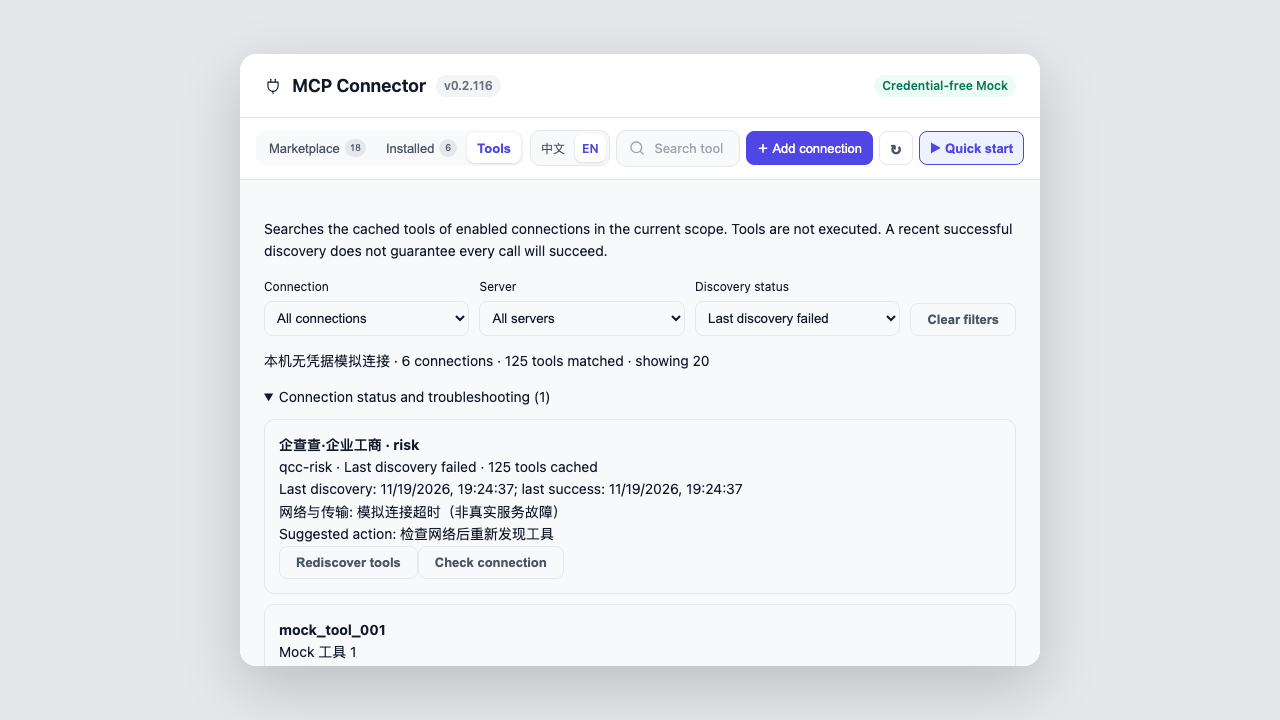 | |
|
|
165
165
|
|
|
166
|
-
<!-- generated:media -->English UI screenshots and GIF were captured from v0.2.
|
|
166
|
+
<!-- generated:media -->English UI screenshots and GIF were captured from v0.2.113 (2026-11-18), using the credential-free Mock harness. Provider content retains its original language. They demonstrate UI, not real business acceptance; counts are fixtures. See [asset provenance](docs/screenshots/README.md).<!-- /generated:media -->
|
|
167
167
|
|
|
168
168
|
## Installation
|
|
169
169
|
|
|
@@ -305,7 +305,7 @@ npm run dev:ui
|
|
|
305
305
|
|
|
306
306
|
Every Registry merge regenerates `catalog-stats.json`; an hourly workflow in this repository synchronizes the Chinese and English product copy plus a local stats snapshot. The static npm README updates with package releases, while the live badges above read the Registry directly and therefore stay current without another npm release.
|
|
307
307
|
|
|
308
|
-
<!-- generated:version -->The current public version is [`dsh-mcp-connector@0.2.
|
|
308
|
+
<!-- generated:version -->The current public version is [`dsh-mcp-connector@0.2.113`](https://www.npmjs.com/package/dsh-mcp-connector), with [GitHub Release v0.2.113](https://github.com/duhu2000/dsh-mcp-connector/releases/tag/v0.2.113).<!-- /generated:version -->
|
|
309
309
|
|
|
310
310
|
See [CHANGELOG.md](CHANGELOG.md) for version history and [docs/DESKTOP-E2E.md](docs/DESKTOP-E2E.md) for the Desktop release checklist.
|
|
311
311
|
|
package/README.md
CHANGED
|
@@ -177,7 +177,7 @@ Desktop 需要完全退出并重新启动应用;Web 需要停止原 `dsh web`
|
|
|
177
177
|
| 连接诊断与最后成功缓存 | |
|
|
178
178
|
| 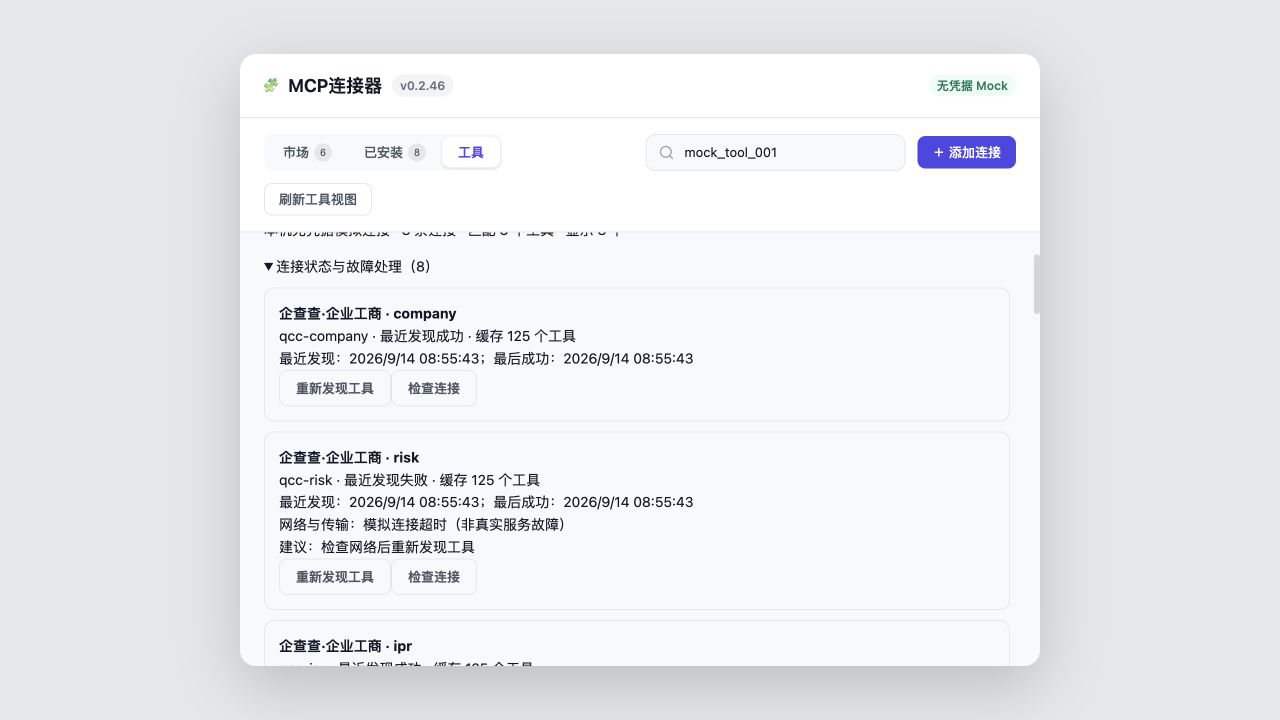 | |
|
|
179
179
|
|
|
180
|
-
<!-- generated:media -->截图与 GIF 采集自 v0.2.
|
|
180
|
+
<!-- generated:media -->截图与 GIF 采集自 v0.2.113(2026-11-18)无凭据 Mock 页面,展示界面而非真实业务验收;市场数量是测试夹具。来源与更新方法见 [素材说明](docs/screenshots/README.md)。<!-- /generated:media -->
|
|
181
181
|
|
|
182
182
|
## 安装
|
|
183
183
|
|
|
@@ -312,7 +312,7 @@ npm run dev:ui
|
|
|
312
312
|
|
|
313
313
|
公共 Registry 每次合并后会生成 `catalog-stats.json`;本仓库的定时工作流每小时同步中英文介绍和统计快照。npm 页面中的静态正文随版本发布更新,上方动态统计徽标则直接读取 Registry,可在不发布新 npm 版本时保持实时数量一致。
|
|
314
314
|
|
|
315
|
-
<!-- generated:version -->当前公开版本为 [`dsh-mcp-connector@0.2.
|
|
315
|
+
<!-- generated:version -->当前公开版本为 [`dsh-mcp-connector@0.2.113`](https://www.npmjs.com/package/dsh-mcp-connector),对应 [GitHub Release v0.2.113](https://github.com/duhu2000/dsh-mcp-connector/releases/tag/v0.2.113)。<!-- /generated:version -->
|
|
316
316
|
|
|
317
317
|
版本能力与变更记录见 [CHANGELOG.md](CHANGELOG.md)。
|
|
318
318
|
Desktop 发版回归见 [docs/DESKTOP-E2E.md](docs/DESKTOP-E2E.md)。
|
package/docs/USER-GUIDE.md
CHANGED
|
@@ -431,3 +431,18 @@ Windows 下 `.cmd` / `.bat` 是脚本包装器,不等同于可直接启动的
|
|
|
431
431
|
### 如何反馈问题
|
|
432
432
|
|
|
433
433
|
提交 [GitHub Issue](https://github.com/duhu2000/dsh-mcp-connector/issues) 时,请提供 DSH 版本、插件版本、连接器名称、复现步骤和已脱敏的错误信息。不要附带 Token、API Key、Cookie、授权码或包含真实凭据的配置文件。
|
|
434
|
+
|
|
435
|
+
|
|
436
|
+
## 自定义 MCP:粘贴 JSON 或填写 URL 后授权
|
|
437
|
+
|
|
438
|
+
在「添加连接」中粘贴标准 `mcpServers` JSON,或手动填写 MCP URL 并保留「自动检测认证(含 OAuth)」。无需创建市场卡片或提供 Registry JSON 地址。
|
|
439
|
+
|
|
440
|
+
```json
|
|
441
|
+
{"mcpServers":{"qcc-company":{"url":"https://agent.qcc.com/mcp/company/stream"},"tradesparq-trade-data":{"type":"streamable-http","url":"https://mcp.tradesparq.com/mcp/data-search"}}}
|
|
442
|
+
```
|
|
443
|
+
|
|
444
|
+
服务返回 HTTP 401 且提供可用的 OAuth 元数据时,配置保存为「待身份验证」。进入「已安装」逐项点击「进行身份验证」,在服务商页面确认授权。授权、MCP 初始化及首次工具同步成功后才启用连接;取消、超时或失败不会把待授权配置显示为已连接。可以取消后重试,重启后也可以继续授权。
|
|
445
|
+
|
|
446
|
+
自动授权适用于支持 Authorization Code、PKCE S256 和公共客户端动态注册的服务。需要预登记客户端、API Key 或自定义认证 Header 的服务仍需按服务商说明配置;403、网络故障不会被当作 OAuth 授权提示。已有凭据不会被自动替换。自定义授权只绑定所填写的资源,不自动开通同一服务商的其他 MCP Server。
|
|
447
|
+
|
|
448
|
+
授权在运行 DSH 的主机上发起,回调使用该主机的本地地址。远程访问 DSH 时,浏览器必须能访问该回调主机;本功能不会自动建立隧道。凭据沿用插件的本机存储与刷新机制,待授权配置不会注册可调用工具。
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
@@ -1,6 +1,6 @@
|
|
|
1
1
|
# 产品截图与演示的来源及更新
|
|
2
2
|
|
|
3
|
-
<!-- generated:media -->本组 8 张截图和 GIF 均从 v0.2.
|
|
3
|
+
<!-- generated:media -->本组 8 张截图和 GIF 均从 v0.2.113 于 2026-11-18 重新采集,未修改截图中的版本文字。<!-- /generated:media -->
|
|
4
4
|
|
|
5
5
|
前七张素材由真实产品 UI 的无凭据 Mock harness 渲染:1280×720 浏览器视口、800px 产品面板、桌面两列卡片。顶部保留“无凭据 Mock”标识;目录数、连接数与工具数是演示夹具,不代表生产统计或真实授权、业务验收。不会读取用户 profile、调用服务商或上传业务数据。
|
|
6
6
|
|
|
@@ -3,8 +3,8 @@
|
|
|
3
3
|
"capture": {
|
|
4
4
|
"locale": "zh-CN",
|
|
5
5
|
"capturedOn": "2026-11-18",
|
|
6
|
-
"sourceVersion": "0.2.
|
|
7
|
-
"sourceFingerprint": "
|
|
6
|
+
"sourceVersion": "0.2.113",
|
|
7
|
+
"sourceFingerprint": "a815e3bdcd6ecdd753ce911467e5b6e48b8df8e2a5c7d7a7e4f6505184b16373",
|
|
8
8
|
"browserViewport": {
|
|
9
9
|
"width": 1280,
|
|
10
10
|
"height": 720
|
|
@@ -17,63 +17,63 @@
|
|
|
17
17
|
"screenshots": [
|
|
18
18
|
{
|
|
19
19
|
"path": "docs/screenshots/01-market-overview.jpg",
|
|
20
|
-
"sha256": "
|
|
20
|
+
"sha256": "1b81ec946e9684802389245dc47b374db253a51db96c09c634f3471f00f79fe0",
|
|
21
21
|
"width": 1280,
|
|
22
22
|
"height": 720,
|
|
23
23
|
"capturedOn": "2026-11-18",
|
|
24
|
-
"sourceVersion": "0.2.
|
|
24
|
+
"sourceVersion": "0.2.113"
|
|
25
25
|
},
|
|
26
26
|
{
|
|
27
27
|
"path": "docs/screenshots/02-connector-detail.jpg",
|
|
28
|
-
"sha256": "
|
|
28
|
+
"sha256": "80cb6e1fbb27964c43426e63e42e8aed29cbd77dc7c85fb2c99416a3d07ef13d",
|
|
29
29
|
"width": 1280,
|
|
30
30
|
"height": 720,
|
|
31
31
|
"capturedOn": "2026-11-18",
|
|
32
|
-
"sourceVersion": "0.2.
|
|
32
|
+
"sourceVersion": "0.2.113"
|
|
33
33
|
},
|
|
34
34
|
{
|
|
35
35
|
"path": "docs/screenshots/03-tool-discovery.jpg",
|
|
36
|
-
"sha256": "
|
|
36
|
+
"sha256": "c3848190e52b050eb781f76ebc66fc28fbf89443ff5169476930750f0cd42d7c",
|
|
37
37
|
"width": 1280,
|
|
38
38
|
"height": 720,
|
|
39
39
|
"capturedOn": "2026-11-18",
|
|
40
|
-
"sourceVersion": "0.2.
|
|
40
|
+
"sourceVersion": "0.2.113"
|
|
41
41
|
},
|
|
42
42
|
{
|
|
43
43
|
"path": "docs/screenshots/04-json-import.jpg",
|
|
44
|
-
"sha256": "
|
|
44
|
+
"sha256": "7435779242734d4ac15b28a6ad48bbfbf65330a554957a1809ec6e6472cc29a0",
|
|
45
45
|
"width": 1280,
|
|
46
46
|
"height": 720,
|
|
47
47
|
"capturedOn": "2026-11-18",
|
|
48
|
-
"sourceVersion": "0.2.
|
|
48
|
+
"sourceVersion": "0.2.113"
|
|
49
49
|
},
|
|
50
50
|
{
|
|
51
51
|
"path": "docs/screenshots/05-unified-tool-search.png",
|
|
52
|
-
"sha256": "
|
|
52
|
+
"sha256": "e76a535528789cd21448dc9d27aa545313c0945fdc4db152d9c9373791f6f4ca",
|
|
53
53
|
"width": 1280,
|
|
54
54
|
"height": 720,
|
|
55
55
|
"capturedOn": "2026-11-18",
|
|
56
|
-
"sourceVersion": "0.2.
|
|
56
|
+
"sourceVersion": "0.2.113"
|
|
57
57
|
},
|
|
58
58
|
{
|
|
59
59
|
"path": "docs/screenshots/06-tool-parameters.png",
|
|
60
|
-
"sha256": "
|
|
60
|
+
"sha256": "858c5870cd4c1077d8a7042cfa7feb59266a821e8c3a668938ccf22450627f92",
|
|
61
61
|
"width": 1280,
|
|
62
62
|
"height": 720,
|
|
63
63
|
"capturedOn": "2026-11-18",
|
|
64
|
-
"sourceVersion": "0.2.
|
|
64
|
+
"sourceVersion": "0.2.113"
|
|
65
65
|
},
|
|
66
66
|
{
|
|
67
67
|
"path": "docs/screenshots/07-connection-diagnostics.png",
|
|
68
|
-
"sha256": "
|
|
68
|
+
"sha256": "6e984a0ddaded381c1b8352e76a7081aab56c2ba2d46cc0709daaefed11482ff",
|
|
69
69
|
"width": 1280,
|
|
70
70
|
"height": 720,
|
|
71
71
|
"capturedOn": "2026-11-18",
|
|
72
|
-
"sourceVersion": "0.2.
|
|
72
|
+
"sourceVersion": "0.2.113"
|
|
73
73
|
},
|
|
74
74
|
{
|
|
75
75
|
"path": "docs/screenshots/08-ten-recommendations.jpg",
|
|
76
|
-
"sha256": "
|
|
76
|
+
"sha256": "75a1bc2e54ba458eab6ae0442f737af23070f989ed20a8293bb98f3184d7e02f",
|
|
77
77
|
"width": 1280,
|
|
78
78
|
"height": 1400,
|
|
79
79
|
"browserViewport": {
|
|
@@ -82,16 +82,16 @@
|
|
|
82
82
|
},
|
|
83
83
|
"panelHeight": 1280,
|
|
84
84
|
"capturedOn": "2026-11-18",
|
|
85
|
-
"sourceVersion": "0.2.
|
|
85
|
+
"sourceVersion": "0.2.113"
|
|
86
86
|
}
|
|
87
87
|
],
|
|
88
88
|
"demo": {
|
|
89
89
|
"path": "docs/demo.gif",
|
|
90
|
-
"sha256": "
|
|
90
|
+
"sha256": "d169782bd0914f920e5c228a953d51e56030694a7785142dbecd8f23c2e48224",
|
|
91
91
|
"width": 960,
|
|
92
92
|
"height": 540,
|
|
93
93
|
"capturedOn": "2026-11-18",
|
|
94
|
-
"sourceVersion": "0.2.
|
|
94
|
+
"sourceVersion": "0.2.113",
|
|
95
95
|
"durationSeconds": 36
|
|
96
96
|
}
|
|
97
97
|
}
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
Binary file
|
|
@@ -3,8 +3,8 @@
|
|
|
3
3
|
"capture": {
|
|
4
4
|
"locale": "en",
|
|
5
5
|
"capturedOn": "2026-11-18",
|
|
6
|
-
"sourceVersion": "0.2.
|
|
7
|
-
"sourceFingerprint": "
|
|
6
|
+
"sourceVersion": "0.2.113",
|
|
7
|
+
"sourceFingerprint": "a815e3bdcd6ecdd753ce911467e5b6e48b8df8e2a5c7d7a7e4f6505184b16373",
|
|
8
8
|
"browserViewport": {
|
|
9
9
|
"width": 1280,
|
|
10
10
|
"height": 720
|
|
@@ -17,63 +17,63 @@
|
|
|
17
17
|
"screenshots": [
|
|
18
18
|
{
|
|
19
19
|
"path": "docs/screenshots/en/01-market-overview.jpg",
|
|
20
|
-
"sha256": "
|
|
20
|
+
"sha256": "3c1fa1f4d1f5abee2209bfecc56585c5f422282b73ed0e915d758c9bd2438585",
|
|
21
21
|
"width": 1280,
|
|
22
22
|
"height": 720,
|
|
23
23
|
"capturedOn": "2026-11-18",
|
|
24
|
-
"sourceVersion": "0.2.
|
|
24
|
+
"sourceVersion": "0.2.113"
|
|
25
25
|
},
|
|
26
26
|
{
|
|
27
27
|
"path": "docs/screenshots/en/02-connector-detail.jpg",
|
|
28
|
-
"sha256": "
|
|
28
|
+
"sha256": "3662d80f940c0b9fe5600637cdc61c2a9d9d3f98d3e662c76d94939084f652ed",
|
|
29
29
|
"width": 1280,
|
|
30
30
|
"height": 720,
|
|
31
31
|
"capturedOn": "2026-11-18",
|
|
32
|
-
"sourceVersion": "0.2.
|
|
32
|
+
"sourceVersion": "0.2.113"
|
|
33
33
|
},
|
|
34
34
|
{
|
|
35
35
|
"path": "docs/screenshots/en/03-tool-discovery.jpg",
|
|
36
|
-
"sha256": "
|
|
36
|
+
"sha256": "ad5e025720bbb0cdd20fb0224c3f26e8a7d1291be35a5deaa72f47f9cb41b9a6",
|
|
37
37
|
"width": 1280,
|
|
38
38
|
"height": 720,
|
|
39
39
|
"capturedOn": "2026-11-18",
|
|
40
|
-
"sourceVersion": "0.2.
|
|
40
|
+
"sourceVersion": "0.2.113"
|
|
41
41
|
},
|
|
42
42
|
{
|
|
43
43
|
"path": "docs/screenshots/en/04-json-import.jpg",
|
|
44
|
-
"sha256": "
|
|
44
|
+
"sha256": "b1a9c876ed3a19c22203c8ba8660523a973d6ff34248313794618af834a95ba8",
|
|
45
45
|
"width": 1280,
|
|
46
46
|
"height": 720,
|
|
47
47
|
"capturedOn": "2026-11-18",
|
|
48
|
-
"sourceVersion": "0.2.
|
|
48
|
+
"sourceVersion": "0.2.113"
|
|
49
49
|
},
|
|
50
50
|
{
|
|
51
51
|
"path": "docs/screenshots/en/05-unified-tool-search.png",
|
|
52
|
-
"sha256": "
|
|
52
|
+
"sha256": "d8b5e30e8c6075ba7410cb5b518968715a685a69357a547575501fba0ecf4405",
|
|
53
53
|
"width": 1280,
|
|
54
54
|
"height": 720,
|
|
55
55
|
"capturedOn": "2026-11-18",
|
|
56
|
-
"sourceVersion": "0.2.
|
|
56
|
+
"sourceVersion": "0.2.113"
|
|
57
57
|
},
|
|
58
58
|
{
|
|
59
59
|
"path": "docs/screenshots/en/06-tool-parameters.png",
|
|
60
|
-
"sha256": "
|
|
60
|
+
"sha256": "97f9afd6cf1bde2ec92d6c7ec83a5139e6ec89f280666ab60e473606c939de8a",
|
|
61
61
|
"width": 1280,
|
|
62
62
|
"height": 720,
|
|
63
63
|
"capturedOn": "2026-11-18",
|
|
64
|
-
"sourceVersion": "0.2.
|
|
64
|
+
"sourceVersion": "0.2.113"
|
|
65
65
|
},
|
|
66
66
|
{
|
|
67
67
|
"path": "docs/screenshots/en/07-connection-diagnostics.png",
|
|
68
|
-
"sha256": "
|
|
68
|
+
"sha256": "08a3a101d3817e54eb7d56b70e53f7d27febc25ba64826785efdc11e74c16fde",
|
|
69
69
|
"width": 1280,
|
|
70
70
|
"height": 720,
|
|
71
71
|
"capturedOn": "2026-11-18",
|
|
72
|
-
"sourceVersion": "0.2.
|
|
72
|
+
"sourceVersion": "0.2.113"
|
|
73
73
|
},
|
|
74
74
|
{
|
|
75
75
|
"path": "docs/screenshots/en/08-ten-recommendations.jpg",
|
|
76
|
-
"sha256": "
|
|
76
|
+
"sha256": "45d61e4f8b9ab3a2a1922b5bba6646fd142e02f6612a65f7d3e17a52b80ed23c",
|
|
77
77
|
"width": 1280,
|
|
78
78
|
"height": 1400,
|
|
79
79
|
"browserViewport": {
|
|
@@ -82,16 +82,16 @@
|
|
|
82
82
|
},
|
|
83
83
|
"panelHeight": 1280,
|
|
84
84
|
"capturedOn": "2026-11-18",
|
|
85
|
-
"sourceVersion": "0.2.
|
|
85
|
+
"sourceVersion": "0.2.113"
|
|
86
86
|
}
|
|
87
87
|
],
|
|
88
88
|
"demo": {
|
|
89
89
|
"path": "docs/screenshots/en/demo.gif",
|
|
90
|
-
"sha256": "
|
|
90
|
+
"sha256": "f8663a8b789df97fe039878c37a5461e7188e5209e18932f07686244f399ac73",
|
|
91
91
|
"width": 960,
|
|
92
92
|
"height": 540,
|
|
93
93
|
"capturedOn": "2026-11-18",
|
|
94
|
-
"sourceVersion": "0.2.
|
|
94
|
+
"sourceVersion": "0.2.113",
|
|
95
95
|
"durationSeconds": 36
|
|
96
96
|
}
|
|
97
97
|
}
|
|
Binary file
|
|
@@ -8,7 +8,7 @@
|
|
|
8
8
|
|
|
9
9
|
| 项目 | 验收要求 |
|
|
10
10
|
|---|---|
|
|
11
|
-
| 前提 | <!-- generated:version -->正式 `dsh-mcp-connector@0.2.
|
|
11
|
+
| 前提 | <!-- generated:version -->正式 `dsh-mcp-connector@0.2.113`<!-- /generated:version -->;当前 Workspace;企查查 OAuth 可用;测试账号具有目标企业数据权限 |
|
|
12
12
|
| 权限/管理员 | 账号权限、组织授权和可见字段由服务商控制;企业组织可能需要管理员开通,当前文档不能替代审批 |
|
|
13
13
|
| 费用 | 可能受套餐、次数或字段权限影响;MCP连接器无法确认本次费用,调用前在服务商侧核对 |
|
|
14
14
|
| 运行/数据去向 | 远程 MCP Server;企业名称、查询参数和调用结果经 DSH Host 发送到/返回自 `agent.qcc.com` |
|
package/lib/connection-editor.js
CHANGED
|
@@ -16,7 +16,7 @@ export const KEEP_EXISTING_VALUE = '<KEEP_EXISTING>';
|
|
|
16
16
|
|
|
17
17
|
export function connectionConfigurationEditable(record) {
|
|
18
18
|
return [CUSTOM_CONNECTOR_ID, JSON_CONNECTOR_ID].includes(record?.connectorId)
|
|
19
|
-
&& record?.auth?.mode !== 'oauth';
|
|
19
|
+
&& !record?.oauthDiscovery && record?.auth?.mode !== 'oauth';
|
|
20
20
|
}
|
|
21
21
|
|
|
22
22
|
function keepObjectKeys(input, path, preservedFields) {
|
|
@@ -157,6 +157,7 @@ export function normalizeJsonImport(input, { t = tZh } = {}) {
|
|
|
157
157
|
serverName: slugServerName(cfg.serverName ?? name),
|
|
158
158
|
headers,
|
|
159
159
|
auth,
|
|
160
|
+
authDetection: 'auto',
|
|
160
161
|
enabled: cfg.enabled !== false,
|
|
161
162
|
injectionMode: normalizeInjectionMode(cfg.injectionMode),
|
|
162
163
|
createdAt: Date.now(),
|
|
@@ -196,6 +197,7 @@ export function normalizeJsonImport(input, { t = tZh } = {}) {
|
|
|
196
197
|
serverName: slugServerName(item.serverName ?? name),
|
|
197
198
|
headers: coerceHeaders(item.headers),
|
|
198
199
|
auth: authFromFields(item),
|
|
200
|
+
authDetection: 'auto',
|
|
199
201
|
enabled: item.enabled !== false,
|
|
200
202
|
injectionMode: normalizeInjectionMode(item.injectionMode),
|
|
201
203
|
createdAt: Date.now(),
|
|
@@ -62,7 +62,7 @@ export function buildManualRecord(params = {}, { t = tZh } = {}) {
|
|
|
62
62
|
if (transport === 'stdio') {
|
|
63
63
|
const command = String(params.command ?? '').trim();
|
|
64
64
|
if (!command) throw new Error(t('transport=stdio 时 command 必填'));
|
|
65
|
-
if (params.authMode && params.authMode !== 'none') throw new Error(t('stdio 鉴权请通过 envJson 传入环境变量'));
|
|
65
|
+
if (params.authMode && params.authMode !== 'none' && params.authMode !== 'auto') throw new Error(t('stdio 鉴权请通过 envJson 传入环境变量'));
|
|
66
66
|
if (params.args !== undefined && !Array.isArray(params.args)) throw new Error(t('args 必须是字符串数组'));
|
|
67
67
|
const args = (params.args ?? []).map((value) => String(value));
|
|
68
68
|
const env = parseEnvJson(params.envJson ?? params.env, { t });
|
|
@@ -95,7 +95,7 @@ export function buildManualRecord(params = {}, { t = tZh } = {}) {
|
|
|
95
95
|
&& params.allowInsecurePrivateNetwork === true;
|
|
96
96
|
const headers = parseHeadersJson(params.headersJson, { t });
|
|
97
97
|
|
|
98
|
-
const authMode = params.authMode ?? '
|
|
98
|
+
const authMode = params.authMode ?? 'auto';
|
|
99
99
|
let auth;
|
|
100
100
|
if (authMode === 'bearer') {
|
|
101
101
|
if (!params.bearerToken) throw new Error(t('authMode=bearer 时 bearerToken 必填'));
|
|
@@ -104,7 +104,7 @@ export function buildManualRecord(params = {}, { t = tZh } = {}) {
|
|
|
104
104
|
const apiKeyHeader = assertSafeHeaderName(params.apiKeyHeader ?? 'X-Api-Key');
|
|
105
105
|
if (params.apiKeyValue === undefined || params.apiKeyValue === '') throw new Error(t('authMode=api-key 时 apiKeyValue 必填'));
|
|
106
106
|
auth = { mode: 'api-key', apiKeyHeader, apiKeyValue: String(params.apiKeyValue) };
|
|
107
|
-
} else if (authMode !== 'none') {
|
|
107
|
+
} else if (authMode !== 'none' && authMode !== 'auto') {
|
|
108
108
|
throw new Error(`unsupported authMode: ${authMode}`);
|
|
109
109
|
}
|
|
110
110
|
|
|
@@ -119,6 +119,7 @@ export function buildManualRecord(params = {}, { t = tZh } = {}) {
|
|
|
119
119
|
serverName,
|
|
120
120
|
headers,
|
|
121
121
|
auth,
|
|
122
|
+
authDetection: authMode === 'auto' ? 'auto' : 'none',
|
|
122
123
|
enabled: true,
|
|
123
124
|
injectionMode: normalizeInjectionMode(params.injectionMode),
|
|
124
125
|
createdAt: Date.now(),
|
|
@@ -98,7 +98,7 @@ export function describeOAuthAuthorizationError(error, { t = tZh } = {}) {
|
|
|
98
98
|
* @param {{info:Function,warn:Function,error:Function}} args.logger
|
|
99
99
|
* @param {AbortSignal} [args.signal]
|
|
100
100
|
*/
|
|
101
|
-
export async function oauthAuthorize({ connector, config, logger, signal }) {
|
|
101
|
+
export async function oauthAuthorize({ connector, config, logger, signal, expectedDiscovery }) {
|
|
102
102
|
const entryServer = connector.servers.find((server) => server.url);
|
|
103
103
|
if (!entryServer) throw stagedError('resource-discovery', `connector "${connector.id}" has no HTTP OAuth resource`);
|
|
104
104
|
|
|
@@ -109,6 +109,9 @@ export async function oauthAuthorize({ connector, config, logger, signal }) {
|
|
|
109
109
|
const issuer = protectedResource.authorizationServers[0] ?? connector.auth.issuer;
|
|
110
110
|
if (!issuer) throw stagedError('resource-discovery', `connector "${connector.id}" missing issuer`);
|
|
111
111
|
|
|
112
|
+
if (expectedDiscovery && (issuer !== expectedDiscovery.issuer || (protectedResource.resource ?? entryServer.url) !== expectedDiscovery.resource)) {
|
|
113
|
+
throw stagedError('resource-discovery', 'OAuth metadata changed; remove and add this connection again');
|
|
114
|
+
}
|
|
112
115
|
const metadata = await atOAuthStage(
|
|
113
116
|
'server-metadata',
|
|
114
117
|
() => discoverServerMetadata(issuer, config.requestTimeoutMs),
|
|
@@ -0,0 +1,52 @@
|
|
|
1
|
+
/** Local custom connections: discovery does not open a browser or register a client. */
|
|
2
|
+
import { discoverProtectedResource, discoverServerMetadata } from './oauth.js';
|
|
3
|
+
import { validateConnectionRecord } from './mcp-validation.js';
|
|
4
|
+
import { assertSafeUrl } from './util.js';
|
|
5
|
+
import { createTranslator, DEFAULT_LOCALE } from './i18n/index.js';
|
|
6
|
+
|
|
7
|
+
export async function discoverCustomOAuth(record, timeoutMs) {
|
|
8
|
+
assertSafeUrl(record.url);
|
|
9
|
+
const resource = await discoverProtectedResource(record.url, timeoutMs);
|
|
10
|
+
const resourceUrl = resource.resource || record.url;
|
|
11
|
+
assertSafeUrl(resourceUrl);
|
|
12
|
+
// Never infer a grant for another service from arbitrary metadata.
|
|
13
|
+
if (new URL(resourceUrl).origin !== new URL(record.url).origin) throw new Error('OAuth resource origin mismatch');
|
|
14
|
+
const issuer = resource.authorizationServers[0];
|
|
15
|
+
const metadata = await discoverServerMetadata(issuer, timeoutMs);
|
|
16
|
+
if (metadata.codeChallengeMethodsSupported.length && !metadata.codeChallengeMethodsSupported.includes('S256')) throw new Error('OAuth PKCE S256 unavailable');
|
|
17
|
+
if (metadata.tokenEndpointAuthMethodsSupported.length && !metadata.tokenEndpointAuthMethodsSupported.includes('none')) throw new Error('OAuth public client registration unavailable');
|
|
18
|
+
return { issuer, resource: resourceUrl, scope: resource.challengeScope ?? resource.scopesSupported.join(' ') };
|
|
19
|
+
}
|
|
20
|
+
|
|
21
|
+
export async function prepareCustomConnections(records, { timeoutMs, t = createTranslator(DEFAULT_LOCALE) } = {}) {
|
|
22
|
+
const prepared = [], results = [];
|
|
23
|
+
for (const input of records) {
|
|
24
|
+
const record = { ...input, pendingAuthorization: false, oauthDiscovery: undefined };
|
|
25
|
+
const result = await validateConnectionRecord(record, { timeoutMs, t });
|
|
26
|
+
const eligible = record.transport === 'streamable-http' && record.authDetection !== 'none'
|
|
27
|
+
&& !record.auth && !Object.keys(record.headers ?? {}).length && !record.allowInsecurePrivateNetwork;
|
|
28
|
+
if (!result.ok && result.httpStatus === 401 && eligible) {
|
|
29
|
+
try {
|
|
30
|
+
const oauthDiscovery = await discoverCustomOAuth(record, timeoutMs);
|
|
31
|
+
prepared.push({ ...record, enabled: false, pendingAuthorization: true, oauthDiscovery });
|
|
32
|
+
results.push({ ...result, ok: true, kind: 'authorization-required', message: t('待身份验证') });
|
|
33
|
+
continue;
|
|
34
|
+
} catch {
|
|
35
|
+
results.push({ ...result, message: t('服务要求认证,但未发现可自动使用的 OAuth 配置;请核对服务商的凭据或客户端准入要求') });
|
|
36
|
+
prepared.push(record);
|
|
37
|
+
continue;
|
|
38
|
+
}
|
|
39
|
+
}
|
|
40
|
+
prepared.push(record);
|
|
41
|
+
results.push(result);
|
|
42
|
+
}
|
|
43
|
+
const failures = results.filter(result => !result.ok);
|
|
44
|
+
return { ok: failures.length === 0, records: prepared, detail: { results },
|
|
45
|
+
message: failures.length ? t('连接验证失败:{summary}{more}。未保存连接,请修正后重试。', { summary: failures.map(result => `${result.serverName}: ${result.message}`).join('; '), more: '' }) : '' };
|
|
46
|
+
}
|
|
47
|
+
|
|
48
|
+
export function customOAuthDescriptor(record) {
|
|
49
|
+
return { id: record.key, name: record.name,
|
|
50
|
+
auth: { mode: 'oauth2-pkce', ...record.oauthDiscovery, clientName: 'DeepSeek Harness - MCP Connector', tokenEndpointAuthMethod: 'none', grantSharing: 'connector' },
|
|
51
|
+
servers: [{ serverKey: record.serverName, serverName: record.serverName, url: record.url, oauthResource: record.oauthDiscovery.resource, transport: 'streamable-http' }] };
|
|
52
|
+
}
|
|
@@ -4,6 +4,18 @@
|
|
|
4
4
|
* msgid 为中文原文;缺译文时回退中文原文,不会显示空白。
|
|
5
5
|
*/
|
|
6
6
|
export default {
|
|
7
|
+
"同名连接已存在,请先断开旧连接或使用不同名称": "A connection with this name exists. Disconnect it or use a different name.",
|
|
8
|
+
"配置已保存,请在已安装页点击进行身份验证": "Configuration saved. Click Authenticate in Installed.",
|
|
9
|
+
"此连接没有待处理的 OAuth 授权": "This connection has no OAuth authorization to process.",
|
|
10
|
+
"授权正在进行,请完成或取消当前授权": "Authorization is in progress. Complete or cancel it first.",
|
|
11
|
+
"身份验证与工具同步已完成": "Authentication and tool synchronization completed.",
|
|
12
|
+
"已取消授权,配置已保留": "Authorization cancelled. Configuration retained.",
|
|
13
|
+
"已保存 {count} 条配置,其中 {pending} 条待身份验证;请在已安装页逐项授权": "Saved {count} configurations; {pending} require authentication. Authorize each in Installed.",
|
|
14
|
+
"请先点击进行身份验证": "Click Authenticate first.",
|
|
15
|
+
"鉴权方式,默认自动检测 OAuth": "Authentication method; defaults to automatic OAuth detection",
|
|
16
|
+
"待身份验证": "Authentication required",
|
|
17
|
+
"服务要求认证,但未发现可自动使用的 OAuth 配置;请核对服务商的凭据或客户端准入要求": "Authentication required, but automatic OAuth setup is unavailable. Check provider credentials or client registration requirements.",
|
|
18
|
+
|
|
7
19
|
'"{name}" 已是“始终注入”': '"{name}" is already set to "Always inject"',
|
|
8
20
|
'"{name}" 已是“按会话启用”': '"{name}" is already set to "Enable per session"',
|
|
9
21
|
'Host 已注册 {count} 个工具': 'The Host registered {count} tools',
|
package/lib/index.js
CHANGED
|
@@ -12,6 +12,7 @@
|
|
|
12
12
|
* disconnect / refresh_catalog / publish / tools_list / tool_search / tool_detail
|
|
13
13
|
*/
|
|
14
14
|
import { ConnectionStatistics, observeConnectionSuccess } from './connection-statistics.js';
|
|
15
|
+
import { prepareCustomConnections, customOAuthDescriptor } from './custom-oauth.js';
|
|
15
16
|
import { randomUUID } from 'node:crypto';
|
|
16
17
|
import z from '@deepseek-ai/schemastery';
|
|
17
18
|
import {
|
|
@@ -933,6 +934,7 @@ export async function apply(ctx, config) {
|
|
|
933
934
|
}
|
|
934
935
|
|
|
935
936
|
async function provisionUntilReady(record, original, { strictStartup = true } = {}) {
|
|
937
|
+
if (record.pendingAuthorization) return; // Draft only; never mount an unauthenticated Host entry.
|
|
936
938
|
if (record.localOverrides && !canEditLocalOverrides(record)) throw new Error(t('当前市场配置不再允许本地参数覆盖,请先清除覆盖'));
|
|
937
939
|
if (!strictStartup) {
|
|
938
940
|
return provision(ctx, config, record, grantMap(), { failOnStartupError: false });
|
|
@@ -1994,6 +1996,8 @@ export async function apply(ctx, config) {
|
|
|
1994
1996
|
|
|
1995
1997
|
/* ───────────────────────── api 门面 ───────────────────────── */
|
|
1996
1998
|
|
|
1999
|
+
const customAuthorizations = new Map();
|
|
2000
|
+
ctx.effect(() => () => { for (const controller of customAuthorizations.values()) controller.abort(); });
|
|
1997
2001
|
const api = {
|
|
1998
2002
|
async connectionStatistics() {
|
|
1999
2003
|
return { ok: true, detail: { ...connectionStatistics.snapshot(), persistent: config.persistSecrets === true }, message: t("本 profile 成功连接过的卡片数;不是连接次数或社区总量,不上传数据") };
|
|
@@ -2530,10 +2534,13 @@ export async function apply(ctx, config) {
|
|
|
2530
2534
|
detail: { connectorId: connector.id, keys: created, snapshotId: snapshot?.key ?? null, scopeRevision, scopeRollbackRevision },
|
|
2531
2535
|
};
|
|
2532
2536
|
}
|
|
2533
|
-
const
|
|
2534
|
-
const validation = await
|
|
2535
|
-
if (!validation.ok) return validation;
|
|
2537
|
+
const candidate = buildManualRecord(params);
|
|
2538
|
+
const validation = await prepareCustomConnections([candidate], { timeoutMs: config.requestTimeoutMs, t });
|
|
2539
|
+
if (!validation.ok) return { ok: false, message: validation.message, detail: validation.detail };
|
|
2540
|
+
const [record] = validation.records;
|
|
2541
|
+
if (record.pendingAuthorization && state.connections.has(record.key)) return { ok: false, message: t('同名连接已存在,请先断开旧连接或使用不同名称') };
|
|
2536
2542
|
const { committed: [committed], snapshot, scopeRevision, scopeRollbackRevision } = await commitScopedWithSnapshot([record], 'configure', { scopeInput: params });
|
|
2543
|
+
if (committed.pendingAuthorization) return { ok: true, message: t('配置已保存,请在已安装页点击进行身份验证'), detail: { key: committed.key, pendingAuthorization: true } };
|
|
2537
2544
|
cacheHealth(committed.connectorId, [committed], readinessResults([committed], validation.detail.results));
|
|
2538
2545
|
return { ok: true, message: t(`已配置并连接 "{name}"(serverName={serverName},{scope})`, { name: committed.name, serverName: committed.serverName, scope: scopeLabel(connectionScopes.binding(committed.key), workspaceNames()) }), detail: { key: committed.key, serverName: committed.serverName, snapshotId: snapshot?.key ?? null, scopeRevision, scopeRollbackRevision } };
|
|
2539
2546
|
} catch (error) {
|
|
@@ -2543,18 +2550,61 @@ export async function apply(ctx, config) {
|
|
|
2543
2550
|
}
|
|
2544
2551
|
},
|
|
2545
2552
|
|
|
2546
|
-
async
|
|
2553
|
+
async authorizeCustom(key) {
|
|
2554
|
+
const record = state.connections.get(key);
|
|
2555
|
+
if (!record?.oauthDiscovery) return { ok: false, message: t('此连接没有待处理的 OAuth 授权') };
|
|
2556
|
+
if (customAuthorizations.has(key)) return { ok: false, message: t('授权正在进行,请完成或取消当前授权') };
|
|
2557
|
+
const controller = new AbortController();
|
|
2558
|
+
customAuthorizations.set(key, controller);
|
|
2559
|
+
let grantKey;
|
|
2547
2560
|
try {
|
|
2548
|
-
const {
|
|
2549
|
-
|
|
2550
|
-
|
|
2551
|
-
|
|
2561
|
+
const authz = await oauthAuthorize({ connector: customOAuthDescriptor(record), config, logger, signal: controller.signal, expectedDiscovery: record.oauthDiscovery });
|
|
2562
|
+
if (controller.signal.aborted || state.connections.get(key) !== record) throw new Error(t('连接配置已变化,请重新检查后重试'));
|
|
2563
|
+
const grant = {
|
|
2564
|
+
key: `${grantStore.keyFor(config.account, authz.issuer, authz.clientId, authz.scope)}:custom:${record.key}:${randomUUID()}`,
|
|
2565
|
+
issuer: authz.issuer, clientId: authz.clientId, clientSecret: authz.clientSecret,
|
|
2566
|
+
clientSecretExpiresAt: authz.clientSecretExpiresAt, tokenEndpointAuthMethod: authz.tokenEndpointAuthMethod ?? 'none',
|
|
2567
|
+
clientName: authz.clientName, scope: authz.scope, account: config.account,
|
|
2568
|
+
accessToken: authz.token.accessToken, accessTokenExpiresAt: Date.now() + authz.token.expiresIn * 1000,
|
|
2569
|
+
refreshToken: authz.token.refreshToken ?? '', authorizedResources: [record.oauthDiscovery.resource],
|
|
2570
|
+
connectorIds: [], updatedAt: Date.now(),
|
|
2571
|
+
};
|
|
2572
|
+
grantKey = grant.key;
|
|
2573
|
+
state.grants.set(grantKey, grantRuntime(grant));
|
|
2574
|
+
if (config.persistSecrets) await grantStore.put(grant);
|
|
2575
|
+
const next = { ...record, pendingAuthorization: false, enabled: true, auth: { mode: 'oauth', grantKey } };
|
|
2576
|
+
const validation = await validateConnectionRecords([next], { timeoutMs: config.requestTimeoutMs, grants: grantMap() });
|
|
2577
|
+
if (!validation.ok) throw new Error(validation.message);
|
|
2578
|
+
await queueConnectionAction(key, async () => {
|
|
2579
|
+
if (controller.signal.aborted || state.connections.get(key) !== record) throw new Error(t('连接配置已变化,请重新检查后重试'));
|
|
2580
|
+
const { committed: [committed] } = await commitScopedWithSnapshot([next], 'custom-oauth');
|
|
2581
|
+
cacheHealth(committed.connectorId, [committed], readinessResults([committed], validation.detail.results));
|
|
2552
2582
|
});
|
|
2553
|
-
|
|
2583
|
+
scheduleRefresh(grantKey);
|
|
2584
|
+
if (record.auth?.grantKey && record.auth.grantKey !== grantKey) await retireGrantIfUnused(record.auth.grantKey, { revoke: true });
|
|
2585
|
+
return { ok: true, message: t('身份验证与工具同步已完成'), detail: { key } };
|
|
2586
|
+
} catch (error) {
|
|
2587
|
+
if (grantKey) await retireGrantIfUnused(grantKey, { revoke: true }).catch(() => {});
|
|
2588
|
+
return { ok: false, message: controller.signal.aborted ? t('已取消授权,配置已保留') : describeOAuthAuthorizationError(error).message };
|
|
2589
|
+
} finally { customAuthorizations.delete(key); }
|
|
2590
|
+
},
|
|
2591
|
+
async cancelCustomAuthorization(key) {
|
|
2592
|
+
customAuthorizations.get(key)?.abort();
|
|
2593
|
+
return { ok: true, message: t('已取消授权,配置已保留') };
|
|
2594
|
+
},
|
|
2595
|
+
|
|
2596
|
+
async importJson(json, scopeInput = {}) {
|
|
2597
|
+
try {
|
|
2598
|
+
const { records: candidates, skipped } = normalizeJsonImport(json);
|
|
2599
|
+
const validation = await prepareCustomConnections(candidates, { timeoutMs: config.requestTimeoutMs, t });
|
|
2600
|
+
if (!validation.ok) return { ok: false, message: validation.message, detail: validation.detail };
|
|
2601
|
+
const records = validation.records;
|
|
2602
|
+
if (records.some(record => record.pendingAuthorization && state.connections.has(record.key))) return { ok: false, message: t('同名连接已存在,请先断开旧连接或使用不同名称') };
|
|
2554
2603
|
const { committed, snapshot, scopeRevision, scopeRollbackRevision } = await commitScopedWithSnapshot(records, 'import', { scopeInput });
|
|
2555
2604
|
const keys = committed.map((record) => record.key);
|
|
2556
2605
|
const grouped = new Map();
|
|
2557
2606
|
for (const record of committed) {
|
|
2607
|
+
if (record.pendingAuthorization) continue;
|
|
2558
2608
|
if (!grouped.has(record.connectorId)) grouped.set(record.connectorId, []);
|
|
2559
2609
|
grouped.get(record.connectorId).push(record);
|
|
2560
2610
|
}
|
|
@@ -2568,7 +2618,9 @@ export async function apply(ctx, config) {
|
|
|
2568
2618
|
const extra = skipped.length ? t(';跳过:{skipped}', { skipped: skipped.join(t('、')) }) : '';
|
|
2569
2619
|
return {
|
|
2570
2620
|
ok: true,
|
|
2571
|
-
message:
|
|
2621
|
+
message: committed.some(record => record.pendingAuthorization)
|
|
2622
|
+
? t('已保存 {count} 条配置,其中 {pending} 条待身份验证;请在已安装页逐项授权', { count: keys.length, pending: committed.filter(record => record.pendingAuthorization).length })
|
|
2623
|
+
: t(`已导入并连接 {count} 个 MCP{extra};JSON 导入属于本机连接,不会自动上架市场`, { count: keys.length, extra: extra }),
|
|
2572
2624
|
detail: { keys, skipped, snapshotId: snapshot?.key ?? null, scopeRevision, scopeRollbackRevision },
|
|
2573
2625
|
};
|
|
2574
2626
|
} catch (error) {
|
|
@@ -2746,10 +2798,12 @@ export async function apply(ctx, config) {
|
|
|
2746
2798
|
enabled: record.enabled !== false,
|
|
2747
2799
|
injectionMode: normalizeInjectionMode(record.injectionMode),
|
|
2748
2800
|
injectionLabel: normalizeInjectionMode(record.injectionMode) === 'session' ? t('按会话启用(实验)') : t('始终注入'),
|
|
2749
|
-
authMode: record.auth?.mode ?? 'none',
|
|
2801
|
+
authMode: record.oauthDiscovery ? 'oauth' : record.auth?.mode ?? 'none',
|
|
2802
|
+
customOAuth: Boolean(record.oauthDiscovery),
|
|
2803
|
+
pendingAuthorization: record.pendingAuthorization === true,
|
|
2750
2804
|
grant: grantInfo,
|
|
2751
2805
|
lastError: record.lastError ?? null,
|
|
2752
|
-
connectionState: record.enabled === false && !legacyMigrationNeedsReauth(record)
|
|
2806
|
+
connectionState: record.pendingAuthorization ? 'authorization-required' : record.enabled === false && !legacyMigrationNeedsReauth(record)
|
|
2753
2807
|
? 'disabled' : diagnostic?.state ?? health?.connectionState ?? 'unknown',
|
|
2754
2808
|
healthCheckedAt: health?.checkedAt ?? null,
|
|
2755
2809
|
lastSuccessfulAt: diagnostic?.lastSuccessfulAt ?? null,
|
|
@@ -3089,6 +3143,7 @@ export async function apply(ctx, config) {
|
|
|
3089
3143
|
async setEnabled(key, enabled) {
|
|
3090
3144
|
const record = state.connections.get(key);
|
|
3091
3145
|
if (!record) return { ok: false, message: t(`连接 "{key}" 不存在`, { key: key }) };
|
|
3146
|
+
if (record.pendingAuthorization && enabled) return { ok: false, message: t('请先点击进行身份验证') };
|
|
3092
3147
|
const next = { ...record, enabled: !!enabled, updatedAt: Date.now() };
|
|
3093
3148
|
if (next.enabled) {
|
|
3094
3149
|
try {
|
|
@@ -3950,7 +4005,7 @@ export async function apply(ctx, config) {
|
|
|
3950
4005
|
? queueConnectionAction(`${connector.id}-${server.serverKey}`, run)
|
|
3951
4006
|
: run();
|
|
3952
4007
|
};
|
|
3953
|
-
const discoveryMutations = new Set(['connect', 'configure', 'importJson', 'installFromUrl', 'reconfigureConnection', 'applyLocalOverrides', 'setEnabled', 'reconnect', 'restoreSnapshot', 'migrateLegacy']);
|
|
4008
|
+
const discoveryMutations = new Set(['authorizeCustom', 'connect', 'configure', 'importJson', 'installFromUrl', 'reconfigureConnection', 'applyLocalOverrides', 'setEnabled', 'reconnect', 'restoreSnapshot', 'migrateLegacy']);
|
|
3954
4009
|
const discoveryApi = new Proxy(api, { get(target, property) {
|
|
3955
4010
|
const value = target[property];
|
|
3956
4011
|
if (!discoveryMutations.has(property)) return value;
|
package/lib/oauth.js
CHANGED
|
@@ -34,7 +34,7 @@ async function fetchJson(url, options = {}, timeoutMs = DEFAULT_REQUEST_TIMEOUT_
|
|
|
34
34
|
const controller = new AbortController();
|
|
35
35
|
const timer = setTimeout(() => controller.abort(new Error('timeout')), timeoutMs);
|
|
36
36
|
try {
|
|
37
|
-
const response = await fetch(url, { ...options, signal: controller.signal });
|
|
37
|
+
const response = await fetch(url, { ...options, redirect: 'error', signal: controller.signal });
|
|
38
38
|
const text = await response.text();
|
|
39
39
|
let body;
|
|
40
40
|
try {
|
|
@@ -77,13 +77,14 @@ function parseWwwAuthenticateParam(header, key) {
|
|
|
77
77
|
}
|
|
78
78
|
|
|
79
79
|
/** 对 stream 端点发一次 initialize,尝试从 WWW-Authenticate 读出 resource_metadata 地址。 */
|
|
80
|
-
async function probeResourceMetadataFromChallenge(streamUrl, timeoutMs) {
|
|
80
|
+
export async function probeResourceMetadataFromChallenge(streamUrl, timeoutMs) {
|
|
81
81
|
try {
|
|
82
82
|
assertSafeUrl(streamUrl);
|
|
83
83
|
const controller = new AbortController();
|
|
84
84
|
const timer = setTimeout(() => controller.abort(new Error('timeout')), timeoutMs);
|
|
85
85
|
const response = await fetch(streamUrl, {
|
|
86
86
|
method: 'POST',
|
|
87
|
+
redirect: 'error',
|
|
87
88
|
headers: {
|
|
88
89
|
'Content-Type': 'application/json',
|
|
89
90
|
Accept: 'application/json, text/event-stream',
|
|
@@ -102,7 +103,8 @@ async function probeResourceMetadataFromChallenge(streamUrl, timeoutMs) {
|
|
|
102
103
|
});
|
|
103
104
|
clearTimeout(timer);
|
|
104
105
|
const auth = response.headers.get('www-authenticate');
|
|
105
|
-
|
|
106
|
+
void response.body?.cancel().catch(() => {});
|
|
107
|
+
return { url: parseWwwAuthenticateParam(auth, 'resource_metadata'), scope: parseWwwAuthenticateParam(auth, 'scope') };
|
|
106
108
|
} catch {
|
|
107
109
|
return null;
|
|
108
110
|
}
|
|
@@ -123,13 +125,14 @@ export function resourceMetadataUrlFallback(streamUrl) {
|
|
|
123
125
|
|
|
124
126
|
export async function discoverProtectedResource(streamUrl, timeoutMs) {
|
|
125
127
|
const fromChallenge = await probeResourceMetadataFromChallenge(streamUrl, timeoutMs);
|
|
126
|
-
const url = fromChallenge ?? resourceMetadataUrlFallback(streamUrl);
|
|
128
|
+
const url = fromChallenge?.url ?? resourceMetadataUrlFallback(streamUrl);
|
|
127
129
|
assertSafeUrl(url);
|
|
128
130
|
const body = await fetchJson(url, { method: 'GET' }, timeoutMs);
|
|
129
131
|
if (!Array.isArray(body.authorization_servers) || body.authorization_servers.length === 0) {
|
|
130
132
|
throw new OAuthError('invalid_metadata', 'protected resource metadata missing authorization_servers');
|
|
131
133
|
}
|
|
132
134
|
return {
|
|
135
|
+
challengeScope: fromChallenge?.scope,
|
|
133
136
|
resource: body.resource,
|
|
134
137
|
authorizationServers: body.authorization_servers,
|
|
135
138
|
scopesSupported: body.scopes_supported ?? [],
|
package/lib/schema.js
CHANGED
|
@@ -122,6 +122,9 @@ export const connectionRecordSchema = z.object({
|
|
|
122
122
|
key: z.string().min(1),
|
|
123
123
|
connectorId: z.string().min(1),
|
|
124
124
|
kind: z.enum(['oauth', 'manual', 'json']),
|
|
125
|
+
authDetection: z.enum(['auto', 'none']).optional(),
|
|
126
|
+
oauthDiscovery: z.object({ issuer: z.string().url(), resource: z.string().url(), scope: z.string() }).optional(),
|
|
127
|
+
pendingAuthorization: z.boolean().optional(),
|
|
125
128
|
name: z.string().min(1),
|
|
126
129
|
serverKey: z.string().min(1).optional(),
|
|
127
130
|
transport: z.enum(['streamable-http', 'sse', 'stdio']),
|
|
@@ -386,6 +389,7 @@ export function normalizeConnectionRecord(raw, { t = tZh } = {}) {
|
|
|
386
389
|
&& data.allowInsecurePrivateNetwork === true;
|
|
387
390
|
return {
|
|
388
391
|
...data,
|
|
392
|
+
...(data.pendingAuthorization ? { enabled: false } : {}),
|
|
389
393
|
transport,
|
|
390
394
|
url: parsedUrl?.toString(),
|
|
391
395
|
allowInsecurePrivateNetwork: allowInsecurePrivateNetwork || undefined,
|
package/lib/status-events.js
CHANGED
package/lib/tools.js
CHANGED
|
@@ -366,7 +366,7 @@ export function registerTools(ctx, api, { compact = false, t = createTranslator(
|
|
|
366
366
|
envJson: { type: 'string', description: t('transport=stdio 时的环境变量 JSON;可能含凭据,仅保存在本机') },
|
|
367
367
|
cwd: { type: 'string', description: t('transport=stdio 时的工作目录;默认 DSH 当前目录') },
|
|
368
368
|
serverName: { type: 'string', description: t('serverName(决定工具名前缀 mcp__<serverName>__*,默认由 name 归一)') },
|
|
369
|
-
authMode: { type: 'string', enum: ['none', 'bearer', 'api-key'], description: t('
|
|
369
|
+
authMode: { type: 'string', enum: ['auto', 'none', 'bearer', 'api-key'], description: t('鉴权方式,默认自动检测 OAuth') },
|
|
370
370
|
bearerToken: { type: 'string', description: t('authMode=bearer 时的 token') },
|
|
371
371
|
apiKeyHeader: { type: 'string', description: t('authMode=api-key 时的头名,默认 X-Api-Key') },
|
|
372
372
|
apiKeyValue: { type: 'string', description: t('authMode=api-key 时的值') },
|
package/lib/web.js
CHANGED
|
@@ -45,6 +45,8 @@ const API_WHITELIST = new Map([
|
|
|
45
45
|
['migrationPreview', (api, p) => api.migrationPreview(p ?? {})],
|
|
46
46
|
['migrateLegacy', (api, p) => api.migrateLegacy(p?.candidateIds ?? [])],
|
|
47
47
|
['connect', (api, p) => api.connect(p?.connectorId, p?.serverKey, undefined, p ?? {})],
|
|
48
|
+
['authorizeCustom', (api, p) => api.authorizeCustom(p?.key)],
|
|
49
|
+
['cancelCustomAuthorization', (api, p) => api.cancelCustomAuthorization(p?.key)],
|
|
48
50
|
['configure', (api, p) => api.configure(p ?? {})],
|
|
49
51
|
['importJson', (api, p) => api.importJson(p?.json, p ?? {})],
|
|
50
52
|
['exportConfig', (api) => api.exportConfig()],
|
package/package.json
CHANGED
|
@@ -1,6 +1,6 @@
|
|
|
1
1
|
{
|
|
2
2
|
"name": "dsh-mcp-connector",
|
|
3
|
-
"version": "0.2.
|
|
3
|
+
"version": "0.2.113",
|
|
4
4
|
"description": "MCP Connector for DeepSeek Harness: a data marketplace connecting enterprise, financial, legal, patent and research data. Manage authorization, search tools and troubleshoot MCP connections. Supports OAuth, API keys and HTTP/stdio.",
|
|
5
5
|
"type": "module",
|
|
6
6
|
"main": "lib/index.js",
|
package/ui/index.html
CHANGED
|
@@ -656,6 +656,14 @@
|
|
|
656
656
|
// 的扁平映射(与 lib/i18n/locales/en/*.js 同一约定)。缺项回退中文原文,绝不空白。
|
|
657
657
|
// 少量同名中文在不同上下文需要不同英文时,用 LABELS 的 key 单独提供词条。
|
|
658
658
|
MESSAGES.en = {
|
|
659
|
+
"进行身份验证": "Authenticate",
|
|
660
|
+
"取消授权": "Cancel authorization",
|
|
661
|
+
"无凭据的 HTTP 服务会自动检测 OAuth;导入后在已安装页逐项进行身份验证,不会同时打开多个授权窗口。": "HTTP services without credentials are checked for OAuth. Authenticate each connection in Installed after import. Authorization windows are not opened in bulk.",
|
|
662
|
+
"只需填写 MCP 地址。检测到 OAuth 后保存为待身份验证,再由你点击授权;无需市场卡片地址。": "Enter the MCP URL. If OAuth is detected, save and click Authenticate. No marketplace card URL is needed.",
|
|
663
|
+
"自动检测认证(含 OAuth)": "Detect authentication (including OAuth)",
|
|
664
|
+
"正在授权…": "Authorizing\u2026",
|
|
665
|
+
"待身份验证": "Authentication required",
|
|
666
|
+
|
|
659
667
|
"如何获取 TuShare Token": "How to get a TuShare Token",
|
|
660
668
|
"connect": "Connect",
|
|
661
669
|
"切换界面语言": "Change interface language",
|
|
@@ -1288,7 +1296,6 @@
|
|
|
1288
1296
|
'my-server': {
|
|
1289
1297
|
type: 'streamable-http',
|
|
1290
1298
|
url: 'https://example.com/mcp',
|
|
1291
|
-
headers: { Authorization: 'Bearer YOUR_ACCESS_TOKEN' },
|
|
1292
1299
|
},
|
|
1293
1300
|
'local-server': {
|
|
1294
1301
|
type: 'stdio',
|
|
@@ -2666,7 +2673,7 @@
|
|
|
2666
2673
|
const canRename = r.canRename === true;
|
|
2667
2674
|
const canEditConfiguration = r.canEditConfiguration === true;
|
|
2668
2675
|
const authMode = r.authMode === 'oauth' ? `<span class="badge auth-oauth">OAuth</span>` : `<span class="badge">${esc(r.authMode || 'manual')}</span>`;
|
|
2669
|
-
const healthLabels = { healthy: '已连接', unknown: '状态未知', configured: '已配置', reauth: '需重新授权', recovering: '自动重试中', degraded: '部分异常', unavailable: '连接异常', disabled: '已停用' };
|
|
2676
|
+
const healthLabels = { 'authorization-required': '待身份验证', healthy: '已连接', unknown: '状态未知', configured: '已配置', reauth: '需重新授权', recovering: '自动重试中', degraded: '部分异常', unavailable: '连接异常', disabled: '已停用' };
|
|
2670
2677
|
const healthClass = r.connectionState === 'healthy' ? 'pass' : ['reauth', 'recovering', 'degraded'].includes(r.connectionState) ? 'partial' : r.connectionState === 'unavailable' ? 'fail' : '';
|
|
2671
2678
|
const healthBadge = `<span class="badge ${healthClass}">${esc(t(healthLabels[r.connectionState] || '状态未知'))}</span>`;
|
|
2672
2679
|
const scopeBadge = `<span class="badge">${esc(t(r.scope?.label || '全局'))}</span>`;
|
|
@@ -2687,15 +2694,16 @@
|
|
|
2687
2694
|
<option value="session" ${injectionMode === 'session' ? 'selected' : ''}>${t('按会话启用(实验)')}</option>
|
|
2688
2695
|
</select>
|
|
2689
2696
|
<label class="switch" title="${t(enabled ? '停用' : '启用')}" aria-label="${t(enabled ? '停用' : '启用')} ${esc(r.name)}">
|
|
2690
|
-
<input type="checkbox" ${enabled ? 'checked' : ''} onchange="window.__mcp.toggle(${keyJs}, this.checked)">
|
|
2697
|
+
<input type="checkbox" ${r.pendingAuthorization ? 'disabled' : ''} ${enabled ? 'checked' : ''} onchange="window.__mcp.toggle(${keyJs}, this.checked)">
|
|
2691
2698
|
<span class="slider"></span>
|
|
2692
2699
|
</label>
|
|
2693
2700
|
${canEditConfiguration ? `<button class="btn ghost" type="button" onclick="window.__mcp.openEditor(${keyJs})">${t('编辑配置')}</button>` : ''}
|
|
2694
2701
|
${r.canEditLocalOverrides ? `<button class="btn ghost" type="button" onclick="window.__mcp.openLocalEditor(${keyJs})">${t('本地参数')}</button>` : r.hasLocalOverrides ? `<button class="btn ghost" type="button" onclick="window.__mcp.submitLocalOverrides(${keyJs}, true)">${t('清除本地参数')}</button>` : ''}
|
|
2695
2702
|
${canRename ? `<button class="btn ghost" type="button" onclick="window.__mcp.openRename(${keyJs})">${t('重命名')}</button>` : ''}
|
|
2696
2703
|
${enabled ? `<button class="btn ghost" type="button" onclick="window.__mcp.showConnectionTools(${keyJs})">${t('工具')}</button>` : ''}
|
|
2704
|
+
${r.customOAuth && (r.pendingAuthorization || r.connectionState === 'reauth') ? `<button class="btn" type="button" onclick="window.__mcp.authorizeCustom(${keyJs}, this)">${t('进行身份验证')}</button><button class="btn ghost" type="button" onclick="window.__mcp.cancelCustomAuthorization(${keyJs})">${t('取消授权')}</button>` : ''}
|
|
2697
2705
|
${r.diagnostic?.legacyConflict ? `<button class="btn status-bad" type="button" onclick="window.__mcp.showConnectionTools(${keyJs})">${t('查看处理步骤')}</button>`
|
|
2698
|
-
: r.connectionState === 'reauth' && r.authMode === 'oauth' ? `<button class="btn" type="button" onclick="window.__mcp.reauthorize(${jsString(r.connectorId)})">${t('reauthorize')}</button>`
|
|
2706
|
+
: !r.customOAuth && r.connectionState === 'reauth' && r.authMode === 'oauth' ? `<button class="btn" type="button" onclick="window.__mcp.reauthorize(${jsString(r.connectorId)})">${t('reauthorize')}</button>`
|
|
2699
2707
|
: enabled && r.connectionState !== 'healthy' ? `<button class="btn ghost" type="button" title="${t('重新建立 Host 侧条目并复检:不改配置、凭据、范围或注入模式')}" onclick="window.__mcp.reconnect(${keyJs})">${t('重新连接')}</button>` : ''}
|
|
2700
2708
|
<button class="btn ghost" type="button" onclick="window.__mcp.openScope(${keyJs})">${t('范围')}</button>
|
|
2701
2709
|
<button class="btn danger" onclick="window.__mcp.disconnect(${keyJs})">${t('断开')}</button>
|
|
@@ -2875,6 +2883,7 @@
|
|
|
2875
2883
|
<div class="field-label-row"><label for="import-json">${t('粘贴 MCP JSON')}</label><button class="text-btn" type="button" onclick="window.__mcp.formatImportJson(false)">${t('格式化 JSON')}</button></div>
|
|
2876
2884
|
<textarea id="import-json" rows="8" spellcheck="false" placeholder="${esc(MCP_JSON_EXAMPLE)}" onpaste="setTimeout(() => window.__mcp.formatImportJson(true), 0)"></textarea>
|
|
2877
2885
|
<div class="field-help">${t('支持 {code} 的 Streamable HTTP、SSE 与 stdio(command/args/env/cwd),配置和凭据仅保存在 DSH 本机。私有 IP 明文 HTTP 必须在对应条目显式设置 {flag}。', { code: `<code>mcpServers</code>`, flag: `<code>"allowInsecurePrivateNetwork": true</code>` })}</div>
|
|
2886
|
+
<p class="field-help">${t('无凭据的 HTTP 服务会自动检测 OAuth;导入后在已安装页逐项进行身份验证,不会同时打开多个授权窗口。')}</p>
|
|
2878
2887
|
${scopeFieldHtml()}
|
|
2879
2888
|
<div class="inline-error" id="modal-error" tabindex="-1"></div>
|
|
2880
2889
|
<div class="m-actions"><button class="btn ghost" type="button" onclick="window.__mcp.closeModal()">${t('取消')}</button><button class="btn" type="button" onclick="window.__mcp.submitImport()">${t('校验并导入')}</button></div>`);
|
|
@@ -2891,7 +2900,7 @@
|
|
|
2891
2900
|
<div class="m-actions"><button class="btn ghost" type="button" onclick="window.__mcp.closeModal()">${t('取消')}</button><button class="btn" type="button" onclick="window.__mcp.submitUrl()">${t('验证并安装')}</button></div>`);
|
|
2892
2901
|
return;
|
|
2893
2902
|
}
|
|
2894
|
-
const suggestedAuth = preset.authMode === 'bearer' || preset.authMode === 'api-key' ? preset.authMode : '
|
|
2903
|
+
const suggestedAuth = preset.authMode === 'bearer' || preset.authMode === 'api-key' ? preset.authMode : 'auto';
|
|
2895
2904
|
openModal(t('添加 MCP 连接'), `${addTabs(mode)}
|
|
2896
2905
|
<p class="field-help">${t('适合私有、内网或暂未上架的 MCP Server。凭据只写入 DSH 本机 storage domain。')}</p>
|
|
2897
2906
|
${scopeFieldHtml()}
|
|
@@ -2899,10 +2908,10 @@
|
|
|
2899
2908
|
<div><label for="cfg-sname">serverName${t('(工具前缀)')}</label><input id="cfg-sname" value="${esc(server.serverName || '')}" placeholder="my-server" /></div></div>
|
|
2900
2909
|
<label for="cfg-transport">${t('传输方式')}</label><select id="cfg-transport" onchange="window.__mcp.syncTransportFields()"><option value="streamable-http">${t('Streamable HTTP(兼容 SSE)')}</option><option value="stdio">${t('stdio(本地进程)')}</option></select>
|
|
2901
2910
|
<div id="cfg-http-fields">
|
|
2902
|
-
<label for="cfg-url">${t('MCP URL(必填)')}</label><input id="cfg-url" type="url" value="${esc(server.url || '')}" placeholder="https://example.com/mcp" />
|
|
2911
|
+
<p class="field-help">${t('只需填写 MCP 地址。检测到 OAuth 后保存为待身份验证,再由你点击授权;无需市场卡片地址。')}</p><label for="cfg-url">${t('MCP URL(必填)')}</label><input id="cfg-url" type="url" value="${esc(server.url || '')}" placeholder="https://example.com/mcp" />
|
|
2903
2912
|
<label class="insecure-network-consent" for="cfg-allow-insecure-lan"><input id="cfg-allow-insecure-lan" type="checkbox" />${t('我确认这是可信的局域网私有 IP,并接受 HTTP 传输可被同网段监听或篡改的风险。')}</label>
|
|
2904
2913
|
<div class="field-help">${t('仅放行 10/8、172.16/12、192.168/16 和 IPv6 ULA 字面量;域名、公网 HTTP、链路本地与云元数据地址仍会被拒绝。')}</div>
|
|
2905
|
-
<label for="cfg-auth">${t('鉴权方式')}</label><select id="cfg-auth" onchange="window.__mcp.syncAuthFields()"><option value="none" ${suggestedAuth === 'none' ? 'selected' : ''}>${t('无鉴权')}</option><option value="bearer" ${suggestedAuth === 'bearer' ? 'selected' : ''}>Bearer Token</option><option value="api-key" ${suggestedAuth === 'api-key' ? 'selected' : ''}>API Key</option></select>
|
|
2914
|
+
<label for="cfg-auth">${t('鉴权方式')}</label><select id="cfg-auth" onchange="window.__mcp.syncAuthFields()"><option value="auto" ${suggestedAuth === 'auto' ? 'selected' : ''}>${t('自动检测认证(含 OAuth)')}</option><option value="none" ${suggestedAuth === 'none' ? 'selected' : ''}>${t('无鉴权')}</option><option value="bearer" ${suggestedAuth === 'bearer' ? 'selected' : ''}>Bearer Token</option><option value="api-key" ${suggestedAuth === 'api-key' ? 'selected' : ''}>API Key</option></select>
|
|
2906
2915
|
<div id="cfg-bearer"><label for="cfg-token">Bearer Token${t('(必填)')}</label><input id="cfg-token" type="password" autocomplete="off" placeholder="${t('仅保存在本机')}" /></div>
|
|
2907
2916
|
<div id="cfg-apikey" class="form-row"><div><label for="cfg-key-header">API Key Header</label><input id="cfg-key-header" value="${esc(preset.authMode === 'api-key' ? 'X-Api-Key' : '')}" placeholder="X-Api-Key" /></div><div><label for="cfg-key-value">API Key${t('(必填)')}</label><input id="cfg-key-value" type="password" autocomplete="off" placeholder="${t('仅保存在本机')}" /></div></div>
|
|
2908
2917
|
<label for="cfg-headers">${t('额外 Headers(可选 JSON)')}</label><textarea id="cfg-headers" rows="2" spellcheck="false" placeholder='{"X-Tenant":"team-a"}'></textarea>
|
|
@@ -2966,6 +2975,20 @@
|
|
|
2966
2975
|
}
|
|
2967
2976
|
|
|
2968
2977
|
window.__mcp = {
|
|
2978
|
+
async authorizeCustom(key, button) {
|
|
2979
|
+
button.disabled = true;
|
|
2980
|
+
button.textContent = t('正在授权…');
|
|
2981
|
+
try {
|
|
2982
|
+
const result = await call('authorizeCustom', { key }, { timeoutMs: 310_000 });
|
|
2983
|
+
showToast(result.message, result.ok);
|
|
2984
|
+
await refresh();
|
|
2985
|
+
} catch (error) { showToast(error.message, false); }
|
|
2986
|
+
finally { button.disabled = false; button.textContent = t('进行身份验证'); }
|
|
2987
|
+
},
|
|
2988
|
+
async cancelCustomAuthorization(key) {
|
|
2989
|
+
const result = await call('cancelCustomAuthorization', { key });
|
|
2990
|
+
showToast(result.message, result.ok);
|
|
2991
|
+
},
|
|
2969
2992
|
async connect(connectorId) {
|
|
2970
2993
|
if ($('#scope-connector-id')?.value !== connectorId) {
|
|
2971
2994
|
openConnectScope(connectorId);
|
|
@@ -3312,7 +3335,7 @@
|
|
|
3312
3335
|
setModalBusy(false);
|
|
3313
3336
|
if (!r.ok) { showModalError(r.message); return; }
|
|
3314
3337
|
markCommunityCtaEligible();
|
|
3315
|
-
closeModal(); showToast(r.message, true); await refresh();
|
|
3338
|
+
closeModal(); showToast(r.message, true); if (r.detail?.pendingAuthorization) { view = 'installed'; syncTabs(); } await refresh();
|
|
3316
3339
|
},
|
|
3317
3340
|
async submitImport() {
|
|
3318
3341
|
let json = $('#import-json').value.trim();
|