dsh-completion-guard 0.4.0 → 0.4.2
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/CHANGELOG.md +17 -2
- package/CHANGELOG.zh-CN.md +17 -2
- package/README.md +51 -11
- package/README.zh-CN.md +51 -11
- package/dist/domain/index.d.ts +2 -2
- package/dist/domain/index.js +2 -2
- package/dist/{domain-CHTQFIT8.js → domain-BXB_BPQg.js} +548 -120
- package/dist/{index-AtjJOrK8.d.ts → index-DNF0OTi-.d.ts} +65 -4
- package/dist/index.d.ts +2 -2
- package/dist/index.js +371 -96
- package/docs/ARCHITECTURE.md +19 -1
- package/docs/COMPATIBILITY.md +22 -5
- package/docs/LOCAL_ACCEPTANCE.md +63 -1
- package/docs/SEMANTIC_COMPATIBILITY.md +25 -2
- package/docs/distribution.md +23 -8
- package/docs/upstream-deltas.json +81 -180
- package/manifests/supported-host.v1.json +209 -0
- package/package.json +9 -9
package/CHANGELOG.md
CHANGED
|
@@ -2,13 +2,28 @@
|
|
|
2
2
|
|
|
3
3
|
All notable changes to this project are documented here. The project is pre-1.0; release versions track the plugin lifecycle, not stabilised API promises.
|
|
4
4
|
|
|
5
|
+
## 0.4.2 - Unreleased
|
|
6
|
+
|
|
7
|
+
- Explain when a task cannot be certified and what the user can clarify. Generic command success still cannot prove an update or a GUI result.
|
|
8
|
+
- Add `context_guard_rebind`: propose a complete split of an old requirement, optionally link a later explicit root-user clarification, then replace it only after the user's exact confirmation. Old sources, unsupported remainders, and one-to-many relationships remain visible; the proposal grants no execution permission.
|
|
9
|
+
- Bound checkpoint pages to 12 KiB and focus default evidence on the current action and target. Item, evidence, and history queries have independent continuation cursors; the full contract is still checked.
|
|
10
|
+
- Reserve recovery space for current constraints, refusal reasons, next steps, and completion rules. Unrelated evidence no longer repeats the same guidance; compact and resume still recover the current state.
|
|
11
|
+
- Add an isolated host-bound native entrypoint with nonempty tool calls and lifecycle checks. Acceptance is bound to the exact candidate and package; see [acceptance scope](docs/LOCAL_ACCEPTANCE.md).
|
|
12
|
+
|
|
13
|
+
- Align npm chart date labels with centered anchors and a fixed day interval, preserve real first-day downloads, and distinguish repeat-checked coverage from API availability.
|
|
14
|
+
|
|
15
|
+
## 0.4.1-rc.1 - 2026-09-04
|
|
16
|
+
|
|
17
|
+
- Add the exact DSH `0.1.2-rc.1` + dshmarket `1.41.0` host cohort for macOS/posix and Windows. The Windows host graph was audited on the native Windows rc.1 runtime; host-graph audits do not replace the cross-platform exact-artifact acceptance of one frozen package.
|
|
18
|
+
- Read session history through the rc.1 `snapshotEvents()` API while retaining the legacy `events` path for previously audited DSH cohorts.
|
|
19
|
+
|
|
5
20
|
## 0.4.0 - 2026-09-02
|
|
6
21
|
|
|
7
22
|
### Added
|
|
8
23
|
|
|
9
24
|
- **DSH alpha.3 is the 0.4.0 implementation baseline.** Version 0.4.0 targets DSH `0.1.2-alpha.3` with dshmarket `1.39.0` and Cordis `4.0.2`.
|
|
10
|
-
- **
|
|
11
|
-
- **
|
|
25
|
+
- **Evidence must prove the unfinished work the user actually requested.** Reading or checking another target cannot close the item. Evidence from another session, evidence for the wrong action or target, and evidence that does not show the required result are rejected.
|
|
26
|
+
- **Changed or damaged proof records cannot be reused.** If the recorded files, task scope, or saved state no longer match, the proof becomes invalid and the work stays open. The Guard keeps only the bounded facts needed for this check, not raw private logs or file contents.
|
|
12
27
|
- **Stage disposition.** The stopped 0.3.3 compatibility candidate is recorded as `superseded_before_candidate`; no 0.3.3 source, artifact, installation, native acceptance, commit, tag, or release existed.
|
|
13
28
|
|
|
14
29
|
### Changed
|
package/CHANGELOG.zh-CN.md
CHANGED
|
@@ -2,13 +2,28 @@
|
|
|
2
2
|
|
|
3
3
|
本项目的重要变化记录在这里。项目仍处于 1.0 之前;版本号跟踪插件生命周期,不代表 API 已稳定。
|
|
4
4
|
|
|
5
|
+
## 0.4.2 - 未发布
|
|
6
|
+
|
|
7
|
+
- 对不能认证的任务说明原因和澄清方法。普通命令成功仍不能证明更新完成或 GUI 效果正确。
|
|
8
|
+
- 新增 `context_guard_rebind`:提出完整的旧要求拆分方案,可关联用户随后明确给出的澄清要求;只有用户精确确认后才替代旧项。保留旧来源、未支持部分和一对多关系,提案本身不授予执行权限。
|
|
9
|
+
- checkpoint 每页不超过 12 KiB,默认只列当前动作和对象相关的证据。要求、证据和历史分别分页,但认证仍检查完整合同。
|
|
10
|
+
- 恢复时为当前限制、拒绝原因、下一步和完成规则预留空间。无关证据不会重复触发同一提示,compact 与 resume 仍恢复当前状态。
|
|
11
|
+
- 增加隔离的宿主原生验收入口,包含非空工具调用和生命周期检查。验收绑定精确候选和包,详见[验收范围](docs/LOCAL_ACCEPTANCE.md)。
|
|
12
|
+
|
|
13
|
+
- 修正 npm 图表日期标签:统一居中与固定天数间隔,保留首日真实下载数,并区分已复查区间和 API 可用日期。
|
|
14
|
+
|
|
15
|
+
## 0.4.1-rc.1 - 2026-09-04
|
|
16
|
+
|
|
17
|
+
- 新增精确的 DSH `0.1.2-rc.1` + dshmarket `1.41.0` 宿主队列,覆盖 macOS/posix 与 Windows。Windows 宿主图谱已在原生 Windows rc.1 运行时上审计;宿主图谱审计不能替代同一冻结包的跨平台 exact-artifact acceptance。
|
|
18
|
+
- 通过 rc.1 的 `snapshotEvents()` API 读取会话历史,同时保留此前已审计 DSH 队列使用的旧版 `events` 路径。
|
|
19
|
+
|
|
5
20
|
## 0.4.0 - 2026-09-02
|
|
6
21
|
|
|
7
22
|
### 新增
|
|
8
23
|
|
|
9
24
|
- **DSH alpha.3 成为 0.4.0 的实现基线。** 0.4.0 面向 DSH `0.1.2-alpha.3`、dshmarket `1.39.0` 和 Cordis `4.0.2`。
|
|
10
|
-
-
|
|
11
|
-
-
|
|
25
|
+
- **证据必须证明用户实际要求、而且仍未完成的工作。** 读取或检查另一个目标不能关闭当前事项;来自其他会话、动作或目标不匹配、没有显示所需结果的证据都会被拒绝。
|
|
26
|
+
- **变化或损坏的证明记录不能继续复用。** 一旦已记录文件、任务范围或保存状态不再匹配,证明就会失效,工作继续保持未完成。Guard 只保留完成核对所需的有限事实,不保存原始私有日志或文件内容。
|
|
12
27
|
- **阶段处置记录。** 已停止的 0.3.3 兼容候选明确记为 `superseded_before_candidate`;该阶段不存在 0.3.3 源码、工件、安装、原生验收、提交、tag 或 release。
|
|
13
28
|
|
|
14
29
|
### 变更
|
package/README.md
CHANGED
|
@@ -8,13 +8,13 @@ An add-on for DeepSeek Harness (DSH) that keeps a task's requirements and checks
|
|
|
8
8
|
|
|
9
9
|
## Quick start
|
|
10
10
|
|
|
11
|
-
Install the published plugin into
|
|
11
|
+
Install the published plugin into the DSH Web environment:
|
|
12
12
|
|
|
13
13
|
```sh
|
|
14
14
|
dsh plugin --profile web add dsh-completion-guard@0.4.0
|
|
15
15
|
```
|
|
16
16
|
|
|
17
|
-
Before restarting DSH, record and verify the
|
|
17
|
+
Before restarting DSH, record and verify the DSH program directory and the Web settings directory. Replace the example paths with the absolute paths on your machine:
|
|
18
18
|
|
|
19
19
|
```sh
|
|
20
20
|
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
@@ -28,7 +28,7 @@ dsh --profile web --dump-config > "$DSH_COMPOSED_DUMP"
|
|
|
28
28
|
"$GUARD_HOST_LOCK" verify-dump --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT" --dump-config "$DSH_COMPOSED_DUMP"
|
|
29
29
|
```
|
|
30
30
|
|
|
31
|
-
On Windows, run the same three subcommands through `dsh-completion-guard-host-lock.cmd` in the
|
|
31
|
+
On Windows, run the same three subcommands through `dsh-completion-guard-host-lock.cmd` in the Web settings directory's `node_modules\.bin` directory and use Windows absolute paths. Repeat this check after upgrading DSH, its Web or Headless settings, or the package. The Guard stays unavailable if the active package set is missing, mixed, duplicated, or different from a checked setup.
|
|
32
32
|
|
|
33
33
|
Restart DSH Web, open a session, and enable the Guard:
|
|
34
34
|
|
|
@@ -49,21 +49,32 @@ Activation is opt-in by default. `status` shows whether the Guard is on and how
|
|
|
49
49
|
|
|
50
50
|
## Status and compatibility
|
|
51
51
|
|
|
52
|
-
|
|
52
|
+
The installation example uses the recorded 0.4.0 release baseline. Install it from [npm](https://www.npmjs.com/package/dsh-completion-guard); its [GitHub Release](https://github.com/GreenLv/dsh-completion-guard/releases/tag/v0.4.0) carries the exact package checksum and native macOS and Windows acceptance records. It targets DSH `0.1.2-alpha.3` with dshmarket `1.39.0` and Cordis `4.0.2`.
|
|
53
|
+
|
|
54
|
+
The source tree now targets **0.4.2 (unreleased)**. It adds bounded checkpoint queries and root-user-confirmed requirement rebinding. The published installation example above does not install these candidate changes. Acceptance is bound to each frozen package; earlier candidate results do not cover later documentation or package changes. See [the changelog](CHANGELOG.md) and [acceptance scope](docs/LOCAL_ACCEPTANCE.md).
|
|
55
|
+
|
|
56
|
+
Version `0.4.1-rc.1` is the published `next` prerelease for DSH `0.1.2-rc.1` with dshmarket `1.41.0`. Its host cohort is audited on native macOS/posix and against the native Windows rc.1 host graph; host-graph audits do not replace the cross-platform exact-artifact acceptance of one frozen package. See [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md).
|
|
53
57
|
|
|
54
58
|
Version 0.3.2 remains available for the checked DSH `0.1.1-rc.2` and `0.1.2-alpha.2` setups. Do not combine packages from different checked setups; the Guard fails closed when the active package set does not match one complete cohort in [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md).
|
|
55
59
|
|
|
56
|
-
Version 0.4.0 remains frozen on this alpha.3 setup. Alpha.4 and later alpha releases
|
|
60
|
+
Version 0.4.0 remains frozen on this alpha.3 setup. Alpha.4 and later alpha releases were skipped. RC adaptation resumed with DSH `0.1.2-rc.1`, supported by the `0.4.1-rc.1` prerelease and retained in the 0.4.2 candidate. Follow upstream releases on the [DeepSeek Harness tags page](https://github.com/deepseek-ai/deepseek-harness/tags).
|
|
57
61
|
|
|
58
62
|
Release packages are built once from a clean commit and published only after those exact bytes pass native macOS and Windows Web and Headless checks. CI, native lifecycle checks, package publication, and public readback remain separate evidence scopes; see [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md).
|
|
59
63
|
|
|
60
|
-
Version 0.3.0 is not recommended. Its package passed native checks, but npm did not record the required source commit, so the version cannot be repaired in place and has no GitHub Release. Use 0.3.2.
|
|
64
|
+
Version 0.3.0 is not recommended. Its package passed native checks, but npm did not record the required source commit, so the version cannot be repaired in place and has no GitHub Release. Use 0.3.2 for the older checked DSH setups, or choose the release matching your host from the compatibility guide.
|
|
61
65
|
|
|
62
66
|
> The project was renamed from `dsh-context-guard` to `dsh-completion-guard` on 2026-08-29 because an unrelated plugin already used the old name. The internal bundle id remains `context-guard`, and the old npm package points users to this one. Supported DSH setups are listed in [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md); Node.js `>=22` and pnpm `>=11` are required.
|
|
63
67
|
|
|
64
68
|
## Activation modes
|
|
65
69
|
|
|
66
|
-
|
|
70
|
+
Context Guard has two activation modes:
|
|
71
|
+
|
|
72
|
+
- `opt-in` (default): protection is off when a session starts. Run `/context-guard on` in that session to turn it on, and `/context-guard off` to turn it off again. This changes only the current session.
|
|
73
|
+
- `always`: DSH sessions are protected automatically. Running `/context-guard off` turns protection off only for that session; other sessions start with protection on.
|
|
74
|
+
|
|
75
|
+
These modes only control Guard protection. They are not the DSH session mode (for example, the standard or minimal mode) that a session starts with. With `always`, the Guard loads before each DSH session starts. DSH currently cannot switch a session's mode after the session has started, so a session protected this way keeps the DSH session mode it started with. `/context-guard on` and `/context-guard off` turn Guard protection on or off; they never change the DSH session mode.
|
|
76
|
+
|
|
77
|
+
To make DSH sessions start with protection on, add this entry to the `cordis.patch.yml` used by the way you start DSH:
|
|
67
78
|
|
|
68
79
|
```yaml
|
|
69
80
|
- id: context-guard
|
|
@@ -72,7 +83,22 @@ The default `opt-in` mode protects a session only after `/context-guard on`. To
|
|
|
72
83
|
activation: always
|
|
73
84
|
```
|
|
74
85
|
|
|
75
|
-
|
|
86
|
+
DSH can run with a **Web** interface in a browser, or **Headless** without a browser interface from a terminal or an automated task. These two ways of running DSH use separate settings files. Edit the file for the one you use, or edit both if you use both:
|
|
87
|
+
|
|
88
|
+
| System | How you use DSH | Default path |
|
|
89
|
+
| --- | --- | --- |
|
|
90
|
+
| macOS / Linux | Web | `$HOME/.dsh/profiles/web/cordis.patch.yml` |
|
|
91
|
+
| macOS / Linux | Headless | `$HOME/.dsh/profiles/headless/cordis.patch.yml` |
|
|
92
|
+
| Windows | Web | `%USERPROFILE%\.dsh\profiles\web\cordis.patch.yml` |
|
|
93
|
+
| Windows | Headless | `%USERPROFILE%\.dsh\profiles\headless\cordis.patch.yml` |
|
|
94
|
+
|
|
95
|
+
If you set a custom `DSH_HOME`, use that directory instead of `$HOME/.dsh` or `%USERPROFILE%\.dsh`.
|
|
96
|
+
|
|
97
|
+
You can also paste this prompt into DSH and let it make the change:
|
|
98
|
+
|
|
99
|
+
> Set `dsh-completion-guard` to `always` mode. Find the `cordis.patch.yml` used by the way I am currently running DSH (Web interface or Headless), back it up first, and only set `activation: always` on the entry with `id: context-guard`. Do not change any other settings or restart DSH. When finished, show me the file path and the exact diff.
|
|
100
|
+
|
|
101
|
+
After the change, restart DSH.
|
|
76
102
|
|
|
77
103
|
## How completion is checked
|
|
78
104
|
|
|
@@ -80,6 +106,14 @@ Once enabled, the Guard saves direct user requirements and acceptance checks. A
|
|
|
80
106
|
|
|
81
107
|
Read-only evidence collection and actions that change packages, files, services, or Git state use separate tools. A successful lookup never grants permission to make a change. Exact command limits and platform evidence are documented in [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md).
|
|
82
108
|
|
|
109
|
+
### When a requirement stays incomplete (0.4.2 candidate)
|
|
110
|
+
|
|
111
|
+
“Update the plugin and check the GUI” can contain work the Guard cannot certify. The checkpoint reports a reason and a next step for each item. A `generic_run_non_certifiable` result means that changing the binding or running another ordinary command cannot close that item.
|
|
112
|
+
|
|
113
|
+
Use `context_guard_rebind` to propose an exact, complete split of the old text. If the action or target needs clarification, first ask the root user for an explicit instruction that includes the original clause; the proposal can reference that new item's ID. The tool returns a proposal ID and a comparison. Only the user's exact reply `确认重绑定 <proposal ID>` applies it. Quoted text, tool output, and model confirmation flags do not count. Unsupported parts remain pending, and a qualified safe end does not mean all work is complete.
|
|
114
|
+
|
|
115
|
+
The default `context_guard_checkpoint` call uses `bindings: []` for diagnosis. It shows at most eight current items/constraints and ten evidence rows, within 12 KiB of plugin JSON. `pagination` reports totals and a separate `next_cursor` for each list; the first page is not the whole contract. Use `item_ids` or `evidence_ids` to focus a query, or `evidence_scope: "history"` for the complete evidence history, including rows marked unavailable. Keep the query unchanged when following a cursor; a changed contract or evidence snapshot requires a fresh query. Large rows expose `detail_id`; retrieve chunks with `detail_offset` and return the first response's `snapshot` as `detail_snapshot` on later chunks. All queries remain read-only and never shrink the certification set.
|
|
116
|
+
|
|
83
117
|
## Boundaries
|
|
84
118
|
|
|
85
119
|
Context Guard certifies completion; DSH still owns Goal, Todo, Compaction, continuation, permissions, and tool execution. This plugin is not a security sandbox, semantic proof system, token-pruning tool, or replacement for those DSH facilities.
|
|
@@ -90,7 +124,9 @@ Evidence is bounded and redacted. Complete prompts, stdout, file contents, crede
|
|
|
90
124
|
|
|
91
125
|
This project began as a DSH port of deterministic behavior from [`GreenLv/codex-context-guard`](https://github.com/GreenLv/codex-context-guard) v0.8.8. That version is the historical starting point, not the current compatibility level.
|
|
92
126
|
|
|
93
|
-
|
|
127
|
+
Version 0.4.0 was deliberately aligned with the shared evidence rules in Codex Context Guard 0.10.0: proof must belong to work that is still open and must show the operation, target, and result the user actually requested. This is a limited behavior-level alignment, not a claim that the two products have the same features.
|
|
128
|
+
|
|
129
|
+
Codex Context Guard 0.11.0 was released afterward. DSH 0.4.0 already has native checks for exact mutation targets, typed waits, and quoted text, but it does not yet include the full 0.11.0 authorization-ticket, work-unit, supersession, or incident-benchmark changes. The plain-language comparison and dated delta ledger are in [`docs/SEMANTIC_COMPATIBILITY.md`](docs/SEMANTIC_COMPATIBILITY.md).
|
|
94
130
|
|
|
95
131
|
The two repositories serve different runtimes:
|
|
96
132
|
|
|
@@ -103,7 +139,11 @@ They do not share runtime state, installers, caches, or release histories. Fixes
|
|
|
103
139
|
|
|
104
140
|
|
|
105
141
|
|
|
106
|
-
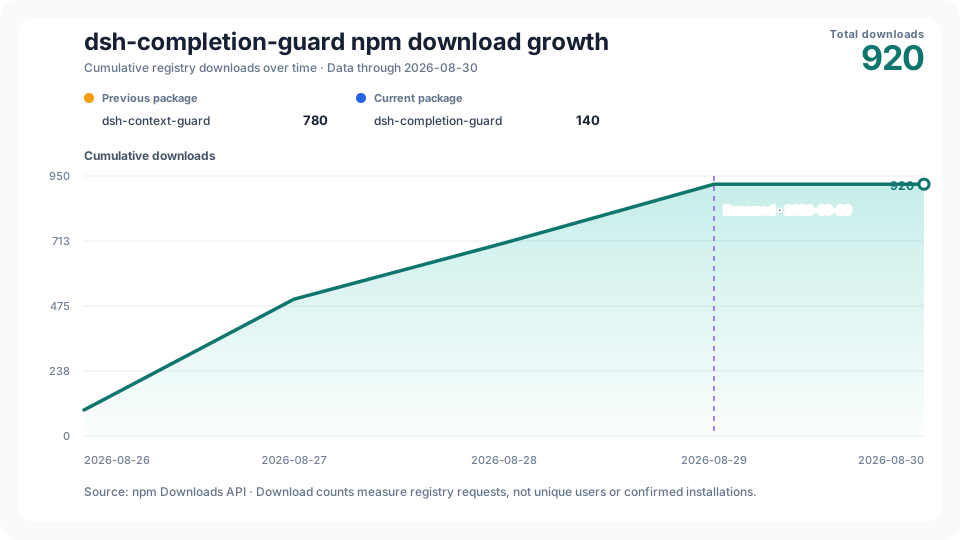
The cumulative chart keeps the old and new npm package totals visibly separate, marks the 2026-08-29 rename, and combines them only for the project growth line. npm download counts measure registry requests; they are not counts of unique users or confirmed installations.
|
|
142
|
+
The cumulative chart keeps the old and new npm package totals visibly separate, marks the 2026-08-29 rename, and combines them only for the project growth line. npm download counts measure registry requests; they are not counts of unique users or confirmed installations.
|
|
143
|
+
|
|
144
|
+
History starts on the first public npm release day, 2026-08-26; its real first-day count is retained even when nonzero. The vertical axis starts at zero. Date labels share one fixed day interval and centered anchors; the caption always gives the exact coverage end.
|
|
145
|
+
|
|
146
|
+
The daily workflow publishes through the last day whose counts are unchanged in checks at least 12 hours apart and at least two UTC calendar days old. The API availability date is shown separately; this observation rule is not an npm guarantee that counts will never change. See the [source data](https://raw.githubusercontent.com/GreenLv/dsh-completion-guard/stats/npm-downloads.json).
|
|
107
147
|
|
|
108
148
|
## Documentation
|
|
109
149
|
|
|
@@ -129,4 +169,4 @@ pnpm run build
|
|
|
129
169
|
pnpm run pack:check
|
|
130
170
|
```
|
|
131
171
|
|
|
132
|
-
These commands validate a local source tree and package. CI, native-platform acceptance, npm publication, GitHub release identity, and
|
|
172
|
+
These commands validate a local source tree and package. CI, native-platform acceptance, npm publication, GitHub release identity, and installation in a live DSH environment remain separate evidence scopes.
|
package/README.zh-CN.md
CHANGED
|
@@ -8,13 +8,13 @@
|
|
|
8
8
|
|
|
9
9
|
## 快速开始
|
|
10
10
|
|
|
11
|
-
将已发布插件安装到 DSH Web
|
|
11
|
+
将已发布插件安装到 DSH 的 Web 运行环境:
|
|
12
12
|
|
|
13
13
|
```sh
|
|
14
14
|
dsh plugin --profile web add dsh-completion-guard@0.4.0
|
|
15
15
|
```
|
|
16
16
|
|
|
17
|
-
重启 DSH
|
|
17
|
+
重启 DSH 前,先记录并验证 DSH 程序目录和 Web 配置目录。请把示例路径替换为本机绝对路径:
|
|
18
18
|
|
|
19
19
|
```sh
|
|
20
20
|
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
@@ -28,7 +28,7 @@ dsh --profile web --dump-config > "$DSH_COMPOSED_DUMP"
|
|
|
28
28
|
"$GUARD_HOST_LOCK" verify-dump --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT" --dump-config "$DSH_COMPOSED_DUMP"
|
|
29
29
|
```
|
|
30
30
|
|
|
31
|
-
Windows 请通过
|
|
31
|
+
Windows 请通过 Web 配置目录下的 `node_modules\.bin\dsh-completion-guard-host-lock.cmd` 运行相同的三个子命令,并使用 Windows 绝对路径。DSH、Web/Headless 配置或包升级后需要重新检查。如果当前包集合缺失、混装、重复或不属于已检查环境,Guard 会保持不可用。
|
|
32
32
|
|
|
33
33
|
然后重启 DSH Web,打开会话并启用 Guard:
|
|
34
34
|
|
|
@@ -49,21 +49,32 @@ Windows 请通过 profile 的 `node_modules\.bin\dsh-completion-guard-host-lock.
|
|
|
49
49
|
|
|
50
50
|
## 状态与兼容性
|
|
51
51
|
|
|
52
|
-
0.4.0
|
|
52
|
+
仓库记录的 0.4.0 发布基线可从 [npm](https://www.npmjs.com/package/dsh-completion-guard) 安装。[GitHub Release](https://github.com/GreenLv/dsh-completion-guard/releases/tag/v0.4.0) 附有精确的包校验和,以及 macOS、Windows 原生验收记录。它面向 DSH `0.1.2-alpha.3`、dshmarket `1.39.0` 和 Cordis `4.0.2`。
|
|
53
|
+
|
|
54
|
+
源码当前目标是 **0.4.2(未发布)**,新增有界 checkpoint 查询和用户确认后的要求重绑定。上方安装命令仍指向已记录的发布版本,不包含这些候选变更。验收绑定每一份冻结包,早期候选的结果不能覆盖后续文档或包变更。详见[更新记录](CHANGELOG.zh-CN.md)和[验收范围](docs/LOCAL_ACCEPTANCE.md)。
|
|
55
|
+
|
|
56
|
+
版本 `0.4.1-rc.1` 是已发布到 `next` 通道、面向 DSH `0.1.2-rc.1` 与 dshmarket `1.41.0` 的预发布版本。其宿主队列已在原生 macOS/posix 上审计,并核对过原生 Windows rc.1 运行时的宿主图谱;宿主图谱审计不能替代同一冻结包的跨平台 exact-artifact acceptance。详见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md)。
|
|
53
57
|
|
|
54
58
|
0.3.2 继续支持已经检查过的 DSH `0.1.1-rc.2` 和 `0.1.2-alpha.2` 环境。不要混用不同环境的包;只有当前包集合完整匹配 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md) 中的一套记录时,Guard 才会启用。
|
|
55
59
|
|
|
56
|
-
0.4.0 的兼容基线继续冻结在这套 alpha.3 环境。alpha.4 及此后的 alpha
|
|
60
|
+
0.4.0 的兼容基线继续冻结在这套 alpha.3 环境。alpha.4 及此后的 alpha 版本已跳过。RC 适配已随 DSH `0.1.2-rc.1` 恢复,由 `0.4.1-rc.1` 预发布版支持,并保留在 0.4.2 候选中。上游版本进度见 [DeepSeek Harness 标签页](https://github.com/deepseek-ai/deepseek-harness/tags)。
|
|
57
61
|
|
|
58
62
|
发布包只从干净提交生成一次;同一份包在 macOS 和 Windows 上完成 Web、Headless 原生检查后才会发布。CI、原生生命周期、包发布和公开读回是四类独立证据,详见 [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md)。
|
|
59
63
|
|
|
60
|
-
不建议使用 0.3.0。它的包通过了原生检查,但 npm 没有记录所需的源码提交,因此不能原地修复,也没有 GitHub Release
|
|
64
|
+
不建议使用 0.3.0。它的包通过了原生检查,但 npm 没有记录所需的源码提交,因此不能原地修复,也没有 GitHub Release。旧版已检查 DSH 环境可使用 0.3.2;其他环境请按兼容性指南选择对应版本。
|
|
61
65
|
|
|
62
66
|
> 本项目于 2026-08-29 由 `dsh-context-guard` 更名为 `dsh-completion-guard`,因为另一个无关插件已经使用旧名称。内部 bundle id 仍为 `context-guard`,旧 npm 包会引导用户使用本包。支持的 DSH 环境见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md);需要 Node.js `>=22` 和 pnpm `>=11`。
|
|
63
67
|
|
|
64
68
|
## 启用模式
|
|
65
69
|
|
|
66
|
-
|
|
70
|
+
Context Guard 有两种启用模式:
|
|
71
|
+
|
|
72
|
+
- `opt-in`(默认):打开会话时不会自动保护。你需要在这个会话中执行 `/context-guard on` 才会启用;执行 `/context-guard off` 可以再次关闭。开关只影响当前会话。
|
|
73
|
+
- `always`:DSH 会话会自动启用保护。如果你在某个会话中执行 `/context-guard off`,只会关闭这个会话;其他会话会自动开启保护。
|
|
74
|
+
|
|
75
|
+
启用模式只控制 Guard 是否保护会话,不是 DSH 的会话模式(例如会话开始时所选的标准模式、极简模式)。选择 `always` 后,Guard 会在每个 DSH 会话开始前自动加载。DSH 当前不支持在会话开始后切换会话模式,因此受这样保护的会话会一直使用它开始时的 DSH 会话模式。`/context-guard on` 和 `/context-guard off` 只负责开启或关闭 Guard 保护,不会改变 DSH 会话模式。
|
|
76
|
+
|
|
77
|
+
如果希望 DSH 会话自动启用保护,请在当前 DSH 启动方式使用的 `cordis.patch.yml` 中增加:
|
|
67
78
|
|
|
68
79
|
```yaml
|
|
69
80
|
- id: context-guard
|
|
@@ -72,7 +83,22 @@ Windows 请通过 profile 的 `node_modules\.bin\dsh-completion-guard-host-lock.
|
|
|
72
83
|
activation: always
|
|
73
84
|
```
|
|
74
85
|
|
|
75
|
-
|
|
86
|
+
DSH 有两种运行方式:**Web** 是在浏览器的网页界面里使用 DSH;**Headless** 是不打开网页界面,通常从终端或自动化任务运行 DSH。两种方式使用不同的配置文件。你用哪一种就修改哪一个;两种都用时需要分别修改:
|
|
87
|
+
|
|
88
|
+
| 系统 | 你怎么使用 DSH | 默认路径 |
|
|
89
|
+
| --- | --- | --- |
|
|
90
|
+
| macOS / Linux | Web | `$HOME/.dsh/profiles/web/cordis.patch.yml` |
|
|
91
|
+
| macOS / Linux | Headless | `$HOME/.dsh/profiles/headless/cordis.patch.yml` |
|
|
92
|
+
| Windows | Web | `%USERPROFILE%\.dsh\profiles\web\cordis.patch.yml` |
|
|
93
|
+
| Windows | Headless | `%USERPROFILE%\.dsh\profiles\headless\cordis.patch.yml` |
|
|
94
|
+
|
|
95
|
+
如果你设置过自定义 `DSH_HOME`,请用该目录替换路径开头的 `$HOME/.dsh` 或 `%USERPROFILE%\.dsh`。
|
|
96
|
+
|
|
97
|
+
不想手动改文件,也可以把下面这段话直接发给 DSH:
|
|
98
|
+
|
|
99
|
+
> 请把 `dsh-completion-guard` 设为 `always` 模式。根据我当前使用 DSH 的方式(网页界面或无网页界面),自动找到对应的 `cordis.patch.yml`,先备份该文件,只把 `id: context-guard` 这一项的 `activation` 设为 `always`,不要修改其他配置,也不要替我重启 DSH。完成后告诉我文件的绝对路径,并显示准确的修改内容。
|
|
100
|
+
|
|
101
|
+
修改完成后,重启 DSH。
|
|
76
102
|
|
|
77
103
|
## 如何检查完成状态
|
|
78
104
|
|
|
@@ -80,6 +106,14 @@ Windows 请通过 profile 的 `node_modules\.bin\dsh-completion-guard-host-lock.
|
|
|
80
106
|
|
|
81
107
|
只读证据收集与修改包、文件、服务或 Git 状态的操作使用不同工具。查询成功不会自动产生变更权限。精确命令限制和平台证据见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md)。
|
|
82
108
|
|
|
109
|
+
### 要求一直未完成时(0.4.2 候选)
|
|
110
|
+
|
|
111
|
+
“更新插件并检查 GUI”可能包含 Guard 尚不能认证的部分。checkpoint 会逐项说明原因和下一步。`generic_run_non_certifiable` 表示普通命令成功不能关闭该项,反复换绑定或再跑一条命令也无效。
|
|
112
|
+
|
|
113
|
+
用 `context_guard_rebind` 提出完整的原文拆分方案。动作或对象不明确时,先请根用户给出包含原条款的明确澄清要求,再在提案中引用新要求的 ID。工具会返回提案 ID 和原项/替代项对照;只有用户精确回复 `确认重绑定 <proposal ID>` 才会应用。引用文字、工具输出和模型自称确认都无效。未支持的部分继续保留 pending;按结构化边界安全结束也不表示全部完成。
|
|
114
|
+
|
|
115
|
+
用 `bindings: []` 调用 `context_guard_checkpoint` 可查询诊断。默认最多展示八个当前要求/限制和十条证据,插件 JSON 不超过 12 KiB。`pagination` 给出总数及各列表独立的 `next_cursor`,首页不代表完整合同。`item_ids`、`evidence_ids` 可按 ID 查询;`evidence_scope: "history"` 可查看完整证据历史,其中不可引用项会明确标记。翻页时保持查询条件不变,合同或证据快照变化后需重新查询。超长行提供 `detail_id`,用 `detail_offset` 取分片;后续分片需把首次返回的 `snapshot` 作为 `detail_snapshot` 传回。分页只改变展示,不会减少认证时检查的要求。
|
|
116
|
+
|
|
83
117
|
## 边界
|
|
84
118
|
|
|
85
119
|
Context Guard 负责完成认证;Goal、Todo、Compaction、continuation、权限和工具执行仍由 DSH 管理。它不是安全沙箱、语义证明系统、token pruning 工具,也不替代这些 DSH 能力。
|
|
@@ -90,7 +124,9 @@ Context Guard 负责完成认证;Goal、Todo、Compaction、continuation、权
|
|
|
90
124
|
|
|
91
125
|
本项目最初从 [`GreenLv/codex-context-guard`](https://github.com/GreenLv/codex-context-guard) v0.8.8 移植确定性行为。这个版本只是历史起点,不代表当前兼容程度。
|
|
92
126
|
|
|
93
|
-
|
|
127
|
+
0.4.0 明确对齐了 Codex Context Guard 0.10.0 的共享证据规则:证据必须对应仍未完成的工作,并证明用户实际要求的操作、目标和结果。这只是有边界的行为对齐,不表示两个产品拥有相同功能。
|
|
128
|
+
|
|
129
|
+
Codex Context Guard 0.11.0 在此后发布。DSH 0.4.0 已经能按自己的宿主机制核对精确变更目标、等待状态和引用文字,但还没有完整同步 0.11.0 的一次性授权票据、工作单元、需求替代归因和事故 benchmark。通俗对照表与注明日期的差异台账见 [`docs/SEMANTIC_COMPATIBILITY.md`](docs/SEMANTIC_COMPATIBILITY.md)。
|
|
94
130
|
|
|
95
131
|
两个项目服务于不同运行时:
|
|
96
132
|
|
|
@@ -103,7 +139,11 @@ Context Guard 负责完成认证;Goal、Todo、Compaction、continuation、权
|
|
|
103
139
|
|
|
104
140
|
|
|
105
141
|
|
|
106
|
-
累计图分别显示更名前后的 npm 包下载总量,标记 2026-08-29 的更名,并仅在项目增长曲线中合并两者。npm 下载量统计的是 registry
|
|
142
|
+
累计图分别显示更名前后的 npm 包下载总量,标记 2026-08-29 的更名,并仅在项目增长曲线中合并两者。npm 下载量统计的是 registry 请求,不等于独立用户数或已确认的真实安装人数。
|
|
143
|
+
|
|
144
|
+
历史从首次公开发布 npm 的 2026-08-26 开始,保留首日真实下载数,不强行归零;纵轴从零起算。日期标签统一居中,按固定天数间隔显示,图注始终保留精确截止日。
|
|
145
|
+
|
|
146
|
+
每日工作流仅发布至少相隔 12 小时复查一致、且距离当日已有两个 UTC 日历日的数据,另行标明 API 数据可用日期。这是项目的观测规则,不代表 npm 保证数值永不修订。详见[源数据](https://raw.githubusercontent.com/GreenLv/dsh-completion-guard/stats/npm-downloads.json)。
|
|
107
147
|
|
|
108
148
|
## 文档
|
|
109
149
|
|
|
@@ -129,4 +169,4 @@ pnpm run build
|
|
|
129
169
|
pnpm run pack:check
|
|
130
170
|
```
|
|
131
171
|
|
|
132
|
-
这些命令验证本地源码树与包。CI、原生平台验收、npm 发布、GitHub Release 身份和真实
|
|
172
|
+
这些命令验证本地源码树与包。CI、原生平台验收、npm 发布、GitHub Release 身份和真实 DSH 环境安装仍是相互独立的证据范围。
|
package/dist/domain/index.d.ts
CHANGED
|
@@ -1,2 +1,2 @@
|
|
|
1
|
-
import { $ as
|
|
2
|
-
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ALPHA2_DSHMARKET_139_HOST_PACKAGES, ALPHA2_HOST_PACKAGES, ALPHA3_HOST_PACKAGES, ActionManifest, ActionSpec, ActiveProfileHostLock, AssistantOutcomeObservation, AuditedExecutable, AuthorityBlock, AuthorityBlockKind, AuthorityKind, BASE_HOST_PACKAGES, BoundaryDisposition, BoundaryEffectuation, BoundaryQualification, BoundaryQualificationKind, BoundaryRequest, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, CanonicalArgv, CanonicalCommandSurface, CaptureScope, CheckpointResult, ClassifiedClause, ClauseSegment, CommandSurfaceManifest, CompletionDisposition, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, DeferAuthorization, DeriveConfig, DeriveResult, DeriveScope, DerivedEnvelope, EXPECTED_HOST_PACKAGES, EvidenceBinding, EvidenceFacetCoverage, EvidenceOutcome, EvidenceParseStatus, EvidenceRole, ExecutableIdentity, ExecutableIdentityBinding, ExpectedTransition, ExternalOperation, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, GitAdapterAction, GitCommandAccepted, GitCommandManifest, GitCommandParseResult, GitCommandRejected, GitEffectExecution, GitEffectRunner, GitPrestateCheck, GitPrestateEnvelope, GitTargetIdentity, GoalActivationState, GoalBoundaryAccess, GoalRef, GuardBoundary, GuardCheckpoint, GuardEvidence, GuardIntegrity, GuardItem, GuardItemKind, GuardItemStatus, GuardOperation, GuardProjection, HOST_CAPABILITY_PACKAGE_GROUPS, HOST_COHORTS, HostCapabilityEvaluation, HostCapabilityId, HostCapabilityRequest, HostCohort, HostCohortSelection, HostCohortSelectionReason, HostLockContext, HostLockEvaluation, HostLockStatus, HostPlatform, HostProfileError, HostProfileKind, HostStatus, HostToolSurface, LinearCommitReadback, ManifestIssue, OperationVerbEntry, PROOF_KINDS, PROOF_PROTOCOL_VERSION, PROTOCOL_V3_NOTICE, ParsedShell, PersistenceAuthorization, ProofKind, ProofManifest, ProofObligation, ProofSurface, RecoveryOptions, RejectedBinding, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, SemanticAction, SessionQuery, ShellParseStatus, StatefulAction, TargetCaptureReasonCode, TargetCaptureStatus, TargetTuple, TargetValue, ToolCallInput, ToolResultInput, ToolSubject, TurnStoppingDecision, UserInteractionKind, VerificationContract, WaitAuthorization, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindProofToProjection, bindingSatisfies, canonicalArgvFromCommand, canonicalProjection, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, createProofManifest, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, proofDigest, proofEvidenceConstraints, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, selectHostCohort, semanticActionFromCommand, semanticActionFromText, sessionQuery, sha256, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, validateProofManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|
|
1
|
+
import { $ as resolveInstalledHostLock, $n as DeriveResult, $t as HostCapabilityEvaluation, A as createProofManifest, An as ClassifiedClause, Ar as ActionManifest, At as hasCurrentCertificate, B as COMMAND_SURFACE_MANIFEST, Bn as BoundaryEffectuation, Br as isStatefulAction, Bt as PROTOCOL_V3_NOTICE, C as ProofKind, Cn as segmentAuthorityBlocks, Cr as TargetValue, Ct as ParsedShell, D as SessionQuery, Dn as RejectedBinding, Dt as parsePwshCommand, E as ProofSurface, En as CheckpointResult, Er as createProjection, Et as isRunExecutable, F as EvidenceFacetCoverage, Fn as extractArtifactPaths, Fr as STOP_PROTOCOL_VERSION, Ft as extractTextContent, G as ActiveProfileHostLock, Gn as availableBoundaryQualifications, Gr as validateActionManifest, Gt as BASE_HOST_PACKAGES, H as ManifestIssue, Hn as BoundaryRequest, Hr as requestedTargetMatchesResolved, Ht as ALPHA2_DSHMARKET_139_HOST_PACKAGES, I as bindingSatisfies, In as extractMethod, Ir as SUPPORTED_EVIDENCE_ADAPTERS, It as extractToolSubject, J as hostLockRowsFromComposedDump, Jn as qualifyBoundary, Jr as digestStrings, Jt as ExecutableIdentity, K as HostProfileError, Kn as effectuateBoundary, Kr as validateActionTarget, Kt as DEFAULT_HOST_LOCK, L as evidenceCoverage, Ln as extractOperation, Lr as SemanticAction, Lt as isDeterministicCheck, M as proofEvidenceConstraints, Mn as captureClause, Mr as CERTIFICATE_VERSION, Mt as ToolResultInput, N as sessionQuery, Nn as captureItem, Nr as SEMANTIC_ACTIONS, Nt as ToolSubject, O as bindProofToProjection, On as certifyCheckpoint, Or as ACTION_MANIFEST, Ot as parseShellCommand, P as validateProofManifest, Pn as classifyClause, Pr as STATEFUL_ACTIONS, Pt as evidenceFromPersistedToolResult, Q as resolveActiveProfileHostLock, Qn as DeriveConfig, Qr as sha256, Qt as HOST_COHORTS, R as evidenceMatchesItem, Rn as isInformationalMessage, Rr as StatefulAction, Rt as withDurability, S as PROOF_PROTOCOL_VERSION, Sn as authorityCaptureCounts, Sr as TargetTuple, St as CanonicalCommandSurface, T as ProofObligation, Tn as classifyUserInteraction, Tr as WaitAuthorization, Tt as canonicalArgvFromCommand, U as OperationVerbEntry, Un as GoalActivationState, Ur as semanticActionFromCommand, Ut as ALPHA2_HOST_PACKAGES, V as CommandSurfaceManifest, Vn as BoundaryQualification, Vr as requestedTargetAuthorizesMutation, Vt as deriveProjection, W as validateManifest, Wn as GoalBoundaryAccess, Wr as semanticActionFromText, Wt as AuditedExecutable, X as packageRowsFromActiveGraph, Xn as BoundaryQualificationKind, Xr as sanitizeClauseText, Xt as GOAL_HOST_PACKAGES, Y as injectActiveProfileHostLock, Yn as BoundaryDisposition, Yr as normalizeClause, Yt as ExecutableIdentityBinding, Z as packageRowsFromPnpmLock, Zn as DeferAuthorization, Zr as sanitizeUrl, Zt as HOST_CAPABILITY_PACKAGE_GROUPS, _ as openItems, _n as selectHostCohort, _r as GuardProjection, _t as gitCommandMatchesTarget, a as classifyCompletionClaim, an as HostLockContext, ar as EvidenceRole, at as GitCommandParseResult, b as ALPHA3_HOST_PACKAGES, bn as AuthorityBlockKind, br as TargetCaptureReasonCode, bt as verifiedLinearCommitReadback, c as isWholeTaskCompletionClaim, cn as HostPlatform, cr as GoalRef, ct as GitEffectRunner, d as snapshotSessionEvents, dn as bindExecutableIdentity, dr as GuardEvidence, dt as GitTargetIdentity, en as HostCapabilityId, er as DeriveScope, et as verifyComposedHostLockDump, f as RC1_HOST_PACKAGES, fn as bindLiveGoalCapability, fr as GuardIntegrity, ft as LinearCommitReadback, g as closingHint, gn as evaluateToolSurfaceCapability, gr as GuardOperation, gt as executeRevalidatedGitEffect, h as RecoveryOptions, hn as evaluateHostLock, hr as GuardItemStatus, ht as createGitPrestateEnvelope, i as TurnStoppingDecision, in as HostCohortSelectionReason, ir as EvidenceParseStatus, it as GitCommandManifest, j as proofDigest, jn as ClauseSegment, jr as ActionSpec, jt as ToolCallInput, k as canonicalProjection, kn as CaptureScope, kr as ACTION_MANIFEST_VERSION, kt as goalCompletionDenial, l as latestAssistantText, ln as HostProfileKind, lr as GuardBoundary, lt as GitPrestateCheck, m as MIN_RECOVERY_CHAR_BUDGET, mn as evaluateHostCapability, mr as GuardItemKind, mt as commitTreeSnapshotDigest, n as AssistantOutcomeObservation, nn as HostCohort, nr as EvidenceBinding, nt as GitAdapterAction, o as decideTurnBoundary, on as HostLockEvaluation, or as ExpectedTransition, ot as GitCommandRejected, p as DEFAULT_RECOVERY_CHAR_BUDGET, pn as evaluateExternalWaitCapability, pr as GuardItem, pt as commitIndexSnapshotDigest, q as hostLockContextFromComposedDump, qn as isCurrentAcceptedBoundary, qr as canonicalizePath, qt as EXPECTED_HOST_PACKAGES, r as CompletionDisposition, rn as HostCohortSelection, rr as EvidenceOutcome, rt as GitCommandAccepted, s as decideTurnStopping, sn as HostLockStatus, sr as ExternalOperation, st as GitEffectExecution, t as supersedeItem, tn as HostCapabilityRequest, tr as DerivedEnvelope, tt as GIT_COMMAND_MANIFEST_IDS, u as observeAssistantOutcome, un as HostToolSurface, ur as GuardCheckpoint, ut as GitPrestateEnvelope, v as recoveryDigest, vn as currentContractDigest, vr as HostStatus, vt as parseGitCommandManifest, w as ProofManifest, wn as UserInteractionKind, wr as VerificationContract, wt as ShellParseStatus, x as PROOF_KINDS, xn as AuthorityKind, xr as TargetCaptureStatus, xt as CanonicalArgv, y as renderRecoveryPacket, yn as AuthorityBlock, yr as PersistenceAuthorization, yt as revalidateGitPrestate, z as isVerifyingCapability, zn as segmentClauses, zr as actionCompatible, zt as CAPTURE_V042_NOTICE } from "../index-DNF0OTi-.js";
|
|
2
|
+
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ALPHA2_DSHMARKET_139_HOST_PACKAGES, ALPHA2_HOST_PACKAGES, ALPHA3_HOST_PACKAGES, ActionManifest, ActionSpec, ActiveProfileHostLock, AssistantOutcomeObservation, AuditedExecutable, AuthorityBlock, AuthorityBlockKind, AuthorityKind, BASE_HOST_PACKAGES, BoundaryDisposition, BoundaryEffectuation, BoundaryQualification, BoundaryQualificationKind, BoundaryRequest, CAPTURE_V042_NOTICE, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, CanonicalArgv, CanonicalCommandSurface, CaptureScope, CheckpointResult, ClassifiedClause, ClauseSegment, CommandSurfaceManifest, CompletionDisposition, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, DeferAuthorization, DeriveConfig, DeriveResult, DeriveScope, DerivedEnvelope, EXPECTED_HOST_PACKAGES, EvidenceBinding, EvidenceFacetCoverage, EvidenceOutcome, EvidenceParseStatus, EvidenceRole, ExecutableIdentity, ExecutableIdentityBinding, ExpectedTransition, ExternalOperation, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, GitAdapterAction, GitCommandAccepted, GitCommandManifest, GitCommandParseResult, GitCommandRejected, GitEffectExecution, GitEffectRunner, GitPrestateCheck, GitPrestateEnvelope, GitTargetIdentity, GoalActivationState, GoalBoundaryAccess, GoalRef, GuardBoundary, GuardCheckpoint, GuardEvidence, GuardIntegrity, GuardItem, GuardItemKind, GuardItemStatus, GuardOperation, GuardProjection, HOST_CAPABILITY_PACKAGE_GROUPS, HOST_COHORTS, HostCapabilityEvaluation, HostCapabilityId, HostCapabilityRequest, HostCohort, HostCohortSelection, HostCohortSelectionReason, HostLockContext, HostLockEvaluation, HostLockStatus, HostPlatform, HostProfileError, HostProfileKind, HostStatus, HostToolSurface, LinearCommitReadback, MIN_RECOVERY_CHAR_BUDGET, ManifestIssue, OperationVerbEntry, PROOF_KINDS, PROOF_PROTOCOL_VERSION, PROTOCOL_V3_NOTICE, ParsedShell, PersistenceAuthorization, ProofKind, ProofManifest, ProofObligation, ProofSurface, RC1_HOST_PACKAGES, RecoveryOptions, RejectedBinding, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, SemanticAction, SessionQuery, ShellParseStatus, StatefulAction, TargetCaptureReasonCode, TargetCaptureStatus, TargetTuple, TargetValue, ToolCallInput, ToolResultInput, ToolSubject, TurnStoppingDecision, UserInteractionKind, VerificationContract, WaitAuthorization, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindProofToProjection, bindingSatisfies, canonicalArgvFromCommand, canonicalProjection, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, createProofManifest, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, proofDigest, proofEvidenceConstraints, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, selectHostCohort, semanticActionFromCommand, semanticActionFromText, sessionQuery, sha256, snapshotSessionEvents, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, validateProofManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|
package/dist/domain/index.js
CHANGED
|
@@ -1,3 +1,3 @@
|
|
|
1
|
-
import { $ as
|
|
1
|
+
import { $ as DEFAULT_HOST_LOCK, $t as SUPPORTED_EVIDENCE_ADAPTERS, A as decideTurnBoundary, At as bindingSatisfies, B as extractTextContent, Bt as extractArtifactPaths, C as createGitPrestateEnvelope, Ct as closingHint, D as revalidateGitPrestate, E as parseGitCommandManifest, Et as renderRecoveryPacket, F as CAPTURE_V042_NOTICE, Ft as createProjection, G as isRunExecutable, H as isDeterministicCheck, Ht as extractOperation, I as PROTOCOL_V3_NOTICE, J as goalCompletionDenial, Jt as ACTION_MANIFEST_VERSION, K as parsePwshCommand, L as deriveProjection, Lt as captureClause, M as isWholeTaskCompletionClaim, Mt as evidenceMatchesItem, N as latestAssistantText, Nt as isVerifyingCapability, O as verifiedLinearCommitReadback, P as observeAssistantOutcome, Pt as currentContractDigest, Q as BASE_HOST_PACKAGES, Qt as STOP_PROTOCOL_VERSION, R as supersedeItem, Rt as captureItem, S as commitTreeSnapshotDigest, St as MIN_RECOVERY_CHAR_BUDGET, T as gitCommandMatchesTarget, Tt as recoveryDigest, U as withDurability, Ut as isInformationalMessage, V as extractToolSubject, Vt as extractMethod, W as canonicalArgvFromCommand, Wt as segmentClauses, X as ALPHA2_DSHMARKET_139_HOST_PACKAGES, Xt as SEMANTIC_ACTIONS, Y as hasCurrentCertificate, Yt as CERTIFICATE_VERSION, Z as ALPHA2_HOST_PACKAGES, Zt as STATEFUL_ACTIONS, _ as resolveInstalledHostLock, _t as effectuateBoundary, a as createProofManifest, an as semanticActionFromText, at as bindLiveGoalCapability, b as GIT_COMMAND_MANIFEST_IDS, bt as certifyCheckpoint, c as sessionQuery, cn as COMMAND_SURFACE_MANIFEST, ct as evaluateHostLock, d as hostLockContextFromComposedDump, dn as digestStrings, dt as RC1_HOST_PACKAGES, en as actionCompatible, et as EXPECTED_HOST_PACKAGES, f as hostLockRowsFromComposedDump, fn as normalizeClause, ft as ALPHA3_HOST_PACKAGES, g as resolveActiveProfileHostLock, gt as availableBoundaryQualifications, h as packageRowsFromPnpmLock, hn as sha256, ht as classifyUserInteraction, i as canonicalProjection, in as semanticActionFromCommand, it as bindExecutableIdentity, j as decideTurnStopping, jt as evidenceCoverage, k as classifyCompletionClaim, l as validateProofManifest, ln as validateManifest, lt as evaluateToolSurfaceCapability, m as packageRowsFromActiveGraph, mn as sanitizeUrl, mt as segmentAuthorityBlocks, n as PROOF_PROTOCOL_VERSION, nn as requestedTargetAuthorizesMutation, nt as HOST_CAPABILITY_PACKAGE_GROUPS, o as proofDigest, on as validateActionManifest, ot as evaluateExternalWaitCapability, p as injectActiveProfileHostLock, pn as sanitizeClauseText, pt as authorityCaptureCounts, q as parseShellCommand, qt as ACTION_MANIFEST, r as bindProofToProjection, rn as requestedTargetMatchesResolved, rt as HOST_COHORTS, s as proofEvidenceConstraints, sn as validateActionTarget, st as evaluateHostCapability, t as PROOF_KINDS, tn as isStatefulAction, tt as GOAL_HOST_PACKAGES, u as HostProfileError, un as canonicalizePath, ut as selectHostCohort, v as verifyComposedHostLockDump, vt as isCurrentAcceptedBoundary, w as executeRevalidatedGitEffect, wt as openItems, x as commitIndexSnapshotDigest, xt as DEFAULT_RECOVERY_CHAR_BUDGET, y as snapshotSessionEvents, yt as qualifyBoundary, z as evidenceFromPersistedToolResult, zt as classifyClause } from "../domain-BXB_BPQg.js";
|
|
2
2
|
|
|
3
|
-
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ALPHA2_DSHMARKET_139_HOST_PACKAGES, ALPHA2_HOST_PACKAGES, ALPHA3_HOST_PACKAGES, BASE_HOST_PACKAGES, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, EXPECTED_HOST_PACKAGES, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, HOST_CAPABILITY_PACKAGE_GROUPS, HOST_COHORTS, HostProfileError, PROOF_KINDS, PROOF_PROTOCOL_VERSION, PROTOCOL_V3_NOTICE, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindProofToProjection, bindingSatisfies, canonicalArgvFromCommand, canonicalProjection, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, createProofManifest, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, proofDigest, proofEvidenceConstraints, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, selectHostCohort, semanticActionFromCommand, semanticActionFromText, sessionQuery, sha256, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, validateProofManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|
|
3
|
+
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ALPHA2_DSHMARKET_139_HOST_PACKAGES, ALPHA2_HOST_PACKAGES, ALPHA3_HOST_PACKAGES, BASE_HOST_PACKAGES, CAPTURE_V042_NOTICE, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, EXPECTED_HOST_PACKAGES, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, HOST_CAPABILITY_PACKAGE_GROUPS, HOST_COHORTS, HostProfileError, MIN_RECOVERY_CHAR_BUDGET, PROOF_KINDS, PROOF_PROTOCOL_VERSION, PROTOCOL_V3_NOTICE, RC1_HOST_PACKAGES, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindProofToProjection, bindingSatisfies, canonicalArgvFromCommand, canonicalProjection, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, createProofManifest, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, proofDigest, proofEvidenceConstraints, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, selectHostCohort, semanticActionFromCommand, semanticActionFromText, sessionQuery, sha256, snapshotSessionEvents, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, validateProofManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|