dsh-completion-guard 0.3.0 → 0.3.2
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/CHANGELOG.md +40 -9
- package/CHANGELOG.zh-CN.md +40 -9
- package/README.md +39 -62
- package/README.zh-CN.md +39 -62
- package/dist/domain/index.d.ts +2 -2
- package/dist/domain/index.js +2 -2
- package/dist/{domain-CBvBQHTL.js → domain-DPPFAcbF.js} +394 -87
- package/dist/{index-GvKLkTqV.d.ts → index-CTFLYvNL.d.ts} +62 -12
- package/dist/index.d.ts +2 -2
- package/dist/index.js +2 -2
- package/docs/ARCHITECTURE.md +1 -1
- package/docs/COMPATIBILITY.md +5 -5
- package/docs/LOCAL_ACCEPTANCE.md +122 -10
- package/docs/distribution.md +33 -14
- package/docs/upstream-deltas.json +1 -1
- package/manifests/supported-host.v1.json +485 -59
- package/package.json +20 -18
package/CHANGELOG.md
CHANGED
|
@@ -2,27 +2,58 @@
|
|
|
2
2
|
|
|
3
3
|
All notable changes to this project are documented here. The project is pre-1.0; release versions track the plugin lifecycle, not stabilised API promises.
|
|
4
4
|
|
|
5
|
+
## 0.3.2 - Unreleased (source candidate)
|
|
6
|
+
|
|
7
|
+
### Added
|
|
8
|
+
|
|
9
|
+
- **Two exact DSH setups are recognized.** The `0.1.1-rc.2` + dshmarket `1.36.0` and `0.1.2-alpha.2` + dshmarket `1.38.1` package sets are both checked on macOS and Windows.
|
|
10
|
+
- **The whole package set must match.** Every required package must appear once with the expected version and integrity. Missing, mixed, duplicate, unidentified, or unknown packages make the entire host unavailable instead of leaving part of the Guard enabled. Status now lists missing packages, and switching setups invalidates earlier completion certificates.
|
|
11
|
+
|
|
12
|
+
### Changed
|
|
13
|
+
|
|
14
|
+
- Peer dependencies accept only the two checked version sets (`0.1.1-rc.2 || 0.1.2-alpha.2`, Cordis `4.0.1 || 4.0.2`). A source comparison found no change in the DSH events, Goal calls, tool definitions, or terminal results that the Guard uses.
|
|
15
|
+
|
|
16
|
+
### Fixed
|
|
17
|
+
|
|
18
|
+
- **Release packaging now works with Windows tar.** Archive extraction uses paths relative to the temporary working directory instead of passing absolute archive paths, without changing the files placed in the package.
|
|
19
|
+
|
|
20
|
+
### Validation
|
|
21
|
+
|
|
22
|
+
- The complete 20-file suite passes 359 tests with one Windows-only skip on macOS. Native Windows matched all 34 alpha.2 package rows with no missing, extra, or duplicate entries. The packaging portability fix at `a3e77de` passed the six-job Ubuntu, macOS, and Windows CI matrix on Node.js 22 and 24.
|
|
23
|
+
- Still pending: a clean committed candidate containing the Windows registration and final documentation, isolated Web and Headless installation, native macOS and Windows checks of those exact package bytes, final candidate CI, tag, npm publication, GitHub Release, and public readback.
|
|
24
|
+
|
|
25
|
+
## 0.3.1 - 2026-08-31
|
|
26
|
+
|
|
27
|
+
### Fixed
|
|
28
|
+
|
|
29
|
+
- **Frozen npm artifacts now carry their exact source commit.** The release packer stages the npm file set, injects the full 40-character Git HEAD into the staged package manifest, packs twice, and fails unless both tgz files are byte-identical. It also emits a SHA-256 checksum and a machine-readable artifact record before any registry mutation.
|
|
30
|
+
- **The incomplete 0.3.0 publication is not promoted as a complete release.** Its npm artifact remains installable and passed native same-byte validation, but the registry omitted `gitHead`; no GitHub Release is created for `v0.3.0`. Version 0.3.1 supersedes that consumed version without moving its tag or attempting to reuse its npm identity.
|
|
31
|
+
|
|
32
|
+
### Validation
|
|
33
|
+
|
|
34
|
+
- The frozen 0.3.1 package passed native macOS and Windows lifecycle checks, was published to npm, and has a matching GitHub Release. Exact artifact and public readback evidence is recorded in [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md).
|
|
35
|
+
|
|
5
36
|
## 0.3.0 - 2026-08-31
|
|
6
37
|
|
|
7
38
|
### Added
|
|
8
39
|
|
|
9
|
-
- **
|
|
10
|
-
- **
|
|
11
|
-
- **
|
|
40
|
+
- **High-impact changes must match the user's exact request.** Package, file, service, and Git operations are tied to one target and an expected result. A generic successful command cannot certify a different action.
|
|
41
|
+
- **Changes require independent readback.** Install, apply, file editing, restart, Git, and publish operations must show both the intended effect and the resulting saved state before they can close a requirement.
|
|
42
|
+
- **Read-only checks and mutations use separate tools.** Looking up a target never grants permission to change it. Mutations require a current, matching root-user instruction; prohibitions and acceptance checks cannot provide that authority.
|
|
12
43
|
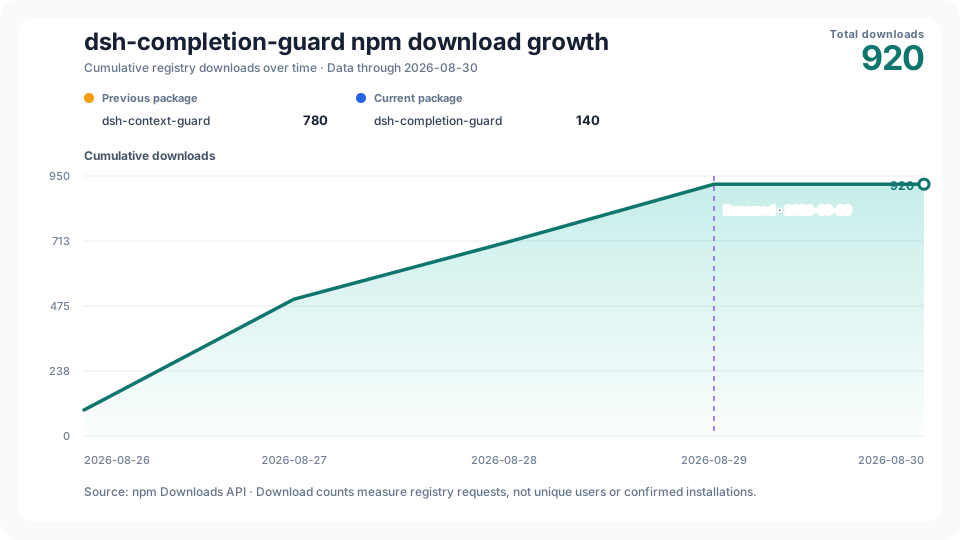
- **Bilingual npm download history.** A daily cumulative chart keeps the renamed `dsh-context-guard` and current `dsh-completion-guard` package totals separate while presenting one project-growth line. Collection reconciles npm range and point responses before publishing English and Simplified Chinese SVGs.
|
|
13
44
|
|
|
14
45
|
### Fixed
|
|
15
46
|
|
|
16
|
-
- Assistant
|
|
17
|
-
-
|
|
18
|
-
-
|
|
19
|
-
-
|
|
20
|
-
- Windows
|
|
47
|
+
- Assistant wording no longer controls whether DSH continues a task. Only a saved wait or deferral state can end the current round without claiming completion.
|
|
48
|
+
- Missing, unknown, or changed DSH package identities keep the affected Guard capabilities unavailable. Direct internal Goal or session writes are reported as integrity problems but are not claimed to be preventable.
|
|
49
|
+
- Host-lock injection is repeatable, folded YAML integrity values are read correctly, and a fresh empty profile can be updated safely.
|
|
50
|
+
- Package publishing and file edits bind the expected destination before making a change and reject changed input or different resulting bytes.
|
|
51
|
+
- Windows actions pin both the command wrapper and the system command interpreter, then reuse those checked paths instead of searching again at execution time.
|
|
21
52
|
- The npm statistics publisher now rejects non-default refs before checkout, isolates read-only collection from the write-capable publication job, does not persist credentials during collection, and pins all official Actions to immutable commits.
|
|
22
53
|
|
|
23
54
|
### Changed
|
|
24
55
|
|
|
25
|
-
- **Package renamed from `dsh-context-guard` to `dsh-completion-guard`.** An unrelated DSH plugin
|
|
56
|
+
- **Package renamed from `dsh-context-guard` to `dsh-completion-guard`.** An unrelated DSH plugin already uses the old name. The internal Cordis bundle id stays `context-guard`, so installed profiles keep their runtime identity; all published versions of the previous npm package are deprecated and point readers to the new package.
|
|
26
57
|
|
|
27
58
|
### Validation
|
|
28
59
|
|
package/CHANGELOG.zh-CN.md
CHANGED
|
@@ -2,27 +2,58 @@
|
|
|
2
2
|
|
|
3
3
|
本项目的重要变化记录在这里。项目仍处于 1.0 之前;版本号跟踪插件生命周期,不代表 API 已稳定。
|
|
4
4
|
|
|
5
|
+
## 0.3.2 - 未发布(源码候选)
|
|
6
|
+
|
|
7
|
+
### 新增
|
|
8
|
+
|
|
9
|
+
- **可识别两套精确的 DSH 环境。** `0.1.1-rc.2` + dshmarket `1.36.0` 与 `0.1.2-alpha.2` + dshmarket `1.38.1` 两套包集合均已在 macOS 和 Windows 检查。
|
|
10
|
+
- **必须完整匹配整套包。** 每个必需包都必须恰好出现一次,并具有预期版本和完整性值。缺包、混装、重复、缺少身份或未知包都会让整个宿主保持不可用,不会只启用部分 Guard。状态会列出缺少的包,切换环境也会使旧完成证书失效。
|
|
11
|
+
|
|
12
|
+
### 变更
|
|
13
|
+
|
|
14
|
+
- peer dependencies 只接受两套已检查版本(`0.1.1-rc.2 || 0.1.2-alpha.2`,Cordis `4.0.1 || 4.0.2`)。源码对比未发现 Guard 使用的 DSH 事件、Goal 调用、工具定义或终端结果发生变化。
|
|
15
|
+
|
|
16
|
+
### 修复
|
|
17
|
+
|
|
18
|
+
- **发布打包现在兼容 Windows tar。** 解包时改用相对于临时工作目录的路径,不再把归档绝对路径传给 tar;包内文件不变。
|
|
19
|
+
|
|
20
|
+
### 验证
|
|
21
|
+
|
|
22
|
+
- 20 个测试文件全量通过 359 项,macOS 跳过 1 项仅适用于 Windows 的测试。Windows 原生核对 alpha.2 的 34 行包清单全部匹配,没有缺失、额外或重复项。打包兼容性修复提交 `a3e77de` 已通过 Ubuntu、macOS、Windows 和 Node.js 22/24 的六项 CI 矩阵。
|
|
23
|
+
- 尚待完成:提交包含 Windows 注册和最终文档的干净候选、隔离 Web/Headless 安装、对该同一包的原生 macOS/Windows 验收、最终候选 CI、tag、npm 发布、GitHub Release 和公开读回。
|
|
24
|
+
|
|
25
|
+
## 0.3.1 - 2026-08-31
|
|
26
|
+
|
|
27
|
+
### 修复
|
|
28
|
+
|
|
29
|
+
- **冻结 npm 工件现在携带精确源码提交。** release packer 会先构造 npm 文件集,在 staging 包 manifest 中注入完整 40 字符 Git HEAD,再重复打包两次;只有两个 tgz 逐字节一致才通过。registry mutation 前还会生成 SHA-256 校验文件与机器可读工件记录。
|
|
30
|
+
- **不把未闭合的 0.3.0 publication 提升为完整 release。** 其 npm 工件仍可安装,并已通过原生平台同字节验收,但 registry 缺少 `gitHead`;因此不为 `v0.3.0` 创建 GitHub Release。0.3.1 在不移动旧 tag、不尝试复用旧 npm 身份的前提下取代该已消费版本。
|
|
31
|
+
|
|
32
|
+
### 验证
|
|
33
|
+
|
|
34
|
+
- 冻结的 0.3.1 包已通过 macOS 和 Windows 原生生命周期检查,并已发布到 npm 和对应 GitHub Release。精确工件与公开读回证据见 [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md)。
|
|
35
|
+
|
|
5
36
|
## 0.3.0 - 2026-08-31
|
|
6
37
|
|
|
7
38
|
### 新增
|
|
8
39
|
|
|
9
|
-
-
|
|
10
|
-
-
|
|
11
|
-
-
|
|
40
|
+
- **高影响变更必须匹配用户的精确要求。** 包、文件、服务和 Git 操作会绑定到一个目标和预期结果;普通命令成功不能替代另一个动作的完成证据。
|
|
41
|
+
- **变更后必须独立读回。** 安装、更新、文件修改、重启、Git 和发布操作需要同时证明预期动作与最终保存状态,才能关闭要求。
|
|
42
|
+
- **只读检查和实际变更使用不同工具。** 查询目标不会自动产生修改权限。变更必须对应当前根用户要求;禁止项和验收条件不能提供这份授权。
|
|
12
43
|
- **双语 npm 下载量历史。** 每日累计图分别保留更名前的 `dsh-context-guard` 与当前 `dsh-completion-guard` 包总量,同时呈现一条项目增长曲线。采集器会先核对 npm range 与 point 响应,再发布英文和简体中文 SVG。
|
|
13
44
|
|
|
14
45
|
### 修复
|
|
15
46
|
|
|
16
|
-
-
|
|
17
|
-
-
|
|
18
|
-
-
|
|
19
|
-
-
|
|
20
|
-
- Windows
|
|
47
|
+
- 助手措辞不再决定 DSH 是否继续任务。只有已保存的等待或延期状态才能结束当前轮次,同时保留未完成要求。
|
|
48
|
+
- DSH 包身份缺失、未知或发生变化时,受影响的 Guard 能力保持不可用。进程内部直接写 Goal/session 会被报告为完整性问题,但不声称一定能够阻止。
|
|
49
|
+
- 宿主身份注入可重复执行,折叠 YAML 中的完整性值可以正确读取,新建空 profile 也能安全更新。
|
|
50
|
+
- 包发布和文件修改会在操作前绑定预期目标,并拒绝已变化的输入或不同的最终字节。
|
|
51
|
+
- Windows 操作会固定命令包装器和系统命令解释器,执行时复用已检查路径,不再重新搜索。
|
|
21
52
|
- npm 统计发布器现在会在 checkout 前拒绝非默认 ref,把只读采集与具有写权限的发布 job 隔离,采集阶段不持久化凭据,并把全部官方 Action 固定到不可变提交。
|
|
22
53
|
|
|
23
54
|
### 变更
|
|
24
55
|
|
|
25
|
-
- **包名由 `dsh-context-guard` 更名为 `dsh-completion-guard`。**
|
|
56
|
+
- **包名由 `dsh-context-guard` 更名为 `dsh-completion-guard`。** 另一个无关 DSH 插件已经使用旧名称。内部 Cordis bundle id 仍为 `context-guard`,已安装 profile 的运行时身份不受影响;旧 npm 包的所有已发布版本均已标为弃用,并引导读者使用新包。
|
|
26
57
|
|
|
27
58
|
### 验证
|
|
28
59
|
|
package/README.md
CHANGED
|
@@ -2,7 +2,7 @@
|
|
|
2
2
|
|
|
3
3
|
[简体中文](README.zh-CN.md)
|
|
4
4
|
|
|
5
|
-
|
|
5
|
+
An add-on for DeepSeek Harness (DSH) that keeps a task's requirements and checks them before the task is marked complete. It restores the same checklist after a resumed session and accepts only matching saved tool results as evidence.
|
|
6
6
|
|
|
7
7
|

|
|
8
8
|
|
|
@@ -11,87 +11,70 @@ A task-contract and completion-certification plugin for DeepSeek Harness (DSH).
|
|
|
11
11
|
Install the published plugin into a DSH Web profile:
|
|
12
12
|
|
|
13
13
|
```sh
|
|
14
|
-
dsh plugin --profile web add dsh-completion-guard@0.3.
|
|
14
|
+
dsh plugin --profile web add dsh-completion-guard@0.3.1
|
|
15
15
|
```
|
|
16
16
|
|
|
17
|
-
|
|
17
|
+
Before restarting DSH, record and verify the active runtime and profile. Replace the example paths with the absolute paths on your machine:
|
|
18
18
|
|
|
19
|
-
```
|
|
20
|
-
/
|
|
21
|
-
/
|
|
22
|
-
|
|
23
|
-
|
|
24
|
-
Activation is opt-in by default. `status` reports whether the guard is enabled, the current epoch and contract revision, pending and passed item counts, the evidence count, and integrity state. `off` stops capture and gating for the session while preserving its prior history; `clear` supersedes every pending requirement/acceptance under a `CLEAR:` sentinel (prohibitions retained) so an empty-binding checkpoint can certify while the guard stays on; `diagnose` returns a bounded diagnostic view.
|
|
25
|
-
|
|
26
|
-
### Activation modes
|
|
19
|
+
```sh
|
|
20
|
+
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
21
|
+
DSH_PROFILE_ROOT=/absolute/path/to/.dsh/profiles/web
|
|
22
|
+
DSH_COMPOSED_DUMP=/tmp/dsh-web-composed.yml
|
|
23
|
+
GUARD_HOST_LOCK="$DSH_PROFILE_ROOT/node_modules/.bin/dsh-completion-guard-host-lock"
|
|
27
24
|
|
|
28
|
-
|
|
25
|
+
"$GUARD_HOST_LOCK" inspect --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
26
|
+
"$GUARD_HOST_LOCK" inject --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
27
|
+
dsh --profile web --dump-config > "$DSH_COMPOSED_DUMP"
|
|
28
|
+
"$GUARD_HOST_LOCK" verify-dump --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT" --dump-config "$DSH_COMPOSED_DUMP"
|
|
29
|
+
```
|
|
29
30
|
|
|
30
|
-
|
|
31
|
-
| --- | --- |
|
|
32
|
-
| `opt-in` | Default. A session remains unprotected until `/context-guard on` is recorded in that session. |
|
|
33
|
-
| `always` | Starts enabled before the session log is replayed. `/context-guard off` disables the guard for that session until a later `/context-guard on`. |
|
|
31
|
+
On Windows, run the same three subcommands through `dsh-completion-guard-host-lock.cmd` in the profile's `node_modules\.bin` directory and use Windows absolute paths. Repeat this check after a DSH, profile, or package upgrade. The Guard stays unavailable if the active package set is missing, mixed, duplicated, or different from a checked setup.
|
|
34
32
|
|
|
35
|
-
|
|
33
|
+
Restart DSH Web, open a session, and enable the Guard:
|
|
36
34
|
|
|
37
|
-
```
|
|
38
|
-
|
|
39
|
-
|
|
40
|
-
config:
|
|
41
|
-
activation: always
|
|
35
|
+
```text
|
|
36
|
+
/context-guard on
|
|
37
|
+
/context-guard status
|
|
42
38
|
```
|
|
43
39
|
|
|
44
|
-
|
|
45
|
-
|
|
46
|
-
Once enabled, Context Guard captures direct user requirements and acceptance criteria. Tool results become citable evidence only after DSH persists them. Before the model claims the whole task is complete, it must call the injected `context_guard_checkpoint` tool with matching evidence IDs; an incomplete or stale binding cannot certify completion.
|
|
40
|
+
Activation is opt-in by default. `status` shows whether the Guard is on and how many checks remain. `off` stops protection for the current session without deleting its history. `clear` closes the current checklist while keeping prohibitions. `diagnose` explains why a completion check passed or failed.
|
|
47
41
|
|
|
48
42
|
## What it protects
|
|
49
43
|
|
|
50
|
-
-
|
|
51
|
-
-
|
|
52
|
-
-
|
|
53
|
-
-
|
|
54
|
-
-
|
|
44
|
+
- Saves requirements, acceptance checks, prohibitions, and later corrections without overwriting history.
|
|
45
|
+
- Uses only tool calls and results that DSH has saved, and stores a redacted summary rather than full output.
|
|
46
|
+
- Accepts evidence only when the action and result match the requested command, file, or other target.
|
|
47
|
+
- Rechecks completion after a session is rebuilt or resumed, and refuses to certify damaged state.
|
|
48
|
+
- Stops the Guard-owned Goal completion path when the current checklist has not passed. DSH internals can still bypass this path, so the plugin reports those cases rather than claiming to block every possible write.
|
|
55
49
|
|
|
56
50
|
## Status and compatibility
|
|
57
51
|
|
|
58
|
-
Version 0.3.
|
|
59
|
-
|
|
60
|
-
> The project was renamed from `dsh-context-guard` to `dsh-completion-guard` on 2026-08-29 to avoid a name collision with an unrelated DSH plugin (kpl0111/dsh-context-guard, tool-result pruning). The internal Cordis bundle id stays `context-guard`, and the previous npm package `dsh-context-guard` will be deprecated in favor of this package. It targets DSH `0.1.1-rc.2`, Node.js `>=22`, and pnpm `>=11`.
|
|
61
|
-
|
|
62
|
-
### Earlier v0.2.x evidence
|
|
63
|
-
|
|
64
|
-
The 0.2.1 release suite contains 138 tests (105 domain/core). It attributes shell evidence to the session cwd when the tool omits `workdir`, supports literal `2>&1` diagnostics and read-only inspection commands, maps process verbs to run evidence, and exposes actionable hints when a checkpoint binding is rejected. 0.2.1 adds a session-layer capture filter so clarification questions, meta comments, and bare progression phrases (`继续`, `continue`) never become contract items; de-duplicates repeated recovery notifications; adds `/context-guard clear`; and documents how a goal completes when the guard is disabled or blocked. A macOS live Web run loaded the published profile package and certified a real `pnpm test` result.
|
|
65
|
-
|
|
66
|
-
The Windows TEMP readback verifies the `b75868e9e73d29f50530ddaba15cfaef82e03ece` source matrix and the exact-source tarball → isolated installation → dump-config → Web startup log and cleanup chain. HTTP 200 appeared only in the first-run stdout, was not persisted, and was not rerun during readback, so the HTTP response itself is not independently confirmed. A real model-session smoke remains not run.
|
|
52
|
+
Version 0.3.1 is the current published release. Install it from [npm](https://www.npmjs.com/package/dsh-completion-guard); its [GitHub Release](https://github.com/GreenLv/dsh-completion-guard/releases/tag/v0.3.1) and exact public checks are recorded in [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md).
|
|
67
53
|
|
|
68
|
-
|
|
54
|
+
Version 0.3.2 is an unreleased source candidate. It recognizes the exact DSH `0.1.1-rc.2` and `0.1.2-alpha.2` package sets checked on macOS and Windows. See [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md) for the package sets and [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md) for the remaining release checks.
|
|
69
55
|
|
|
70
|
-
Version 0.3.0
|
|
56
|
+
Version 0.3.0 is not recommended. Its package passed native checks, but npm did not record the required source commit, so the version cannot be repaired in place and has no GitHub Release. Use 0.3.1, which keeps the same runtime behavior and fixes that release record.
|
|
71
57
|
|
|
72
|
-
The
|
|
58
|
+
> The project was renamed from `dsh-context-guard` to `dsh-completion-guard` on 2026-08-29 because an unrelated plugin already used the old name. The internal bundle id remains `context-guard`, and the old npm package points users to this one. Supported DSH setups are listed in [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md); Node.js `>=22` and pnpm `>=11` are required.
|
|
73
59
|
|
|
74
|
-
|
|
60
|
+
## Activation modes
|
|
75
61
|
|
|
76
|
-
|
|
77
|
-
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
78
|
-
DSH_PROFILE_ROOT=/absolute/path/to/.dsh/profiles/web
|
|
79
|
-
DSH_COMPOSED_DUMP=/tmp/dsh-web-composed.yml
|
|
80
|
-
GUARD_HOST_LOCK="$DSH_PROFILE_ROOT/node_modules/.bin/dsh-completion-guard-host-lock"
|
|
62
|
+
The default `opt-in` mode protects a session only after `/context-guard on`. To enable the Guard automatically for a DSH profile, add this override to that profile's `cordis.patch.yml`:
|
|
81
63
|
|
|
82
|
-
|
|
83
|
-
|
|
84
|
-
dsh
|
|
85
|
-
|
|
64
|
+
```yaml
|
|
65
|
+
- id: context-guard
|
|
66
|
+
name: dsh-completion-guard
|
|
67
|
+
config:
|
|
68
|
+
activation: always
|
|
86
69
|
```
|
|
87
70
|
|
|
88
|
-
|
|
71
|
+
Restart the profile, then run `/context-guard status`. In `always` mode, rebuilding an existing session can also capture earlier user messages from its saved log. Keep `opt-in` if protection should start only after an explicit command.
|
|
89
72
|
|
|
90
|
-
|
|
73
|
+
## How completion is checked
|
|
91
74
|
|
|
92
|
-
|
|
75
|
+
Once enabled, the Guard saves direct user requirements and acceptance checks. A saved tool result counts only when it matches the requested command, file, or other target. Before claiming the whole task complete, the model must pass the Guard's checkpoint; missing, stale, or mismatched evidence leaves the task open.
|
|
93
76
|
|
|
94
|
-
|
|
77
|
+
Read-only evidence collection and actions that change packages, files, services, or Git state use separate tools. A successful lookup never grants permission to make a change. Exact command limits and platform evidence are documented in [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md).
|
|
95
78
|
|
|
96
79
|
## Boundaries
|
|
97
80
|
|
|
@@ -108,12 +91,6 @@ This project ports deterministic behavior from [`GreenLv/codex-context-guard`](h
|
|
|
108
91
|
|
|
109
92
|
They do not share runtime state, installers, caches, or release histories. Fixes are contributed to the repository that owns the affected runtime and are ported deliberately when the same behavior belongs in both products. See [`docs/UPSTREAM_BASE.md`](docs/UPSTREAM_BASE.md) and [`docs/PORTING_NOTES.md`](docs/PORTING_NOTES.md) for the exact reused and replaced boundaries.
|
|
110
93
|
|
|
111
|
-
## npm download history
|
|
112
|
-
|
|
113
|
-
|
|
114
|
-
|
|
115
|
-
The cumulative chart keeps the old and new npm package totals visibly separate, marks the 2026-08-29 rename, and combines them only for the project growth line. npm download counts measure registry requests; they are not counts of unique users or confirmed installations. The workflow runs daily and can also be triggered manually.
|
|
116
|
-
|
|
117
94
|
## Documentation
|
|
118
95
|
|
|
119
96
|
- [`CHANGELOG.md`](CHANGELOG.md) — versioned user-visible changes.
|
package/README.zh-CN.md
CHANGED
|
@@ -2,7 +2,7 @@
|
|
|
2
2
|
|
|
3
3
|
[English](README.md)
|
|
4
4
|
|
|
5
|
-
面向 DeepSeek Harness(DSH
|
|
5
|
+
面向 DeepSeek Harness(DSH)的任务保护插件。它保存任务要求,并在任务标记完成前逐项核对;会话恢复后仍使用同一份检查表,只有匹配的已保存工具结果才能作为证据。
|
|
6
6
|
|
|
7
7
|

|
|
8
8
|
|
|
@@ -11,87 +11,70 @@
|
|
|
11
11
|
将已发布插件安装到 DSH Web profile:
|
|
12
12
|
|
|
13
13
|
```sh
|
|
14
|
-
dsh plugin --profile web add dsh-completion-guard@0.3.
|
|
14
|
+
dsh plugin --profile web add dsh-completion-guard@0.3.1
|
|
15
15
|
```
|
|
16
16
|
|
|
17
|
-
重启 DSH
|
|
17
|
+
重启 DSH 前,先记录并验证当前 runtime 和 profile。请把示例路径替换为本机绝对路径:
|
|
18
18
|
|
|
19
|
-
```
|
|
20
|
-
/
|
|
21
|
-
/
|
|
22
|
-
|
|
23
|
-
|
|
24
|
-
默认采用 opt-in。`status` 会返回启用状态、当前 epoch 和合同修订、待完成与已通过条目数量、证据数量及完整性状态;`off` 停止本会话的捕获和门禁,但保留已有历史;`clear` 在 `CLEAR:` 哨兵下使所有待完成的 requirement/acceptance 成为 superseded(保留 prohibition),从而让空绑定 checkpoint 也能在 Guard 保持开启的情况下签发证书;`diagnose` 返回有界的诊断信息。
|
|
25
|
-
|
|
26
|
-
### 启用模式
|
|
19
|
+
```sh
|
|
20
|
+
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
21
|
+
DSH_PROFILE_ROOT=/absolute/path/to/.dsh/profiles/web
|
|
22
|
+
DSH_COMPOSED_DUMP=/tmp/dsh-web-composed.yml
|
|
23
|
+
GUARD_HOST_LOCK="$DSH_PROFILE_ROOT/node_modules/.bin/dsh-completion-guard-host-lock"
|
|
27
24
|
|
|
28
|
-
|
|
25
|
+
"$GUARD_HOST_LOCK" inspect --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
26
|
+
"$GUARD_HOST_LOCK" inject --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
27
|
+
dsh --profile web --dump-config > "$DSH_COMPOSED_DUMP"
|
|
28
|
+
"$GUARD_HOST_LOCK" verify-dump --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT" --dump-config "$DSH_COMPOSED_DUMP"
|
|
29
|
+
```
|
|
29
30
|
|
|
30
|
-
|
|
31
|
-
| --- | --- |
|
|
32
|
-
| `opt-in` | 默认值。只有本会话记录了 `/context-guard on` 后才开始保护。 |
|
|
33
|
-
| `always` | 在重放会话日志前就进入启用状态。`/context-guard off` 会关闭本会话的 Guard,直到后续再次执行 `/context-guard on`。 |
|
|
31
|
+
Windows 请通过 profile 的 `node_modules\.bin\dsh-completion-guard-host-lock.cmd` 运行相同的三个子命令,并使用 Windows 绝对路径。DSH、profile 或包升级后需要重新检查。如果当前包集合缺失、混装、重复或不属于已检查环境,Guard 会保持不可用。
|
|
34
32
|
|
|
35
|
-
|
|
33
|
+
然后重启 DSH Web,打开会话并启用 Guard:
|
|
36
34
|
|
|
37
|
-
```
|
|
38
|
-
|
|
39
|
-
|
|
40
|
-
config:
|
|
41
|
-
activation: always
|
|
35
|
+
```text
|
|
36
|
+
/context-guard on
|
|
37
|
+
/context-guard status
|
|
42
38
|
```
|
|
43
39
|
|
|
44
|
-
|
|
45
|
-
|
|
46
|
-
启用后,Context Guard 从用户直接给出的要求和验收条件建立合同。工具结果只有在 DSH 持久化后才会成为可引用证据。模型在声称整个任务完成前,必须调用注入的 `context_guard_checkpoint` 工具并绑定匹配的证据 ID;不完整、过期或对象不匹配的绑定不能签发证书。
|
|
40
|
+
默认采用 opt-in。`status` 显示 Guard 是否开启以及还有多少检查项。`off` 停止保护当前会话,但不删除历史。`clear` 关闭当前待办,同时保留禁止项。`diagnose` 说明完成检查为什么通过或失败。
|
|
47
41
|
|
|
48
42
|
## 它保护什么
|
|
49
43
|
|
|
50
|
-
-
|
|
51
|
-
-
|
|
52
|
-
-
|
|
53
|
-
-
|
|
54
|
-
-
|
|
44
|
+
- 保存需求、验收条件、禁止项和后续修正,不覆盖旧记录。
|
|
45
|
+
- 只使用 DSH 已保存的工具调用和结果,并保存脱敏摘要而不是完整输出。
|
|
46
|
+
- 只有动作和结果对应指定命令、文件或其他目标时,证据才有效。
|
|
47
|
+
- 会话重建或恢复后重新检查完成状态;记录损坏时拒绝签发证书。
|
|
48
|
+
- 当前检查表尚未通过时,阻止 Guard 自己守卫的 Goal 完成路径。DSH 内部仍可能绕过这条路径,因此插件会报告这些情况,不声称能阻止所有写入。
|
|
55
49
|
|
|
56
50
|
## 状态与兼容性
|
|
57
51
|
|
|
58
|
-
0.3.
|
|
59
|
-
|
|
60
|
-
> 本项目于 2026-08-29 由 `dsh-context-guard` 更名为 `dsh-completion-guard`,以避免与无关的 DSH 插件(kpl0111/dsh-context-guard,工具结果剪裁)撞名。内部 Cordis bundle id 保持 `context-guard` 不变;原 npm 包 `dsh-context-guard` 将被 deprecate 并指向本包。目标环境为 DSH `0.1.1-rc.2`、Node.js `>=22`、pnpm `>=11`。
|
|
61
|
-
|
|
62
|
-
### 早期 v0.2.x 证据
|
|
63
|
-
|
|
64
|
-
0.2.1 版本测试共 138 项,其中 domain/core 105 项。它会在 shell 工具未提供 `workdir` 时使用会话 cwd 归因证据,支持字面量 `2>&1` 和只读检查命令,把过程动词映射为 run 证据,并在 checkpoint 绑定被拒时提供可执行提示。0.2.1 新增会话层捕获过滤,使澄清提问、元评论和纯推进语(`继续`、`continue`)不再成为合同条目;对重复恢复通知做内容去重;新增 `/context-guard clear`;并文档化在 Guard 关闭或阻塞时 goal 如何完成。macOS 真实 Web 会话已加载公开 profile 包并认证 `pnpm test` 结果。
|
|
65
|
-
|
|
66
|
-
Windows TEMP 读回现已确认 `b75868e9e73d29f50530ddaba15cfaef82e03ece` 的源码矩阵,以及 exact-source tarball → 隔离安装 → dump-config → Web 启动日志与清理链。HTTP 200 只出现在首轮 stdout,未持久化且复核时没有重跑,因此 HTTP 响应本身不能写成“独立复核已确认”。真实模型会话 smoke 仍未运行。
|
|
52
|
+
0.3.1 是当前已发布版本,可从 [npm](https://www.npmjs.com/package/dsh-completion-guard) 安装。[GitHub Release](https://github.com/GreenLv/dsh-completion-guard/releases/tag/v0.3.1) 和精确的公开检查记录见 [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md)。
|
|
67
53
|
|
|
68
|
-
|
|
54
|
+
0.3.2 是未发布的源码候选,可识别已在 macOS 和 Windows 检查过的 DSH `0.1.1-rc.2` 与 `0.1.2-alpha.2` 精确包集合。包集合见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md),剩余发布检查见 [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md)。
|
|
69
55
|
|
|
70
|
-
|
|
56
|
+
不建议使用 0.3.0。它的包通过了原生检查,但 npm 没有记录所需的源码提交,因此不能原地修复,也没有 GitHub Release。请使用 0.3.1;运行行为不变,发布记录已修复。
|
|
71
57
|
|
|
72
|
-
|
|
58
|
+
> 本项目于 2026-08-29 由 `dsh-context-guard` 更名为 `dsh-completion-guard`,因为另一个无关插件已经使用旧名称。内部 bundle id 仍为 `context-guard`,旧 npm 包会引导用户使用本包。支持的 DSH 环境见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md);需要 Node.js `>=22` 和 pnpm `>=11`。
|
|
73
59
|
|
|
74
|
-
|
|
60
|
+
## 启用模式
|
|
75
61
|
|
|
76
|
-
|
|
77
|
-
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
78
|
-
DSH_PROFILE_ROOT=/absolute/path/to/.dsh/profiles/web
|
|
79
|
-
DSH_COMPOSED_DUMP=/tmp/dsh-web-composed.yml
|
|
80
|
-
GUARD_HOST_LOCK="$DSH_PROFILE_ROOT/node_modules/.bin/dsh-completion-guard-host-lock"
|
|
62
|
+
默认 `opt-in` 模式只在会话执行 `/context-guard on` 后开始保护。如需让某个 DSH profile 自动启用 Guard,请在该 profile 的 `cordis.patch.yml` 中增加:
|
|
81
63
|
|
|
82
|
-
|
|
83
|
-
|
|
84
|
-
dsh
|
|
85
|
-
|
|
64
|
+
```yaml
|
|
65
|
+
- id: context-guard
|
|
66
|
+
name: dsh-completion-guard
|
|
67
|
+
config:
|
|
68
|
+
activation: always
|
|
86
69
|
```
|
|
87
70
|
|
|
88
|
-
|
|
71
|
+
重启 profile 后执行 `/context-guard status`。`always` 会在日志重放前启用 Guard,因此重建已有会话时也可能捕获日志中的早期用户消息。如果只希望从显式命令开始保护,请保留 `opt-in`。
|
|
89
72
|
|
|
90
|
-
|
|
73
|
+
## 如何检查完成状态
|
|
91
74
|
|
|
92
|
-
|
|
75
|
+
启用后,Guard 会保存用户直接给出的要求和验收条件。只有已保存的工具结果与指定命令、文件或其他目标一致时,才能作为证据。模型在报告整个任务完成前必须通过 Guard 检查;证据缺失、过期或对象不一致时,任务会保持未完成。
|
|
93
76
|
|
|
94
|
-
|
|
77
|
+
只读证据收集与修改包、文件、服务或 Git 状态的操作使用不同工具。查询成功不会自动产生变更权限。精确命令限制和平台证据见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md)。
|
|
95
78
|
|
|
96
79
|
## 边界
|
|
97
80
|
|
|
@@ -108,12 +91,6 @@ Context Guard 负责完成认证;Goal、Todo、Compaction、continuation、权
|
|
|
108
91
|
|
|
109
92
|
两个项目不共享运行时状态、安装器、缓存或发布历史。修复应先进入拥有对应运行时的仓库;只有同一行为确实适用于两侧时,才显式迁移。具体复用与替换边界见 [`docs/UPSTREAM_BASE.md`](docs/UPSTREAM_BASE.md) 和 [`docs/PORTING_NOTES.md`](docs/PORTING_NOTES.md)。
|
|
110
93
|
|
|
111
|
-
## npm 下载量历史
|
|
112
|
-
|
|
113
|
-
|
|
114
|
-
|
|
115
|
-
该累计图分别展示新旧 npm 包的总量,以竖线标记 2026-08-29 更名,并且只在项目增长曲线中合并两者。npm 下载量统计的是 registry 请求次数,不等于独立用户数或已确认的真实安装人数。工作流每天运行,也支持手动触发。
|
|
116
|
-
|
|
117
94
|
## 文档
|
|
118
95
|
|
|
119
96
|
- [`CHANGELOG.zh-CN.md`](CHANGELOG.zh-CN.md) — 面向使用者的版本变化。
|
package/dist/domain/index.d.ts
CHANGED
|
@@ -1,2 +1,2 @@
|
|
|
1
|
-
import { $ as gitCommandMatchesTarget, $n as
|
|
2
|
-
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ActionManifest, ActionSpec, ActiveProfileHostLock, AssistantOutcomeObservation, AuditedExecutable, AuthorityBlock, AuthorityBlockKind, AuthorityKind, BASE_HOST_PACKAGES, BoundaryDisposition, BoundaryEffectuation, BoundaryQualification, BoundaryQualificationKind, BoundaryRequest, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, CanonicalArgv, CanonicalCommandSurface, CaptureScope, CheckpointResult, ClassifiedClause, ClauseSegment, CommandSurfaceManifest, CompletionDisposition, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, DeferAuthorization, DeriveConfig, DeriveResult, DeriveScope, DerivedEnvelope, EXPECTED_HOST_PACKAGES, EvidenceBinding, EvidenceFacetCoverage, EvidenceOutcome, EvidenceParseStatus, EvidenceRole, ExecutableIdentity, ExecutableIdentityBinding, ExpectedTransition, ExternalOperation, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, GitAdapterAction, GitCommandAccepted, GitCommandManifest, GitCommandParseResult, GitCommandRejected, GitEffectExecution, GitEffectRunner, GitPrestateCheck, GitPrestateEnvelope, GitTargetIdentity, GoalActivationState, GoalBoundaryAccess, GoalRef, GuardBoundary, GuardCheckpoint, GuardEvidence, GuardIntegrity, GuardItem, GuardItemKind, GuardItemStatus, GuardOperation, GuardProjection, HOST_CAPABILITY_PACKAGE_GROUPS, HostCapabilityEvaluation, HostCapabilityId, HostCapabilityRequest, HostLockContext, HostLockEvaluation, HostLockStatus, HostPlatform, HostProfileError, HostProfileKind, HostStatus, HostToolSurface, LinearCommitReadback, ManifestIssue, OperationVerbEntry, PROTOCOL_V3_NOTICE, ParsedShell, PersistenceAuthorization, RecoveryOptions, RejectedBinding, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS,
|
|
1
|
+
import { $ as gitCommandMatchesTarget, $n as TargetCaptureReasonCode, $t as AuthorityBlockKind, A as hostLockRowsFromComposedDump, An as DeferAuthorization, Ar as sanitizeUrl, At as HOST_CAPABILITY_PACKAGE_GROUPS, B as GitCommandManifest, Bn as ExternalOperation, Bt as HostLockStatus, C as CommandSurfaceManifest, Cn as GoalBoundaryAccess, Cr as semanticActionFromText, Ct as AuditedExecutable, D as ActiveProfileHostLock, Dn as qualifyBoundary, Dr as digestStrings, Dt as ExecutableIdentity, E as validateManifest, En as isCurrentAcceptedBoundary, Er as canonicalizePath, Et as EXPECTED_HOST_PACKAGES, F as resolveInstalledHostLock, Fn as EvidenceBinding, Ft as HostCohort, G as GitPrestateCheck, Gn as GuardIntegrity, Gt as bindLiveGoalCapability, H as GitCommandRejected, Hn as GuardBoundary, Ht as HostProfileKind, I as verifyComposedHostLockDump, In as EvidenceOutcome, It as HostCohortSelection, J as LinearCommitReadback, Jn as GuardItemStatus, Jt as evaluateHostLock, K as GitPrestateEnvelope, Kn as GuardItem, Kt as evaluateExternalWaitCapability, L as GIT_COMMAND_MANIFEST_IDS, Ln as EvidenceParseStatus, Lt as HostCohortSelectionReason, M as packageRowsFromActiveGraph, Mn as DeriveResult, Mt as HostCapabilityEvaluation, N as packageRowsFromPnpmLock, Nn as DeriveScope, Nt as HostCapabilityId, O as HostProfileError, On as BoundaryDisposition, Or as normalizeClause, Ot as ExecutableIdentityBinding, P as resolveActiveProfileHostLock, Pn as DerivedEnvelope, Pt as HostCapabilityRequest, Q as executeRevalidatedGitEffect, Qn as PersistenceAuthorization, Qt as AuthorityBlock, R as GitAdapterAction, Rn as EvidenceRole, Rt as HostLockContext, S as COMMAND_SURFACE_MANIFEST, Sn as GoalActivationState, Sr as semanticActionFromCommand, St as deriveProjection, T as OperationVerbEntry, Tn as effectuateBoundary, Tr as validateActionTarget, Tt as DEFAULT_HOST_LOCK, U as GitEffectExecution, Un as GuardCheckpoint, Ut as HostToolSurface, V as GitCommandParseResult, Vn as GoalRef, Vt as HostPlatform, W as GitEffectRunner, Wn as GuardEvidence, Wt as bindExecutableIdentity, X as commitTreeSnapshotDigest, Xn as GuardProjection, Xt as selectHostCohort, Y as commitIndexSnapshotDigest, Yn as GuardOperation, Yt as evaluateToolSurfaceCapability, Z as createGitPrestateEnvelope, Zn as HostStatus, Zt as currentContractDigest, _ as EvidenceFacetCoverage, _n as isInformationalMessage, _r as StatefulAction, _t as extractTextContent, a as classifyCompletionClaim, an as CheckpointResult, ar as createProjection, at as ParsedShell, b as evidenceMatchesItem, bn as BoundaryQualification, br as requestedTargetAuthorizesMutation, bt as withDurability, c as isWholeTaskCompletionClaim, cn as CaptureScope, cr as ACTION_MANIFEST_VERSION, ct as isRunExecutable, d as DEFAULT_RECOVERY_CHAR_BUDGET, dn as captureClause, dr as CERTIFICATE_VERSION, dt as goalCompletionDenial, en as AuthorityKind, er as TargetCaptureStatus, et as parseGitCommandManifest, f as RecoveryOptions, fn as captureItem, fr as SEMANTIC_ACTIONS, ft as hasCurrentCertificate, g as renderRecoveryPacket, gn as extractOperation, gr as SemanticAction, gt as evidenceFromPersistedToolResult, h as recoveryDigest, hn as extractMethod, hr as SUPPORTED_EVIDENCE_ADAPTERS, ht as ToolSubject, i as TurnStoppingDecision, in as classifyUserInteraction, ir as WaitAuthorization, it as CanonicalCommandSurface, j as injectActiveProfileHostLock, jn as DeriveConfig, jr as sha256, jt as HOST_COHORTS, k as hostLockContextFromComposedDump, kn as BoundaryQualificationKind, kr as sanitizeClauseText, kt as GOAL_HOST_PACKAGES, l as latestAssistantText, ln as ClassifiedClause, lr as ActionManifest, lt as parsePwshCommand, m as openItems, mn as extractArtifactPaths, mr as STOP_PROTOCOL_VERSION, mt as ToolResultInput, n as AssistantOutcomeObservation, nn as segmentAuthorityBlocks, nr as TargetValue, nt as verifiedLinearCommitReadback, o as decideTurnBoundary, on as RejectedBinding, ot as ShellParseStatus, p as closingHint, pn as classifyClause, pr as STATEFUL_ACTIONS, pt as ToolCallInput, q as GitTargetIdentity, qn as GuardItemKind, qt as evaluateHostCapability, r as CompletionDisposition, rn as UserInteractionKind, rr as VerificationContract, rt as CanonicalArgv, s as decideTurnStopping, sn as certifyCheckpoint, sr as ACTION_MANIFEST, st as canonicalArgvFromCommand, t as supersedeItem, tn as authorityCaptureCounts, tr as TargetTuple, tt as revalidateGitPrestate, u as observeAssistantOutcome, un as ClauseSegment, ur as ActionSpec, ut as parseShellCommand, v as bindingSatisfies, vn as segmentClauses, vr as actionCompatible, vt as extractToolSubject, w as ManifestIssue, wn as availableBoundaryQualifications, wr as validateActionManifest, wt as BASE_HOST_PACKAGES, x as isVerifyingCapability, xn as BoundaryRequest, xr as requestedTargetMatchesResolved, xt as PROTOCOL_V3_NOTICE, y as evidenceCoverage, yn as BoundaryEffectuation, yr as isStatefulAction, yt as isDeterministicCheck, z as GitCommandAccepted, zn as ExpectedTransition, zt as HostLockEvaluation } from "../index-CTFLYvNL.js";
|
|
2
|
+
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ActionManifest, ActionSpec, ActiveProfileHostLock, AssistantOutcomeObservation, AuditedExecutable, AuthorityBlock, AuthorityBlockKind, AuthorityKind, BASE_HOST_PACKAGES, BoundaryDisposition, BoundaryEffectuation, BoundaryQualification, BoundaryQualificationKind, BoundaryRequest, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, CanonicalArgv, CanonicalCommandSurface, CaptureScope, CheckpointResult, ClassifiedClause, ClauseSegment, CommandSurfaceManifest, CompletionDisposition, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, DeferAuthorization, DeriveConfig, DeriveResult, DeriveScope, DerivedEnvelope, EXPECTED_HOST_PACKAGES, EvidenceBinding, EvidenceFacetCoverage, EvidenceOutcome, EvidenceParseStatus, EvidenceRole, ExecutableIdentity, ExecutableIdentityBinding, ExpectedTransition, ExternalOperation, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, GitAdapterAction, GitCommandAccepted, GitCommandManifest, GitCommandParseResult, GitCommandRejected, GitEffectExecution, GitEffectRunner, GitPrestateCheck, GitPrestateEnvelope, GitTargetIdentity, GoalActivationState, GoalBoundaryAccess, GoalRef, GuardBoundary, GuardCheckpoint, GuardEvidence, GuardIntegrity, GuardItem, GuardItemKind, GuardItemStatus, GuardOperation, GuardProjection, HOST_CAPABILITY_PACKAGE_GROUPS, HOST_COHORTS, HostCapabilityEvaluation, HostCapabilityId, HostCapabilityRequest, HostCohort, HostCohortSelection, HostCohortSelectionReason, HostLockContext, HostLockEvaluation, HostLockStatus, HostPlatform, HostProfileError, HostProfileKind, HostStatus, HostToolSurface, LinearCommitReadback, ManifestIssue, OperationVerbEntry, PROTOCOL_V3_NOTICE, ParsedShell, PersistenceAuthorization, RecoveryOptions, RejectedBinding, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, SemanticAction, ShellParseStatus, StatefulAction, TargetCaptureReasonCode, TargetCaptureStatus, TargetTuple, TargetValue, ToolCallInput, ToolResultInput, ToolSubject, TurnStoppingDecision, UserInteractionKind, VerificationContract, WaitAuthorization, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindingSatisfies, canonicalArgvFromCommand, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, selectHostCohort, semanticActionFromCommand, semanticActionFromText, sha256, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|
package/dist/domain/index.js
CHANGED
|
@@ -1,3 +1,3 @@
|
|
|
1
|
-
import { $ as
|
|
1
|
+
import { $ as segmentAuthorityBlocks, A as extractToolSubject, At as STATEFUL_ACTIONS, B as DEFAULT_HOST_LOCK, Bt as validateActionTarget, C as latestAssistantText, Ct as segmentClauses, D as supersedeItem, Dt as ACTION_MANIFEST_VERSION, E as deriveProjection, Et as ACTION_MANIFEST, F as parsePwshCommand, Ft as requestedTargetAuthorizesMutation, G as bindExecutableIdentity, Gt as normalizeClause, H as GOAL_HOST_PACKAGES, Ht as validateManifest, I as parseShellCommand, It as requestedTargetMatchesResolved, J as evaluateHostCapability, Jt as sha256, K as bindLiveGoalCapability, Kt as sanitizeClauseText, L as goalCompletionDenial, Lt as semanticActionFromCommand, M as withDurability, Mt as SUPPORTED_EVIDENCE_ADAPTERS, N as canonicalArgvFromCommand, Nt as actionCompatible, O as evidenceFromPersistedToolResult, Ot as CERTIFICATE_VERSION, P as isRunExecutable, Pt as isStatefulAction, Q as authorityCaptureCounts, R as hasCurrentCertificate, Rt as semanticActionFromText, S as isWholeTaskCompletionClaim, St as isInformationalMessage, T as PROTOCOL_V3_NOTICE, U as HOST_CAPABILITY_PACKAGE_GROUPS, Ut as canonicalizePath, V as EXPECTED_HOST_PACKAGES, Vt as COMMAND_SURFACE_MANIFEST, W as HOST_COHORTS, Wt as digestStrings, X as evaluateToolSurfaceCapability, Y as evaluateHostLock, Yt as createProjection, Z as selectHostCohort, _ as revalidateGitPrestate, _t as captureItem, a as packageRowsFromActiveGraph, at as certifyCheckpoint, b as decideTurnBoundary, bt as extractMethod, c as resolveInstalledHostLock, ct as openItems, d as commitIndexSnapshotDigest, dt as bindingSatisfies, et as classifyUserInteraction, f as commitTreeSnapshotDigest, ft as evidenceCoverage, g as parseGitCommandManifest, gt as captureClause, h as gitCommandMatchesTarget, ht as currentContractDigest, i as injectActiveProfileHostLock, it as qualifyBoundary, j as isDeterministicCheck, jt as STOP_PROTOCOL_VERSION, k as extractTextContent, kt as SEMANTIC_ACTIONS, l as verifyComposedHostLockDump, lt as recoveryDigest, m as executeRevalidatedGitEffect, mt as isVerifyingCapability, n as hostLockContextFromComposedDump, nt as effectuateBoundary, o as packageRowsFromPnpmLock, ot as DEFAULT_RECOVERY_CHAR_BUDGET, p as createGitPrestateEnvelope, pt as evidenceMatchesItem, q as evaluateExternalWaitCapability, qt as sanitizeUrl, r as hostLockRowsFromComposedDump, rt as isCurrentAcceptedBoundary, s as resolveActiveProfileHostLock, st as closingHint, t as HostProfileError, tt as availableBoundaryQualifications, u as GIT_COMMAND_MANIFEST_IDS, ut as renderRecoveryPacket, v as verifiedLinearCommitReadback, vt as classifyClause, w as observeAssistantOutcome, x as decideTurnStopping, xt as extractOperation, y as classifyCompletionClaim, yt as extractArtifactPaths, z as BASE_HOST_PACKAGES, zt as validateActionManifest } from "../domain-DPPFAcbF.js";
|
|
2
2
|
|
|
3
|
-
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, BASE_HOST_PACKAGES, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, EXPECTED_HOST_PACKAGES, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, HOST_CAPABILITY_PACKAGE_GROUPS, HostProfileError, PROTOCOL_V3_NOTICE, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS,
|
|
3
|
+
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, BASE_HOST_PACKAGES, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, EXPECTED_HOST_PACKAGES, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, HOST_CAPABILITY_PACKAGE_GROUPS, HOST_COHORTS, HostProfileError, PROTOCOL_V3_NOTICE, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindingSatisfies, canonicalArgvFromCommand, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, selectHostCohort, semanticActionFromCommand, semanticActionFromText, sha256, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|