dsh-completion-guard 0.2.1 → 0.3.0
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/CHANGELOG.md +24 -1
- package/CHANGELOG.zh-CN.md +24 -1
- package/README.md +45 -5
- package/README.zh-CN.md +45 -5
- package/bin/dsh-completion-guard-host-lock.mjs +52 -0
- package/dist/domain/index.d.ts +2 -2
- package/dist/domain/index.js +2 -2
- package/dist/domain-CBvBQHTL.js +5828 -0
- package/dist/index-GvKLkTqV.d.ts +957 -0
- package/dist/index.d.ts +9 -2
- package/dist/index.js +2463 -119
- package/docs/ARCHITECTURE.md +11 -7
- package/docs/COMPATIBILITY.md +23 -3
- package/docs/LOCAL_ACCEPTANCE.md +192 -1
- package/docs/SEMANTIC_COMPATIBILITY.md +118 -0
- package/docs/distribution.md +45 -0
- package/docs/upstream-deltas.json +217 -0
- package/manifests/action-manifest.v1.json +33 -0
- package/manifests/git-command-manifest.v2.json +52 -0
- package/manifests/supported-host.v1.json +66 -0
- package/package.json +52 -14
- package/dist/domain-BN3_AuUr.js +0 -1997
- package/dist/index-Dk4SkQ8H.d.ts +0 -448
package/CHANGELOG.md
CHANGED
|
@@ -2,12 +2,35 @@
|
|
|
2
2
|
|
|
3
3
|
All notable changes to this project are documented here. The project is pre-1.0; release versions track the plugin lifecycle, not stabilised API promises.
|
|
4
4
|
|
|
5
|
-
##
|
|
5
|
+
## 0.3.0 - 2026-08-31
|
|
6
|
+
|
|
7
|
+
### Added
|
|
8
|
+
|
|
9
|
+
- **v0.3 semantic completion gates.** Adds exact paired optional Goal state/tool peers, an injected exact-version/integrity action/platform host lock, versioned action/Git/supported-host manifests, authority-aware contract segmentation, typed boundaries, structured checkpoint diagnostics, and digest-v3 certificates bound to session, host, contract, evidence, binding, expected transition, and optional Goal identity.
|
|
10
|
+
- **Stateful action readback.** `install`, `apply`, `create`, `modify`, `restart`, `commit`, `push`, `publish`, `pull`, and `fetch` require distinct resolution, effect, and independent state evidence with same-target role closure. Generic-run evidence cannot authorize a v0.3 user-level completion; legacy generic-run certificates remain audit history only.
|
|
11
|
+
- **Explicit read-only and mutation tools.** `context_guard_evidence` never mutates; `context_guard_action` owns exact-tgz package/registry effects, two-phase dshmarket restart, and exact Git effects only after an exact pending root requirement/revision, complete action-specific requested identity, target digest, host identity, executable identity, and live prestate all match. Prohibitions/acceptances cannot authorize effects; v0.3 package versions and Git refs are exact-only.
|
|
12
|
+
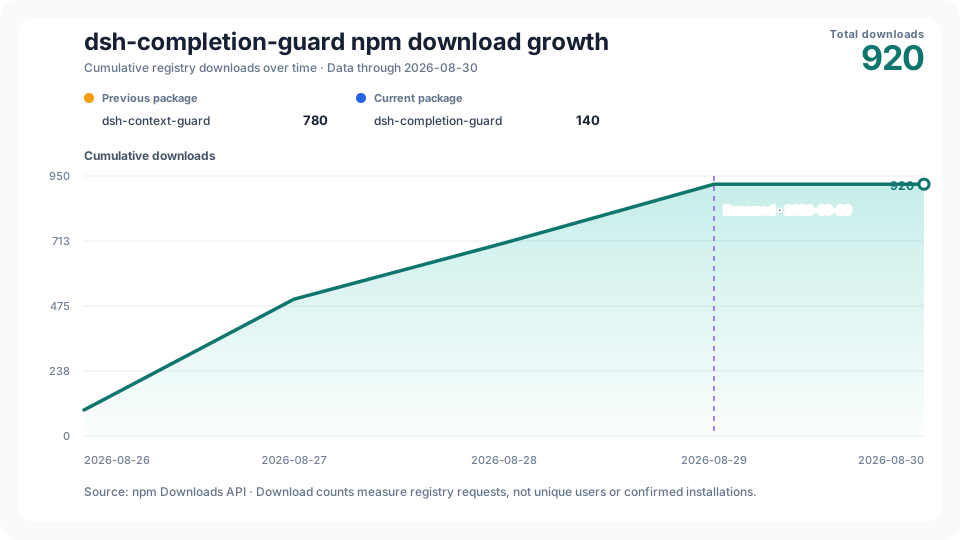
- **Bilingual npm download history.** A daily cumulative chart keeps the renamed `dsh-context-guard` and current `dsh-completion-guard` package totals separate while presenting one project-growth line. Collection reconciles npm range and point responses before publishing English and Simplified Chinese SVGs.
|
|
13
|
+
|
|
14
|
+
### Fixed
|
|
15
|
+
|
|
16
|
+
- Assistant prose no longer controls turn stopping. Goal continuation remains owned by the Goal Round Driver; only persisted, qualified typed boundaries can trigger post-commit same-ref disarm readback.
|
|
17
|
+
- Unknown, missing, or drifted host identities fail closed. The Guard-owned `update_goal(action=complete)` path is checked before mutation; trusted in-process direct Goal/session writes are detected as integrity violations but are not claimed to be preventable.
|
|
18
|
+
- Active host identity is supplied before certificate replay, managed host-lock injection is idempotent, DSH folded-YAML SRI output is parsed exactly, and a fresh profile's sole top-level `[]` sentinel is safely replaced before the managed list is appended.
|
|
19
|
+
- Publish now freezes one canonical HTTPS registry across capture, npm argv, and standard packument readback, with `--ignore-scripts`; create/modify freeze their expected post-effect bytes at resolution time instead of copying the observed digest into the predicate, and modify rejects source-byte drift against its frozen pre-digest.
|
|
20
|
+
- Windows stateful actions now resolve and version-probe audited `.cmd`/`.bat` shims through a closed invocation whose interpreter is pinned to the canonical `SystemRoot\\System32\\cmd.exe` realpath and version. Resolution and effect bind both identities, then execute the same revalidated paths instead of searching `PATH` or trusting a changed `ComSpec`; shell-control and expansion characters remain fail-closed.
|
|
21
|
+
- The npm statistics publisher now rejects non-default refs before checkout, isolates read-only collection from the write-capable publication job, does not persist credentials during collection, and pins all official Actions to immutable commits.
|
|
6
22
|
|
|
7
23
|
### Changed
|
|
8
24
|
|
|
9
25
|
- **Package renamed from `dsh-context-guard` to `dsh-completion-guard`.** An unrelated DSH plugin (kpl0111/dsh-context-guard, tool-result pruning) already uses the name; the rename removes the collision for name-keyed registries and lists. The internal Cordis bundle id stays `context-guard`, so installed profiles keep their runtime identity. The previous npm package `dsh-context-guard` will be deprecated once `dsh-completion-guard` is published.
|
|
10
26
|
|
|
27
|
+
### Validation
|
|
28
|
+
|
|
29
|
+
- Runtime source commit `4f079499509822425c80e0b5ab98d1ebc58da9d5` passed the 19-file deterministic suite on macOS (351 passed, one Windows-only capability skip) and native Windows (352 passed, no skips), including all 37 portable semantic cases and 29 digest vectors.
|
|
30
|
+
- Canonical pre-release artifact `72d848e313a0e35e06fd1f493215cc0338b86a79a8001a4f07156e782157fe08` from commit `a33b69326eb46fbefc56affc55e2a486695f545c` passed same-byte isolated Web/Headless installation, host-lock readback, real dshmarket restart, HTTP recovery, and cleanup on macOS and native Windows. CI run 33320743166 passed the exact commit on Ubuntu, macOS, and Windows with Node.js 22 and 24.
|
|
31
|
+
- A credentialed model session produced a valid evidence binding and exercised persisted typed-boundary acceptance plus same-Goal disarm readback. An intentionally over-broad prompt remained incomplete and received no false completion certificate; this bounded result is not a claim that arbitrary model instructions are semantically certifiable.
|
|
32
|
+
- The npm statistics suite passes 8 focused tests covering date chunking, response normalization and reconciliation, scoped package URLs, upstream failures, and preservation of the previous output set. Release packaging freezes one documentation-inclusive tarball for native-platform verification and registry publication; published checksums and registry integrity identify those exact bytes.
|
|
33
|
+
|
|
11
34
|
## 0.2.1 - 2026-08-28
|
|
12
35
|
|
|
13
36
|
### Fixed
|
package/CHANGELOG.zh-CN.md
CHANGED
|
@@ -2,12 +2,35 @@
|
|
|
2
2
|
|
|
3
3
|
本项目的重要变化记录在这里。项目仍处于 1.0 之前;版本号跟踪插件生命周期,不代表 API 已稳定。
|
|
4
4
|
|
|
5
|
-
##
|
|
5
|
+
## 0.3.0 - 2026-08-31
|
|
6
|
+
|
|
7
|
+
### 新增
|
|
8
|
+
|
|
9
|
+
- **v0.3 语义完成门禁。** 增加 Goal state/tool 成对精确 optional peers、显式注入的 exact version/integrity action/platform 宿主锁、版本化 action/Git/supported-host manifests、按权威分段的合同捕获、typed boundary、结构化 checkpoint 诊断,以及绑定 session、host、contract、evidence、binding、expected transition 与可选 Goal 身份的 digest-v3 证书。
|
|
10
|
+
- **有状态动作独立读回。** `install`、`apply`、`create`、`modify`、`restart`、`commit`、`push`、`publish`、`pull`、`fetch` 必须提供不同 ID 的 resolution、effect 与独立 state evidence,并完成同目标 role 闭合。generic-run 证据不能授权 v0.3 用户级完成;旧 generic-run 证书只保留为审计历史。
|
|
11
|
+
- **显式只读/变更工具。** `context_guard_evidence` 永不执行 mutation;`context_guard_action` 仅在精确的 pending 根用户 requirement/修订、完整动作身份、target digest、宿主身份、可执行文件身份和 live prestate 全部匹配后,才执行 exact-tgz package/registry effect、两阶段 dshmarket restart 或精确 Git effect。prohibition/acceptance 不得授权 effect;v0.3 package 版本与 Git ref 仅支持 exact。
|
|
12
|
+
- **双语 npm 下载量历史。** 每日累计图分别保留更名前的 `dsh-context-guard` 与当前 `dsh-completion-guard` 包总量,同时呈现一条项目增长曲线。采集器会先核对 npm range 与 point 响应,再发布英文和简体中文 SVG。
|
|
13
|
+
|
|
14
|
+
### 修复
|
|
15
|
+
|
|
16
|
+
- assistant 散文不再控制 turn stopping。正常 Goal 续行仍只由 Goal Round Driver 调度;只有已持久化且资格成立的 typed boundary 才能在提交后触发同 Goal ref 的 disarm 双读回。
|
|
17
|
+
- 未知、缺失或漂移的宿主身份一律 fail-closed。Guard 自己注册并守卫的 `update_goal(action=complete)` 路径在 mutation 前检查;可信进程内直接写 Goal/session 的旁路只记录 integrity violation,不声称能够阻止。
|
|
18
|
+
- 活动 host identity 会在 certificate replay 前传入;managed host-lock injection 保持幂等;DSH folded-YAML SRI 输出会被精确解析,新 profile 唯一的顶层 `[]` sentinel 会在追加 managed list 前安全替换。
|
|
19
|
+
- Publish 现在会在捕获、npm argv 与标准 packument readback 之间冻结同一个 canonical HTTPS registry,并显式使用 `--ignore-scripts`;create/modify 在 resolution 阶段冻结预期 post-effect 字节,不再把 observed digest 回填为谓词,且 modify 会按冻结 pre-digest 拒绝源字节漂移。
|
|
20
|
+
- Windows 有状态动作现在通过封闭调用解析并探测已审计 `.cmd`/`.bat` shim 的版本,其中解释器固定为 canonical `SystemRoot\\System32\\cmd.exe` realpath 与版本。resolution/effect 同时绑定 shim 与解释器身份,执行时复用经重校验的路径,不再二次搜索 `PATH` 或信任已变化的 `ComSpec`;shell 控制字符与展开字符继续 fail-closed。
|
|
21
|
+
- npm 统计发布器现在会在 checkout 前拒绝非默认 ref,把只读采集与具有写权限的发布 job 隔离,采集阶段不持久化凭据,并把全部官方 Action 固定到不可变提交。
|
|
6
22
|
|
|
7
23
|
### 变更
|
|
8
24
|
|
|
9
25
|
- **包名由 `dsh-context-guard` 更名为 `dsh-completion-guard`。** 无关的 DSH 插件(kpl0111/dsh-context-guard,工具结果剪裁)已占用该名称;更名消除按名字建索引的注册面与列表上的冲突。内部 Cordis bundle id 保持 `context-guard` 不变,已安装 profile 的运行时身份不受影响。`dsh-completion-guard` 发布后,原 npm 包 `dsh-context-guard` 将被 deprecate。
|
|
10
26
|
|
|
27
|
+
### 验证
|
|
28
|
+
|
|
29
|
+
- 运行时源码提交 `4f079499509822425c80e0b5ab98d1ebc58da9d5` 的 19 文件确定性测试在 macOS 通过 351 项并按能力跳过 1 项 Windows-only 测试,在原生 Windows 通过全部 352 项且无跳过;其中包含 37 个 portable semantic case 和 29 个 digest vector。
|
|
30
|
+
- 提交 `a33b69326eb46fbefc56affc55e2a486695f545c` 生成的 canonical 预发布工件 `72d848e313a0e35e06fd1f493215cc0338b86a79a8001a4f07156e782157fe08`,以同一字节在 macOS 与原生 Windows 通过隔离 Web/Headless 安装、host-lock 读回、真实 dshmarket 重启、HTTP 恢复与清理。CI run 33320743166 在 Ubuntu、macOS、Windows 的 Node.js 22/24 组合上通过该精确提交。
|
|
31
|
+
- 带凭据的真实模型会话产生了有效 evidence binding,并验证持久化 typed boundary 接受与同一 Goal 的 disarm 读回。一个刻意过宽的提示词保持 incomplete,且未被错误签发完成证书;该有界结果不表示任意模型指令都能获得语义认证。
|
|
32
|
+
- npm 统计套件的 8 项聚焦测试覆盖日期切块、响应规范化与核对、scope 包 URL、上游失败以及失败时保留上一组输出。发布打包会冻结一份包含文档的 tarball,供原生平台验证与 registry 发布;公开 checksum 与 registry integrity 标识这份精确字节。
|
|
33
|
+
|
|
11
34
|
## 0.2.1 - 2026-08-28
|
|
12
35
|
|
|
13
36
|
### 修复
|
package/README.md
CHANGED
|
@@ -4,12 +4,14 @@
|
|
|
4
4
|
|
|
5
5
|
A task-contract and completion-certification plugin for DeepSeek Harness (DSH). It preserves requirements, prohibitions, acceptance criteria, later corrections, and bounded evidence so a task can be certified only when current successful evidence matches the current contract.
|
|
6
6
|
|
|
7
|
+

|
|
8
|
+
|
|
7
9
|
## Quick start
|
|
8
10
|
|
|
9
11
|
Install the published plugin into a DSH Web profile:
|
|
10
12
|
|
|
11
13
|
```sh
|
|
12
|
-
dsh plugin --profile web add dsh-completion-guard@0.
|
|
14
|
+
dsh plugin --profile web add dsh-completion-guard@0.3.0
|
|
13
15
|
```
|
|
14
16
|
|
|
15
17
|
Restart DSH Web, open a session, and enable the guard:
|
|
@@ -49,15 +51,45 @@ Once enabled, Context Guard captures direct user requirements and acceptance cri
|
|
|
49
51
|
- Derives bounded, redacted evidence from persisted DSH tool calls and results.
|
|
50
52
|
- Requires method, operation, subject, surface, and outcome to match where the contract makes them explicit.
|
|
51
53
|
- Re-verifies certificates when a session is rebuilt or resumed and fails closed on integrity loss.
|
|
52
|
-
- Blocks
|
|
54
|
+
- Blocks the Guard-owned model-tool Goal completion path while enabled unless a current certificate exists; trusted in-process direct Goal/session writes are detected as integrity violations, not universally prevented.
|
|
53
55
|
|
|
54
56
|
## Status and compatibility
|
|
55
57
|
|
|
56
|
-
Version 0.
|
|
58
|
+
Version 0.3.0 is available from [npm](https://www.npmjs.com/package/dsh-completion-guard) and the [GitHub release](https://github.com/GreenLv/dsh-completion-guard/releases/tag/v0.3.0).
|
|
57
59
|
|
|
58
60
|
> The project was renamed from `dsh-context-guard` to `dsh-completion-guard` on 2026-08-29 to avoid a name collision with an unrelated DSH plugin (kpl0111/dsh-context-guard, tool-result pruning). The internal Cordis bundle id stays `context-guard`, and the previous npm package `dsh-context-guard` will be deprecated in favor of this package. It targets DSH `0.1.1-rc.2`, Node.js `>=22`, and pnpm `>=11`.
|
|
59
61
|
|
|
60
|
-
|
|
62
|
+
### Earlier v0.2.x evidence
|
|
63
|
+
|
|
64
|
+
The 0.2.1 release suite contains 138 tests (105 domain/core). It attributes shell evidence to the session cwd when the tool omits `workdir`, supports literal `2>&1` diagnostics and read-only inspection commands, maps process verbs to run evidence, and exposes actionable hints when a checkpoint binding is rejected. 0.2.1 adds a session-layer capture filter so clarification questions, meta comments, and bare progression phrases (`继续`, `continue`) never become contract items; de-duplicates repeated recovery notifications; adds `/context-guard clear`; and documents how a goal completes when the guard is disabled or blocked. A macOS live Web run loaded the published profile package and certified a real `pnpm test` result.
|
|
65
|
+
|
|
66
|
+
The Windows TEMP readback verifies the `b75868e9e73d29f50530ddaba15cfaef82e03ece` source matrix and the exact-source tarball → isolated installation → dump-config → Web startup log and cleanup chain. HTTP 200 appeared only in the first-run stdout, was not persisted, and was not rerun during readback, so the HTTP response itself is not independently confirmed. A real model-session smoke remains not run.
|
|
67
|
+
|
|
68
|
+
### v0.3.0
|
|
69
|
+
|
|
70
|
+
Version 0.3.0 adds semantic action/target binding, independent state readback for stateful actions, typed boundaries, digest-v3 certificates, exact active-host identity, and paired optional Goal integration. The 19-file deterministic suite passed 351 tests with one Windows-only capability skip on macOS and all 352 tests without skips on native Windows. One canonical pre-release tarball was then installed and read back byte-for-byte on both native platforms, while CI covered Ubuntu, macOS, and Windows on Node.js 22 and 24. A credentialed model session verified a valid evidence binding and persisted typed-boundary/disarm flow; an intentionally over-broad prompt stayed incomplete and received no false certificate. [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md) separates these source, artifact, CI, model-session, and publication evidence scopes.
|
|
71
|
+
|
|
72
|
+
The release uses [`manifests/action-manifest.v1.json`](manifests/action-manifest.v1.json), [`manifests/git-command-manifest.v2.json`](manifests/git-command-manifest.v2.json), and [`manifests/supported-host.v1.json`](manifests/supported-host.v1.json). Goal integration requires the exact optional peers `@deepseek-ai/dsh-goal@0.1.1-rc.2` and `@deepseek-ai/dsh-tool-goal@0.1.1-rc.2` together. It fails closed unless the active DSH runtime/profile graph injects the exact `hostLockPackages`, platform, and profile identity. A nearest lockfile is not accepted because DSH core and profile plugins use separate package graphs. The default bundled patch deliberately contains no fabricated lock.
|
|
73
|
+
|
|
74
|
+
After installing the release into a profile, generate and verify its active identity with the packaged CLI. Use absolute paths for the actual DSH installation; the dump is an inspection artifact, not a configuration source:
|
|
75
|
+
|
|
76
|
+
```sh
|
|
77
|
+
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
78
|
+
DSH_PROFILE_ROOT=/absolute/path/to/.dsh/profiles/web
|
|
79
|
+
DSH_COMPOSED_DUMP=/tmp/dsh-web-composed.yml
|
|
80
|
+
GUARD_HOST_LOCK="$DSH_PROFILE_ROOT/node_modules/.bin/dsh-completion-guard-host-lock"
|
|
81
|
+
|
|
82
|
+
"$GUARD_HOST_LOCK" inspect --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
83
|
+
"$GUARD_HOST_LOCK" inject --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
84
|
+
dsh --profile web --dump-config > "$DSH_COMPOSED_DUMP"
|
|
85
|
+
"$GUARD_HOST_LOCK" verify-dump --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT" --dump-config "$DSH_COMPOSED_DUMP"
|
|
86
|
+
```
|
|
87
|
+
|
|
88
|
+
`inspect` and `inject` reject missing, duplicate, multi-version, or drifted critical packages. `verify-dump` then proves that DSH composed the same bounded tuple that was read from the active graphs. Repeat the flow after any DSH/profile/package upgrade. Until it succeeds, certification, Goal-dependent completion, and affected action capabilities remain unavailable. Release validation used fresh isolated profiles and did not overwrite the user's existing DSH profiles.
|
|
89
|
+
|
|
90
|
+
`context_guard_evidence` is read-only: it resolves targets, validates persisted effects, and performs independent state readback. Mutating install/apply/restart/publish and exact Git commit/push/pull/fetch operations use the separately named `context_guard_action` tool. A resolution is not mutation authority: the caller must identify the exact pending root-owned requirement and revision, repeat the persisted target digest, and match every action-specific identity field before any executable, HTTP request, or restart intent runs. Prohibitions and acceptance clauses never authorize mutation. Package/apply/publish authority is exact-version-only in v0.3; Git authority requires an explicit remote and canonical full ref/refspec. The presentation surface shows the canonical target and command-manifest digest before execution.
|
|
91
|
+
|
|
92
|
+
Publish targets use one canonical HTTPS registry base with no credentials, query, fragment, ambiguous path, or control characters; the same base is frozen in the root contract, npm argv, and registry readback. Create and modify resolutions freeze the expected post-write digest before effect; modify re-hashes the source bytes against the frozen pre-digest before applying the pinned unique UTF-8 replacement semantics, so either prestate drift or different post-effect bytes fail closed.
|
|
61
93
|
|
|
62
94
|
Context Guard recognizes only a small, auditable shell and PowerShell command subset. Unsupported or ambiguous syntax stays incomplete instead of being partially trusted. Compound commands, variables, non-whitelisted executables, file-target redirects, and in-place `sed` remain outside the certifiable surface. See [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md) for the exact grammar and platform evidence.
|
|
63
95
|
|
|
@@ -76,12 +108,19 @@ This project ports deterministic behavior from [`GreenLv/codex-context-guard`](h
|
|
|
76
108
|
|
|
77
109
|
They do not share runtime state, installers, caches, or release histories. Fixes are contributed to the repository that owns the affected runtime and are ported deliberately when the same behavior belongs in both products. See [`docs/UPSTREAM_BASE.md`](docs/UPSTREAM_BASE.md) and [`docs/PORTING_NOTES.md`](docs/PORTING_NOTES.md) for the exact reused and replaced boundaries.
|
|
78
110
|
|
|
111
|
+
## npm download history
|
|
112
|
+
|
|
113
|
+
|
|
114
|
+
|
|
115
|
+
The cumulative chart keeps the old and new npm package totals visibly separate, marks the 2026-08-29 rename, and combines them only for the project growth line. npm download counts measure registry requests; they are not counts of unique users or confirmed installations. The workflow runs daily and can also be triggered manually.
|
|
116
|
+
|
|
79
117
|
## Documentation
|
|
80
118
|
|
|
81
119
|
- [`CHANGELOG.md`](CHANGELOG.md) — versioned user-visible changes.
|
|
82
120
|
- [`docs/ARCHITECTURE.md`](docs/ARCHITECTURE.md) — ownership, durable state, and certification pipeline.
|
|
83
121
|
- [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md) — supported DSH versions and certifiable command subset.
|
|
84
122
|
- [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md) — deterministic, isolated, native, and public-package validation scopes.
|
|
123
|
+
- [`docs/distribution.md`](docs/distribution.md) — verified public distribution destinations and the rename note.
|
|
85
124
|
- [`docs/PRIVACY.md`](docs/PRIVACY.md) — stored facts, prohibited data, and failure behavior.
|
|
86
125
|
- [`docs/UPSTREAM_BASE.md`](docs/UPSTREAM_BASE.md) — semantic baseline and repository authority boundary.
|
|
87
126
|
- [`docs/PORTING_NOTES.md`](docs/PORTING_NOTES.md) — behavior retained from Codex and DSH-specific replacements.
|
|
@@ -90,6 +129,7 @@ They do not share runtime state, installers, caches, or release histories. Fixes
|
|
|
90
129
|
|
|
91
130
|
```sh
|
|
92
131
|
pnpm install --frozen-lockfile
|
|
132
|
+
pnpm run test:stats
|
|
93
133
|
pnpm run typecheck
|
|
94
134
|
pnpm test
|
|
95
135
|
pnpm run lint
|
|
@@ -97,4 +137,4 @@ pnpm run build
|
|
|
97
137
|
pnpm run pack:check
|
|
98
138
|
```
|
|
99
139
|
|
|
100
|
-
These commands validate
|
|
140
|
+
These commands validate a local source tree and package. CI, native-platform acceptance, npm publication, GitHub release identity, and runtime-profile installation remain separate evidence scopes.
|
package/README.zh-CN.md
CHANGED
|
@@ -4,12 +4,14 @@
|
|
|
4
4
|
|
|
5
5
|
面向 DeepSeek Harness(DSH)的任务合同与完成认证插件。它保存需求、禁止项、验收条件、后续修订和有界证据,只有当前成功证据与当前合同匹配时,任务才能获得完成认证。
|
|
6
6
|
|
|
7
|
+

|
|
8
|
+
|
|
7
9
|
## 快速开始
|
|
8
10
|
|
|
9
11
|
将已发布插件安装到 DSH Web profile:
|
|
10
12
|
|
|
11
13
|
```sh
|
|
12
|
-
dsh plugin --profile web add dsh-completion-guard@0.
|
|
14
|
+
dsh plugin --profile web add dsh-completion-guard@0.3.0
|
|
13
15
|
```
|
|
14
16
|
|
|
15
17
|
重启 DSH Web,打开一个会话并启用 Guard:
|
|
@@ -49,15 +51,45 @@ dsh plugin --profile web add dsh-completion-guard@0.2.1
|
|
|
49
51
|
- 只从 DSH 已持久化的工具调用与结果派生有界、脱敏的证据。
|
|
50
52
|
- 当合同明确指定时,同时匹配方法、操作、对象、surface 和结果状态。
|
|
51
53
|
- 在会话重建或恢复时重新验证证书,完整性丢失时 fail-closed。
|
|
52
|
-
-
|
|
54
|
+
- 启用期间,如果没有当前有效证书,就在 mutation 前阻止 Guard 自己守卫的模型工具 Goal 完成路径;可信进程内直接写 Goal/session 的旁路只检测为 integrity violation,不声称能普遍阻止。
|
|
53
55
|
|
|
54
56
|
## 状态与兼容性
|
|
55
57
|
|
|
56
|
-
0.
|
|
58
|
+
0.3.0 已发布到 [npm](https://www.npmjs.com/package/dsh-completion-guard) 和 [GitHub Release](https://github.com/GreenLv/dsh-completion-guard/releases/tag/v0.3.0)。
|
|
57
59
|
|
|
58
60
|
> 本项目于 2026-08-29 由 `dsh-context-guard` 更名为 `dsh-completion-guard`,以避免与无关的 DSH 插件(kpl0111/dsh-context-guard,工具结果剪裁)撞名。内部 Cordis bundle id 保持 `context-guard` 不变;原 npm 包 `dsh-context-guard` 将被 deprecate 并指向本包。目标环境为 DSH `0.1.1-rc.2`、Node.js `>=22`、pnpm `>=11`。
|
|
59
61
|
|
|
60
|
-
|
|
62
|
+
### 早期 v0.2.x 证据
|
|
63
|
+
|
|
64
|
+
0.2.1 版本测试共 138 项,其中 domain/core 105 项。它会在 shell 工具未提供 `workdir` 时使用会话 cwd 归因证据,支持字面量 `2>&1` 和只读检查命令,把过程动词映射为 run 证据,并在 checkpoint 绑定被拒时提供可执行提示。0.2.1 新增会话层捕获过滤,使澄清提问、元评论和纯推进语(`继续`、`continue`)不再成为合同条目;对重复恢复通知做内容去重;新增 `/context-guard clear`;并文档化在 Guard 关闭或阻塞时 goal 如何完成。macOS 真实 Web 会话已加载公开 profile 包并认证 `pnpm test` 结果。
|
|
65
|
+
|
|
66
|
+
Windows TEMP 读回现已确认 `b75868e9e73d29f50530ddaba15cfaef82e03ece` 的源码矩阵,以及 exact-source tarball → 隔离安装 → dump-config → Web 启动日志与清理链。HTTP 200 只出现在首轮 stdout,未持久化且复核时没有重跑,因此 HTTP 响应本身不能写成“独立复核已确认”。真实模型会话 smoke 仍未运行。
|
|
67
|
+
|
|
68
|
+
### v0.3.0
|
|
69
|
+
|
|
70
|
+
v0.3.0 增加语义 action/target 绑定、有状态动作的独立状态读回、typed boundary、digest-v3 证书、精确活动宿主身份,以及成对 optional Goal 集成。19 个测试文件在 macOS 通过 351 项并按能力跳过 1 项 Windows-only 测试,在原生 Windows 则 352 项全部通过且无跳过。随后,同一份 canonical 预发布 tarball 以逐字节一致方式在两个原生平台完成安装与读回;CI 还覆盖 Ubuntu、macOS、Windows 的 Node.js 22/24。带凭据的真实模型会话验证了有效 evidence binding 与持久化 typed-boundary/disarm 流程;一个刻意过宽的提示词保持 incomplete,且未被错误签发证书。[`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md) 分别记录源码、工件、CI、模型会话与发布证据边界。
|
|
71
|
+
|
|
72
|
+
该版本使用 [`manifests/action-manifest.v1.json`](manifests/action-manifest.v1.json)、[`manifests/git-command-manifest.v2.json`](manifests/git-command-manifest.v2.json) 与 [`manifests/supported-host.v1.json`](manifests/supported-host.v1.json)。Goal 集成要求精确 optional peers `@deepseek-ai/dsh-goal@0.1.1-rc.2` 和 `@deepseek-ai/dsh-tool-goal@0.1.1-rc.2` 同时存在。活动 DSH runtime/profile graph 未显式注入精确 `hostLockPackages`、platform 与 profile 身份时一律 fail-closed。由于 DSH 核心与 profile 插件使用不同 package graph,运行时不接受“向上找到的最近 lockfile”替代活动宿主身份;默认 bundle patch 也不会伪造这份锁。
|
|
73
|
+
|
|
74
|
+
把该版本安装到 profile 后,使用随包提供的 CLI 生成并回读活动身份。请把下列路径替换为实际 DSH 安装的绝对路径;dump 只是检查产物,不是配置来源:
|
|
75
|
+
|
|
76
|
+
```sh
|
|
77
|
+
DSH_RUNTIME_ROOT=/absolute/path/to/.dsh-runtime
|
|
78
|
+
DSH_PROFILE_ROOT=/absolute/path/to/.dsh/profiles/web
|
|
79
|
+
DSH_COMPOSED_DUMP=/tmp/dsh-web-composed.yml
|
|
80
|
+
GUARD_HOST_LOCK="$DSH_PROFILE_ROOT/node_modules/.bin/dsh-completion-guard-host-lock"
|
|
81
|
+
|
|
82
|
+
"$GUARD_HOST_LOCK" inspect --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
83
|
+
"$GUARD_HOST_LOCK" inject --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT"
|
|
84
|
+
dsh --profile web --dump-config > "$DSH_COMPOSED_DUMP"
|
|
85
|
+
"$GUARD_HOST_LOCK" verify-dump --runtime-root "$DSH_RUNTIME_ROOT" --profile-root "$DSH_PROFILE_ROOT" --dump-config "$DSH_COMPOSED_DUMP"
|
|
86
|
+
```
|
|
87
|
+
|
|
88
|
+
`inspect` 与 `inject` 会拒绝缺失、重复、多版本或漂移的关键包;`verify-dump` 再证明 DSH compose 出的有界 tuple 与活动 graph 读回一致。每次 DSH/profile/package 升级后都应重跑。流程未通过前,证书、依赖 Goal 的完成路径及受影响 action capability 均保持 unavailable。发布验收使用全新隔离 profile,未覆盖用户现有 DSH profile。
|
|
89
|
+
|
|
90
|
+
`context_guard_evidence` 只读:负责 target resolution、已持久 effect 验证和独立 state readback。install/apply/restart/publish 以及精确 Git commit/push/pull/fetch mutation 使用单独命名的 `context_guard_action`。resolution 本身不授予 mutation 权限:调用方必须给出精确的 pending 根用户 requirement 及修订、复述已持久 target digest,并逐字段匹配动作所需身份;prohibition 与 acceptance 条目绝不授权 mutation。v0.3 的 package/apply/publish 只接受精确版本授权,Git 授权必须给出 remote 与 canonical 完整 ref/refspec。这些检查在任何 executable、HTTP 请求或 restart intent 之前完成。审批/展示面会在执行前呈现 canonical target 和 command-manifest digest。
|
|
91
|
+
|
|
92
|
+
Publish target 只接受不含凭证、query、fragment、歧义路径或控制字符的 canonical HTTPS registry base;根合同、npm argv 与 registry readback 冻结同一值。Create/modify resolution 会在 effect 前冻结预期写入后的 digest;modify 还会先把源字节重新散列并与冻结的 pre-digest 比较,再按 pinned、唯一 UTF-8 replacement 语义推导 post-digest,因此 prestate 漂移或不同的实际文件字节都会 fail closed。
|
|
61
93
|
|
|
62
94
|
Context Guard 只识别一小组可审计的 shell 与 PowerShell 命令。无法支持或存在歧义的语法会保持 incomplete,而不会被部分信任。复合命令、变量、非白名单可执行文件、文件目标重定向和 in-place `sed` 仍不在可认证范围内。精确语法和平台证据见 [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md)。
|
|
63
95
|
|
|
@@ -76,12 +108,19 @@ Context Guard 负责完成认证;Goal、Todo、Compaction、continuation、权
|
|
|
76
108
|
|
|
77
109
|
两个项目不共享运行时状态、安装器、缓存或发布历史。修复应先进入拥有对应运行时的仓库;只有同一行为确实适用于两侧时,才显式迁移。具体复用与替换边界见 [`docs/UPSTREAM_BASE.md`](docs/UPSTREAM_BASE.md) 和 [`docs/PORTING_NOTES.md`](docs/PORTING_NOTES.md)。
|
|
78
110
|
|
|
111
|
+
## npm 下载量历史
|
|
112
|
+
|
|
113
|
+
|
|
114
|
+
|
|
115
|
+
该累计图分别展示新旧 npm 包的总量,以竖线标记 2026-08-29 更名,并且只在项目增长曲线中合并两者。npm 下载量统计的是 registry 请求次数,不等于独立用户数或已确认的真实安装人数。工作流每天运行,也支持手动触发。
|
|
116
|
+
|
|
79
117
|
## 文档
|
|
80
118
|
|
|
81
119
|
- [`CHANGELOG.zh-CN.md`](CHANGELOG.zh-CN.md) — 面向使用者的版本变化。
|
|
82
120
|
- [`docs/ARCHITECTURE.md`](docs/ARCHITECTURE.md) — 所有权、持久状态和认证管线。
|
|
83
121
|
- [`docs/COMPATIBILITY.md`](docs/COMPATIBILITY.md) — 支持的 DSH 版本和可认证命令子集。
|
|
84
122
|
- [`docs/LOCAL_ACCEPTANCE.md`](docs/LOCAL_ACCEPTANCE.md) — 确定性、隔离环境、原生平台和公开包验证范围。
|
|
123
|
+
- [`docs/distribution.md`](docs/distribution.md) — 已验证的公开分发去向与更名说明。
|
|
85
124
|
- [`docs/PRIVACY.md`](docs/PRIVACY.md) — 保存的事实、禁止数据和失败行为。
|
|
86
125
|
- [`docs/UPSTREAM_BASE.md`](docs/UPSTREAM_BASE.md) — 语义基线与仓库权威边界。
|
|
87
126
|
- [`docs/PORTING_NOTES.md`](docs/PORTING_NOTES.md) — 从 Codex 保留的行为和 DSH 专属替换。
|
|
@@ -90,6 +129,7 @@ Context Guard 负责完成认证;Goal、Todo、Compaction、continuation、权
|
|
|
90
129
|
|
|
91
130
|
```sh
|
|
92
131
|
pnpm install --frozen-lockfile
|
|
132
|
+
pnpm run test:stats
|
|
93
133
|
pnpm run typecheck
|
|
94
134
|
pnpm test
|
|
95
135
|
pnpm run lint
|
|
@@ -97,4 +137,4 @@ pnpm run build
|
|
|
97
137
|
pnpm run pack:check
|
|
98
138
|
```
|
|
99
139
|
|
|
100
|
-
|
|
140
|
+
这些命令验证本地源码树与包。CI、原生平台验收、npm 发布、GitHub Release 身份和真实 profile 安装仍是相互独立的证据范围。
|
|
@@ -0,0 +1,52 @@
|
|
|
1
|
+
#!/usr/bin/env node
|
|
2
|
+
|
|
3
|
+
import { readFileSync } from 'node:fs'
|
|
4
|
+
import { fileURLToPath } from 'node:url'
|
|
5
|
+
import { dirname, join } from 'node:path'
|
|
6
|
+
import {
|
|
7
|
+
injectActiveProfileHostLock,
|
|
8
|
+
resolveActiveProfileHostLock,
|
|
9
|
+
verifyComposedHostLockDump,
|
|
10
|
+
} from '../dist/domain/index.js'
|
|
11
|
+
|
|
12
|
+
function option(name) {
|
|
13
|
+
const index = process.argv.indexOf(name)
|
|
14
|
+
if (index < 0 || !process.argv[index + 1]) throw new Error(`missing ${name}`)
|
|
15
|
+
return process.argv[index + 1]
|
|
16
|
+
}
|
|
17
|
+
|
|
18
|
+
function summary(evaluation) {
|
|
19
|
+
return {
|
|
20
|
+
status: evaluation.status,
|
|
21
|
+
host_lock_digest: evaluation.digest,
|
|
22
|
+
goal_available: evaluation.goalAvailable,
|
|
23
|
+
platform: evaluation.platform,
|
|
24
|
+
profile: evaluation.profileKind,
|
|
25
|
+
capabilities: Object.fromEntries(Object.entries(evaluation.capabilities)
|
|
26
|
+
.map(([id, result]) => [id, result.status])),
|
|
27
|
+
package_count: evaluation.packages.filter((row) => row.version && row.integrity).length,
|
|
28
|
+
}
|
|
29
|
+
}
|
|
30
|
+
|
|
31
|
+
try {
|
|
32
|
+
const command = process.argv[2]
|
|
33
|
+
if (!['inspect', 'inject', 'verify-dump'].includes(command)) {
|
|
34
|
+
throw new Error('usage: dsh-completion-guard-host-lock <inspect|inject|verify-dump> --runtime-root PATH --profile-root PATH [--dump-config FILE]')
|
|
35
|
+
}
|
|
36
|
+
const packageRoot = dirname(dirname(fileURLToPath(import.meta.url)))
|
|
37
|
+
const packageManifest = JSON.parse(readFileSync(join(packageRoot, 'package.json'), 'utf8'))
|
|
38
|
+
const active = resolveActiveProfileHostLock(
|
|
39
|
+
option('--runtime-root'),
|
|
40
|
+
option('--profile-root'),
|
|
41
|
+
packageManifest.version,
|
|
42
|
+
)
|
|
43
|
+
if (command === 'inject') injectActiveProfileHostLock(active)
|
|
44
|
+
if (command === 'verify-dump') {
|
|
45
|
+
verifyComposedHostLockDump(readFileSync(option('--dump-config'), 'utf8'), active.evaluation)
|
|
46
|
+
}
|
|
47
|
+
process.stdout.write(`${JSON.stringify(summary(active.evaluation))}\n`)
|
|
48
|
+
} catch (error) {
|
|
49
|
+
const code = error && typeof error === 'object' && 'code' in error ? String(error.code) : 'host_lock_command_failed'
|
|
50
|
+
process.stderr.write(`${JSON.stringify({ status: 'unavailable', reason_code: code })}\n`)
|
|
51
|
+
process.exitCode = 1
|
|
52
|
+
}
|
package/dist/domain/index.d.ts
CHANGED
|
@@ -1,2 +1,2 @@
|
|
|
1
|
-
import { $ as
|
|
2
|
-
export { COMMAND_SURFACE_MANIFEST, CaptureScope, CheckpointResult, ClassifiedClause, ClauseSegment, CommandSurfaceManifest, CompletionDisposition, DEFAULT_RECOVERY_CHAR_BUDGET, DeriveConfig, DeriveResult, DeriveScope, DerivedEnvelope, EvidenceBinding, EvidenceFacetCoverage, EvidenceOutcome, GuardCheckpoint, GuardEvidence, GuardIntegrity, GuardItem, GuardItemKind, GuardItemStatus, GuardOperation, GuardProjection, ManifestIssue, OperationVerbEntry, ParsedShell, RecoveryOptions, RejectedBinding, ShellParseStatus, ToolCallInput, ToolResultInput, ToolSubject, TurnStoppingDecision, UserInteractionKind, VerificationContract, bindingSatisfies, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, createProjection, decideTurnStopping, deriveProjection, digestStrings, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, goalCompletionDenial, hasCurrentCertificate, isDeterministicCheck, isInformationalMessage, isRunExecutable, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, openItems, parsePwshCommand, parseShellCommand, recoveryDigest, renderRecoveryPacket, sanitizeClauseText, sanitizeUrl, segmentClauses, sha256, supersedeItem, validateManifest, withDurability };
|
|
1
|
+
import { $ as gitCommandMatchesTarget, $n as VerificationContract, $t as UserInteractionKind, A as hostLockRowsFromComposedDump, An as DerivedEnvelope, At as HOST_CAPABILITY_PACKAGE_GROUPS, B as GitCommandManifest, Bn as GuardEvidence, Bt as SUPPORTED_HOST_MANIFEST, C as CommandSurfaceManifest, Cn as qualifyBoundary, Cr as digestStrings, Ct as AuditedExecutable, D as ActiveProfileHostLock, Dn as DeriveConfig, Dr as sha256, Dt as ExecutableIdentity, E as validateManifest, En as DeferAuthorization, Er as sanitizeUrl, Et as EXPECTED_HOST_PACKAGES, F as resolveInstalledHostLock, Fn as ExpectedTransition, Ft as HostLockEvaluation, G as GitPrestateCheck, Gn as GuardOperation, Gt as evaluateHostLock, H as GitCommandRejected, Hn as GuardItem, Ht as bindLiveGoalCapability, I as verifyComposedHostLockDump, In as ExternalOperation, It as HostLockStatus, J as LinearCommitReadback, Jn as PersistenceAuthorization, Jt as AuthorityBlock, K as GitPrestateEnvelope, Kn as GuardProjection, Kt as evaluateToolSurfaceCapability, L as GIT_COMMAND_MANIFEST_IDS, Ln as GoalRef, Lt as HostPlatform, M as packageRowsFromActiveGraph, Mn as EvidenceOutcome, Mt as HostCapabilityId, N as packageRowsFromPnpmLock, Nn as EvidenceParseStatus, Nt as HostCapabilityRequest, O as HostProfileError, On as DeriveResult, Ot as ExecutableIdentityBinding, P as resolveActiveProfileHostLock, Pn as EvidenceRole, Pt as HostLockContext, Q as executeRevalidatedGitEffect, Qn as TargetValue, Qt as segmentAuthorityBlocks, R as GitAdapterAction, Rn as GuardBoundary, Rt as HostProfileKind, S as COMMAND_SURFACE_MANIFEST, Sn as isCurrentAcceptedBoundary, Sr as canonicalizePath, St as deriveProjection, T as OperationVerbEntry, Tn as BoundaryQualificationKind, Tr as sanitizeClauseText, Tt as DEFAULT_HOST_LOCK, U as GitEffectExecution, Un as GuardItemKind, Ut as evaluateExternalWaitCapability, V as GitCommandParseResult, Vn as GuardIntegrity, Vt as bindExecutableIdentity, W as GitEffectRunner, Wn as GuardItemStatus, Wt as evaluateHostCapability, X as commitTreeSnapshotDigest, Xn as TargetCaptureStatus, Xt as AuthorityKind, Y as commitIndexSnapshotDigest, Yn as TargetCaptureReasonCode, Yt as AuthorityBlockKind, Z as createGitPrestateEnvelope, Zn as TargetTuple, Zt as authorityCaptureCounts, _ as EvidenceFacetCoverage, _n as BoundaryRequest, _r as requestedTargetMatchesResolved, _t as extractTextContent, a as classifyCompletionClaim, an as ClassifiedClause, ar as ActionManifest, at as ParsedShell, b as evidenceMatchesItem, bn as availableBoundaryQualifications, br as validateActionManifest, bt as withDurability, c as isWholeTaskCompletionClaim, cn as captureItem, cr as SEMANTIC_ACTIONS, ct as isRunExecutable, d as DEFAULT_RECOVERY_CHAR_BUDGET, dn as extractMethod, dr as SUPPORTED_EVIDENCE_ADAPTERS, dt as goalCompletionDenial, en as classifyUserInteraction, er as WaitAuthorization, et as parseGitCommandManifest, f as RecoveryOptions, fn as extractOperation, fr as SemanticAction, ft as hasCurrentCertificate, g as renderRecoveryPacket, gn as BoundaryQualification, gr as requestedTargetAuthorizesMutation, gt as evidenceFromPersistedToolResult, h as recoveryDigest, hn as BoundaryEffectuation, hr as isStatefulAction, ht as ToolSubject, i as TurnStoppingDecision, in as CaptureScope, ir as ACTION_MANIFEST_VERSION, it as CanonicalCommandSurface, j as injectActiveProfileHostLock, jn as EvidenceBinding, jt as HostCapabilityEvaluation, k as hostLockContextFromComposedDump, kn as DeriveScope, kt as GOAL_HOST_PACKAGES, l as latestAssistantText, ln as classifyClause, lr as STATEFUL_ACTIONS, lt as parsePwshCommand, m as openItems, mn as segmentClauses, mr as actionCompatible, mt as ToolResultInput, n as AssistantOutcomeObservation, nn as RejectedBinding, nt as verifiedLinearCommitReadback, o as decideTurnBoundary, on as ClauseSegment, or as ActionSpec, ot as ShellParseStatus, p as closingHint, pn as isInformationalMessage, pr as StatefulAction, pt as ToolCallInput, q as GitTargetIdentity, qn as HostStatus, qt as currentContractDigest, r as CompletionDisposition, rn as certifyCheckpoint, rr as ACTION_MANIFEST, rt as CanonicalArgv, s as decideTurnStopping, sn as captureClause, sr as CERTIFICATE_VERSION, st as canonicalArgvFromCommand, t as supersedeItem, tn as CheckpointResult, tr as createProjection, tt as revalidateGitPrestate, u as observeAssistantOutcome, un as extractArtifactPaths, ur as STOP_PROTOCOL_VERSION, ut as parseShellCommand, v as bindingSatisfies, vn as GoalActivationState, vr as semanticActionFromCommand, vt as extractToolSubject, w as ManifestIssue, wn as BoundaryDisposition, wr as normalizeClause, wt as BASE_HOST_PACKAGES, x as isVerifyingCapability, xn as effectuateBoundary, xr as validateActionTarget, xt as PROTOCOL_V3_NOTICE, y as evidenceCoverage, yn as GoalBoundaryAccess, yr as semanticActionFromText, yt as isDeterministicCheck, z as GitCommandAccepted, zn as GuardCheckpoint, zt as HostToolSurface } from "../index-GvKLkTqV.js";
|
|
2
|
+
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, ActionManifest, ActionSpec, ActiveProfileHostLock, AssistantOutcomeObservation, AuditedExecutable, AuthorityBlock, AuthorityBlockKind, AuthorityKind, BASE_HOST_PACKAGES, BoundaryDisposition, BoundaryEffectuation, BoundaryQualification, BoundaryQualificationKind, BoundaryRequest, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, CanonicalArgv, CanonicalCommandSurface, CaptureScope, CheckpointResult, ClassifiedClause, ClauseSegment, CommandSurfaceManifest, CompletionDisposition, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, DeferAuthorization, DeriveConfig, DeriveResult, DeriveScope, DerivedEnvelope, EXPECTED_HOST_PACKAGES, EvidenceBinding, EvidenceFacetCoverage, EvidenceOutcome, EvidenceParseStatus, EvidenceRole, ExecutableIdentity, ExecutableIdentityBinding, ExpectedTransition, ExternalOperation, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, GitAdapterAction, GitCommandAccepted, GitCommandManifest, GitCommandParseResult, GitCommandRejected, GitEffectExecution, GitEffectRunner, GitPrestateCheck, GitPrestateEnvelope, GitTargetIdentity, GoalActivationState, GoalBoundaryAccess, GoalRef, GuardBoundary, GuardCheckpoint, GuardEvidence, GuardIntegrity, GuardItem, GuardItemKind, GuardItemStatus, GuardOperation, GuardProjection, HOST_CAPABILITY_PACKAGE_GROUPS, HostCapabilityEvaluation, HostCapabilityId, HostCapabilityRequest, HostLockContext, HostLockEvaluation, HostLockStatus, HostPlatform, HostProfileError, HostProfileKind, HostStatus, HostToolSurface, LinearCommitReadback, ManifestIssue, OperationVerbEntry, PROTOCOL_V3_NOTICE, ParsedShell, PersistenceAuthorization, RecoveryOptions, RejectedBinding, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, SUPPORTED_HOST_MANIFEST, SemanticAction, ShellParseStatus, StatefulAction, TargetCaptureReasonCode, TargetCaptureStatus, TargetTuple, TargetValue, ToolCallInput, ToolResultInput, ToolSubject, TurnStoppingDecision, UserInteractionKind, VerificationContract, WaitAuthorization, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindingSatisfies, canonicalArgvFromCommand, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, semanticActionFromCommand, semanticActionFromText, sha256, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|
package/dist/domain/index.js
CHANGED
|
@@ -1,3 +1,3 @@
|
|
|
1
|
-
import { A as
|
|
1
|
+
import { $ as classifyUserInteraction, A as extractToolSubject, At as STOP_PROTOCOL_VERSION, B as DEFAULT_HOST_LOCK, Bt as COMMAND_SURFACE_MANIFEST, C as latestAssistantText, D as supersedeItem, Dt as CERTIFICATE_VERSION, E as deriveProjection, Et as ACTION_MANIFEST_VERSION, F as parsePwshCommand, Ft as requestedTargetMatchesResolved, G as bindExecutableIdentity, Gt as sanitizeClauseText, H as GOAL_HOST_PACKAGES, Ht as canonicalizePath, I as parseShellCommand, It as semanticActionFromCommand, J as evaluateHostCapability, Jt as createProjection, K as bindLiveGoalCapability, Kt as sanitizeUrl, L as goalCompletionDenial, Lt as semanticActionFromText, M as withDurability, Mt as actionCompatible, N as canonicalArgvFromCommand, Nt as isStatefulAction, O as evidenceFromPersistedToolResult, Ot as SEMANTIC_ACTIONS, P as isRunExecutable, Pt as requestedTargetAuthorizesMutation, Q as segmentAuthorityBlocks, R as hasCurrentCertificate, Rt as validateActionManifest, S as isWholeTaskCompletionClaim, St as segmentClauses, T as PROTOCOL_V3_NOTICE, Tt as ACTION_MANIFEST, U as HOST_CAPABILITY_PACKAGE_GROUPS, Ut as digestStrings, V as EXPECTED_HOST_PACKAGES, Vt as validateManifest, W as SUPPORTED_HOST_MANIFEST, Wt as normalizeClause, X as evaluateToolSurfaceCapability, Y as evaluateHostLock, Z as authorityCaptureCounts, _ as revalidateGitPrestate, _t as classifyClause, a as packageRowsFromActiveGraph, at as DEFAULT_RECOVERY_CHAR_BUDGET, b as decideTurnBoundary, bt as extractOperation, c as resolveInstalledHostLock, ct as recoveryDigest, d as commitIndexSnapshotDigest, dt as evidenceCoverage, et as availableBoundaryQualifications, f as commitTreeSnapshotDigest, ft as evidenceMatchesItem, g as parseGitCommandManifest, gt as captureItem, h as gitCommandMatchesTarget, ht as captureClause, i as injectActiveProfileHostLock, it as certifyCheckpoint, j as isDeterministicCheck, jt as SUPPORTED_EVIDENCE_ADAPTERS, k as extractTextContent, kt as STATEFUL_ACTIONS, l as verifyComposedHostLockDump, lt as renderRecoveryPacket, m as executeRevalidatedGitEffect, mt as currentContractDigest, n as hostLockContextFromComposedDump, nt as isCurrentAcceptedBoundary, o as packageRowsFromPnpmLock, ot as closingHint, p as createGitPrestateEnvelope, pt as isVerifyingCapability, q as evaluateExternalWaitCapability, qt as sha256, r as hostLockRowsFromComposedDump, rt as qualifyBoundary, s as resolveActiveProfileHostLock, st as openItems, t as HostProfileError, tt as effectuateBoundary, u as GIT_COMMAND_MANIFEST_IDS, ut as bindingSatisfies, v as verifiedLinearCommitReadback, vt as extractArtifactPaths, w as observeAssistantOutcome, x as decideTurnStopping, xt as isInformationalMessage, y as classifyCompletionClaim, yt as extractMethod, z as BASE_HOST_PACKAGES, zt as validateActionTarget } from "../domain-CBvBQHTL.js";
|
|
2
2
|
|
|
3
|
-
export { COMMAND_SURFACE_MANIFEST, DEFAULT_RECOVERY_CHAR_BUDGET, bindingSatisfies, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, createProjection, decideTurnStopping, deriveProjection, digestStrings, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, goalCompletionDenial, hasCurrentCertificate, isDeterministicCheck, isInformationalMessage, isRunExecutable, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, openItems, parsePwshCommand, parseShellCommand, recoveryDigest, renderRecoveryPacket, sanitizeClauseText, sanitizeUrl, segmentClauses, sha256, supersedeItem, validateManifest, withDurability };
|
|
3
|
+
export { ACTION_MANIFEST, ACTION_MANIFEST_VERSION, BASE_HOST_PACKAGES, CERTIFICATE_VERSION, COMMAND_SURFACE_MANIFEST, DEFAULT_HOST_LOCK, DEFAULT_RECOVERY_CHAR_BUDGET, EXPECTED_HOST_PACKAGES, GIT_COMMAND_MANIFEST_IDS, GOAL_HOST_PACKAGES, HOST_CAPABILITY_PACKAGE_GROUPS, HostProfileError, PROTOCOL_V3_NOTICE, SEMANTIC_ACTIONS, STATEFUL_ACTIONS, STOP_PROTOCOL_VERSION, SUPPORTED_EVIDENCE_ADAPTERS, SUPPORTED_HOST_MANIFEST, actionCompatible, authorityCaptureCounts, availableBoundaryQualifications, bindExecutableIdentity, bindLiveGoalCapability, bindingSatisfies, canonicalArgvFromCommand, canonicalizePath, captureClause, captureItem, certifyCheckpoint, classifyClause, classifyCompletionClaim, classifyUserInteraction, closingHint, commitIndexSnapshotDigest, commitTreeSnapshotDigest, createGitPrestateEnvelope, createProjection, currentContractDigest, decideTurnBoundary, decideTurnStopping, deriveProjection, digestStrings, effectuateBoundary, evaluateExternalWaitCapability, evaluateHostCapability, evaluateHostLock, evaluateToolSurfaceCapability, evidenceCoverage, evidenceFromPersistedToolResult, evidenceMatchesItem, executeRevalidatedGitEffect, extractArtifactPaths, extractMethod, extractOperation, extractTextContent, extractToolSubject, gitCommandMatchesTarget, goalCompletionDenial, hasCurrentCertificate, hostLockContextFromComposedDump, hostLockRowsFromComposedDump, injectActiveProfileHostLock, isCurrentAcceptedBoundary, isDeterministicCheck, isInformationalMessage, isRunExecutable, isStatefulAction, isVerifyingCapability, isWholeTaskCompletionClaim, latestAssistantText, normalizeClause, observeAssistantOutcome, openItems, packageRowsFromActiveGraph, packageRowsFromPnpmLock, parseGitCommandManifest, parsePwshCommand, parseShellCommand, qualifyBoundary, recoveryDigest, renderRecoveryPacket, requestedTargetAuthorizesMutation, requestedTargetMatchesResolved, resolveActiveProfileHostLock, resolveInstalledHostLock, revalidateGitPrestate, sanitizeClauseText, sanitizeUrl, segmentAuthorityBlocks, segmentClauses, semanticActionFromCommand, semanticActionFromText, sha256, supersedeItem, validateActionManifest, validateActionTarget, validateManifest, verifiedLinearCommitReadback, verifyComposedHostLockDump, withDurability };
|