@xtandard/audit 0.0.0-stage → 0.1.0
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/LICENSE +21 -0
- package/README.md +384 -2
- package/bin/xtandard-audit.mjs +3 -0
- package/dist/basic-DU_nPrWV.mjs +176 -0
- package/dist/basic-DU_nPrWV.mjs.map +1 -0
- package/dist/basic-hcXnMF9X.cjs +199 -0
- package/dist/basic-hcXnMF9X.cjs.map +1 -0
- package/dist/canonical-BOgkrX9_.d.cts +17 -0
- package/dist/canonical-CL7gfwhb.d.mts +17 -0
- package/dist/chunk-D7D4PA-g.mjs +13 -0
- package/dist/cli.cjs +773 -0
- package/dist/cli.cjs.map +1 -0
- package/dist/cli.d.cts +46 -0
- package/dist/cli.d.mts +46 -0
- package/dist/cli.mjs +762 -0
- package/dist/cli.mjs.map +1 -0
- package/dist/context-BtR9k9Mt.d.mts +52 -0
- package/dist/context-CJM87uG8.d.cts +52 -0
- package/dist/context-shared-AgBWIRUQ.d.mts +29 -0
- package/dist/context-shared-CUq3cSpV.d.cts +29 -0
- package/dist/context-shared-CupikwQo.mjs +39 -0
- package/dist/context-shared-CupikwQo.mjs.map +1 -0
- package/dist/context-shared-X2ulHHSB.cjs +44 -0
- package/dist/context-shared-X2ulHHSB.cjs.map +1 -0
- package/dist/context.cjs +82 -0
- package/dist/context.cjs.map +1 -0
- package/dist/context.d.cts +2 -0
- package/dist/context.d.mts +2 -0
- package/dist/context.mjs +78 -0
- package/dist/context.mjs.map +1 -0
- package/dist/contract-BljSE-Hx.mjs +33 -0
- package/dist/contract-BljSE-Hx.mjs.map +1 -0
- package/dist/contract-BmwHIiMR.d.mts +150 -0
- package/dist/contract-CWJSYoJl.d.cts +150 -0
- package/dist/contract-Cht05WYQ.d.mts +159 -0
- package/dist/contract-CqYQzB6e.d.cts +49 -0
- package/dist/contract-DYvBNdnR.cjs +74 -0
- package/dist/contract-DYvBNdnR.cjs.map +1 -0
- package/dist/contract-DlTo4u2t.d.cts +30 -0
- package/dist/contract-DlTo4u2t.d.mts +30 -0
- package/dist/contract-DsVL5-gy.cjs +50 -0
- package/dist/contract-DsVL5-gy.cjs.map +1 -0
- package/dist/contract-isM9SjjQ.mjs +39 -0
- package/dist/contract-isM9SjjQ.mjs.map +1 -0
- package/dist/contract-pU3wGFmo.d.cts +159 -0
- package/dist/contract-yPNuFnVy.d.mts +49 -0
- package/dist/core-C0ceVOTk.d.cts +513 -0
- package/dist/core-CTr7dw0v.cjs +1725 -0
- package/dist/core-CTr7dw0v.cjs.map +1 -0
- package/dist/core-IdGEbYdM.mjs +1541 -0
- package/dist/core-IdGEbYdM.mjs.map +1 -0
- package/dist/core-KtEHRScZ.d.mts +513 -0
- package/dist/core.cjs +9 -0
- package/dist/core.d.cts +2 -0
- package/dist/core.d.mts +2 -0
- package/dist/core.mjs +2 -0
- package/dist/create-fetch-handler-1pXSEhGi.d.cts +311 -0
- package/dist/create-fetch-handler-BwQQ_IWf.mjs +2156 -0
- package/dist/create-fetch-handler-BwQQ_IWf.mjs.map +1 -0
- package/dist/create-fetch-handler-D8cTMVX9.cjs +2232 -0
- package/dist/create-fetch-handler-D8cTMVX9.cjs.map +1 -0
- package/dist/create-fetch-handler-zioPVS18.d.mts +311 -0
- package/dist/elysia-shared-C7geKqPP.mjs +55 -0
- package/dist/elysia-shared-C7geKqPP.mjs.map +1 -0
- package/dist/elysia-shared-DT4bfekR.d.cts +20 -0
- package/dist/elysia-shared-DXyAyGz_.cjs +66 -0
- package/dist/elysia-shared-DXyAyGz_.cjs.map +1 -0
- package/dist/elysia-shared-DoL5ab52.d.mts +20 -0
- package/dist/entry-auth-basic.cjs +5 -0
- package/dist/entry-auth-basic.d.cts +83 -0
- package/dist/entry-auth-basic.d.mts +83 -0
- package/dist/entry-auth-basic.mjs +2 -0
- package/dist/entry-auth-delegated.cjs +28 -0
- package/dist/entry-auth-delegated.cjs.map +1 -0
- package/dist/entry-auth-delegated.d.cts +36 -0
- package/dist/entry-auth-delegated.d.mts +36 -0
- package/dist/entry-auth-delegated.mjs +27 -0
- package/dist/entry-auth-delegated.mjs.map +1 -0
- package/dist/entry-auth-none.cjs +4 -0
- package/dist/entry-auth-none.d.cts +25 -0
- package/dist/entry-auth-none.d.mts +25 -0
- package/dist/entry-auth-none.mjs +2 -0
- package/dist/entry-authorization-delegated.cjs +28 -0
- package/dist/entry-authorization-delegated.cjs.map +1 -0
- package/dist/entry-authorization-delegated.d.cts +32 -0
- package/dist/entry-authorization-delegated.d.mts +32 -0
- package/dist/entry-authorization-delegated.mjs +27 -0
- package/dist/entry-authorization-delegated.mjs.map +1 -0
- package/dist/entry-authorization-none.cjs +3 -0
- package/dist/entry-authorization-none.d.cts +18 -0
- package/dist/entry-authorization-none.d.mts +18 -0
- package/dist/entry-authorization-none.mjs +2 -0
- package/dist/entry-authorization-roles.cjs +8 -0
- package/dist/entry-authorization-roles.d.cts +64 -0
- package/dist/entry-authorization-roles.d.mts +64 -0
- package/dist/entry-authorization-roles.mjs +3 -0
- package/dist/entry-bun.cjs +55 -0
- package/dist/entry-bun.cjs.map +1 -0
- package/dist/entry-bun.d.cts +29 -0
- package/dist/entry-bun.d.mts +29 -0
- package/dist/entry-bun.mjs +52 -0
- package/dist/entry-bun.mjs.map +1 -0
- package/dist/entry-drizzle-audit.cjs +191 -0
- package/dist/entry-drizzle-audit.cjs.map +1 -0
- package/dist/entry-drizzle-audit.d.cts +118 -0
- package/dist/entry-drizzle-audit.d.mts +118 -0
- package/dist/entry-drizzle-audit.mjs +186 -0
- package/dist/entry-drizzle-audit.mjs.map +1 -0
- package/dist/entry-drizzle-mysql.cjs +75 -0
- package/dist/entry-drizzle-mysql.cjs.map +1 -0
- package/dist/entry-drizzle-mysql.d.cts +42 -0
- package/dist/entry-drizzle-mysql.d.mts +42 -0
- package/dist/entry-drizzle-mysql.mjs +71 -0
- package/dist/entry-drizzle-mysql.mjs.map +1 -0
- package/dist/entry-drizzle-pg.cjs +82 -0
- package/dist/entry-drizzle-pg.cjs.map +1 -0
- package/dist/entry-drizzle-pg.d.cts +48 -0
- package/dist/entry-drizzle-pg.d.mts +48 -0
- package/dist/entry-drizzle-pg.mjs +78 -0
- package/dist/entry-drizzle-pg.mjs.map +1 -0
- package/dist/entry-drizzle-sqlite.cjs +71 -0
- package/dist/entry-drizzle-sqlite.cjs.map +1 -0
- package/dist/entry-drizzle-sqlite.d.cts +37 -0
- package/dist/entry-drizzle-sqlite.d.mts +37 -0
- package/dist/entry-drizzle-sqlite.mjs +67 -0
- package/dist/entry-drizzle-sqlite.mjs.map +1 -0
- package/dist/entry-elysia.cjs +112 -0
- package/dist/entry-elysia.cjs.map +1 -0
- package/dist/entry-elysia.d.cts +710 -0
- package/dist/entry-elysia.d.mts +710 -0
- package/dist/entry-elysia.mjs +109 -0
- package/dist/entry-elysia.mjs.map +1 -0
- package/dist/entry-elysia2.cjs +101 -0
- package/dist/entry-elysia2.cjs.map +1 -0
- package/dist/entry-elysia2.d.cts +905 -0
- package/dist/entry-elysia2.d.mts +905 -0
- package/dist/entry-elysia2.mjs +98 -0
- package/dist/entry-elysia2.mjs.map +1 -0
- package/dist/entry-express.cjs +90 -0
- package/dist/entry-express.cjs.map +1 -0
- package/dist/entry-express.d.cts +24 -0
- package/dist/entry-express.d.mts +24 -0
- package/dist/entry-express.mjs +88 -0
- package/dist/entry-express.mjs.map +1 -0
- package/dist/entry-hono.cjs +36 -0
- package/dist/entry-hono.cjs.map +1 -0
- package/dist/entry-hono.d.cts +24 -0
- package/dist/entry-hono.d.mts +24 -0
- package/dist/entry-hono.mjs +34 -0
- package/dist/entry-hono.mjs.map +1 -0
- package/dist/entry-hooks-log.cjs +22 -0
- package/dist/entry-hooks-log.cjs.map +1 -0
- package/dist/entry-hooks-log.d.cts +23 -0
- package/dist/entry-hooks-log.d.mts +23 -0
- package/dist/entry-hooks-log.mjs +21 -0
- package/dist/entry-hooks-log.mjs.map +1 -0
- package/dist/entry-sinks-console.cjs +43 -0
- package/dist/entry-sinks-console.cjs.map +1 -0
- package/dist/entry-sinks-console.d.cts +26 -0
- package/dist/entry-sinks-console.d.mts +26 -0
- package/dist/entry-sinks-console.mjs +41 -0
- package/dist/entry-sinks-console.mjs.map +1 -0
- package/dist/entry-sinks-datadog.cjs +97 -0
- package/dist/entry-sinks-datadog.cjs.map +1 -0
- package/dist/entry-sinks-datadog.d.cts +66 -0
- package/dist/entry-sinks-datadog.d.mts +66 -0
- package/dist/entry-sinks-datadog.mjs +91 -0
- package/dist/entry-sinks-datadog.mjs.map +1 -0
- package/dist/entry-sinks-file.cjs +100 -0
- package/dist/entry-sinks-file.cjs.map +1 -0
- package/dist/entry-sinks-file.d.cts +70 -0
- package/dist/entry-sinks-file.d.mts +70 -0
- package/dist/entry-sinks-file.mjs +97 -0
- package/dist/entry-sinks-file.mjs.map +1 -0
- package/dist/entry-sinks-http.cjs +63 -0
- package/dist/entry-sinks-http.cjs.map +1 -0
- package/dist/entry-sinks-http.d.cts +55 -0
- package/dist/entry-sinks-http.d.mts +55 -0
- package/dist/entry-sinks-http.mjs +60 -0
- package/dist/entry-sinks-http.mjs.map +1 -0
- package/dist/entry-sinks-s3.cjs +115 -0
- package/dist/entry-sinks-s3.cjs.map +1 -0
- package/dist/entry-sinks-s3.d.cts +79 -0
- package/dist/entry-sinks-s3.d.mts +79 -0
- package/dist/entry-sinks-s3.mjs +112 -0
- package/dist/entry-sinks-s3.mjs.map +1 -0
- package/dist/entry-sinks-splunk.cjs +80 -0
- package/dist/entry-sinks-splunk.cjs.map +1 -0
- package/dist/entry-sinks-splunk.d.cts +58 -0
- package/dist/entry-sinks-splunk.d.mts +58 -0
- package/dist/entry-sinks-splunk.mjs +77 -0
- package/dist/entry-sinks-splunk.mjs.map +1 -0
- package/dist/entry-sinks-webhook.cjs +130 -0
- package/dist/entry-sinks-webhook.cjs.map +1 -0
- package/dist/entry-sinks-webhook.d.cts +69 -0
- package/dist/entry-sinks-webhook.d.mts +69 -0
- package/dist/entry-sinks-webhook.mjs +125 -0
- package/dist/entry-sinks-webhook.mjs.map +1 -0
- package/dist/entry-sinks-xtandard-webhooks.cjs +64 -0
- package/dist/entry-sinks-xtandard-webhooks.cjs.map +1 -0
- package/dist/entry-sinks-xtandard-webhooks.d.cts +64 -0
- package/dist/entry-sinks-xtandard-webhooks.d.mts +64 -0
- package/dist/entry-sinks-xtandard-webhooks.mjs +63 -0
- package/dist/entry-sinks-xtandard-webhooks.mjs.map +1 -0
- package/dist/entry-storage-cloudflare-kv.cjs +47 -0
- package/dist/entry-storage-cloudflare-kv.cjs.map +1 -0
- package/dist/entry-storage-cloudflare-kv.d.cts +42 -0
- package/dist/entry-storage-cloudflare-kv.d.mts +42 -0
- package/dist/entry-storage-cloudflare-kv.mjs +46 -0
- package/dist/entry-storage-cloudflare-kv.mjs.map +1 -0
- package/dist/entry-storage-drizzle.cjs +228 -0
- package/dist/entry-storage-drizzle.cjs.map +1 -0
- package/dist/entry-storage-drizzle.d.cts +43 -0
- package/dist/entry-storage-drizzle.d.mts +43 -0
- package/dist/entry-storage-drizzle.mjs +227 -0
- package/dist/entry-storage-drizzle.mjs.map +1 -0
- package/dist/entry-storage-file.cjs +175 -0
- package/dist/entry-storage-file.cjs.map +1 -0
- package/dist/entry-storage-file.d.cts +41 -0
- package/dist/entry-storage-file.d.mts +41 -0
- package/dist/entry-storage-file.mjs +171 -0
- package/dist/entry-storage-file.mjs.map +1 -0
- package/dist/entry-storage-libsql.cjs +133 -0
- package/dist/entry-storage-libsql.cjs.map +1 -0
- package/dist/entry-storage-libsql.d.cts +60 -0
- package/dist/entry-storage-libsql.d.mts +60 -0
- package/dist/entry-storage-libsql.mjs +132 -0
- package/dist/entry-storage-libsql.mjs.map +1 -0
- package/dist/entry-storage-memory.cjs +3 -0
- package/dist/entry-storage-memory.d.cts +2 -0
- package/dist/entry-storage-memory.d.mts +2 -0
- package/dist/entry-storage-memory.mjs +2 -0
- package/dist/entry-storage-mongodb.cjs +306 -0
- package/dist/entry-storage-mongodb.cjs.map +1 -0
- package/dist/entry-storage-mongodb.d.cts +65 -0
- package/dist/entry-storage-mongodb.d.mts +65 -0
- package/dist/entry-storage-mongodb.mjs +304 -0
- package/dist/entry-storage-mongodb.mjs.map +1 -0
- package/dist/entry-storage-postgres.cjs +261 -0
- package/dist/entry-storage-postgres.cjs.map +1 -0
- package/dist/entry-storage-postgres.d.cts +66 -0
- package/dist/entry-storage-postgres.d.mts +66 -0
- package/dist/entry-storage-postgres.mjs +260 -0
- package/dist/entry-storage-postgres.mjs.map +1 -0
- package/dist/entry-storage-redis.cjs +223 -0
- package/dist/entry-storage-redis.cjs.map +1 -0
- package/dist/entry-storage-redis.d.cts +77 -0
- package/dist/entry-storage-redis.d.mts +77 -0
- package/dist/entry-storage-redis.mjs +221 -0
- package/dist/entry-storage-redis.mjs.map +1 -0
- package/dist/entry-storage-sqlite.cjs +85 -0
- package/dist/entry-storage-sqlite.cjs.map +1 -0
- package/dist/entry-storage-sqlite.d.cts +40 -0
- package/dist/entry-storage-sqlite.d.mts +40 -0
- package/dist/entry-storage-sqlite.mjs +84 -0
- package/dist/entry-storage-sqlite.mjs.map +1 -0
- package/dist/entry-storage-unstorage.cjs +57 -0
- package/dist/entry-storage-unstorage.cjs.map +1 -0
- package/dist/entry-storage-unstorage.d.cts +29 -0
- package/dist/entry-storage-unstorage.d.mts +29 -0
- package/dist/entry-storage-unstorage.mjs +56 -0
- package/dist/entry-storage-unstorage.mjs.map +1 -0
- package/dist/export-B9S-JeYl.mjs +239 -0
- package/dist/export-B9S-JeYl.mjs.map +1 -0
- package/dist/export-BZq0KCCn.d.mts +70 -0
- package/dist/export-DYfMd-ep.cjs +280 -0
- package/dist/export-DYfMd-ep.cjs.map +1 -0
- package/dist/export-Dh8T8I1p.d.cts +70 -0
- package/dist/index.cjs +279 -0
- package/dist/index.cjs.map +1 -0
- package/dist/index.d.cts +286 -0
- package/dist/index.d.mts +284 -0
- package/dist/index.mjs +177 -0
- package/dist/index.mjs.map +1 -0
- package/dist/integrity-BHhjTBNk.cjs +614 -0
- package/dist/integrity-BHhjTBNk.cjs.map +1 -0
- package/dist/integrity-kfY2DNAi.mjs +483 -0
- package/dist/integrity-kfY2DNAi.mjs.map +1 -0
- package/dist/memory-CfykUo9W.cjs +155 -0
- package/dist/memory-CfykUo9W.cjs.map +1 -0
- package/dist/memory-DrR-Tlbf.d.mts +28 -0
- package/dist/memory-GG2Nba1D.mjs +150 -0
- package/dist/memory-GG2Nba1D.mjs.map +1 -0
- package/dist/memory-HpFdlMR_.d.cts +28 -0
- package/dist/none-Be7r6kHH.cjs +33 -0
- package/dist/none-Be7r6kHH.cjs.map +1 -0
- package/dist/none-CGmIIbI8.cjs +49 -0
- package/dist/none-CGmIIbI8.cjs.map +1 -0
- package/dist/none-CkV5mZsB.mjs +33 -0
- package/dist/none-CkV5mZsB.mjs.map +1 -0
- package/dist/none-DBeBeU0Z.mjs +23 -0
- package/dist/none-DBeBeU0Z.mjs.map +1 -0
- package/dist/query-ChGGtlA7.cjs +243 -0
- package/dist/query-ChGGtlA7.cjs.map +1 -0
- package/dist/query-LvZbyi37.mjs +172 -0
- package/dist/query-LvZbyi37.mjs.map +1 -0
- package/dist/react.css +1 -0
- package/dist/react.js +31935 -0
- package/dist/recorder-B3dG3jbd.d.mts +64 -0
- package/dist/recorder-CGY7HK29.d.cts +64 -0
- package/dist/roles-BARtYLSX.cjs +112 -0
- package/dist/roles-BARtYLSX.cjs.map +1 -0
- package/dist/roles-D7Pg89IJ.mjs +83 -0
- package/dist/roles-D7Pg89IJ.mjs.map +1 -0
- package/dist/schema-DmU7Wp0F.d.cts +251 -0
- package/dist/schema-DmU7Wp0F.d.mts +251 -0
- package/dist/schema.cjs +20 -0
- package/dist/schema.cjs.map +1 -0
- package/dist/schema.d.cts +2 -0
- package/dist/schema.d.mts +2 -0
- package/dist/schema.mjs +17 -0
- package/dist/schema.mjs.map +1 -0
- package/dist/shared-CJOyJKqT.d.mts +20 -0
- package/dist/shared-DSDY-V0n.mjs +100 -0
- package/dist/shared-DSDY-V0n.mjs.map +1 -0
- package/dist/shared-EANCdRqn.d.cts +20 -0
- package/dist/shared-OOAq-U4S.cjs +141 -0
- package/dist/shared-OOAq-U4S.cjs.map +1 -0
- package/dist/sql-B7b6HzGy.cjs +280 -0
- package/dist/sql-B7b6HzGy.cjs.map +1 -0
- package/dist/sql-COjPyn3F.mjs +209 -0
- package/dist/sql-COjPyn3F.mjs.map +1 -0
- package/dist/sqlite-event-log-BnoG8eos.cjs +184 -0
- package/dist/sqlite-event-log-BnoG8eos.cjs.map +1 -0
- package/dist/sqlite-event-log-nXmS2DS_.mjs +179 -0
- package/dist/sqlite-event-log-nXmS2DS_.mjs.map +1 -0
- package/dist/streams-CRuxOYcb.d.cts +124 -0
- package/dist/streams-DU0_gvI8.d.mts +124 -0
- package/dist/table-BcarDd10.d.cts +48 -0
- package/dist/table-BcarDd10.d.mts +48 -0
- package/dist/testing.cjs +189 -0
- package/dist/testing.cjs.map +1 -0
- package/dist/testing.d.cts +103 -0
- package/dist/testing.d.mts +103 -0
- package/dist/testing.mjs +185 -0
- package/dist/testing.mjs.map +1 -0
- package/dist/types-elysia2/adapters/bun.d.ts +47 -0
- package/dist/types-elysia2/adapters/context-shared.d.ts +40 -0
- package/dist/types-elysia2/adapters/elysia-shared.d.ts +36 -0
- package/dist/types-elysia2/adapters/elysia2.d.ts +588 -0
- package/dist/types-elysia2/auth/contract.d.ts +26 -0
- package/dist/types-elysia2/authorization/contract.d.ts +54 -0
- package/dist/types-elysia2/canonical.d.ts +25 -0
- package/dist/types-elysia2/context.d.ts +61 -0
- package/dist/types-elysia2/core.d.ts +232 -0
- package/dist/types-elysia2/duration.d.ts +26 -0
- package/dist/types-elysia2/entry-elysia2.d.ts +10 -0
- package/dist/types-elysia2/event-log.d.ts +33 -0
- package/dist/types-elysia2/export.d.ts +77 -0
- package/dist/types-elysia2/hooks/contract.d.ts +177 -0
- package/dist/types-elysia2/id.d.ts +27 -0
- package/dist/types-elysia2/integrity.d.ts +193 -0
- package/dist/types-elysia2/keys.d.ts +91 -0
- package/dist/types-elysia2/portal.d.ts +137 -0
- package/dist/types-elysia2/query.d.ts +88 -0
- package/dist/types-elysia2/schema.d.ts +247 -0
- package/dist/types-elysia2/server/base-path.d.ts +15 -0
- package/dist/types-elysia2/server/cors.d.ts +36 -0
- package/dist/types-elysia2/server/create-fetch-handler.d.ts +140 -0
- package/dist/types-elysia2/server/openapi.d.ts +25 -0
- package/dist/types-elysia2/server/render-index-html.d.ts +18 -0
- package/dist/types-elysia2/server/routes.d.ts +83 -0
- package/dist/types-elysia2/server/static-assets.d.ts +13 -0
- package/dist/types-elysia2/standard-schema.d.ts +100 -0
- package/dist/types-elysia2/storage/contract.d.ts +106 -0
- package/dist/types-elysia2/streams.d.ts +134 -0
- package/dist/types-elysia2/transforms.d.ts +56 -0
- package/dist/types-elysia2/validation.d.ts +48 -0
- package/dist/types-react/canonical.d.ts +25 -0
- package/dist/types-react/context.d.ts +61 -0
- package/dist/types-react/core.d.ts +232 -0
- package/dist/types-react/duration.d.ts +26 -0
- package/dist/types-react/event-log.d.ts +33 -0
- package/dist/types-react/hooks/contract.d.ts +177 -0
- package/dist/types-react/id.d.ts +27 -0
- package/dist/types-react/integrity.d.ts +193 -0
- package/dist/types-react/keys.d.ts +91 -0
- package/dist/types-react/query.d.ts +88 -0
- package/dist/types-react/react.d.ts +114 -0
- package/dist/types-react/schema.d.ts +247 -0
- package/dist/types-react/standard-schema.d.ts +100 -0
- package/dist/types-react/storage/contract.d.ts +106 -0
- package/dist/types-react/streams.d.ts +134 -0
- package/dist/types-react/transforms.d.ts +56 -0
- package/dist/types-react/ui/App.d.ts +36 -0
- package/dist/types-react/ui/api.d.ts +61 -0
- package/dist/types-react/ui/components/ActionFilter.d.ts +17 -0
- package/dist/types-react/ui/components/ExportMenu.d.ts +13 -0
- package/dist/types-react/ui/components/JsonCodeEditor.d.ts +12 -0
- package/dist/types-react/ui/components/ThemeToggle.d.ts +2 -0
- package/dist/types-react/ui/components/Toast.d.ts +16 -0
- package/dist/types-react/ui/components/audit-bits.d.ts +91 -0
- package/dist/types-react/ui/components/integrity-bits.d.ts +19 -0
- package/dist/types-react/ui/components/primitives.d.ts +50 -0
- package/dist/types-react/ui/components/ui-bits.d.ts +22 -0
- package/dist/types-react/ui/lib/filters.d.ts +70 -0
- package/dist/types-react/ui/lib/format.d.ts +82 -0
- package/dist/types-react/ui/lib/nav-guard.d.ts +20 -0
- package/dist/types-react/ui/lib/portal-container.d.ts +24 -0
- package/dist/types-react/ui/lib/utils.d.ts +3 -0
- package/dist/types-react/ui/theme.d.ts +40 -0
- package/dist/types-react/ui/types.d.ts +67 -0
- package/dist/types-react/ui/views/ActionsView.d.ts +10 -0
- package/dist/types-react/ui/views/EventDrawer.d.ts +15 -0
- package/dist/types-react/ui/views/EventsView.d.ts +10 -0
- package/dist/types-react/ui/views/IntegrityView.d.ts +10 -0
- package/dist/types-react/ui/views/OverviewView.d.ts +9 -0
- package/dist/types-react/ui/views/StreamsView.d.ts +10 -0
- package/dist/types-react/ui/views/TenantsView.d.ts +6 -0
- package/dist/types-react/validation.d.ts +48 -0
- package/dist/ui/assets/favicon-BSj8MPnj.svg +11 -0
- package/dist/ui/assets/index-Cd-mcIwC.css +1 -0
- package/dist/ui/assets/index-DUAgpiot.js +244 -0
- package/dist/ui/index.html +15 -0
- package/dist/validation-DFrLESZD.mjs +150 -0
- package/dist/validation-DFrLESZD.mjs.map +1 -0
- package/dist/validation-lb0YXrxx.cjs +235 -0
- package/dist/validation-lb0YXrxx.cjs.map +1 -0
- package/dist/verify.cjs +14 -0
- package/dist/verify.d.cts +5 -0
- package/dist/verify.d.mts +5 -0
- package/dist/verify.mjs +3 -0
- package/package.json +610 -4
package/LICENSE
ADDED
|
@@ -0,0 +1,21 @@
|
|
|
1
|
+
MIT License
|
|
2
|
+
|
|
3
|
+
Copyright (c) 2026 Santiago Montoya
|
|
4
|
+
|
|
5
|
+
Permission is hereby granted, free of charge, to any person obtaining a copy
|
|
6
|
+
of this software and associated documentation files (the "Software"), to deal
|
|
7
|
+
in the Software without restriction, including without limitation the rights
|
|
8
|
+
to use, copy, modify, merge, publish, distribute, sublicense, and/or sell
|
|
9
|
+
copies of the Software, and to permit persons to whom the Software is
|
|
10
|
+
furnished to do so, subject to the following conditions:
|
|
11
|
+
|
|
12
|
+
The above copyright notice and this permission notice shall be included in all
|
|
13
|
+
copies or substantial portions of the Software.
|
|
14
|
+
|
|
15
|
+
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR
|
|
16
|
+
IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY,
|
|
17
|
+
FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE
|
|
18
|
+
AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER
|
|
19
|
+
LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM,
|
|
20
|
+
OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE
|
|
21
|
+
SOFTWARE.
|
package/README.md
CHANGED
|
@@ -1,3 +1,385 @@
|
|
|
1
|
-
|
|
1
|
+
<div align="center">
|
|
2
2
|
|
|
3
|
-
|
|
3
|
+
<picture>
|
|
4
|
+
<source media="(prefers-color-scheme: dark)" srcset="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/lockup-horizontal-dark.png" />
|
|
5
|
+
<img src="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/lockup-horizontal-light.png" alt="@xtandard/audit" height="64" />
|
|
6
|
+
</picture>
|
|
7
|
+
|
|
8
|
+
# @xtandard/audit
|
|
9
|
+
|
|
10
|
+
**Self-hosted, embeddable, tamper-evident audit-log control plane for B2B SaaS.**
|
|
11
|
+
|
|
12
|
+
Record typed audit events from your app, store them in the database you already run, and give every customer a verifiable, browsable, exportable log of what happened in their organization — no per-event SaaS pricing, no separate service to operate.
|
|
13
|
+
|
|
14
|
+
[](https://github.com/xantiagoma/xtandard-audit/actions/workflows/ci.yml)
|
|
15
|
+
[](https://www.npmjs.com/package/@xtandard/audit)
|
|
16
|
+
[](./LICENSE)
|
|
17
|
+
[](https://me.xantiagoma.com/xtandard-audit/)
|
|
18
|
+
|
|
19
|
+
**Documentation: [me.xantiagoma.com/xtandard-audit](https://me.xantiagoma.com/xtandard-audit/)** — guides and the full API reference.
|
|
20
|
+
|
|
21
|
+
<picture>
|
|
22
|
+
<source media="(prefers-color-scheme: dark)" srcset="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/ui-events-dark.png" />
|
|
23
|
+
<img src="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/ui-events-light.png" alt="Events explorer: every tenant's log, filtered and paginated" width="800" />
|
|
24
|
+
</picture>
|
|
25
|
+
|
|
26
|
+
</div>
|
|
27
|
+
|
|
28
|
+
> `record()` is one call in your request handler. Every tenant gets its own hash chain with signed checkpoints, so your customers — and their auditors — can **verify** that nobody, including you, altered or deleted their history.
|
|
29
|
+
|
|
30
|
+
## Contents
|
|
31
|
+
|
|
32
|
+
- [Why another audit-log tool?](#why-another-audit-log-tool)
|
|
33
|
+
- [How it works](#how-it-works)
|
|
34
|
+
- [Quickstart](#quickstart)
|
|
35
|
+
- [Record your first events](#record-your-first-events)
|
|
36
|
+
- [Typed actions](#typed-actions)
|
|
37
|
+
- [Querying](#querying)
|
|
38
|
+
- [Tamper evidence](#tamper-evidence)
|
|
39
|
+
- [The customer portal](#the-customer-portal)
|
|
40
|
+
- [Exports and streaming](#exports-and-streaming)
|
|
41
|
+
- [Storage backends](#storage-backends)
|
|
42
|
+
- [Subpath exports](#subpath-exports)
|
|
43
|
+
- [Examples](#examples)
|
|
44
|
+
- [Screenshots](#screenshots)
|
|
45
|
+
- [CLI](#cli)
|
|
46
|
+
- [Documentation](#documentation)
|
|
47
|
+
- [Project status](#project-status)
|
|
48
|
+
- [The xtandard ecosystem](#the-xtandard-ecosystem)
|
|
49
|
+
|
|
50
|
+
## Why another audit-log tool?
|
|
51
|
+
|
|
52
|
+
Every B2B SaaS ends up needing an audit log its customers can see — it is on every enterprise security questionnaire. The options today:
|
|
53
|
+
|
|
54
|
+
- **WorkOS Audit Logs / Pangea** are excellent — and SaaS, priced per event, with your customers' activity data in someone else's cloud.
|
|
55
|
+
- **Retraced** (Apache-2.0) is a standalone service with Postgres, Elasticsearch and NSQ to operate, and has had no release since 2024.
|
|
56
|
+
- **ORM plugins** (paper_trail, audited, drizzle-audit, …) record row diffs, not tenant-facing business events, and have no viewer, export, streaming or verification.
|
|
57
|
+
|
|
58
|
+
`@xtandard/audit` is the 20% everyone needs, as a library: a typed event model, pluggable storage, keyset search, per-tenant hash chains with signed checkpoints and an offline verifier, a customer-facing portal you embed in your product, CSV/JSON exports, SIEM streaming, retention and GDPR erasure that keeps the chain verifiable. The full market survey is in [docs/research/landscape.md](docs/research/landscape.md).
|
|
59
|
+
|
|
60
|
+
Part of [the xtandard ecosystem](#the-xtandard-ecosystem): its closest siblings, [`@xtandard/webhooks`](https://github.com/xantiagoma/xtandard-webhooks) and [`@xtandard/flags`](https://github.com/xantiagoma/xtandard-flags), share the same architecture and design system.
|
|
61
|
+
|
|
62
|
+
## How it works
|
|
63
|
+
|
|
64
|
+
```mermaid
|
|
65
|
+
flowchart LR
|
|
66
|
+
subgraph host["your app process"]
|
|
67
|
+
A[app code] -- "record()" --> C[core]
|
|
68
|
+
UI[admin UI / customer portal] --> C
|
|
69
|
+
S[stream runner] --> C
|
|
70
|
+
end
|
|
71
|
+
C <--> DB[(your database)]
|
|
72
|
+
S -- "batches + signed checkpoints" --> SIEM[Datadog / Splunk / S3 / webhooks]
|
|
73
|
+
P[customer / auditor] -- "verify bundle" --> V[zero-dep verifier]
|
|
74
|
+
```
|
|
75
|
+
|
|
76
|
+
- **Record plane** — `record()` validates (typed per action), applies transforms (redact/mask/hash), chains the event into its tenant's hash chain and appends it. Synchronous-commit: it throws rather than silently dropping. A buffered `createRecorder()` exists for fire-and-forget hot paths, with retries, a fallback sink and backpressure.
|
|
77
|
+
- **Control plane** — query, export, verify, checkpoints, retention, erasure, the action catalog. Hook-guarded, authorized, and self-audited (exports and erasures land in the tenant's own log).
|
|
78
|
+
- **Streams** read the log by per-tenant sequence cursors — nothing sits on the record path, nothing is lost when a SIEM is down.
|
|
79
|
+
|
|
80
|
+
## Quickstart
|
|
81
|
+
|
|
82
|
+
<details>
|
|
83
|
+
<summary><b>Standalone (Docker)</b></summary>
|
|
84
|
+
|
|
85
|
+
```sh
|
|
86
|
+
docker run -p 3000:3000 -e STORAGE_DRIVER=memory ghcr.io/xantiagoma/xtandard-audit
|
|
87
|
+
# open http://localhost:3000
|
|
88
|
+
```
|
|
89
|
+
|
|
90
|
+
</details>
|
|
91
|
+
|
|
92
|
+
<details>
|
|
93
|
+
<summary><b>CLI (npx / bunx)</b></summary>
|
|
94
|
+
|
|
95
|
+
```sh
|
|
96
|
+
bunx @xtandard/audit serve # STORAGE_DRIVER=file by default → ./.audit
|
|
97
|
+
```
|
|
98
|
+
|
|
99
|
+
</details>
|
|
100
|
+
|
|
101
|
+
<details>
|
|
102
|
+
<summary><b>Hono</b></summary>
|
|
103
|
+
|
|
104
|
+
```ts
|
|
105
|
+
import { Hono } from "hono";
|
|
106
|
+
import { auditPanel } from "@xtandard/audit/hono";
|
|
107
|
+
import { createMemoryStorage } from "@xtandard/audit/storage/memory";
|
|
108
|
+
|
|
109
|
+
const audit = auditPanel({ storage: createMemoryStorage(), basePath: "/audit" });
|
|
110
|
+
const app = new Hono();
|
|
111
|
+
app.route("/audit", audit);
|
|
112
|
+
```
|
|
113
|
+
|
|
114
|
+
</details>
|
|
115
|
+
|
|
116
|
+
<details>
|
|
117
|
+
<summary><b>Elysia</b></summary>
|
|
118
|
+
|
|
119
|
+
```ts
|
|
120
|
+
import { Elysia } from "elysia";
|
|
121
|
+
import { auditPanel } from "@xtandard/audit/elysia";
|
|
122
|
+
import { createMemoryStorage } from "@xtandard/audit/storage/memory";
|
|
123
|
+
|
|
124
|
+
new Elysia()
|
|
125
|
+
.mount("/audit", auditPanel({ storage: createMemoryStorage(), basePath: "/audit" }))
|
|
126
|
+
.listen(3000);
|
|
127
|
+
```
|
|
128
|
+
|
|
129
|
+
</details>
|
|
130
|
+
|
|
131
|
+
<details>
|
|
132
|
+
<summary><b>Express</b></summary>
|
|
133
|
+
|
|
134
|
+
```ts
|
|
135
|
+
import express from "express";
|
|
136
|
+
import { auditPanel } from "@xtandard/audit/express";
|
|
137
|
+
import { createMemoryStorage } from "@xtandard/audit/storage/memory";
|
|
138
|
+
|
|
139
|
+
const app = express();
|
|
140
|
+
app.use("/audit", auditPanel({ storage: createMemoryStorage(), basePath: "/audit" })); // before body-parser
|
|
141
|
+
app.listen(3000);
|
|
142
|
+
```
|
|
143
|
+
|
|
144
|
+
</details>
|
|
145
|
+
|
|
146
|
+
<details>
|
|
147
|
+
<summary><b>Bun</b></summary>
|
|
148
|
+
|
|
149
|
+
```ts
|
|
150
|
+
import { auditPanel } from "@xtandard/audit/bun";
|
|
151
|
+
import { createMemoryStorage } from "@xtandard/audit/storage/memory";
|
|
152
|
+
|
|
153
|
+
const audit = auditPanel({ storage: createMemoryStorage(), basePath: "/audit" });
|
|
154
|
+
Bun.serve({ port: 3000, fetch: audit.fetch });
|
|
155
|
+
```
|
|
156
|
+
|
|
157
|
+
</details>
|
|
158
|
+
|
|
159
|
+
## Record your first events
|
|
160
|
+
|
|
161
|
+
```ts
|
|
162
|
+
import { createAuditCore } from "@xtandard/audit";
|
|
163
|
+
import { createPostgresStorage } from "@xtandard/audit/storage/postgres";
|
|
164
|
+
|
|
165
|
+
const audit = createAuditCore({
|
|
166
|
+
storage: createPostgresStorage({ url: process.env.DATABASE_URL! }),
|
|
167
|
+
});
|
|
168
|
+
|
|
169
|
+
// In the handler where the thing actually happens:
|
|
170
|
+
await audit.record({
|
|
171
|
+
tenant: org.id, // the customer organization
|
|
172
|
+
action: "member.role_changed",
|
|
173
|
+
actor: { id: user.id, name: user.name, email: user.email },
|
|
174
|
+
targets: [{ type: "user", id: member.id, name: member.name }],
|
|
175
|
+
context: { ip, userAgent, requestId },
|
|
176
|
+
metadata: { from: "member", to: "admin" },
|
|
177
|
+
});
|
|
178
|
+
```
|
|
179
|
+
|
|
180
|
+
One line of middleware fills `tenant`, `actor`, `ip`, `userAgent` and `requestId` for every event in a request (`auditContext()` in each framework adapter, or `runWithAuditContext` from `@xtandard/audit/context`).
|
|
181
|
+
|
|
182
|
+
## Typed actions
|
|
183
|
+
|
|
184
|
+
Declare your catalog once with any [Standard Schema](https://standardschema.dev) validator — valibot, zod, arktype — and `record()` is type-checked and validated:
|
|
185
|
+
|
|
186
|
+
```ts
|
|
187
|
+
import * as v from "valibot";
|
|
188
|
+
import { createAuditCore, defineActions } from "@xtandard/audit";
|
|
189
|
+
|
|
190
|
+
const actions = defineActions({
|
|
191
|
+
"invoice.paid": {
|
|
192
|
+
metadata: v.object({ invoiceId: v.string(), amount: v.number() }),
|
|
193
|
+
targets: ["invoice"],
|
|
194
|
+
description: "An invoice was paid",
|
|
195
|
+
group: "Billing",
|
|
196
|
+
},
|
|
197
|
+
"member.removed": { targets: ["user"] },
|
|
198
|
+
});
|
|
199
|
+
|
|
200
|
+
const audit = createAuditCore({ storage, actions });
|
|
201
|
+
await audit.record({
|
|
202
|
+
tenant,
|
|
203
|
+
action: "invoice.paid",
|
|
204
|
+
actor,
|
|
205
|
+
metadata: { invoiceId: "inv_1", amount: 4200 },
|
|
206
|
+
});
|
|
207
|
+
// ^ autocompletes; typos and wrong metadata are compile errors
|
|
208
|
+
```
|
|
209
|
+
|
|
210
|
+
## Querying
|
|
211
|
+
|
|
212
|
+
```ts
|
|
213
|
+
const page = await audit.query({
|
|
214
|
+
tenant: "acme",
|
|
215
|
+
actions: ["invoice.*"], // families
|
|
216
|
+
actorId: "user_1",
|
|
217
|
+
targetType: "invoice",
|
|
218
|
+
from: "2026-01-01",
|
|
219
|
+
search: "refund",
|
|
220
|
+
limit: 50,
|
|
221
|
+
});
|
|
222
|
+
// { items, pageInfo: { hasNextPage, endCursor } } — keyset pagination, stable while new events arrive
|
|
223
|
+
const next = await audit.query({ tenant: "acme", cursor: page.pageInfo.endCursor! });
|
|
224
|
+
```
|
|
225
|
+
|
|
226
|
+
The envelope is `@xtandard/lib`'s `Paginated<T>` shape, so it plugs into `createPaginator` and its TanStack Query helpers unchanged. Details: [docs/QUERYING.md](docs/QUERYING.md).
|
|
227
|
+
|
|
228
|
+
## Tamper evidence
|
|
229
|
+
|
|
230
|
+
Every tenant has its own hash chain: each event commits to the previous one, and the privacy-bearing sections (actor, targets, context, metadata, description) are hashed separately — so personal data can be **erased** without breaking the chain, and the erasure itself is recorded. Signed checkpoints (Ed25519, public key served as a JWKS) bind the chain at points in time; streaming them to the customer makes a later rewrite detectable.
|
|
231
|
+
|
|
232
|
+
```ts
|
|
233
|
+
import { createAuditCore, ed25519Signer } from "@xtandard/audit";
|
|
234
|
+
|
|
235
|
+
const audit = createAuditCore({
|
|
236
|
+
storage,
|
|
237
|
+
signer: await ed25519Signer(JSON.parse(process.env.AUDIT_SIGNING_KEY!)),
|
|
238
|
+
});
|
|
239
|
+
const report = await audit.verify("acme"); // { ok, checked, anchor, signedThrough, erased, issues }
|
|
240
|
+
```
|
|
241
|
+
|
|
242
|
+
Customers verify exports offline with nothing but the bundle — `xtandard-audit verify --bundle acme.jsonl` or the zero-dependency `@xtandard/audit/verify`. Details: [docs/INTEGRITY.md](docs/INTEGRITY.md).
|
|
243
|
+
|
|
244
|
+
<img src="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/ui-integrity.png" alt="Integrity view: verification report and signed checkpoints" width="720" />
|
|
245
|
+
|
|
246
|
+
## The customer portal
|
|
247
|
+
|
|
248
|
+
The WorkOS-style audit-log viewer, self-hosted: your customers browse, filter, export and verify **their own** events inside your product, scoped by a signed token — no sessions, no proxy routes.
|
|
249
|
+
|
|
250
|
+
```tsx
|
|
251
|
+
// Your server: mint a token after your own auth (optionally narrowed by a view filter)
|
|
252
|
+
const token = await createPortalToken(process.env.PORTAL_SECRET!, org.id, {
|
|
253
|
+
filter: { excludeActions: ["support.*"] },
|
|
254
|
+
});
|
|
255
|
+
|
|
256
|
+
// Your React frontend:
|
|
257
|
+
import { AuditPortal } from "@xtandard/audit/react";
|
|
258
|
+
import "@xtandard/audit/react/styles.css";
|
|
259
|
+
|
|
260
|
+
<AuditPortal apiBaseUrl="/audit" token={token} />;
|
|
261
|
+
```
|
|
262
|
+
|
|
263
|
+
<picture>
|
|
264
|
+
<source media="(prefers-color-scheme: dark)" srcset="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/ui-portal-dark.png" />
|
|
265
|
+
<img src="https://raw.githubusercontent.com/xantiagoma/xtandard-audit/main/docs/assets/ui-portal-light.png" alt="The customer portal: a tenant's own log with an integrity badge" width="720" />
|
|
266
|
+
</picture>
|
|
267
|
+
|
|
268
|
+
Details: [docs/PORTAL.md](docs/PORTAL.md).
|
|
269
|
+
|
|
270
|
+
## Exports and streaming
|
|
271
|
+
|
|
272
|
+
- **Exports**: CSV (formula-injection safe), JSON, JSONL, and the **verifiable bundle** (events + checkpoints + JWKS in one file). Every export is itself audited.
|
|
273
|
+
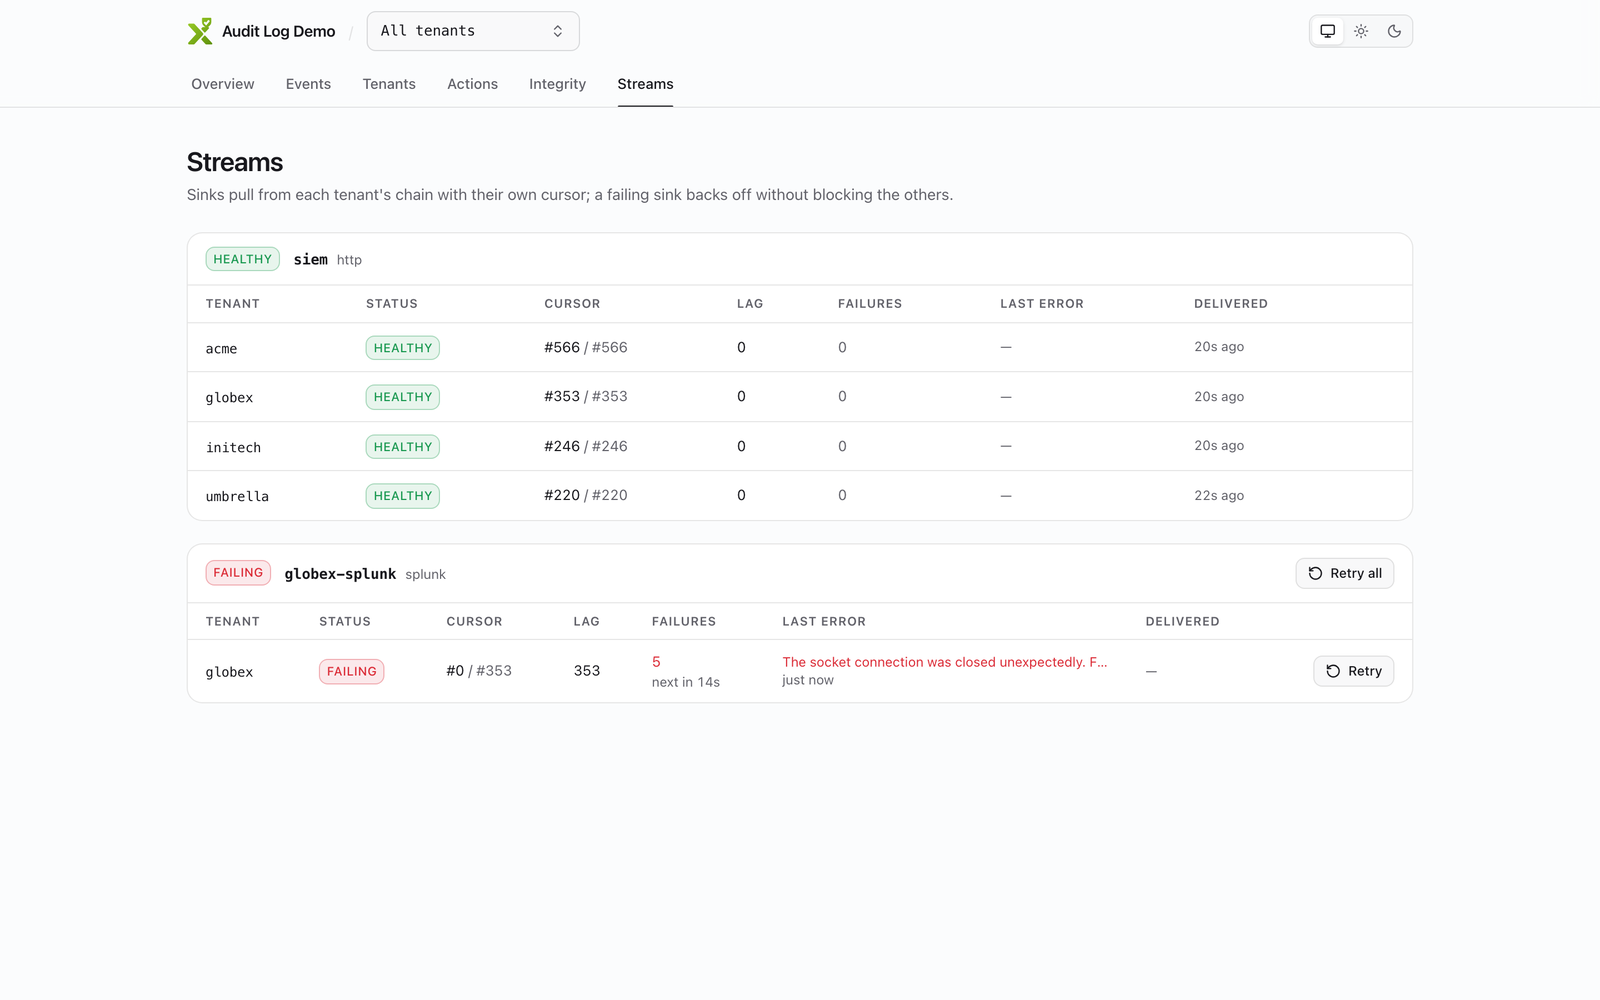
- **Streams**: `httpSink`, `webhookSink` (Standard Webhooks-signed), `datadogSink`, `splunkSink`, `s3Sink`, `fileSink`, `consoleSink` — or bridge into [`@xtandard/webhooks`](https://github.com/xantiagoma/xtandard-webhooks) so each customer manages its own SIEM endpoints. At-least-once, per-tenant ordered, with backoff and lag shown in the admin UI.
|
|
274
|
+
|
|
275
|
+
Details: [docs/STREAMING.md](docs/STREAMING.md).
|
|
276
|
+
|
|
277
|
+
## Storage backends
|
|
278
|
+
|
|
279
|
+
Point it at what you already run — a four-method KV contract plus an optional native event-log capability for indexed queries ([ADR 0005](docs/ADR/0005-storage-kv-contract-event-log-capability.md)):
|
|
280
|
+
|
|
281
|
+
| Backend | Subpath | Event log |
|
|
282
|
+
| -------------- | ----------------------------------------------- | ----------------------- |
|
|
283
|
+
| Memory | `storage/memory` | native |
|
|
284
|
+
| Postgres | `storage/postgres` | native (indexed SQL) |
|
|
285
|
+
| Drizzle | `storage/drizzle` + `drizzle/{pg,mysql,sqlite}` | native, your migrations |
|
|
286
|
+
| SQLite (Bun) | `storage/sqlite` | native |
|
|
287
|
+
| libSQL / Turso | `storage/libsql` | native |
|
|
288
|
+
| MongoDB | `storage/mongodb` | native |
|
|
289
|
+
| Redis | `storage/redis` | KV index fallback |
|
|
290
|
+
| File | `storage/file` | KV index fallback |
|
|
291
|
+
| unstorage | `storage/unstorage` | KV index fallback |
|
|
292
|
+
| Cloudflare KV | `storage/cloudflare-kv` | KV index fallback |
|
|
293
|
+
|
|
294
|
+
Details: [docs/STORAGE.md](docs/STORAGE.md).
|
|
295
|
+
|
|
296
|
+
## Subpath exports
|
|
297
|
+
|
|
298
|
+
| Import | What you get |
|
|
299
|
+
| ---------------------------------------- | ------------------------------------------------------------------------------- |
|
|
300
|
+
| `@xtandard/audit` | core, recorder, transforms, integrity, exports, streams, portal tokens, handler |
|
|
301
|
+
| `…/verify` | zero-dependency verifier for auditors (`verifyBundle`, `verifyChain`) |
|
|
302
|
+
| `…/context` | ambient request context (AsyncLocalStorage) |
|
|
303
|
+
| `…/schema`, `…/core` | types / the core alone |
|
|
304
|
+
| `…/testing` | test core + collecting sink + assertions |
|
|
305
|
+
| `…/storage/*`, `…/drizzle/*` | storage adapters (optional peers) |
|
|
306
|
+
| `…/sinks/*` | stream sinks |
|
|
307
|
+
| `…/drizzle-audit` | bridge from [drizzle-audit](https://github.com/xantiagoma/drizzle-audit) |
|
|
308
|
+
| `…/auth/{none,basic,delegated}` | authentication providers |
|
|
309
|
+
| `…/authorization/{none,roles,delegated}` | authorization providers |
|
|
310
|
+
| `…/hooks/log` | reference logging hook |
|
|
311
|
+
| `…/{elysia,elysia2,hono,express,bun}` | framework adapters + `auditContext` middleware |
|
|
312
|
+
| `…/react`, `…/react/styles.css` | `<AuditDashboard>` + `<AuditPortal>` embeds |
|
|
313
|
+
|
|
314
|
+
## Examples
|
|
315
|
+
|
|
316
|
+
`bun run demo` boots a seeded playground on http://localhost:7790 — four customer tenants with six weeks of realistic history (sign-ins, member and role changes, invoices paid / failed / refunded, API keys, SSO, deployments, exports, GDPR erasures), daily Ed25519 checkpoints, a pruned retention window, a SIEM stream catching up, a customer's Splunk stream stuck on a revoked token, and portal links per tenant.
|
|
317
|
+
|
|
318
|
+
| Example | Shows |
|
|
319
|
+
| ------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------- |
|
|
320
|
+
| [`hono`](examples/hono) / [`elysia`](examples/elysia) / [`express`](examples/express) / [`bun`](examples/bun) | panel + a team-settings app recording on real user actions via `auditContext` |
|
|
321
|
+
| [`auth`](examples/auth) | none/basic/delegated + admin/auditor/viewer roles + portal tokens side by side |
|
|
322
|
+
| [`portal-embed`](examples/portal-embed) | `<AuditPortal>` inside a host React app, with a server minting portal tokens |
|
|
323
|
+
| [`storage-drivers`](examples/storage-drivers) | one contract, every serverless backend, the same query results |
|
|
324
|
+
| [`postgres`](examples/postgres) | docker Postgres + the audit tables in your Drizzle schema, migrated by drizzle-kit |
|
|
325
|
+
| [`siem-streaming`](examples/siem-streaming) | HTTP + signed-webhook + checkpoint-witness streams; failures, backoff, catch-up |
|
|
326
|
+
| [`drizzle-audit-bridge`](examples/drizzle-audit-bridge) | drizzle-audit row changes → the chained, tenant-scoped log |
|
|
327
|
+
| [`verify-export`](examples/verify-export) | signed bundles verified offline: `@xtandard/audit/verify` + CLI exit codes 0/2/1 |
|
|
328
|
+
| [`standalone-docker`](examples/standalone-docker) | compose file for the image, with Postgres |
|
|
329
|
+
|
|
330
|
+
## Screenshots
|
|
331
|
+
|
|
332
|
+
| | |
|
|
333
|
+
| -------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------ |
|
|
334
|
+
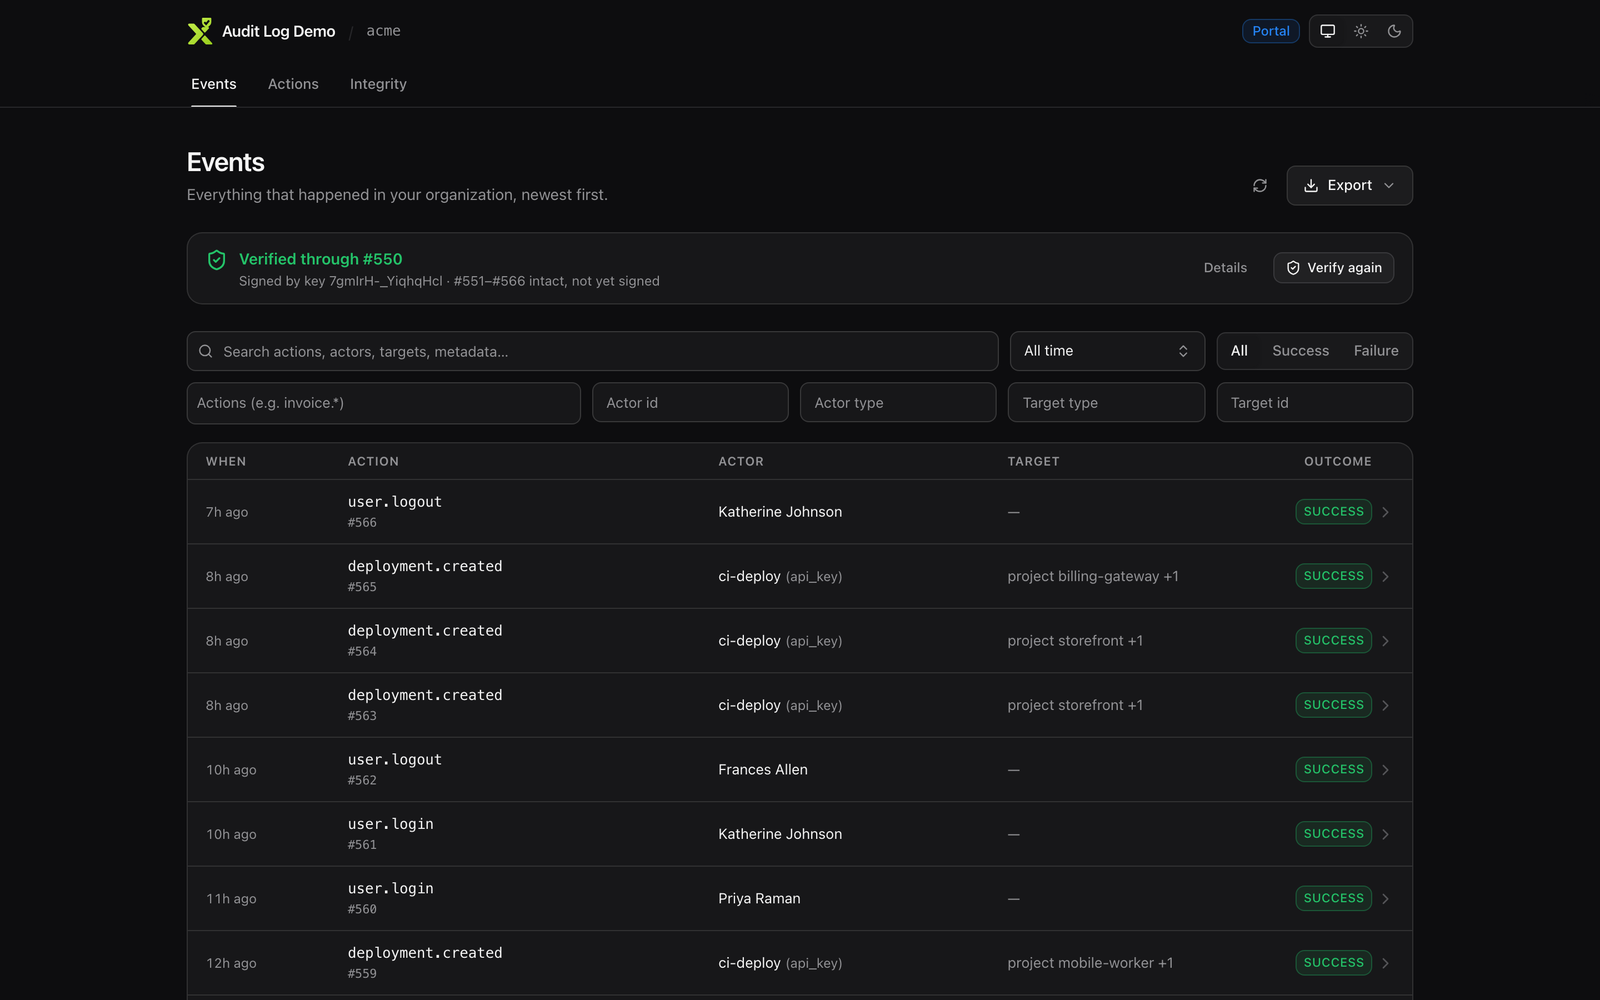
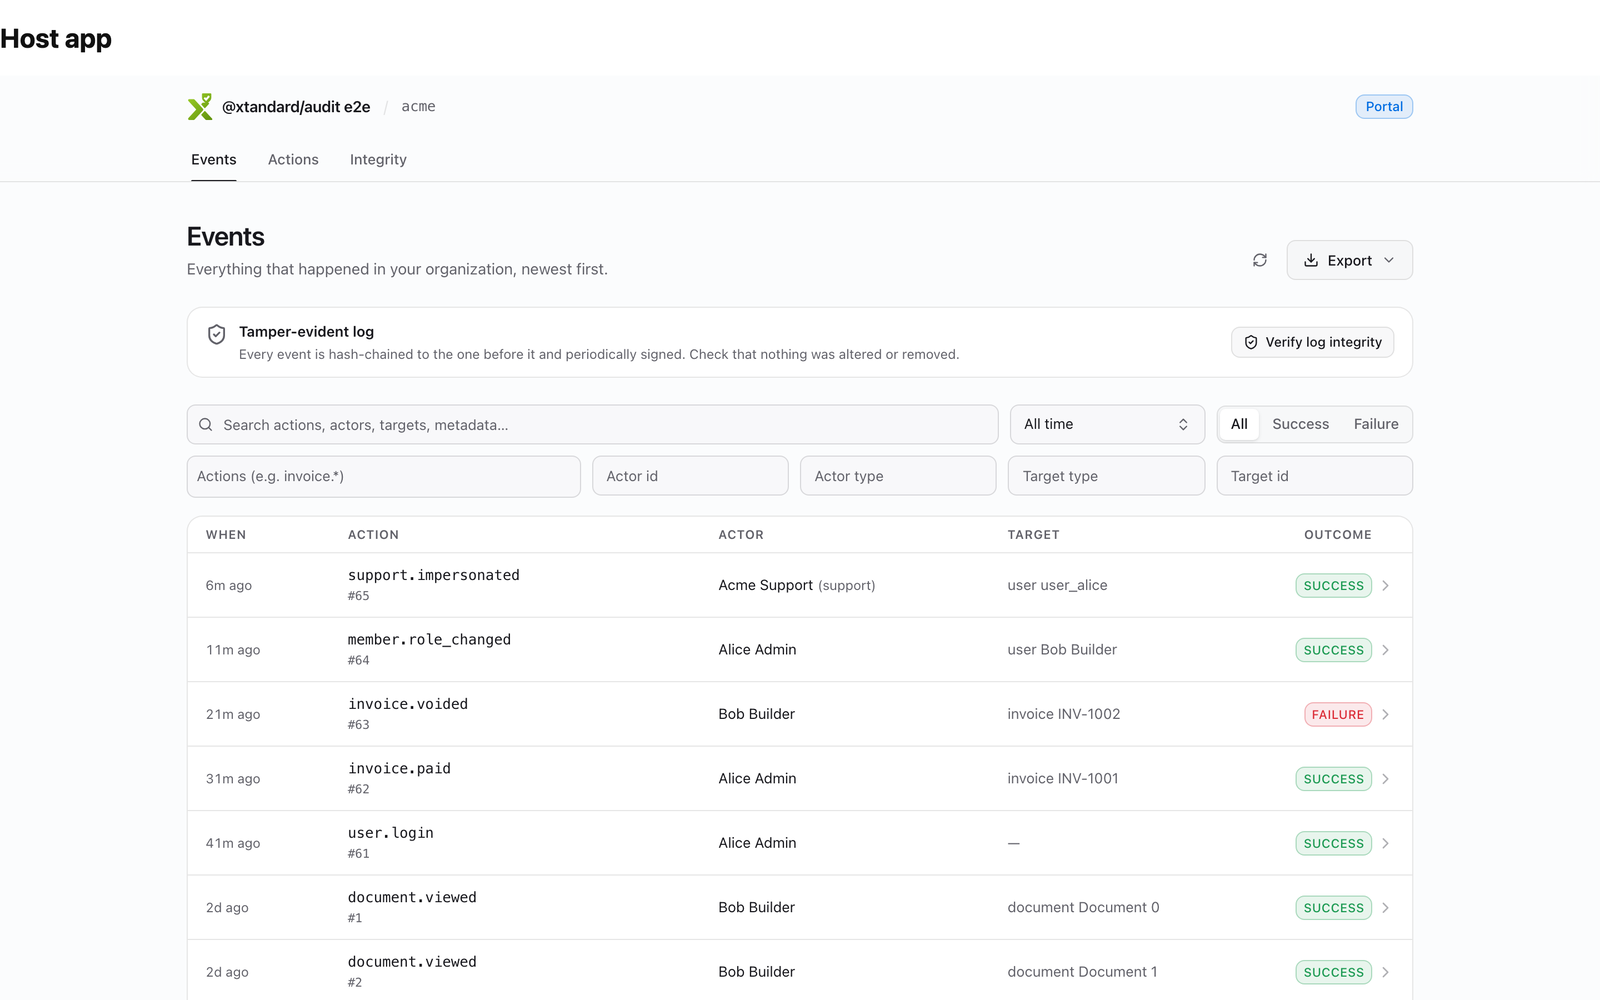
| 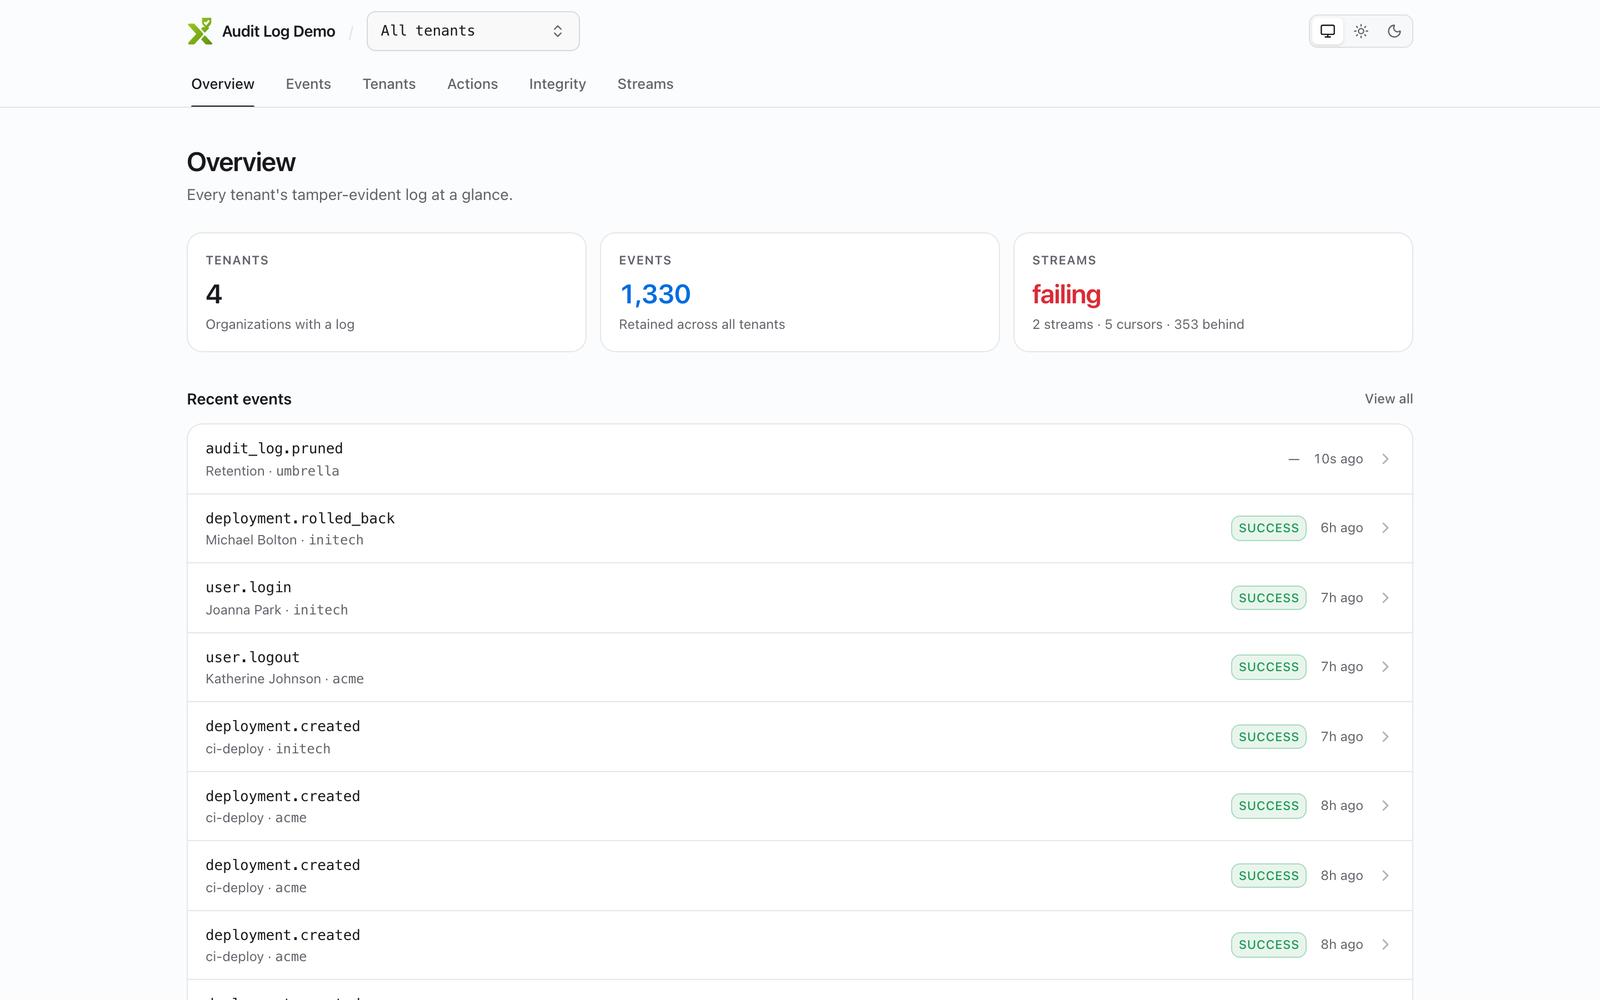 | 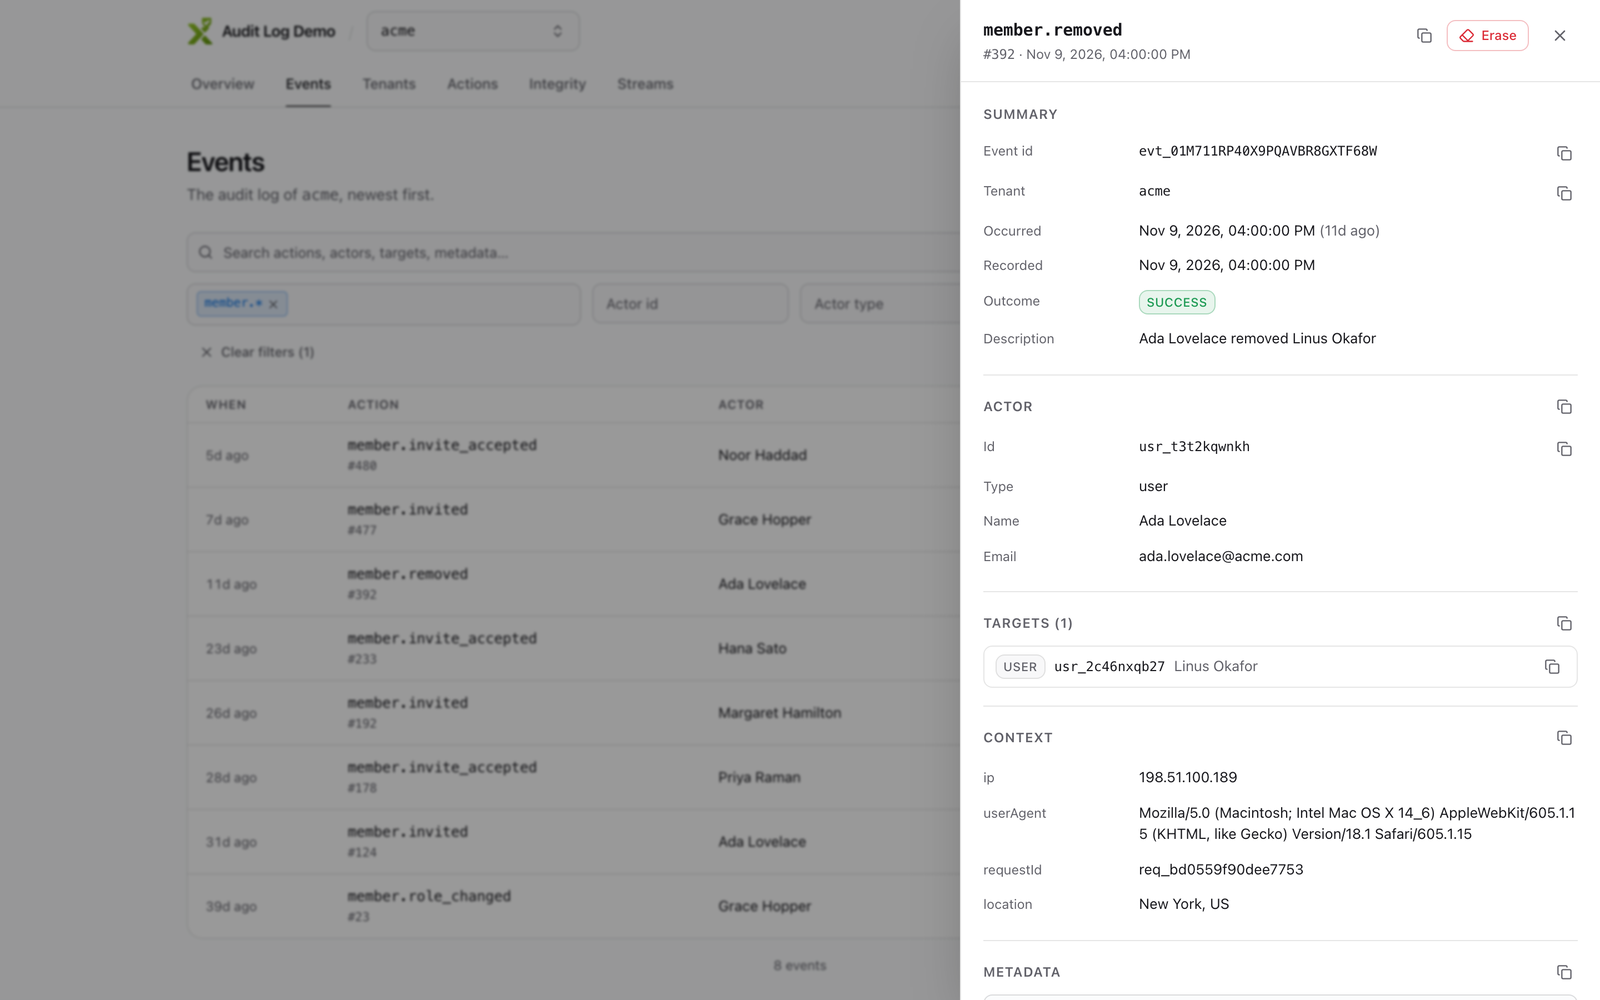 |
|
|
335
|
+
|  | 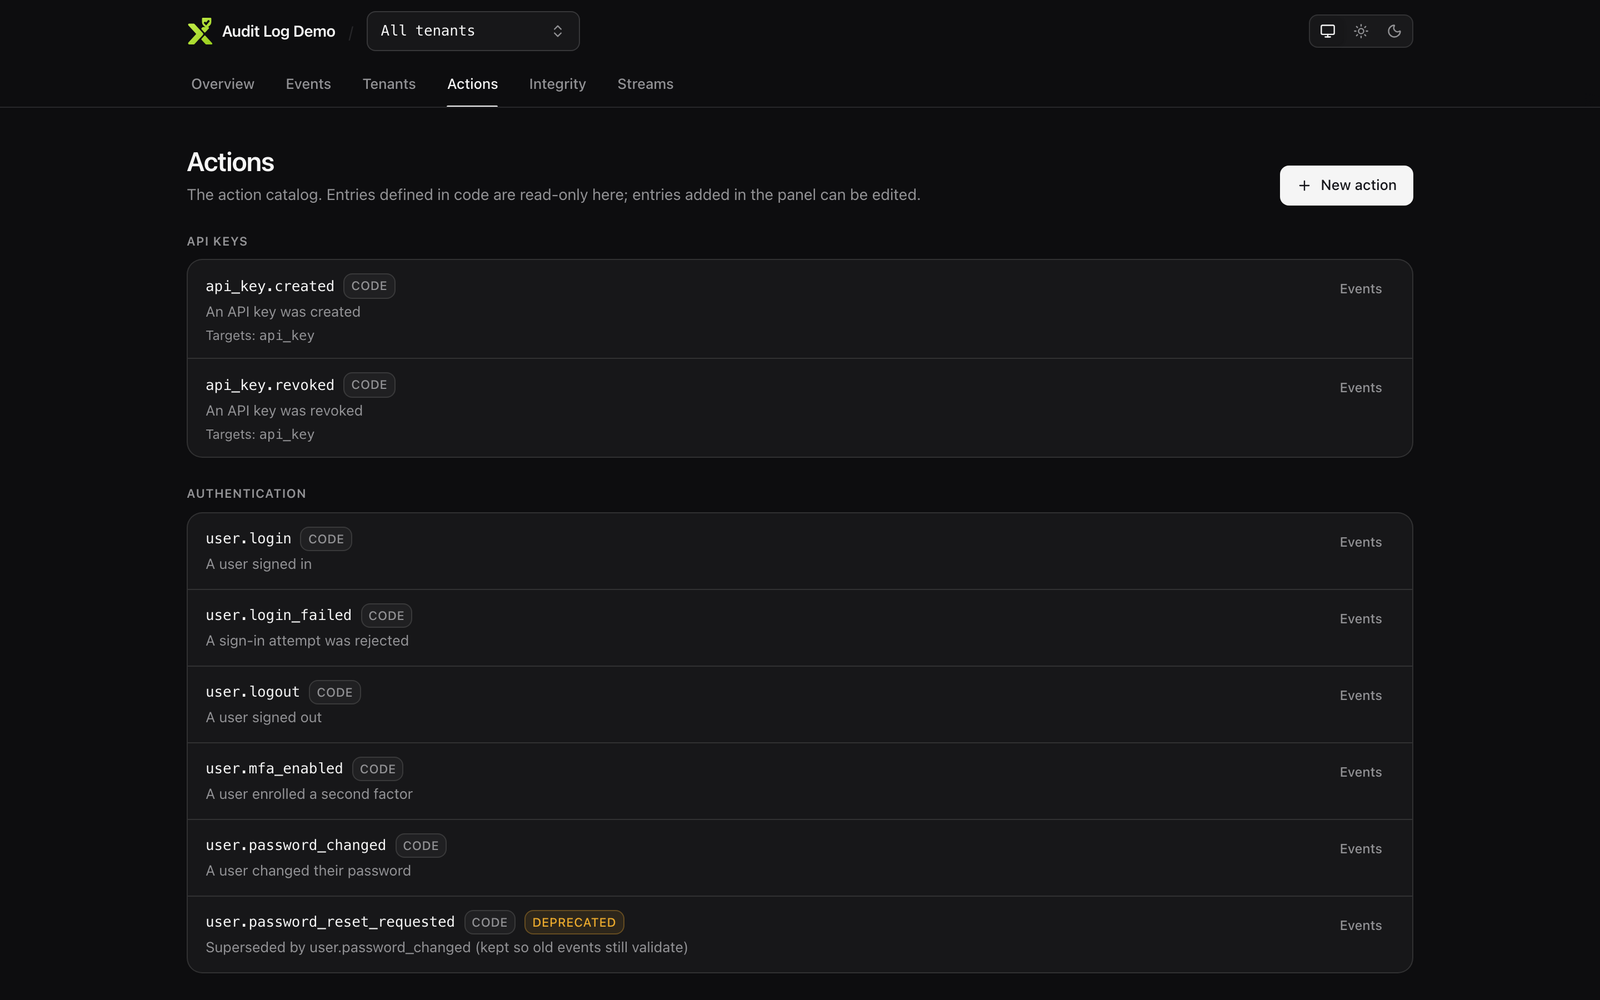 |
|
|
336
|
+
|  |  |
|
|
337
|
+
|
|
338
|
+
`bun run demo` serves this seeded playground on http://localhost:7790.
|
|
339
|
+
|
|
340
|
+
## CLI
|
|
341
|
+
|
|
342
|
+
```txt
|
|
343
|
+
xtandard-audit serve # panel + streams from env
|
|
344
|
+
xtandard-audit record --tenant acme --action user.login --actor u_1
|
|
345
|
+
xtandard-audit query --tenant acme --actions 'invoice.*' --json
|
|
346
|
+
xtandard-audit export --tenant acme --format bundle > acme.jsonl
|
|
347
|
+
xtandard-audit verify --bundle acme.jsonl # exit 0 valid, 2 valid but unanchored, 1 invalid
|
|
348
|
+
xtandard-audit checkpoint --tenant acme
|
|
349
|
+
xtandard-audit prune
|
|
350
|
+
xtandard-audit keygen # Ed25519 signing key + public JWKS
|
|
351
|
+
```
|
|
352
|
+
|
|
353
|
+
Env contract: [docs/DEPLOYMENT.md](docs/DEPLOYMENT.md).
|
|
354
|
+
|
|
355
|
+
## Documentation
|
|
356
|
+
|
|
357
|
+
The full documentation, with the API reference, is at **[me.xantiagoma.com/xtandard-audit](https://me.xantiagoma.com/xtandard-audit/)**. The guides, on GitHub:
|
|
358
|
+
|
|
359
|
+
[Getting started](docs/GETTING_STARTED.md) · [Architecture](docs/ARCHITECTURE.md) · [Querying](docs/QUERYING.md) · [Integrity](docs/INTEGRITY.md) · [Storage](docs/STORAGE.md) · [Streaming](docs/STREAMING.md) · [Portal](docs/PORTAL.md) · [Auth](docs/AUTH.md) · [Authorization](docs/AUTHORIZATION.md) · [Hooks](docs/HOOKS.md) · [UI](docs/UI.md) · [Adapters](docs/ADAPTERS.md) · [HTTP API](docs/HTTP_API.md) · [Deployment](docs/DEPLOYMENT.md) · [Testing](docs/TESTING.md) · [drizzle-audit](docs/DRIZZLE_AUDIT.md) · [Releases](docs/RELEASES.md) · [Brand](docs/BRAND.md) · [ADRs](docs/ADR)
|
|
360
|
+
|
|
361
|
+
## Project status
|
|
362
|
+
|
|
363
|
+
ZeroVer (`0.x`) and pre-first-publish: the surface is stabilizing, minor versions may break, and feedback shapes it — issues welcome. Anti-bloat is a core value: when a feature is composable from an existing primitive in ten lines, we document the recipe instead of shipping the subsystem.
|
|
364
|
+
|
|
365
|
+
## The xtandard ecosystem
|
|
366
|
+
|
|
367
|
+
`@xtandard/audit` is one of a family of open-source, MIT-licensed projects that share the xtandard name. They are independent of each other: use any of them on its own.
|
|
368
|
+
|
|
369
|
+
| Project | What it is | Links |
|
|
370
|
+
| ------------------------------------ | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
|
|
371
|
+
| **`@xtandard/audit`** (this package) | A self-hosted, embeddable, tamper-evident audit-log control plane for B2B SaaS: a WorkOS Audit Logs alternative as a library | [Docs](https://me.xantiagoma.com/xtandard-audit/) · [GitHub](https://github.com/xantiagoma/xtandard-audit) · [npm](https://www.npmjs.com/package/@xtandard/audit) |
|
|
372
|
+
| **`@xtandard/lib`** | Lightweight, type-safe TypeScript utilities with a zero-dependency core | [Docs](https://me.xantiagoma.com/xtandard/) · [GitHub](https://github.com/xantiagoma/xtandard) · [npm](https://www.npmjs.com/package/@xtandard/lib) |
|
|
373
|
+
| **`@xtandard/flags`** | A self-hosted, embeddable, OpenFeature-compatible feature-flag control plane with pluggable storage | [Docs](https://me.xantiagoma.com/xtandard-flags/) · [GitHub](https://github.com/xantiagoma/xtandard-flags) · [npm](https://www.npmjs.com/package/@xtandard/flags) |
|
|
374
|
+
| **`@xtandard/webhooks`** | A self-hosted, embeddable, Standard Webhooks-compliant outbound-webhooks control plane: a Svix alternative as a library | [Docs](https://me.xantiagoma.com/xtandard-webhooks/) · [GitHub](https://github.com/xantiagoma/xtandard-webhooks) · [npm](https://www.npmjs.com/package/@xtandard/webhooks) |
|
|
375
|
+
| **`@xtandard/xyte`** | A Zyte API-compatible `/v1/extract` client and server that runs on any proxy provider, or none | [Docs](https://me.xantiagoma.com/xyte/) · [GitHub](https://github.com/xantiagoma/xyte) · [npm](https://www.npmjs.com/package/@xtandard/xyte) |
|
|
376
|
+
| **xtandard-image** | A self-hosted image and video processing server in Go and libvips: imgproxy-compatible URLs plus the imgix, Cloudinary, ImageKit, Cloudflare and Thumbor dialects, with a TypeScript client (`@xtandard/image`) | [Docs](https://me.xantiagoma.com/xtandard-image/) · [GitHub](https://github.com/xantiagoma/xtandard-image) · [npm](https://www.npmjs.com/package/@xtandard/image) |
|
|
377
|
+
|
|
378
|
+
### Related
|
|
379
|
+
|
|
380
|
+
- [drizzle-cursor](https://github.com/xantiagoma/drizzle-cursor): cursor-based pagination for Drizzle ORM
|
|
381
|
+
- [drizzle-audit](https://github.com/xantiagoma/drizzle-audit): configurable audit logging for Drizzle ORM — capture row-level changes and forward them here with `@xtandard/audit/drizzle-audit`
|
|
382
|
+
|
|
383
|
+
## License
|
|
384
|
+
|
|
385
|
+
[MIT](./LICENSE)
|
|
@@ -0,0 +1,176 @@
|
|
|
1
|
+
import { t as __exportAll } from "./chunk-D7D4PA-g.mjs";
|
|
2
|
+
import { randomBytes, scrypt, timingSafeEqual } from "node:crypto";
|
|
3
|
+
//#region src/auth/basic.ts
|
|
4
|
+
/**
|
|
5
|
+
* HTTP Basic authentication {@link AuthProvider}.
|
|
6
|
+
*
|
|
7
|
+
* Parses the `Authorization: Basic <base64>` header, looks the username up in a
|
|
8
|
+
* configured user list, and verifies the supplied password using one of three
|
|
9
|
+
* credential modes (in order of preference):
|
|
10
|
+
*
|
|
11
|
+
* 1. A custom `passwordVerifier(username, password)` callback — for delegating
|
|
12
|
+
* to your own user store.
|
|
13
|
+
* 2. A `passwordHash` produced by {@link hashPassword} — scrypt with a random
|
|
14
|
+
* salt, verified in constant time. **Recommended for production.**
|
|
15
|
+
* 3. A plain `password` field — **development only**. Never ship real
|
|
16
|
+
* credentials as plaintext; they are compared in constant time but stored as
|
|
17
|
+
* cleartext in your config.
|
|
18
|
+
*
|
|
19
|
+
* On success the matched user becomes a {@link Principal}; on any failure
|
|
20
|
+
* (missing/malformed header, unknown user, bad password) `authenticate` returns
|
|
21
|
+
* `null`. {@link AuthProvider.challenge} emits a `401` with a
|
|
22
|
+
* `WWW-Authenticate: Basic realm="…"` header so browsers prompt for credentials.
|
|
23
|
+
*
|
|
24
|
+
* Password hashing uses Node's `node:crypto` `scrypt`, which is available in
|
|
25
|
+
* both Node and Bun — no Bun-only APIs and no extra dependencies.
|
|
26
|
+
*
|
|
27
|
+
* @module
|
|
28
|
+
*/
|
|
29
|
+
var basic_exports = /* @__PURE__ */ __exportAll({
|
|
30
|
+
basicAuth: () => basicAuth,
|
|
31
|
+
hashPassword: () => hashPassword,
|
|
32
|
+
verifyPassword: () => verifyPassword
|
|
33
|
+
});
|
|
34
|
+
/** scrypt key length (bytes) used by {@link hashPassword}. */
|
|
35
|
+
const KEY_LENGTH = 64;
|
|
36
|
+
/** Salt length (bytes) used by {@link hashPassword}. */
|
|
37
|
+
const SALT_LENGTH = 16;
|
|
38
|
+
/** Prefix identifying a {@link hashPassword} digest. */
|
|
39
|
+
const SCRYPT_PREFIX = "scrypt";
|
|
40
|
+
const scryptAsync = (password, salt, keylen) => new Promise((resolve, reject) => {
|
|
41
|
+
scrypt(password, salt, keylen, (err, derivedKey) => {
|
|
42
|
+
if (err) reject(err);
|
|
43
|
+
else resolve(derivedKey);
|
|
44
|
+
});
|
|
45
|
+
});
|
|
46
|
+
/** Lowercase hex encoding of a buffer. */
|
|
47
|
+
const toHex = (buf) => buf.toString("hex");
|
|
48
|
+
/**
|
|
49
|
+
* Hash a password with scrypt and a fresh random salt.
|
|
50
|
+
*
|
|
51
|
+
* The returned string is self-describing and safe to store in config or a
|
|
52
|
+
* database: `scrypt$<saltHex>$<hashHex>`. Pass it back to
|
|
53
|
+
* {@link verifyPassword} (or supply it as a user's `passwordHash`) to check a
|
|
54
|
+
* candidate password.
|
|
55
|
+
*
|
|
56
|
+
* @example
|
|
57
|
+
* ```ts
|
|
58
|
+
* const stored = await hashPassword("correct horse battery staple");
|
|
59
|
+
* // → "scrypt$<32 hex chars>$<128 hex chars>"
|
|
60
|
+
* ```
|
|
61
|
+
*/
|
|
62
|
+
async function hashPassword(password) {
|
|
63
|
+
const salt = randomBytes(SALT_LENGTH);
|
|
64
|
+
const derived = await scryptAsync(password, salt, KEY_LENGTH);
|
|
65
|
+
return `${SCRYPT_PREFIX}$${toHex(salt)}$${toHex(derived)}`;
|
|
66
|
+
}
|
|
67
|
+
/**
|
|
68
|
+
* Verify a candidate `password` against a digest produced by
|
|
69
|
+
* {@link hashPassword}.
|
|
70
|
+
*
|
|
71
|
+
* Re-derives the scrypt hash using the stored salt and compares it to the stored
|
|
72
|
+
* hash with `crypto.timingSafeEqual` (constant time). Returns `false` — rather
|
|
73
|
+
* than throwing — for malformed or unrecognized digests.
|
|
74
|
+
*/
|
|
75
|
+
async function verifyPassword(password, stored) {
|
|
76
|
+
const parts = stored.split("$");
|
|
77
|
+
if (parts.length !== 3 || parts[0] !== SCRYPT_PREFIX) return false;
|
|
78
|
+
const saltHex = parts[1];
|
|
79
|
+
const hashHex = parts[2];
|
|
80
|
+
if (!saltHex || !hashHex) return false;
|
|
81
|
+
let salt;
|
|
82
|
+
let expected;
|
|
83
|
+
try {
|
|
84
|
+
salt = Buffer.from(saltHex, "hex");
|
|
85
|
+
expected = Buffer.from(hashHex, "hex");
|
|
86
|
+
} catch {
|
|
87
|
+
return false;
|
|
88
|
+
}
|
|
89
|
+
if (salt.length === 0 || expected.length === 0) return false;
|
|
90
|
+
const derived = await scryptAsync(password, salt, expected.length);
|
|
91
|
+
if (derived.length !== expected.length) return false;
|
|
92
|
+
return timingSafeEqual(derived, expected);
|
|
93
|
+
}
|
|
94
|
+
/** Constant-time string comparison that does not leak length via early exit. */
|
|
95
|
+
function constantTimeEquals(a, b) {
|
|
96
|
+
const bufA = Buffer.from(a, "utf8");
|
|
97
|
+
const bufB = Buffer.from(b, "utf8");
|
|
98
|
+
if (bufA.length !== bufB.length) {
|
|
99
|
+
timingSafeEqual(bufA, bufA);
|
|
100
|
+
return false;
|
|
101
|
+
}
|
|
102
|
+
return timingSafeEqual(bufA, bufB);
|
|
103
|
+
}
|
|
104
|
+
/** Decode the `Authorization: Basic <base64>` header, or `null` if absent/malformed. */
|
|
105
|
+
function parseBasicHeader(request) {
|
|
106
|
+
const header = request.headers.get("authorization");
|
|
107
|
+
if (!header) return null;
|
|
108
|
+
const [scheme, encoded] = header.split(" ", 2);
|
|
109
|
+
if (!scheme || scheme.toLowerCase() !== "basic" || !encoded) return null;
|
|
110
|
+
let decoded;
|
|
111
|
+
try {
|
|
112
|
+
decoded = Buffer.from(encoded, "base64").toString("utf8");
|
|
113
|
+
} catch {
|
|
114
|
+
return null;
|
|
115
|
+
}
|
|
116
|
+
const sep = decoded.indexOf(":");
|
|
117
|
+
if (sep < 0) return null;
|
|
118
|
+
return {
|
|
119
|
+
username: decoded.slice(0, sep),
|
|
120
|
+
password: decoded.slice(sep + 1)
|
|
121
|
+
};
|
|
122
|
+
}
|
|
123
|
+
/** Build the {@link Principal} for a successfully authenticated user. */
|
|
124
|
+
function principalFor(user) {
|
|
125
|
+
return {
|
|
126
|
+
id: user.id ?? user.username,
|
|
127
|
+
name: user.username,
|
|
128
|
+
...user.email !== void 0 ? { email: user.email } : {},
|
|
129
|
+
...user.roles !== void 0 ? { roles: user.roles } : {}
|
|
130
|
+
};
|
|
131
|
+
}
|
|
132
|
+
/**
|
|
133
|
+
* Create an HTTP Basic {@link AuthProvider}.
|
|
134
|
+
*
|
|
135
|
+
* @example
|
|
136
|
+
* ```ts
|
|
137
|
+
* import { basicAuth, hashPassword } from "@xtandard/audit/auth/basic";
|
|
138
|
+
*
|
|
139
|
+
* const auth = basicAuth({
|
|
140
|
+
* realm: "Audit Admin",
|
|
141
|
+
* users: [
|
|
142
|
+
* { username: "admin", passwordHash: await hashPassword("s3cret"), roles: ["admin"] },
|
|
143
|
+
* ],
|
|
144
|
+
* });
|
|
145
|
+
* ```
|
|
146
|
+
*/
|
|
147
|
+
function basicAuth(options) {
|
|
148
|
+
const realm = options.realm ?? "xtandard-audit";
|
|
149
|
+
const usersByName = /* @__PURE__ */ new Map();
|
|
150
|
+
for (const user of options.users) usersByName.set(user.username, user);
|
|
151
|
+
return {
|
|
152
|
+
async authenticate(request) {
|
|
153
|
+
const creds = parseBasicHeader(request);
|
|
154
|
+
if (!creds) return null;
|
|
155
|
+
const user = usersByName.get(creds.username);
|
|
156
|
+
if (!user) {
|
|
157
|
+
if (options.passwordVerifier) await options.passwordVerifier(creds.username, creds.password);
|
|
158
|
+
return null;
|
|
159
|
+
}
|
|
160
|
+
if (options.passwordVerifier) return await options.passwordVerifier(creds.username, creds.password) ? principalFor(user) : null;
|
|
161
|
+
if (user.passwordHash !== void 0) return await verifyPassword(creds.password, user.passwordHash) ? principalFor(user) : null;
|
|
162
|
+
if (user.password !== void 0) return constantTimeEquals(creds.password, user.password) ? principalFor(user) : null;
|
|
163
|
+
return null;
|
|
164
|
+
},
|
|
165
|
+
challenge(_request) {
|
|
166
|
+
return new Response("Unauthorized", {
|
|
167
|
+
status: 401,
|
|
168
|
+
headers: { "WWW-Authenticate": `Basic realm="${realm}"` }
|
|
169
|
+
});
|
|
170
|
+
}
|
|
171
|
+
};
|
|
172
|
+
}
|
|
173
|
+
//#endregion
|
|
174
|
+
export { verifyPassword as i, basic_exports as n, hashPassword as r, basicAuth as t };
|
|
175
|
+
|
|
176
|
+
//# sourceMappingURL=basic-DU_nPrWV.mjs.map
|
|
@@ -0,0 +1 @@
|
|
|
1
|
+
{"version":3,"file":"basic-DU_nPrWV.mjs","names":[],"sources":["../src/auth/basic.ts"],"sourcesContent":["/**\n * HTTP Basic authentication {@link AuthProvider}.\n *\n * Parses the `Authorization: Basic <base64>` header, looks the username up in a\n * configured user list, and verifies the supplied password using one of three\n * credential modes (in order of preference):\n *\n * 1. A custom `passwordVerifier(username, password)` callback — for delegating\n * to your own user store.\n * 2. A `passwordHash` produced by {@link hashPassword} — scrypt with a random\n * salt, verified in constant time. **Recommended for production.**\n * 3. A plain `password` field — **development only**. Never ship real\n * credentials as plaintext; they are compared in constant time but stored as\n * cleartext in your config.\n *\n * On success the matched user becomes a {@link Principal}; on any failure\n * (missing/malformed header, unknown user, bad password) `authenticate` returns\n * `null`. {@link AuthProvider.challenge} emits a `401` with a\n * `WWW-Authenticate: Basic realm=\"…\"` header so browsers prompt for credentials.\n *\n * Password hashing uses Node's `node:crypto` `scrypt`, which is available in\n * both Node and Bun — no Bun-only APIs and no extra dependencies.\n *\n * @module\n */\n\nimport { randomBytes, scrypt as scryptCb, timingSafeEqual } from \"node:crypto\";\nimport type { AuthProvider, Principal } from \"./contract.ts\";\n\n/** scrypt key length (bytes) used by {@link hashPassword}. */\nconst KEY_LENGTH = 64;\n/** Salt length (bytes) used by {@link hashPassword}. */\nconst SALT_LENGTH = 16;\n/** Prefix identifying a {@link hashPassword} digest. */\nconst SCRYPT_PREFIX = \"scrypt\";\n\nconst scryptAsync = (password: string, salt: Buffer, keylen: number): Promise<Buffer> =>\n new Promise((resolve, reject) => {\n scryptCb(password, salt, keylen, (err, derivedKey) => {\n if (err) reject(err);\n else resolve(derivedKey);\n });\n });\n\n/** Lowercase hex encoding of a buffer. */\nconst toHex = (buf: Buffer): string => buf.toString(\"hex\");\n\n/**\n * Hash a password with scrypt and a fresh random salt.\n *\n * The returned string is self-describing and safe to store in config or a\n * database: `scrypt$<saltHex>$<hashHex>`. Pass it back to\n * {@link verifyPassword} (or supply it as a user's `passwordHash`) to check a\n * candidate password.\n *\n * @example\n * ```ts\n * const stored = await hashPassword(\"correct horse battery staple\");\n * // → \"scrypt$<32 hex chars>$<128 hex chars>\"\n * ```\n */\nexport async function hashPassword(password: string): Promise<string> {\n const salt = randomBytes(SALT_LENGTH);\n const derived = await scryptAsync(password, salt, KEY_LENGTH);\n return `${SCRYPT_PREFIX}$${toHex(salt)}$${toHex(derived)}`;\n}\n\n/**\n * Verify a candidate `password` against a digest produced by\n * {@link hashPassword}.\n *\n * Re-derives the scrypt hash using the stored salt and compares it to the stored\n * hash with `crypto.timingSafeEqual` (constant time). Returns `false` — rather\n * than throwing — for malformed or unrecognized digests.\n */\nexport async function verifyPassword(password: string, stored: string): Promise<boolean> {\n const parts = stored.split(\"$\");\n if (parts.length !== 3 || parts[0] !== SCRYPT_PREFIX) return false;\n const saltHex = parts[1];\n const hashHex = parts[2];\n if (!saltHex || !hashHex) return false;\n\n let salt: Buffer;\n let expected: Buffer;\n try {\n salt = Buffer.from(saltHex, \"hex\");\n expected = Buffer.from(hashHex, \"hex\");\n } catch {\n return false;\n }\n if (salt.length === 0 || expected.length === 0) return false;\n\n const derived = await scryptAsync(password, salt, expected.length);\n if (derived.length !== expected.length) return false;\n return timingSafeEqual(derived, expected);\n}\n\n/** A configured user for {@link basicAuth}. */\nexport interface BasicAuthUser {\n /** The login name, matched against the Basic credentials. */\n username: string;\n /**\n * A digest produced by {@link hashPassword} (`scrypt$<salt>$<hash>`).\n * Preferred for production.\n */\n passwordHash?: string;\n /**\n * A plaintext password. **Development only** — prefer `passwordHash`. Compared\n * in constant time but stored as cleartext in your config.\n */\n password?: string;\n /** Roles attached to the resulting {@link Principal}. */\n roles?: string[];\n /** Email attached to the resulting {@link Principal}. */\n email?: string;\n /** Principal id. Defaults to {@link BasicAuthUser.username} when omitted. */\n id?: string;\n}\n\n/** Options for {@link basicAuth}. */\nexport interface BasicAuthOptions {\n /** The known users. */\n users: BasicAuthUser[];\n /**\n * Realm advertised in the `WWW-Authenticate` header on challenge.\n * @default \"xtandard-audit\"\n */\n realm?: string;\n /**\n * Custom verifier. When supplied it takes precedence over `passwordHash` and\n * `password` for matched users — delegate to your own credential store and\n * return `true` to accept.\n */\n passwordVerifier?: (username: string, password: string) => Promise<boolean> | boolean;\n}\n\n/** Constant-time string comparison that does not leak length via early exit. */\nfunction constantTimeEquals(a: string, b: string): boolean {\n const bufA = Buffer.from(a, \"utf8\");\n const bufB = Buffer.from(b, \"utf8\");\n // timingSafeEqual requires equal lengths; hash to a fixed width first so the\n // comparison time does not depend on the inputs.\n if (bufA.length !== bufB.length) {\n // Still perform a comparison to keep timing uniform, then fail.\n timingSafeEqual(bufA, bufA);\n return false;\n }\n return timingSafeEqual(bufA, bufB);\n}\n\n/** Result of parsing an `Authorization: Basic` header. */\ninterface BasicCredentials {\n username: string;\n password: string;\n}\n\n/** Decode the `Authorization: Basic <base64>` header, or `null` if absent/malformed. */\nfunction parseBasicHeader(request: Request): BasicCredentials | null {\n const header = request.headers.get(\"authorization\");\n if (!header) return null;\n const [scheme, encoded] = header.split(\" \", 2);\n if (!scheme || scheme.toLowerCase() !== \"basic\" || !encoded) return null;\n\n let decoded: string;\n try {\n decoded = Buffer.from(encoded, \"base64\").toString(\"utf8\");\n } catch {\n return null;\n }\n const sep = decoded.indexOf(\":\");\n if (sep < 0) return null;\n return { username: decoded.slice(0, sep), password: decoded.slice(sep + 1) };\n}\n\n/** Build the {@link Principal} for a successfully authenticated user. */\nfunction principalFor(user: BasicAuthUser): Principal {\n return {\n id: user.id ?? user.username,\n name: user.username,\n ...(user.email !== undefined ? { email: user.email } : {}),\n ...(user.roles !== undefined ? { roles: user.roles } : {}),\n };\n}\n\n/**\n * Create an HTTP Basic {@link AuthProvider}.\n *\n * @example\n * ```ts\n * import { basicAuth, hashPassword } from \"@xtandard/audit/auth/basic\";\n *\n * const auth = basicAuth({\n * realm: \"Audit Admin\",\n * users: [\n * { username: \"admin\", passwordHash: await hashPassword(\"s3cret\"), roles: [\"admin\"] },\n * ],\n * });\n * ```\n */\nexport function basicAuth(options: BasicAuthOptions): AuthProvider {\n const realm = options.realm ?? \"xtandard-audit\";\n const usersByName = new Map<string, BasicAuthUser>();\n for (const user of options.users) usersByName.set(user.username, user);\n\n return {\n async authenticate(request: Request): Promise<Principal | null> {\n const creds = parseBasicHeader(request);\n if (!creds) return null;\n\n const user = usersByName.get(creds.username);\n if (!user) {\n // Run a dummy verification to keep timing roughly uniform for unknown\n // users versus known users.\n if (options.passwordVerifier) {\n await options.passwordVerifier(creds.username, creds.password);\n }\n return null;\n }\n\n // (a) custom verifier wins.\n if (options.passwordVerifier) {\n const ok = await options.passwordVerifier(creds.username, creds.password);\n return ok ? principalFor(user) : null;\n }\n\n // (b) scrypt hash.\n if (user.passwordHash !== undefined) {\n const ok = await verifyPassword(creds.password, user.passwordHash);\n return ok ? principalFor(user) : null;\n }\n\n // (c) dev-only plaintext.\n if (user.password !== undefined) {\n const ok = constantTimeEquals(creds.password, user.password);\n return ok ? principalFor(user) : null;\n }\n\n return null;\n },\n\n challenge(_request: Request): Response {\n return new Response(\"Unauthorized\", {\n status: 401,\n headers: { \"WWW-Authenticate\": `Basic realm=\"${realm}\"` },\n });\n },\n };\n}\n"],"mappings":";;;;;;;;;;;;;;;;;;;;;;;;;;;;;;;;;;AA8BA,MAAM,aAAa;;AAEnB,MAAM,cAAc;;AAEpB,MAAM,gBAAgB;AAEtB,MAAM,eAAe,UAAkB,MAAc,WACnD,IAAI,SAAS,SAAS,WAAW;CAC/B,OAAS,UAAU,MAAM,SAAS,KAAK,eAAe;EACpD,IAAI,KAAK,OAAO,GAAG;OACd,QAAQ,UAAU;CACzB,CAAC;AACH,CAAC;;AAGH,MAAM,SAAS,QAAwB,IAAI,SAAS,KAAK;;;;;;;;;;;;;;;AAgBzD,eAAsB,aAAa,UAAmC;CACpE,MAAM,OAAO,YAAY,WAAW;CACpC,MAAM,UAAU,MAAM,YAAY,UAAU,MAAM,UAAU;CAC5D,OAAO,GAAG,cAAc,GAAG,MAAM,IAAI,EAAE,GAAG,MAAM,OAAO;AACzD;;;;;;;;;AAUA,eAAsB,eAAe,UAAkB,QAAkC;CACvF,MAAM,QAAQ,OAAO,MAAM,GAAG;CAC9B,IAAI,MAAM,WAAW,KAAK,MAAM,OAAO,eAAe,OAAO;CAC7D,MAAM,UAAU,MAAM;CACtB,MAAM,UAAU,MAAM;CACtB,IAAI,CAAC,WAAW,CAAC,SAAS,OAAO;CAEjC,IAAI;CACJ,IAAI;CACJ,IAAI;EACF,OAAO,OAAO,KAAK,SAAS,KAAK;EACjC,WAAW,OAAO,KAAK,SAAS,KAAK;CACvC,QAAQ;EACN,OAAO;CACT;CACA,IAAI,KAAK,WAAW,KAAK,SAAS,WAAW,GAAG,OAAO;CAEvD,MAAM,UAAU,MAAM,YAAY,UAAU,MAAM,SAAS,MAAM;CACjE,IAAI,QAAQ,WAAW,SAAS,QAAQ,OAAO;CAC/C,OAAO,gBAAgB,SAAS,QAAQ;AAC1C;;AA0CA,SAAS,mBAAmB,GAAW,GAAoB;CACzD,MAAM,OAAO,OAAO,KAAK,GAAG,MAAM;CAClC,MAAM,OAAO,OAAO,KAAK,GAAG,MAAM;CAGlC,IAAI,KAAK,WAAW,KAAK,QAAQ;EAE/B,gBAAgB,MAAM,IAAI;EAC1B,OAAO;CACT;CACA,OAAO,gBAAgB,MAAM,IAAI;AACnC;;AASA,SAAS,iBAAiB,SAA2C;CACnE,MAAM,SAAS,QAAQ,QAAQ,IAAI,eAAe;CAClD,IAAI,CAAC,QAAQ,OAAO;CACpB,MAAM,CAAC,QAAQ,WAAW,OAAO,MAAM,KAAK,CAAC;CAC7C,IAAI,CAAC,UAAU,OAAO,YAAY,MAAM,WAAW,CAAC,SAAS,OAAO;CAEpE,IAAI;CACJ,IAAI;EACF,UAAU,OAAO,KAAK,SAAS,QAAQ,EAAE,SAAS,MAAM;CAC1D,QAAQ;EACN,OAAO;CACT;CACA,MAAM,MAAM,QAAQ,QAAQ,GAAG;CAC/B,IAAI,MAAM,GAAG,OAAO;CACpB,OAAO;EAAE,UAAU,QAAQ,MAAM,GAAG,GAAG;EAAG,UAAU,QAAQ,MAAM,MAAM,CAAC;CAAE;AAC7E;;AAGA,SAAS,aAAa,MAAgC;CACpD,OAAO;EACL,IAAI,KAAK,MAAM,KAAK;EACpB,MAAM,KAAK;EACX,GAAI,KAAK,UAAU,KAAA,IAAY,EAAE,OAAO,KAAK,MAAM,IAAI,CAAC;EACxD,GAAI,KAAK,UAAU,KAAA,IAAY,EAAE,OAAO,KAAK,MAAM,IAAI,CAAC;CAC1D;AACF;;;;;;;;;;;;;;;;AAiBA,SAAgB,UAAU,SAAyC;CACjE,MAAM,QAAQ,QAAQ,SAAS;CAC/B,MAAM,8BAAc,IAAI,IAA2B;CACnD,KAAK,MAAM,QAAQ,QAAQ,OAAO,YAAY,IAAI,KAAK,UAAU,IAAI;CAErE,OAAO;EACL,MAAM,aAAa,SAA6C;GAC9D,MAAM,QAAQ,iBAAiB,OAAO;GACtC,IAAI,CAAC,OAAO,OAAO;GAEnB,MAAM,OAAO,YAAY,IAAI,MAAM,QAAQ;GAC3C,IAAI,CAAC,MAAM;IAGT,IAAI,QAAQ,kBACV,MAAM,QAAQ,iBAAiB,MAAM,UAAU,MAAM,QAAQ;IAE/D,OAAO;GACT;GAGA,IAAI,QAAQ,kBAEV,OAAO,MADU,QAAQ,iBAAiB,MAAM,UAAU,MAAM,QAAQ,IAC5D,aAAa,IAAI,IAAI;GAInC,IAAI,KAAK,iBAAiB,KAAA,GAExB,OAAO,MADU,eAAe,MAAM,UAAU,KAAK,YAAY,IACrD,aAAa,IAAI,IAAI;GAInC,IAAI,KAAK,aAAa,KAAA,GAEpB,OADW,mBAAmB,MAAM,UAAU,KAAK,QAC3C,IAAI,aAAa,IAAI,IAAI;GAGnC,OAAO;EACT;EAEA,UAAU,UAA6B;GACrC,OAAO,IAAI,SAAS,gBAAgB;IAClC,QAAQ;IACR,SAAS,EAAE,oBAAoB,gBAAgB,MAAM,GAAG;GAC1D,CAAC;EACH;CACF;AACF"}
|