@moejay/pi-secure 0.1.0 → 0.1.4
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/README.md +28 -7
- package/RELEASING.md +147 -23
- package/SECURITY.md +1 -0
- package/index.ts +23 -7
- package/package.json +43 -10
package/README.md
CHANGED
|
@@ -4,25 +4,33 @@
|
|
|
4
4
|
|
|
5
5
|
Private secret entry, stdout capture, local reveal/copy, and redacted shell execution for [Pi](https://pi.dev). Transcript hygiene—not a sandbox or secret manager.
|
|
6
6
|
|
|
7
|
-
[Website](https://moejay.github.io/pi-secure/) · [Security](SECURITY.md) · [
|
|
7
|
+
[Website](https://moejay.github.io/pi-secure/) · [Security](SECURITY.md) · [Deployment & releases](RELEASING.md)
|
|
8
|
+
|
|
9
|
+
> **Not protection against a malicious or compromised model.** A model acting on a prompt injection can still use its tools to obtain or leak secrets. pi-secure reduces accidental transcript exposure; it does not prevent prompt injection or enforce secret isolation.
|
|
10
|
+
|
|
11
|
+
## Watch it work
|
|
12
|
+
|
|
13
|
+
[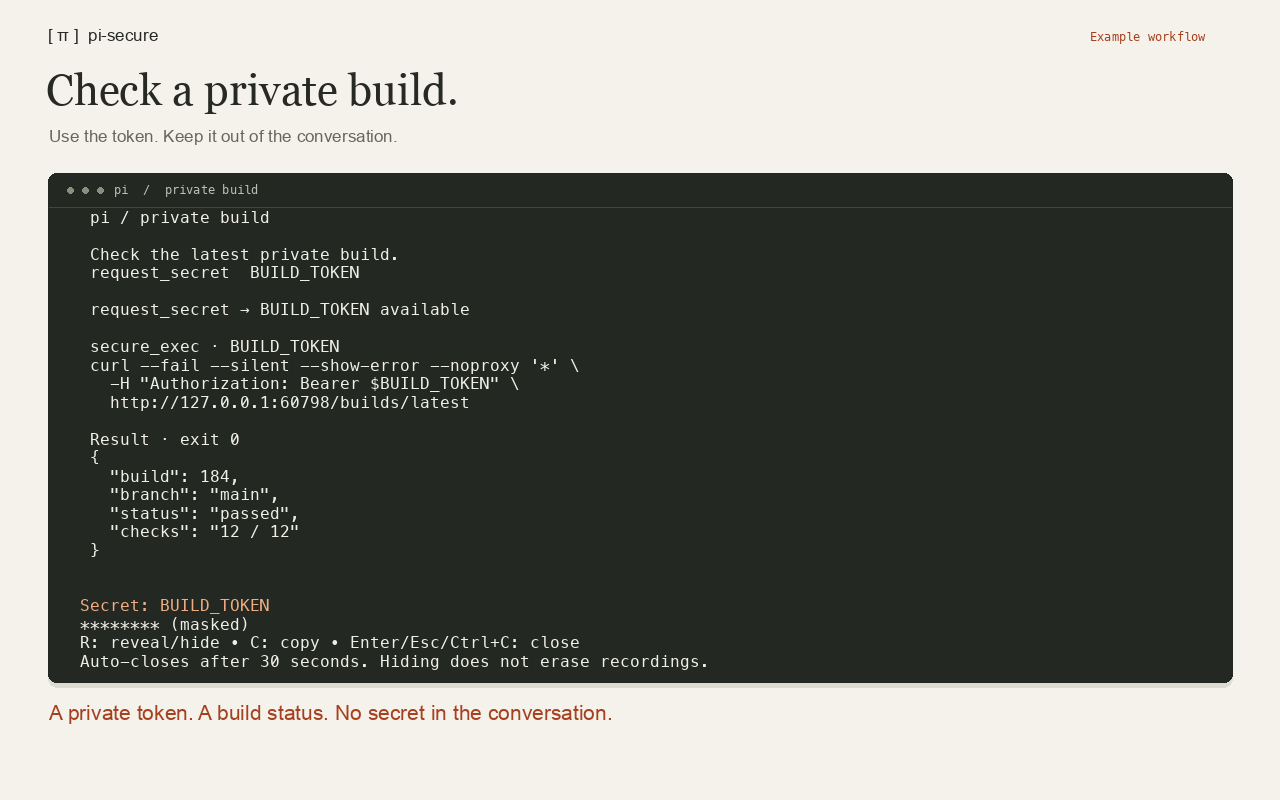](https://moejay.github.io/pi-secure/#watch-demo)
|
|
14
|
+
|
|
15
|
+
[Watch the walkthrough →](https://moejay.github.io/pi-secure/#watch-demo)
|
|
8
16
|
|
|
9
17
|
## Install
|
|
10
18
|
|
|
11
19
|
Requires Node.js 22.19+ and Pi 1.4+; interactive terminal mode is required for private entry and local reveal/copy. Shell execution supports macOS and Linux, not native Windows.
|
|
12
20
|
|
|
13
|
-
Install from
|
|
21
|
+
Install from npm:
|
|
14
22
|
|
|
15
23
|
```sh
|
|
16
|
-
pi install
|
|
24
|
+
pi install npm:@moejay/pi-secure
|
|
17
25
|
```
|
|
18
26
|
|
|
19
|
-
|
|
27
|
+
Or install from GitHub:
|
|
20
28
|
|
|
21
29
|
```sh
|
|
22
|
-
pi install
|
|
30
|
+
pi install git:github.com/moejay/pi-secure
|
|
23
31
|
```
|
|
24
32
|
|
|
25
|
-
|
|
33
|
+
**Fully restart Pi after installing or updating.** On affected Pi versions, `/reload` refreshes the TypeScript entry point but can retain cached `.mjs` helpers. A full restart loads a consistent version and clears in-memory secrets. If capture reports that no secret was stored, restart before retrying; do not use real credentials to diagnose it. For local development, use `pi -e ./index.ts` or `pi install /absolute/path/to/pi-secure`.
|
|
26
34
|
|
|
27
35
|
## Quick start
|
|
28
36
|
|
|
@@ -83,6 +91,8 @@ Output is buffered, then exact known secret values are redacted from stdout/stde
|
|
|
83
91
|
|
|
84
92
|
## Security boundary
|
|
85
93
|
|
|
94
|
+
**A malicious model—or one following a prompt injection—can still obtain or exfiltrate secrets.** For example, it could use a secret-bearing command to write a value to a file and read it with another tool, send it to an external destination, or transform it to evade exact-value redaction. There is no per-command approval or policy enforcement in `secure_exec`; confirmations on local reveal/copy do not protect other tool paths. Use only credentials and tasks you trust the agent to handle, preferably with external sandboxing, network restrictions, and least-privilege, short-lived tokens.
|
|
95
|
+
|
|
86
96
|
**Transcript hygiene, not a sandbox or secret manager.** Commands can use secrets arbitrarily for authorized tasks. There are no destination or file-access restrictions. Keep values out of chat: do not read secret-bearing files through ordinary tools, include values in messages, or encode them to bypass redaction. These are agent instructions, not enforced isolation. Other tools' output is not redacted.
|
|
87
97
|
|
|
88
98
|
Names, reasons, commands, availability, and redacted execution output are logged normally. Host extensions, process inspection, terminal input/debug recording, crash dumps, and the operating system are outside this protection. Only approve credentials for trusted tasks and destinations. Prefer short-lived, least-privilege tokens. Clear does not revoke credentials or erase copies held by running subprocesses.
|
|
@@ -95,7 +105,18 @@ npm run check
|
|
|
95
105
|
npm pack --dry-run --ignore-scripts
|
|
96
106
|
```
|
|
97
107
|
|
|
98
|
-
The package ships source directly, with no build step or runtime dependencies beyond Pi. CI checks Node 22 and 24. See [RELEASING.md](RELEASING.md) for the
|
|
108
|
+
The package ships source directly, with no build step or runtime dependencies beyond Pi. CI checks the minimum Node 22.19.0 plus current Node 22 and 24. See [RELEASING.md](RELEASING.md) for the manually approved OIDC publishing workflow and release checklist.
|
|
109
|
+
|
|
110
|
+
### Dependency maintenance
|
|
111
|
+
|
|
112
|
+
Dependabot checks weekly. GitHub Actions updates are grouped into one PR; routine compiler/type updates are grouped separately, while compiler major upgrades get explicit review. Keep `@types/node` on Node 22 to match the minimum supported runtime—upgrading CI tooling does not raise the package's runtime requirement. Actions remain SHA-pinned, and dependency PRs still require passing CI and maintainer review.
|
|
113
|
+
|
|
114
|
+
## Deployment and releases
|
|
115
|
+
|
|
116
|
+
- **Website:** merge changes under `docs/` through a PR; GitHub Pages deploys automatically from `main` with no build step.
|
|
117
|
+
- **npm:** bump the version in a PR, wait for CI, merge, then tag and manually dispatch `publish.yml` from `main`. The `npm` environment requires human approval; publishing uses OIDC and provenance, not a stored npm token.
|
|
118
|
+
|
|
119
|
+
See [RELEASING.md](RELEASING.md) for preview, deployment, release, verification, and recovery commands. Documentation-only website updates do not require an npm release; the npm README changes only when a new package version is published.
|
|
99
120
|
|
|
100
121
|
## License
|
|
101
122
|
|
package/RELEASING.md
CHANGED
|
@@ -1,32 +1,156 @@
|
|
|
1
|
-
#
|
|
1
|
+
# Deployment and releases
|
|
2
2
|
|
|
3
|
-
##
|
|
3
|
+
## What deploys where
|
|
4
4
|
|
|
5
|
-
|
|
5
|
+
| Target | Source | Trigger | Approval |
|
|
6
|
+
| --- | --- | --- | --- |
|
|
7
|
+
| [Website](https://moejay.github.io/pi-secure/) | Static files in `docs/` | Merge changes to `docs/**` or `pages.yml` into `main`; or manual Pages dispatch | Protected `github-pages` environment |
|
|
8
|
+
| [npm package](https://www.npmjs.com/package/@moejay/pi-secure) | Files allowed by `package.json` | Manual `publish.yml` dispatch from `main`, with an existing `vX.Y.Z` tag | Required human reviewer on `npm` environment |
|
|
9
|
+
| [GitHub release](https://github.com/moejay/pi-secure/releases) | Existing release tag and notes | Maintainer creates it after verifying npm | Maintainer |
|
|
6
10
|
|
|
7
|
-
-
|
|
8
|
-
- Repository: `moejay/pi-secure`
|
|
9
|
-
- Workflow: `publish.yml`
|
|
10
|
-
- GitHub environment: `npm`
|
|
11
|
+
The website has no build step. npm ships source directly. A website-only update needs no version bump or npm release. Changes to the README shipped on npm require a new npm version; existing versions cannot be overwritten.
|
|
11
12
|
|
|
12
|
-
|
|
13
|
+
Version 0.1.0 was bootstrapped manually with 2FA; 0.1.1 verified the GitHub OIDC release path and provenance. Subsequent releases should use CI, not local `npm publish`.
|
|
13
14
|
|
|
14
|
-
|
|
15
|
-
2. Run `npm ci --ignore-scripts && npm run check` and inspect `npm pack --dry-run --ignore-scripts`. Smoke-test the dialogs and native clipboard on your platform.
|
|
16
|
-
3. Bootstrap the package if npm requires it before trusted publisher configuration: use interactive `npm login` and `npm publish --access public` locally with 2FA. Do not give the agent a token or OTP. This first manual upload may not have provenance.
|
|
17
|
-
4. In npm package settings, configure GitHub Actions trusted publishing: owner `moejay`, repo `pi-secure`, workflow filename `publish.yml`, environment `npm`. Allow direct `npm publish` (staged-only permissions will not work with this workflow).
|
|
18
|
-
5. In GitHub, protect the `npm` environment with a required human reviewer; restrict its deployment branch to `main`. Protect main and release tags with rulesets. Require CI and review for workflow/code changes.
|
|
19
|
-
6. Set package publishing access to **Require two-factor authentication and disallow tokens**. Revoke obsolete publishing tokens. Do not add an npm token to Actions.
|
|
20
|
-
7. Set repository Actions variable `NPM_PUBLISH_ENABLED=true` only once the above is complete. Newly configured npm trust must be used within its documented expiry window (currently 2 days). If you bootstrapped 0.1.0, use a new version for the first OIDC release—npm versions cannot be overwritten.
|
|
15
|
+
## Prerequisites and protections
|
|
21
16
|
|
|
22
|
-
|
|
17
|
+
- Node.js 22.19+ and npm for local checks; authenticated `gh` and Git write access for PRs/tags.
|
|
18
|
+
- `main` requires a PR and passing `check (22)` / `check (24)` checks, including for admins. Force pushes and deletion are disabled. The current solo-maintainer setup requires zero independent PR approvals; the release environment still requires explicit human approval.
|
|
19
|
+
- `v*` release tags cannot be updated or deleted. Use a new version/tag to correct a release.
|
|
20
|
+
- npm trusted publisher: GitHub owner `moejay`, repository `pi-secure`, workflow filename `publish.yml`, environment `npm`, with direct `npm publish` allowed.
|
|
21
|
+
- The `npm` environment permits only the `main` deployment branch, requires reviewer `moejay`, and disables admin bypass. Self-review is permitted for the solo maintainer; an agent must leave this approval to the human.
|
|
22
|
+
- Repository Actions variable `NPM_PUBLISH_ENABLED` must be `true`. Disable it to stop future publish jobs. This does not stop an already-running job or revoke credentials.
|
|
23
|
+
- npm publishing access should require 2FA and disallow traditional tokens. No npm credential belongs in GitHub secrets, the repo, chat, or agent tool arguments.
|
|
23
24
|
|
|
24
|
-
1
|
|
25
|
-
2. Create and push the matching `vX.Y.Z` tag at the reviewed main commit.
|
|
26
|
-
3. Run **Publish npm** from main, supplying the existing tag.
|
|
27
|
-
4. Approve the `npm` environment deployment after reviewing the tag.
|
|
28
|
-
5. Verify npm version, tarball files, and provenance before creating a GitHub release.
|
|
25
|
+
CI uses GitHub-hosted Node 24 for publishing, npm >=11.5.1, SHA-pinned Actions, no dependency caching, and disabled install/publish lifecycle scripts. Tests and typechecks run explicitly before publishing. OIDC permission is scoped to the protected publish job. PRs, tag pushes, and GitHub releases do not trigger npm publishing.
|
|
29
26
|
|
|
30
|
-
|
|
27
|
+
## Website: preview and deploy
|
|
31
28
|
|
|
32
|
-
|
|
29
|
+
Start from up-to-date main and use a PR:
|
|
30
|
+
|
|
31
|
+
```sh
|
|
32
|
+
git switch main
|
|
33
|
+
git pull --ff-only
|
|
34
|
+
git switch -c docs/update-site
|
|
35
|
+
# Edit docs/, then preview:
|
|
36
|
+
python3 -m http.server 8080 --directory docs
|
|
37
|
+
```
|
|
38
|
+
|
|
39
|
+
Open http://localhost:8080. Check narrow/mobile and desktop layouts, keyboard navigation, links, and security wording. Stop the server with Ctrl+C, then:
|
|
40
|
+
|
|
41
|
+
```sh
|
|
42
|
+
npm ci --ignore-scripts
|
|
43
|
+
npm run check
|
|
44
|
+
git diff --check
|
|
45
|
+
git add docs/
|
|
46
|
+
git commit -m "docs: update website"
|
|
47
|
+
git push -u origin HEAD
|
|
48
|
+
gh pr create --repo moejay/pi-secure --base main --fill
|
|
49
|
+
```
|
|
50
|
+
|
|
51
|
+
Wait for CI, review and merge the PR. The **Pages** workflow uploads `docs/` and deploys it through the `github-pages` environment. Check the [Pages runs](https://github.com/moejay/pi-secure/actions/workflows/pages.yml) and the live site.
|
|
52
|
+
|
|
53
|
+
To redeploy current main without another commit:
|
|
54
|
+
|
|
55
|
+
```sh
|
|
56
|
+
gh workflow run pages.yml --repo moejay/pi-secure --ref main
|
|
57
|
+
```
|
|
58
|
+
|
|
59
|
+
Keep Pages configured to use **GitHub Actions**, not a branch/Jekyll build. README-only changes do not trigger Pages.
|
|
60
|
+
|
|
61
|
+
## Gallery previews and demo media
|
|
62
|
+
|
|
63
|
+
`package.json` uses `pi.image` and `pi.video` to give the Pi gallery public HTTPS preview URLs. The PNG, MP4, captions, and transcript are hosted under `docs/media/` on Pages, not bundled in the npm tarball. See [scripts/demo/README.md](https://github.com/moejay/pi-secure/blob/main/scripts/demo/README.md) for the isolated, scripted capture process.
|
|
64
|
+
|
|
65
|
+
When updating media:
|
|
66
|
+
|
|
67
|
+
1. Use only an obviously fake credential in an isolated session with no model calls or inherited authentication. Never record your normal terminal session or clipboard history.
|
|
68
|
+
2. Keep simulated clipboard behavior explicitly labeled; do not silently replace the user's clipboard while recording. Include the malicious-model/prompt-injection limitation.
|
|
69
|
+
3. Regenerate the thumbnail, captioned MP4, WebVTT captions, and text transcript together. Check readability, captions, and playback on mobile and desktop.
|
|
70
|
+
4. Merge the media changes and verify the public Pages URLs before publishing npm metadata that points to them. Preserve old URLs when renaming assets so existing package versions do not get broken previews.
|
|
71
|
+
5. A new npm version is needed for updated `pi.image` / `pi.video` metadata or the packaged README. Gallery indexing can lag behind npm; verify the published manifest instead of repeatedly republishing.
|
|
72
|
+
|
|
73
|
+
## npm: prepare a release PR
|
|
74
|
+
|
|
75
|
+
Use a release branch. The example uses a patch increment; choose minor/major deliberately for feature/breaking changes.
|
|
76
|
+
|
|
77
|
+
```sh
|
|
78
|
+
git switch main
|
|
79
|
+
git pull --ff-only
|
|
80
|
+
git switch -c release/next
|
|
81
|
+
npm ci --ignore-scripts
|
|
82
|
+
npm version patch --no-git-tag-version --ignore-scripts
|
|
83
|
+
# Update documentation/release notes as needed.
|
|
84
|
+
npm run check
|
|
85
|
+
npm pack --dry-run --ignore-scripts
|
|
86
|
+
git diff --check
|
|
87
|
+
git add package.json package-lock.json
|
|
88
|
+
# Explicitly stage any documentation changes too.
|
|
89
|
+
git commit -m "chore: prepare release"
|
|
90
|
+
git push -u origin HEAD
|
|
91
|
+
gh pr create --repo moejay/pi-secure --base main --fill
|
|
92
|
+
```
|
|
93
|
+
|
|
94
|
+
Inspect the tarball allowlist: only the intended source, package metadata, license, README, security policy, and release guide should ship. Do not include credentials or local configuration. Fully restart Pi after helper changes or upgrades; on affected Pi versions `/reload` can retain cached native `.mjs` imports. Smoke-test `capture_secret` → `show_secret` with a disposable value (capture must return only name/availability), then masked entry, cancellation, reveal/hide, and native clipboard copy both masked and visible on a supported platform; automated clipboard tests mock native utilities.
|
|
95
|
+
|
|
96
|
+
Review the PR and wait for both Node 22/24 CI checks before merging. Do not bypass branch protections.
|
|
97
|
+
|
|
98
|
+
## npm: tag, dispatch, and approve
|
|
99
|
+
|
|
100
|
+
After the release PR is merged, use the merged main commit, not the release branch's pre-merge commit:
|
|
101
|
+
|
|
102
|
+
```sh
|
|
103
|
+
git switch main
|
|
104
|
+
git pull --ff-only
|
|
105
|
+
VERSION=$(node -p "JSON.parse(require('fs').readFileSync('package.json', 'utf8')).version")
|
|
106
|
+
git tag -a "v$VERSION" -m "pi-secure $VERSION"
|
|
107
|
+
git push origin "v$VERSION"
|
|
108
|
+
gh workflow run publish.yml --repo moejay/pi-secure --ref main -f "tag=v$VERSION"
|
|
109
|
+
gh run list --repo moejay/pi-secure --workflow publish.yml --limit 5
|
|
110
|
+
```
|
|
111
|
+
|
|
112
|
+
The workflow requires a stable `vX.Y.Z` tag, checks that its commit is an ancestor of main, and checks the package name/version. It checks out the tagged source, runs checks, and publishes through OIDC with provenance.
|
|
113
|
+
|
|
114
|
+
Open the new run in GitHub. The human maintainer must select **Review deployments → npm → Approve and deploy**, after checking the tag and commit. Do not approve a release merely because a model requests it. No OTP or npm token should be supplied to CI.
|
|
115
|
+
|
|
116
|
+
## Verify before announcing
|
|
117
|
+
|
|
118
|
+
Once the run succeeds, npm may take several minutes to expose the package. A temporary 404 is not a reason to republish or reuse the version.
|
|
119
|
+
|
|
120
|
+
```sh
|
|
121
|
+
# VERSION is the version just released, set in the previous step.
|
|
122
|
+
npm view "@moejay/pi-secure@$VERSION" version dist --prefer-online --json
|
|
123
|
+
```
|
|
124
|
+
|
|
125
|
+
Check `dist.attestations` for SLSA provenance. Verify the registry signature and provenance in an isolated temporary install, without running lifecycle scripts or installing Pi peers:
|
|
126
|
+
|
|
127
|
+
```sh
|
|
128
|
+
VERIFY_DIR=$(mktemp -d)
|
|
129
|
+
printf '{"name":"pi-secure-verification","version":"1.0.0","private":true}\n' > "$VERIFY_DIR/package.json"
|
|
130
|
+
npm install --prefix "$VERIFY_DIR" --cache "$VERIFY_DIR/cache" \
|
|
131
|
+
--prefer-online --ignore-scripts --legacy-peer-deps --no-audit --no-fund \
|
|
132
|
+
"@moejay/pi-secure@$VERSION"
|
|
133
|
+
npm audit signatures --prefix "$VERIFY_DIR" --cache "$VERIFY_DIR/cache"
|
|
134
|
+
# Inspect the installed files and package.json in $VERIFY_DIR/node_modules/@moejay/pi-secure.
|
|
135
|
+
```
|
|
136
|
+
|
|
137
|
+
Expect a verified registry signature and verified attestation. Check that provenance identifies `moejay/pi-secure`, the intended source commit, and the publishing workflow. Inspect the tarball contents and compare its integrity hash with registry metadata. Then create release notes:
|
|
138
|
+
|
|
139
|
+
```sh
|
|
140
|
+
gh release create "v$VERSION" --repo moejay/pi-secure --verify-tag \
|
|
141
|
+
--title "v$VERSION" --notes-file /path/to/reviewed-release-notes.md
|
|
142
|
+
```
|
|
143
|
+
|
|
144
|
+
Do not claim security isolation: pi-secure does not stop a malicious or prompt-injected model from obtaining or leaking secrets. Keep this boundary explicit in release notes when describing security behavior.
|
|
145
|
+
|
|
146
|
+
## Failure and recovery
|
|
147
|
+
|
|
148
|
+
- **Skipped job:** confirm dispatch was from `main` and `NPM_PUBLISH_ENABLED=true`.
|
|
149
|
+
- **Waiting:** the human reviewer must approve the `npm` environment deployment.
|
|
150
|
+
- **OIDC authentication failure:** verify exact, case-sensitive trusted-publisher fields above, direct publish permission, environment name, and repository URL in `package.json`. Do not work around it by adding a token. Newly configured npm trust can expire before its first successful publish; see current npm documentation.
|
|
151
|
+
- **Publish step failed:** check npm first. If the version is absent and npm did not accept it, fix the underlying issue and rerun the reviewed workflow with a fresh human approval. If it already exists, verify it instead of republishing.
|
|
152
|
+
- **Bad published release:** never move/delete a release tag or overwrite an npm version. Fix forward with a new patch release. For an actual secret exposure, revoke affected credentials first; deleting a release does not erase copies.
|
|
153
|
+
- **Bad website deployment:** revert the site change through a PR and let Pages redeploy. This does not affect the npm package.
|
|
154
|
+
- **Stop publishing:** set `NPM_PUBLISH_ENABLED=false` and cancel any active publish run separately. Remove npm trust if compromised, revoke affected credentials, and review tags/workflows before re-enabling.
|
|
155
|
+
|
|
156
|
+
Trusted-publishing reference: https://docs.npmjs.com/trusted-publishers/
|
package/SECURITY.md
CHANGED
|
@@ -10,6 +10,7 @@ Only the latest release receives fixes. Use short-lived, least-privilege credent
|
|
|
10
10
|
|
|
11
11
|
## Important limits
|
|
12
12
|
|
|
13
|
+
- A malicious or prompt-injected model can still obtain or exfiltrate secrets through its tools. pi-secure does not prevent prompt injection or enforce secret isolation; local reveal/copy confirmations do not secure other tool paths.
|
|
13
14
|
- Shell commands can transmit or persist secrets; approve only trusted tasks.
|
|
14
15
|
- Exact-value output redaction does not cover transformed, encoded, partial, or already-logged values, or other tools' output.
|
|
15
16
|
- Terminal recording, input logging, clipboard managers/sync, process inspection, crash dumps, and other extensions are outside the boundary.
|
package/index.ts
CHANGED
|
@@ -207,14 +207,30 @@ export default function (pi: ExtensionAPI) {
|
|
|
207
207
|
timeout: Type.Optional(Type.Integer({ minimum: 1, maximum: 300 })),
|
|
208
208
|
}),
|
|
209
209
|
async execute(_id, params, signal, _update, ctx) {
|
|
210
|
+
if (!validName(params.name) || vault.has(params.name)) {
|
|
211
|
+
return { ...reply({ available: false, error: "Capture name is invalid or already exists. Choose a new name." }), isError: true };
|
|
212
|
+
}
|
|
210
213
|
const lifetime = lifecycle;
|
|
211
|
-
|
|
212
|
-
|
|
213
|
-
|
|
214
|
-
|
|
215
|
-
|
|
216
|
-
|
|
217
|
-
|
|
214
|
+
let result: Awaited<ReturnType<typeof secureExec>>;
|
|
215
|
+
try {
|
|
216
|
+
result = await secureExec({
|
|
217
|
+
isCurrent: () => lifecycle === lifetime && !lifetime.signal.aborted,
|
|
218
|
+
command: params.command, names: params.secrets ?? [], vault, cwd: ctx.cwd,
|
|
219
|
+
signal: operationSignal(signal), timeout: (params.timeout ?? 60) * 1000,
|
|
220
|
+
captureName: params.name, trimNewline: params.trimNewline ?? true,
|
|
221
|
+
});
|
|
222
|
+
} catch {
|
|
223
|
+
return { ...reply({ name: params.name, available: false, error: "Secret capture failed; output discarded." }), isError: true };
|
|
224
|
+
}
|
|
225
|
+
// Never forward helper results from capture mode. A stale native ESM
|
|
226
|
+
// helper can survive Pi reload and return ordinary execution output.
|
|
227
|
+
if (result.error || result.available !== true || result.name !== params.name || !vault.has(params.name)) {
|
|
228
|
+
const error = result.error
|
|
229
|
+
? "Secret capture failed; output discarded."
|
|
230
|
+
: "Capture did not store a secret. Fully restart Pi before retrying.";
|
|
231
|
+
return { ...reply({ name: params.name, available: false, error }), isError: true };
|
|
232
|
+
}
|
|
233
|
+
return reply({ name: params.name, available: true });
|
|
218
234
|
},
|
|
219
235
|
}));
|
|
220
236
|
|
package/package.json
CHANGED
|
@@ -1,18 +1,51 @@
|
|
|
1
1
|
{
|
|
2
2
|
"name": "@moejay/pi-secure",
|
|
3
|
-
"version": "0.1.
|
|
3
|
+
"version": "0.1.4",
|
|
4
4
|
"type": "module",
|
|
5
|
-
"description": "
|
|
6
|
-
"keywords": [
|
|
5
|
+
"description": "Private secret entry, capture, local reveal/copy, and redacted shell execution for Pi. Transcript hygiene, not a sandbox.",
|
|
6
|
+
"keywords": [
|
|
7
|
+
"pi-package",
|
|
8
|
+
"pi-extension",
|
|
9
|
+
"secrets",
|
|
10
|
+
"security",
|
|
11
|
+
"privacy",
|
|
12
|
+
"credentials",
|
|
13
|
+
"clipboard",
|
|
14
|
+
"developer-tools"
|
|
15
|
+
],
|
|
7
16
|
"license": "MIT",
|
|
8
17
|
"author": "moejay",
|
|
9
|
-
"repository": {
|
|
18
|
+
"repository": {
|
|
19
|
+
"type": "git",
|
|
20
|
+
"url": "git+https://github.com/moejay/pi-secure.git"
|
|
21
|
+
},
|
|
10
22
|
"homepage": "https://moejay.github.io/pi-secure/",
|
|
11
|
-
"bugs": {
|
|
12
|
-
|
|
13
|
-
|
|
14
|
-
"
|
|
15
|
-
|
|
23
|
+
"bugs": {
|
|
24
|
+
"url": "https://github.com/moejay/pi-secure/issues"
|
|
25
|
+
},
|
|
26
|
+
"engines": {
|
|
27
|
+
"node": ">=22.19.0"
|
|
28
|
+
},
|
|
29
|
+
"publishConfig": {
|
|
30
|
+
"access": "public",
|
|
31
|
+
"registry": "https://registry.npmjs.org/"
|
|
32
|
+
},
|
|
33
|
+
"files": [
|
|
34
|
+
"index.ts",
|
|
35
|
+
"secure.mjs",
|
|
36
|
+
"clipboard.mjs",
|
|
37
|
+
"README.md",
|
|
38
|
+
"SECURITY.md",
|
|
39
|
+
"RELEASING.md",
|
|
40
|
+
"LICENSE"
|
|
41
|
+
],
|
|
42
|
+
"pi": {
|
|
43
|
+
"extensions": [
|
|
44
|
+
"./index.ts"
|
|
45
|
+
],
|
|
46
|
+
"image": "https://moejay.github.io/pi-secure/media/preview.png",
|
|
47
|
+
"video": "https://moejay.github.io/pi-secure/media/demo.mp4"
|
|
48
|
+
},
|
|
16
49
|
"scripts": {
|
|
17
50
|
"test": "node --test",
|
|
18
51
|
"typecheck": "tsc --noEmit",
|
|
@@ -24,7 +57,7 @@
|
|
|
24
57
|
"@earendil-works/pi-coding-agent": "1.4.0",
|
|
25
58
|
"@earendil-works/pi-tui": "1.4.0",
|
|
26
59
|
"@types/node": "22.20.5",
|
|
27
|
-
"typescript": "
|
|
60
|
+
"typescript": "7.0.2"
|
|
28
61
|
},
|
|
29
62
|
"peerDependencies": {
|
|
30
63
|
"@earendil-works/pi-ai": "*",
|