@cassiomc1/forgeloop 2.0.0-rc.4 → 2.0.0
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- package/CONTRIBUTING.md +3 -1
- package/DOCS_INDEX.md +3 -0
- package/ENG/accessibility-eng.md +6 -6
- package/ENG/clean-code-eng.md +2 -2
- package/ENG/design-code-eng.md +13 -13
- package/ENG/documentation-quality-eng.md +10 -2
- package/ENG/flutter-development-eng.md +38 -59
- package/ENG/games-code-design-web-eng.md +2 -2
- package/ENG/perf-code-eng.md +3 -3
- package/ENG/php-development-eng.md +2 -2
- package/ENG/premium-sites-studio-eng.md +9 -2
- package/ENG/python-development-eng.md +7 -1
- package/ENG/rust-development-eng.md +22 -32
- package/ENG/sec-code-eng.md +19 -3
- package/ENG/taste-frontend-eng.md +108 -1
- package/ENG/test-code-eng.md +2 -2
- package/GUIDE_ROUTER.md +18 -4
- package/README.md +24 -20
- package/THIRD_PARTY_NOTICES.md +59 -6
- package/docs/AGENT_PROTOCOL_SUMMARY.md +1 -1
- package/docs/AGENT_SKILL.md +31 -0
- package/docs/DOCUMENTATION_GUIDE.md +6 -0
- package/docs/FORGELOOP_AUDIT.md +71 -0
- package/docs/GETTING_STARTED.md +6 -0
- package/docs/GUIDE_MAINTENANCE.md +106 -0
- package/docs/OPENSRC_ADAPTER.md +1 -1
- package/docs/PACKAGE_CONTENTS.md +25 -2
- package/docs/RELEASE_CHECKLIST.md +79 -20
- package/docs/REVENUE_CENTRIC_DESIGN.md +69 -0
- package/docs/SECURITY_AUDIT_SKILL.md +131 -0
- package/docs/SECURITY_REVIEW.md +6 -0
- package/docs/STABLE_2_ACCEPTANCE.md +80 -0
- package/docs/TROUBLESHOOTING.md +15 -2
- package/docs/documentation-manifest.json +255 -0
- package/package.json +14 -4
- package/scripts/generate-forgeloop-skill.mjs +14 -0
- package/scripts/verify-revenue-design-skill.mjs +37 -0
- package/scripts/verify-security-audit-skill.mjs +68 -0
- package/skills/forgeloop/SKILL.md +14 -0
- package/skills/forgeloop/references/revenue-centric-design/LICENSE +30 -0
- package/skills/forgeloop/references/revenue-centric-design/PIN.json +14 -0
- package/skills/forgeloop/references/revenue-centric-design/SKILL.md +64 -0
- package/skills/forgeloop/references/revenue-centric-design/references/playbook.md +36 -0
- package/skills/security-audit/AI-AND-LLM.md +83 -0
- package/skills/security-audit/ATTACK-CLASSES.md +130 -0
- package/skills/security-audit/CLIENT-SIDE.md +83 -0
- package/skills/security-audit/CLOUD-AND-DEPLOYMENT.md +86 -0
- package/skills/security-audit/DATA-ISOLATION-AND-LIFECYCLE.md +84 -0
- package/skills/security-audit/DESKTOP-MOBILE-AND-LOCAL-IPC.md +89 -0
- package/skills/security-audit/HUNTING.md +251 -0
- package/skills/security-audit/LICENSE +21 -0
- package/skills/security-audit/MEMORY-SAFETY-AND-BINARY.md +101 -0
- package/skills/security-audit/PIN.json +30 -0
- package/skills/security-audit/PROTOCOLS-RPC-AND-MESSAGING.md +81 -0
- package/skills/security-audit/RECONNAISSANCE.md +156 -0
- package/skills/security-audit/RESOURCE-EXHAUSTION-AND-AVAILABILITY.md +78 -0
- package/skills/security-audit/SKILL.md +192 -0
- package/skills/security-audit/SUPPLY-CHAIN-AND-RELEASE.md +73 -0
- package/skills/security-audit/VALIDATION-AND-REPORTING.md +186 -0
- package/skills/security-audit/WEB-PROTOCOL-AND-AUTH.md +105 -0
- package/skills/security-audit/report-schema.json +461 -0
- package/skills/security-audit/validate-coverage-ledger.cjs +872 -0
- package/skills/security-audit/validate-coverage-ledger.test.cjs +740 -0
- package/skills/security-audit/validate-findings.cjs +773 -0
- package/skills/security-audit/validate-findings.test.cjs +652 -0
- package/src/core/completion-artifacts.js +4 -7
- package/src/core/diagnosis.js +3 -5
- package/src/core/diagnostic-record.js +4 -4
- package/src/core/next-action-recovery-phases.js +3 -0
- package/src/core/next-action-review-correction.js +26 -0
- package/src/core/next-action-review-phase.js +11 -10
- package/src/core/reconcile-closure.js +5 -0
- package/src/core/review-correction.js +51 -0
- package/src/storage/capabilities.js +1 -1
|
@@ -3,7 +3,7 @@ name: taste-frontend-eng
|
|
|
3
3
|
language: en
|
|
4
4
|
description: "Contextual visual-taste review for premium frontend and brand-heavy work."
|
|
5
5
|
version: "2026.09"
|
|
6
|
-
last-reviewed: "2026-
|
|
6
|
+
last-reviewed: "2026-10-16"
|
|
7
7
|
guide-id: taste
|
|
8
8
|
---
|
|
9
9
|
|
|
@@ -20,6 +20,25 @@ approach. ForgeLoop keeps the useful review vocabulary while applying its own
|
|
|
20
20
|
protocol boundaries: user evidence, accessibility, performance, security, and
|
|
21
21
|
the active product constraints have priority over aesthetic preference.
|
|
22
22
|
|
|
23
|
+
## Upstream Baseline and Intentional Differences
|
|
24
|
+
|
|
25
|
+
Reviewed baseline: [Taste Skill v2.0.0](https://github.com/Leonxlnx/taste-skill/tree/v2.0.0/skills/taste-skill),
|
|
26
|
+
released 2026-10-13 and reviewed for this adaptation on 2026-10-16. See the
|
|
27
|
+
[versioned instructions](https://github.com/Leonxlnx/taste-skill/blob/v2.0.0/skills/taste-skill/SKILL.md)
|
|
28
|
+
and [changelog](https://github.com/Leonxlnx/taste-skill/blob/v2.0.0/CHANGELOG.md).
|
|
29
|
+
This identifies the upstream reference, not full feature parity or automatic
|
|
30
|
+
synchronization. The guide's frontmatter version follows ForgeLoop's guide
|
|
31
|
+
versioning separately.
|
|
32
|
+
|
|
33
|
+
ForgeLoop adapts the content inventory, subject-specific concept, and screenshot
|
|
34
|
+
correction practices. It deliberately keeps direction selection contextual
|
|
35
|
+
rather than requiring a scripted draw. It does not adopt universal bans on
|
|
36
|
+
colors, gradients, borders, fonts, or headline line counts, or minimum image
|
|
37
|
+
and animated-element counts. Existing brand constraints, language expansion,
|
|
38
|
+
content needs, reduced motion, accessibility, and performance determine those
|
|
39
|
+
choices. An aesthetic preference never becomes lifecycle or completion
|
|
40
|
+
authority.
|
|
41
|
+
|
|
23
42
|
## Design Read
|
|
24
43
|
|
|
25
44
|
Before editing, describe the existing or proposed system in observable terms:
|
|
@@ -35,6 +54,39 @@ Before editing, describe the existing or proposed system in observable terms:
|
|
|
35
54
|
Separate observed evidence from inference. If the implementation is not yet
|
|
36
55
|
available, record the read as a hypothesis and keep it reversible.
|
|
37
56
|
|
|
57
|
+
## Client Content Inventory
|
|
58
|
+
|
|
59
|
+
Collect a small, source-backed inventory before choosing a visual direction:
|
|
60
|
+
|
|
61
|
+
- the client's actual product, audience, vocabulary, location, materials, and
|
|
62
|
+
distinguishing constraints, where relevant and supported;
|
|
63
|
+
- available product views, photographs, illustrations, documents, and brand
|
|
64
|
+
assets, with their source and permitted use;
|
|
65
|
+
- the content each requested section must deliver and the evidence supporting
|
|
66
|
+
its claims;
|
|
67
|
+
- missing content, representative examples, and facts requiring confirmation.
|
|
68
|
+
|
|
69
|
+
Reuse the inventory from the premium website brief when it exists. Do not
|
|
70
|
+
invent a differentiator, price, metric, testimonial, customer, or asset to make
|
|
71
|
+
the direction work. Label representative content and keep unsupported proof
|
|
72
|
+
out of release claims. For each section, connect the visitor's question, the
|
|
73
|
+
proposed claim, and its supporting source before committing to a layout.
|
|
74
|
+
|
|
75
|
+
## Visual Concept
|
|
76
|
+
|
|
77
|
+
Write one sentence connecting an evidenced client detail to a concrete visual
|
|
78
|
+
decision and the visitor's goal. For example, an existing product workflow can
|
|
79
|
+
organize the page's composition and sequence. Explain how that decision
|
|
80
|
+
extends beyond the hero into supporting sections and narrow layouts.
|
|
81
|
+
|
|
82
|
+
Check whether the sentence would fit a nearby competitor unchanged. If it
|
|
83
|
+
would, refine it using the inventory rather than inventing a distinction.
|
|
84
|
+
Keep an established brand or design system when appropriate. Add a distinctive
|
|
85
|
+
interaction only when it serves the authorized scope and has an accessible
|
|
86
|
+
fallback; a new interaction is not required merely to make the page unusual.
|
|
87
|
+
Record reversible choices in the existing design artifact or contract
|
|
88
|
+
assumptions, following the normal decision policy.
|
|
89
|
+
|
|
38
90
|
## Design Dials
|
|
39
91
|
|
|
40
92
|
Use three lightweight dials to make an intentional decision rather than a
|
|
@@ -130,6 +182,61 @@ If visual evidence is unavailable, record `NOT_VERIFIED` or a bounded
|
|
|
130
182
|
limitation. Never turn an imagined screenshot or an unrun browser check into
|
|
131
183
|
an observed result.
|
|
132
184
|
|
|
185
|
+
## Screenshot Review
|
|
186
|
+
|
|
187
|
+
Use an already available, authorized browser to capture and inspect the real
|
|
188
|
+
page. A useful starting set is 1440, 768, and 390 CSS pixels wide; adapt it to
|
|
189
|
+
the supported device matrix and include required reflow, zoom, and interaction
|
|
190
|
+
checks. These widths do not replace accessibility requirements.
|
|
191
|
+
|
|
192
|
+
1. Record the tested URL or build, browser, viewport dimensions, relevant
|
|
193
|
+
state, and screenshot references in the task's evidence.
|
|
194
|
+
2. Inspect each capture for hierarchy, content completeness, concept continuity,
|
|
195
|
+
typography, contrast, crops, overflow, and obscured or missing content.
|
|
196
|
+
Check interactive behavior separately; a screenshot alone cannot establish
|
|
197
|
+
keyboard access, form behavior, or runtime performance.
|
|
198
|
+
3. Identify up to three actionable problems with their location, visible
|
|
199
|
+
evidence, and user impact. Prioritize required acceptance criteria over
|
|
200
|
+
stylistic preferences.
|
|
201
|
+
4. Correct the scoped issues through the existing ForgeLoop diagnosis and
|
|
202
|
+
correction loop when verification fails. Re-run affected checks, capture
|
|
203
|
+
the changed states, and inspect them again.
|
|
204
|
+
|
|
205
|
+
Use at most three review rounds by default, within the task contract's limits.
|
|
206
|
+
Stop earlier when the applicable criteria are satisfied. The round limit does
|
|
207
|
+
not waive a failure: report unresolved issues and their verification status,
|
|
208
|
+
then follow the canonical next action or blocker. Do not fabricate aesthetic
|
|
209
|
+
scores or claim browser, inspector, or screenshot evidence that was not
|
|
210
|
+
actually obtained. This procedure adds no separate approval gate.
|
|
211
|
+
|
|
212
|
+
## Optional Upstream Tools
|
|
213
|
+
|
|
214
|
+
The upstream v2 scripts, direction library, and reference collection are not
|
|
215
|
+
bundled with this guide or required by ForgeLoop runtime:
|
|
216
|
+
|
|
217
|
+
| Upstream tool | Optional purpose |
|
|
218
|
+
| --- | --- |
|
|
219
|
+
| `scripts/draw.mjs` | Propose directions and composition blueprints |
|
|
220
|
+
| `scripts/lint.mjs` | Review source against upstream style patterns |
|
|
221
|
+
| `scripts/inspect.mjs` | Measure a page in a browser and capture screenshots |
|
|
222
|
+
| `scripts/assets.mjs` | Find external media and record source and credit information |
|
|
223
|
+
|
|
224
|
+
Use a separately available, reviewed copy only when appropriate and authorized;
|
|
225
|
+
do not install, fetch, or execute it automatically. The reviewed inspector
|
|
226
|
+
requires Node 22+ and an installed Chrome, Edge, or Chromium; the other scripts
|
|
227
|
+
require Node 18+, and media discovery requires network access. Check the
|
|
228
|
+
selected copy's requirements and output paths before use. Upstream tools may
|
|
229
|
+
write project artifacts and user-level history outside ForgeLoop's evidence
|
|
230
|
+
store; those files do not become attested evidence merely by existing.
|
|
231
|
+
|
|
232
|
+
Prefer an available equivalent when it supports the same task checks. Treat
|
|
233
|
+
upstream style findings as contextual recommendations, not new ForgeLoop gates.
|
|
234
|
+
For external media, confirm the exact asset's license, attribution, and
|
|
235
|
+
relevance; search results alone do not establish reuse rights. Identify found
|
|
236
|
+
or generated imagery honestly rather than presenting it as the client's own.
|
|
237
|
+
Record the tool version and checks actually run, and mark unavailable required
|
|
238
|
+
evidence `NOT_VERIFIED` without claiming upstream tool coverage.
|
|
239
|
+
|
|
133
240
|
## Redesign Audit
|
|
134
241
|
|
|
135
242
|
For an existing interface, scan first and classify each issue as hierarchy,
|
package/ENG/test-code-eng.md
CHANGED
|
@@ -3,7 +3,7 @@ name: test-code-eng
|
|
|
3
3
|
language: en
|
|
4
4
|
description: "Risk-based testing strategy and tools for modern languages and platforms."
|
|
5
5
|
version: "2026.09"
|
|
6
|
-
last-reviewed: "2026-
|
|
6
|
+
last-reviewed: "2026-10-17"
|
|
7
7
|
guide-id: test
|
|
8
8
|
completion-evidence:
|
|
9
9
|
- tests
|
|
@@ -15,7 +15,7 @@ completion-evidence:
|
|
|
15
15
|
|
|
16
16
|
**Related documents**: for general clean code principles (names, small functions, formatting), see [`clean-code-eng.md`](./clean-code-eng.md). For security, including SAST/DAST, see [`sec-code-eng.md`](./sec-code-eng.md). For accessibility, use the repository's specific guide together with [WCAG 2.2](https://www.w3.org/TR/WCAG22/). For HTML video and motion, see [HyperFrames](https://hyperframes.heygen.com). This file is the canonical reference for deciding the testing strategy by language and platform.
|
|
17
17
|
|
|
18
|
-
**Tooling policy**: identify the stack, the stage, and the applicable checks; prefer an already available equivalent that produces compatible evidence.
|
|
18
|
+
**Tooling policy**: identify the stack, the stage, and the applicable checks; prefer an already available equivalent that produces compatible evidence. Installation or environment changes require authority; reuse scoped authorization already given rather than asking again. If no safe equivalent exists, record the required check as blocked and never claim that it passed. Do not install merely optional resources.
|
|
19
19
|
|
|
20
20
|
## Start with risk, not a tool
|
|
21
21
|
|
package/GUIDE_ROUTER.md
CHANGED
|
@@ -73,6 +73,10 @@ structural detection and route tests are implemented.
|
|
|
73
73
|
|
|
74
74
|
## Domain rules
|
|
75
75
|
|
|
76
|
+
For catalog upkeep, use the [engineering guide maintenance map](https://github.com/cassiomc1/forgeloop/blob/b9a16e9f665116306e9fca3b905b1f0fe2abd633/docs/GUIDE_MAINTENANCE.md).
|
|
77
|
+
It distinguishes guide discovery, implemented routing, contextual defaults,
|
|
78
|
+
and observed verification; it does not add runtime routing rules.
|
|
79
|
+
|
|
76
80
|
### `clean` — code and structure
|
|
77
81
|
|
|
78
82
|
**Activate when:** creating or modifying code, fixing a bug, refactoring, changing architecture, reviewing quality, or producing development instructions.
|
|
@@ -117,6 +121,12 @@ rg -n '^## |authentication|authorization|upload|SSRF|CSP|OAuth|JWT|secrets|suppl
|
|
|
117
121
|
|
|
118
122
|
**Expected evidence:** explicit trust boundaries, server-side validation, least privilege, no secrets in Git, and negative tests.
|
|
119
123
|
|
|
124
|
+
For requested source audits or focused vulnerability investigations, consult
|
|
125
|
+
the optional bundled Cloudflare `security-audit` companion described by the
|
|
126
|
+
security guide. Ordinary security routing does not start a full audit or
|
|
127
|
+
require the companion. Its reports remain advisory; canonical security gates
|
|
128
|
+
and verification remain unchanged.
|
|
129
|
+
|
|
120
130
|
### `performance` — measurable cost
|
|
121
131
|
|
|
122
132
|
**Activate when:** the request involves latency, scale, a critical path, rendering, bundles, databases, networking, memory, battery, load, Web Vitals, FPS, or a budget.
|
|
@@ -188,12 +198,16 @@ require GSAP or a static-site approach, prescribe fonts/layouts, or override
|
|
|
188
198
|
accessibility, performance, security, or product evidence.
|
|
189
199
|
|
|
190
200
|
```bash
|
|
191
|
-
rg -n '^## (Design Read|Design Dials|Anti-Slop Checks|Typography Quality|Layout Composition|Motion Restraint|Responsive Composition|Design-System Selection|Visual Pre-Flight|Redesign Audit)' ENG/taste-frontend-eng.md
|
|
201
|
+
rg -n '^## (Upstream Baseline and Intentional Differences|Design Read|Client Content Inventory|Visual Concept|Design Dials|Anti-Slop Checks|Typography Quality|Layout Composition|Motion Restraint|Responsive Composition|Design-System Selection|Visual Pre-Flight|Screenshot Review|Optional Upstream Tools|Redesign Audit)' ENG/taste-frontend-eng.md
|
|
192
202
|
```
|
|
193
203
|
|
|
194
|
-
**Expected evidence:** a contextual design read,
|
|
195
|
-
anti-slop review, and
|
|
196
|
-
|
|
204
|
+
**Expected evidence:** a source-backed client inventory, contextual design read,
|
|
205
|
+
visual concept, intentional dials, bounded anti-slop review, and screenshot
|
|
206
|
+
review with up to three correction rounds within the task contract. Run only
|
|
207
|
+
the visual/accessibility/performance checks in scope and retain unresolved
|
|
208
|
+
failures. Upstream scripts remain optional and unbundled; see the guide's
|
|
209
|
+
versioned baseline and intentional differences. Mark unavailable visual
|
|
210
|
+
evidence `NOT_VERIFIED`.
|
|
197
211
|
|
|
198
212
|
### `games` — web game architecture and operation
|
|
199
213
|
|
package/README.md
CHANGED
|
@@ -74,12 +74,13 @@ Routing uses bounded structural evidence; SQL remains a schema/query/migration
|
|
|
74
74
|
overlay. Extensions, tool files, lockfiles, runtime images, and prose alone do
|
|
75
75
|
not establish project identity. Public project evidence remains v1.
|
|
76
76
|
|
|
77
|
+
See the [23-guide maintenance map](./docs/GUIDE_MAINTENANCE.md) for review scope and revalidation.
|
|
78
|
+
|
|
77
79
|
## Distribution and license
|
|
78
80
|
|
|
79
81
|
GitHub hosts source and issues. The core npm package is publicly available;
|
|
80
|
-
the MCP companion retains restricted distribution.
|
|
81
|
-
`latest
|
|
82
|
-
incomplete stable SQLite acceptance.
|
|
82
|
+
the MCP companion retains restricted distribution. Stable `2.0.0` targets
|
|
83
|
+
`latest`; publication requires verified release identity and native user audits.
|
|
83
84
|
ForgeLoop-owned source and documentation are licensed under the
|
|
84
85
|
[PolyForm Noncommercial License 1.0.0](./LICENSE). Commercial use is not granted
|
|
85
86
|
by this license. Third-party notices are documented in
|
|
@@ -89,7 +90,7 @@ by this license. Third-party notices are documented in
|
|
|
89
90
|
|
|
90
91
|
### Installation
|
|
91
92
|
|
|
92
|
-
|
|
93
|
+
Install the public core package from npm; no organization access is required:
|
|
93
94
|
|
|
94
95
|
```bash
|
|
95
96
|
npm install --global @cassiomc1/forgeloop
|
|
@@ -204,7 +205,7 @@ forgeloop protocol-info --json
|
|
|
204
205
|
| Validate completion | Yes | Provides real work and evidence |
|
|
205
206
|
| Schedule agents or LLM inference | No | External to the protocol |
|
|
206
207
|
|
|
207
|
-
|
|
208
|
+
Initialize a target project using the public npm package:
|
|
208
209
|
|
|
209
210
|
```bash
|
|
210
211
|
npx @cassiomc1/forgeloop init
|
|
@@ -247,7 +248,7 @@ host-reported or `UNKNOWN`; values are never estimated.
|
|
|
247
248
|
capability, but advisory recall remains Integration API only. The stock CLI
|
|
248
249
|
does not auto-recall providers and does not expose a `context-recall` command.
|
|
249
250
|
|
|
250
|
-
Validate the source checkout
|
|
251
|
+
Validate the source checkout before preparing a release:
|
|
251
252
|
|
|
252
253
|
```bash
|
|
253
254
|
node src/cli.js init
|
|
@@ -496,18 +497,20 @@ CI audits each supplied task receipt explicitly. With no receipt it reports
|
|
|
496
497
|
completion or attestation. For contributor checks and safe payload retention,
|
|
497
498
|
see [CONTRIBUTING.md](./CONTRIBUTING.md#focused-verification-and-maintenance).
|
|
498
499
|
|
|
500
|
+
## ForgeLoopAudit workspace
|
|
501
|
+
|
|
502
|
+
The read-only auditor lives in `ForgeLoopAudit/`; see its
|
|
503
|
+
[setup, demo and screenshots](./docs/FORGELOOP_AUDIT.md).
|
|
504
|
+
|
|
499
505
|
## Protocol compatibility
|
|
500
506
|
|
|
501
|
-
The npm package version is independent of protocol version.
|
|
502
|
-
|
|
507
|
+
The npm package version is independent of protocol version. Artifacts use
|
|
508
|
+
`schemaVersion: 1` and `protocolVersion: 1`.
|
|
503
509
|
|
|
504
|
-
- Patch releases preserve the v1 schemas
|
|
505
|
-
|
|
506
|
-
- Minor releases preserve existing v1 artifacts and commands; they may add
|
|
507
|
-
documentation, commands, guides, or an explicitly named schema.
|
|
510
|
+
- Patch releases preserve the v1 schemas and existing command contracts.
|
|
511
|
+
- Minor releases preserve existing v1 artifacts; additions remain compatible.
|
|
508
512
|
- Major releases may change required fields, enums, transitions, or safety
|
|
509
|
-
semantics
|
|
510
|
-
change.
|
|
513
|
+
semantics, requiring a new protocol version and documented migration.
|
|
511
514
|
|
|
512
515
|
Consumers must reject unknown artifact fields rather than silently treating
|
|
513
516
|
unrecognized protocol data as valid. The compatibility marker is
|
|
@@ -520,6 +523,10 @@ it must not infer current ownership from `task.json` or `recovery.json` alone.
|
|
|
520
523
|
|
|
521
524
|
## Security and dependency boundary
|
|
522
525
|
|
|
526
|
+
Optional [security audits](./docs/SECURITY_AUDIT_SKILL.md) and
|
|
527
|
+
[product design](./docs/REVENUE_CENTRIC_DESIGN.md) ship with pinned attribution,
|
|
528
|
+
integrity checks and their respective licenses; guidance remains advisory.
|
|
529
|
+
|
|
523
530
|
Runtime uses Node built-ins and the approved exact `@typesafe-ai/sdk` and
|
|
524
531
|
`smol-toml` dependencies; it installs no agents, providers, plugins, services,
|
|
525
532
|
or telemetry. Paths, symlinks, JSON,
|
|
@@ -616,17 +623,15 @@ docs/diagrams/ typed Archify diagram source and inventory
|
|
|
616
623
|
docs/assets/diagrams/ committed HTML, SVG, and generation receipt
|
|
617
624
|
scripts/ checks, renderer, release identity, CI notes
|
|
618
625
|
tests/ Node and Python regression coverage
|
|
619
|
-
.forgeloop/ project-scoped
|
|
626
|
+
.forgeloop/ project-scoped configuration
|
|
620
627
|
.forgeloop/task-state/ isolated live task protocol state
|
|
621
628
|
DOCS_INDEX.md documentation map and ownership boundaries
|
|
622
629
|
```
|
|
623
630
|
|
|
624
|
-
Project-scoped configuration remains under `.forgeloop/`.
|
|
625
631
|
Task-scoped mutable protocol state is stored under
|
|
626
632
|
`.forgeloop/task-state/<taskKey>/`.
|
|
627
633
|
|
|
628
|
-
For
|
|
629
|
-
details, start at [`DOCS_INDEX.md`](./DOCS_INDEX.md).
|
|
634
|
+
For documentation ownership and integrations, see [`DOCS_INDEX.md`](./DOCS_INDEX.md).
|
|
630
635
|
|
|
631
636
|
## Programmatic integration and MCP
|
|
632
637
|
|
|
@@ -636,8 +641,7 @@ ForgeLoop exposes a stable programmatic surface:
|
|
|
636
641
|
import { executeForgeLoopCommand } from "@cassiomc1/forgeloop/integration";
|
|
637
642
|
```
|
|
638
643
|
|
|
639
|
-
The local MCP server (`@cassiomc1/forgeloop-mcp`, stdio)
|
|
640
|
-
this exact API — it never reimplements ForgeLoop. See
|
|
644
|
+
The local MCP server (`@cassiomc1/forgeloop-mcp`, stdio) wraps this API. See
|
|
641
645
|
[`docs/UNIVERSAL_INTEGRATION.md`](./docs/UNIVERSAL_INTEGRATION.md) and
|
|
642
646
|
[`docs/MCP.md`](./docs/MCP.md). MCP is optional; the CLI and instruction-only
|
|
643
647
|
hosts remain fully supported without it.
|
package/THIRD_PARTY_NOTICES.md
CHANGED
|
@@ -97,13 +97,31 @@ dependencies, version, and distribution conditions before adoption.
|
|
|
97
97
|
configure, or enable its CI/agent integrations. Verify current upstream
|
|
98
98
|
license, CLI, telemetry, network behavior, and dependencies before use.
|
|
99
99
|
|
|
100
|
+
### Cloudflare security audit skill — optional bundled companion
|
|
101
|
+
|
|
102
|
+
- Project: [cloudflare/security-audit-skill](https://github.com/cloudflare/security-audit-skill).
|
|
103
|
+
- Pinned source commit: `c1c8a8c1471069fb0e188eeaff69b8e8db6564a8`.
|
|
104
|
+
- License: MIT, copyright (c) 2025-2026 Cloudflare, Inc.; the complete upstream
|
|
105
|
+
notice is preserved at `skills/security-audit/LICENSE`.
|
|
106
|
+
- Use in this collection: the unchanged upstream `skills/security-audit/`
|
|
107
|
+
tree, including references, schema, validators and tests, is bundled for
|
|
108
|
+
optional agent guidance and explicitly requested source audits. The root
|
|
109
|
+
upstream license is copied alongside it. ForgeLoop-owned `PIN.json` records
|
|
110
|
+
the source and per-file SHA-256 digests.
|
|
111
|
+
- Boundary: instruction content and local report validators, not a runtime
|
|
112
|
+
dependency, automatic scanner, Security Review provider, evidence importer,
|
|
113
|
+
or completion gate. It is not installed into a host by `init` or `update`.
|
|
114
|
+
The upstream files retain MIT terms independently of ForgeLoop's license.
|
|
115
|
+
|
|
100
116
|
### Runtime and validator boundary
|
|
101
117
|
|
|
102
118
|
The distributed CLI and repository validators use Node.js and Python standard
|
|
103
119
|
libraries plus the JSON Schema documents shipped in this repository. The core
|
|
104
|
-
CLI
|
|
105
|
-
|
|
106
|
-
|
|
120
|
+
CLI exact-pins `smol-toml` for structural Cargo manifest parsing and
|
|
121
|
+
`@typesafe-ai/sdk` for the semantic decision plane. Parsing is local; configured
|
|
122
|
+
semantic-required operations use the external TypeSafe service under the
|
|
123
|
+
canonical decision contract. Neither dependency gains lifecycle or evidence
|
|
124
|
+
authority. Every future runtime capability must review its own license,
|
|
107
125
|
dependency tree, credentials, network behavior, and distribution terms
|
|
108
126
|
separately.
|
|
109
127
|
|
|
@@ -207,14 +225,19 @@ The contextual frontend taste guide is informed by Taste Skill:
|
|
|
207
225
|
|
|
208
226
|
- Taste Skill, Copyright (c) 2026 Leonxlnx, MIT License.
|
|
209
227
|
- Source: <https://github.com/leonxlnx/taste-skill>
|
|
228
|
+
- Reviewed baseline: [v2.0.0](https://github.com/Leonxlnx/taste-skill/tree/v2.0.0/skills/taste-skill),
|
|
229
|
+
released 2026-10-13; adaptation reviewed 2026-10-16.
|
|
210
230
|
|
|
211
231
|
ForgeLoop includes a short, adapted guide under `ENG/taste-frontend-eng.md`.
|
|
212
|
-
It
|
|
213
|
-
|
|
232
|
+
It incorporates selected content-inventory, visual-concept, and screenshot-review
|
|
233
|
+
practices. It does not vendor upstream scripts or the direction library,
|
|
234
|
+
depend on its repository at runtime, or claim full upstream feature parity.
|
|
235
|
+
Upstream tooling is optional and separately supplied; its prescriptive style
|
|
236
|
+
rules and media or motion counts are not universal ForgeLoop requirements.
|
|
214
237
|
|
|
215
238
|
## Runtime dependencies with upstream notices
|
|
216
239
|
|
|
217
|
-
### smol-toml 1.
|
|
240
|
+
### smol-toml 1.9.0
|
|
218
241
|
|
|
219
242
|
- Project/source: [squirrelchat/smol-toml](https://github.com/squirrelchat/smol-toml).
|
|
220
243
|
- License declared by the upstream package: BSD-3-Clause.
|
|
@@ -224,6 +247,18 @@ or make its prescriptive examples universal.
|
|
|
224
247
|
`package-lock.json`; the dependency has no role in routing authority beyond
|
|
225
248
|
the parser result and is not exposed as a public ForgeLoop integration.
|
|
226
249
|
|
|
250
|
+
### TypeSafe AI SDK 0.6.0
|
|
251
|
+
|
|
252
|
+
- Package: `@typesafe-ai/sdk`; source:
|
|
253
|
+
[typesafe-ai/typesafe-sdk-js](https://github.com/typesafe-ai/typesafe-sdk-js).
|
|
254
|
+
- License declared by the installed upstream package: MIT.
|
|
255
|
+
- Use in this collection: exact-pinned client for the bounded semantic
|
|
256
|
+
decision plane documented in `docs/SEMANTIC_DECISION_PLANE.md`.
|
|
257
|
+
- Boundary: credentials stay outside protocol artifacts. The SDK's responses
|
|
258
|
+
cannot execute commands, grant ownership, record evidence, or establish
|
|
259
|
+
completion. Network requirements remain explicit for semantic-required
|
|
260
|
+
operations; this is separate from optional security audit guidance.
|
|
261
|
+
|
|
227
262
|
### Microsoft tgrep
|
|
228
263
|
|
|
229
264
|
- Project: [microsoft/tgrep](https://github.com/microsoft/tgrep).
|
|
@@ -247,3 +282,21 @@ or make its prescriptive examples universal.
|
|
|
247
282
|
- Boundary: the ForgeLoop core package (`@cassiomc1/forgeloop`) has no
|
|
248
283
|
dependency on the MCP SDK; the SDK ships only inside
|
|
249
284
|
`@cassiomc1/forgeloop-mcp`. Review upstream terms before redistribution.
|
|
285
|
+
|
|
286
|
+
## Revenue-centric design companion
|
|
287
|
+
|
|
288
|
+
- Source: [heliocosta-dev/revenue-centric-design](https://github.com/heliocosta-dev/revenue-centric-design/tree/1942760c2242f609bf63ce2c97204f5a1791bd68).
|
|
289
|
+
- Ideas, frameworks and the term Revenue-Centric Design: Richard
|
|
290
|
+
([@richardrx](https://x.com/richardrx)); upstream curation is used with permission.
|
|
291
|
+
- Terms: [complete custom source-available license](./skills/forgeloop/references/revenue-centric-design/LICENSE),
|
|
292
|
+
retained in full. Attribution and preservation of those terms are required.
|
|
293
|
+
Gambling, betting, casino and real-money games-of-chance uses, including
|
|
294
|
+
loot boxes, are excluded by the author's permission. These terms apply to
|
|
295
|
+
this companion, separately from ForgeLoop's PolyForm license; they are not
|
|
296
|
+
an OSI-approved open-source license.
|
|
297
|
+
- Adaptation: a focused advisory skill and offline journey playbook under
|
|
298
|
+
`skills/forgeloop/references/revenue-centric-design/`, with a reviewed commit
|
|
299
|
+
and normalized-text integrity pin. Upstream themes are pinned links; media,
|
|
300
|
+
updater scripts and scraping dependencies are not bundled.
|
|
301
|
+
- Authority: the companion adds no runtime dependency, guide ID, automatic
|
|
302
|
+
gate or completion authority. See [setup and boundaries](./docs/REVENUE_CENTRIC_DESIGN.md).
|
|
@@ -7,7 +7,7 @@
|
|
|
7
7
|
ForgeLoop is a portable protocol and support CLI for verifiable engineering workflows. It records and validates task state, contracts, routing, checks, evidence, continuity, and optional code attestations. It does not become an agent scheduler, delegation service, source-control authority, or secret manager.
|
|
8
8
|
|
|
9
9
|
Protocol version: 1
|
|
10
|
-
Package version: 2.0.0
|
|
10
|
+
Package version: 2.0.0
|
|
11
11
|
|
|
12
12
|
## Canonical loop
|
|
13
13
|
|
package/docs/AGENT_SKILL.md
CHANGED
|
@@ -48,6 +48,21 @@ behavioral certification for every external harness. Existing native
|
|
|
48
48
|
`AGENTS.md`, `CLAUDE.md`, Cursor, and Copilot integration surfaces remain
|
|
49
49
|
intact.
|
|
50
50
|
|
|
51
|
+
## ForgeLoopAudit workspace guidance
|
|
52
|
+
|
|
53
|
+
The generated Skill documents the Audit component at `ForgeLoopAudit/` inside
|
|
54
|
+
the ForgeLoop repository, replacing the standalone repository and
|
|
55
|
+
`../ForgeLoopAudit`. It directs agents to
|
|
56
|
+
resolve the target project root before running commands: core ForgeLoop uses
|
|
57
|
+
the parent root; Audit uses its own directory, instructions, package scripts,
|
|
58
|
+
and configured protocol runtime. ForgeLoop is the source and contribution home
|
|
59
|
+
for both components; their package commands, task state, and receipt provenance
|
|
60
|
+
remain scoped to the target root. Audit remains a read-only auditor.
|
|
61
|
+
|
|
62
|
+
Maintain this guidance in `scripts/generate-forgeloop-skill.mjs`, then run
|
|
63
|
+
`npm run skill:generate` and `npm run skill:check`. An independently installed
|
|
64
|
+
Skill must be updated separately; generation only writes the repository copy.
|
|
65
|
+
|
|
51
66
|
## Safety Boundaries
|
|
52
67
|
|
|
53
68
|
Agents must discover tasks first, follow `next`, respect claims, require
|
|
@@ -59,8 +74,24 @@ authorization headers must never be persisted in ForgeLoop artifacts.
|
|
|
59
74
|
External Agent Skills tooling is not a ForgeLoop dependency and is not used in
|
|
60
75
|
CI. ForgeLoop adds no runtime Skill installation or synchronization command.
|
|
61
76
|
|
|
77
|
+
## Optional product design guidance
|
|
78
|
+
|
|
79
|
+
The [revenue-centric design companion](./REVENUE_CENTRIC_DESIGN.md) lives under
|
|
80
|
+
`skills/forgeloop/references/revenue-centric-design/`. Its focused skill and
|
|
81
|
+
local journey playbook support relevant product work with source attribution,
|
|
82
|
+
custom license terms, informed choice and measurable hypotheses. It adds no
|
|
83
|
+
runtime dependency, guide ID or lifecycle authority. The generator links to
|
|
84
|
+
this maintained reference tree and does not overwrite or install it.
|
|
85
|
+
|
|
62
86
|
## Packaging
|
|
63
87
|
|
|
88
|
+
The optional [Cloudflare security audit companion](./SECURITY_AUDIT_SKILL.md)
|
|
89
|
+
ships separately at `skills/security-audit/`. The generated ForgeLoop Skill
|
|
90
|
+
points to it for requested security work without starting a full audit or
|
|
91
|
+
requiring installation. Its upstream files, license, and hash manifest remain
|
|
92
|
+
separate from the generated ForgeLoop Skill. Host discovery copies are opt-in
|
|
93
|
+
and are not synchronized by the generator or by `init`/`update`.
|
|
94
|
+
|
|
64
95
|
The generated Skill, this document, and the bounded generator ship in the npm
|
|
65
96
|
package as instruction/documentation content. They add no runtime dependency.
|
|
66
97
|
Harness-specific installed copies and caches are not shipped.
|
|
@@ -40,6 +40,12 @@ Persistent transport truth -> src/persistent-transport/*, CLI search dispatcher,
|
|
|
40
40
|
|
|
41
41
|
Operational documentation must explain canonical behavior, not redefine it.
|
|
42
42
|
|
|
43
|
+
For the 23 engineering guides, use the
|
|
44
|
+
[guide maintenance map](./GUIDE_MAINTENANCE.md). Check activation descriptions
|
|
45
|
+
against the detector/router and frontmatter requirements before changing a
|
|
46
|
+
guide. Keep contextual styling and optional tools separate from lifecycle
|
|
47
|
+
gates; do not update review dates on untouched material.
|
|
48
|
+
|
|
43
49
|
Terminology must remain consistent across active documents: say “advisory
|
|
44
50
|
context,” not “canonical memory”; “handoff acceptance,” not “ownership
|
|
45
51
|
transfer”; and “operational receipt,” not “delegation.” Advisory output is
|
|
@@ -0,0 +1,71 @@
|
|
|
1
|
+
# ForgeLoopAudit — setup and usage
|
|
2
|
+
|
|
3
|
+
ForgeLoopAudit is the local, read-only web interface for inspecting ForgeLoop
|
|
4
|
+
projects. It lives in [`ForgeLoopAudit/`](https://github.com/cassiomc1/forgeloop/blob/main/ForgeLoopAudit/README.md) in this
|
|
5
|
+
repository; the standalone repository is retired. Use it to inspect task
|
|
6
|
+
progress, findings, verification evidence, quality, history and reports.
|
|
7
|
+
ForgeLoop remains the authority for lifecycle and completion decisions.
|
|
8
|
+
|
|
9
|
+
## Start ForgeLoopAudit
|
|
10
|
+
|
|
11
|
+
Use Node.js **24.19.0 or newer**. From a checkout of this repository:
|
|
12
|
+
|
|
13
|
+
```bash
|
|
14
|
+
cd ForgeLoopAudit
|
|
15
|
+
npm ci
|
|
16
|
+
npm run build:web
|
|
17
|
+
node dist/server/cli.mjs --demo
|
|
18
|
+
```
|
|
19
|
+
|
|
20
|
+
The CLI starts a loopback-only server and opens the browser. If it does not
|
|
21
|
+
open automatically, use the one-time bootstrap URL printed in the terminal.
|
|
22
|
+
Keep the terminal running while using Audit; press `Ctrl+C` to stop the server.
|
|
23
|
+
|
|
24
|
+
To inspect your own ForgeLoop project, replace the demo command with an
|
|
25
|
+
explicit project path, still from `ForgeLoopAudit/`:
|
|
26
|
+
|
|
27
|
+
```bash
|
|
28
|
+
node dist/server/cli.mjs --project /absolute/path/to/your-project
|
|
29
|
+
```
|
|
30
|
+
|
|
31
|
+
To inspect the parent ForgeLoop checkout itself, use `--project ..`.
|
|
32
|
+
Audit reads native SQLite task state through ForgeLoop's public Integration API.
|
|
33
|
+
Legacy JSON projects open as `ARTIFACT_ONLY`; Audit does not migrate them or
|
|
34
|
+
change task state. Project selection stays with the local server rather than
|
|
35
|
+
uploading a repository through the browser.
|
|
36
|
+
|
|
37
|
+
## Explore the audit views
|
|
38
|
+
|
|
39
|
+
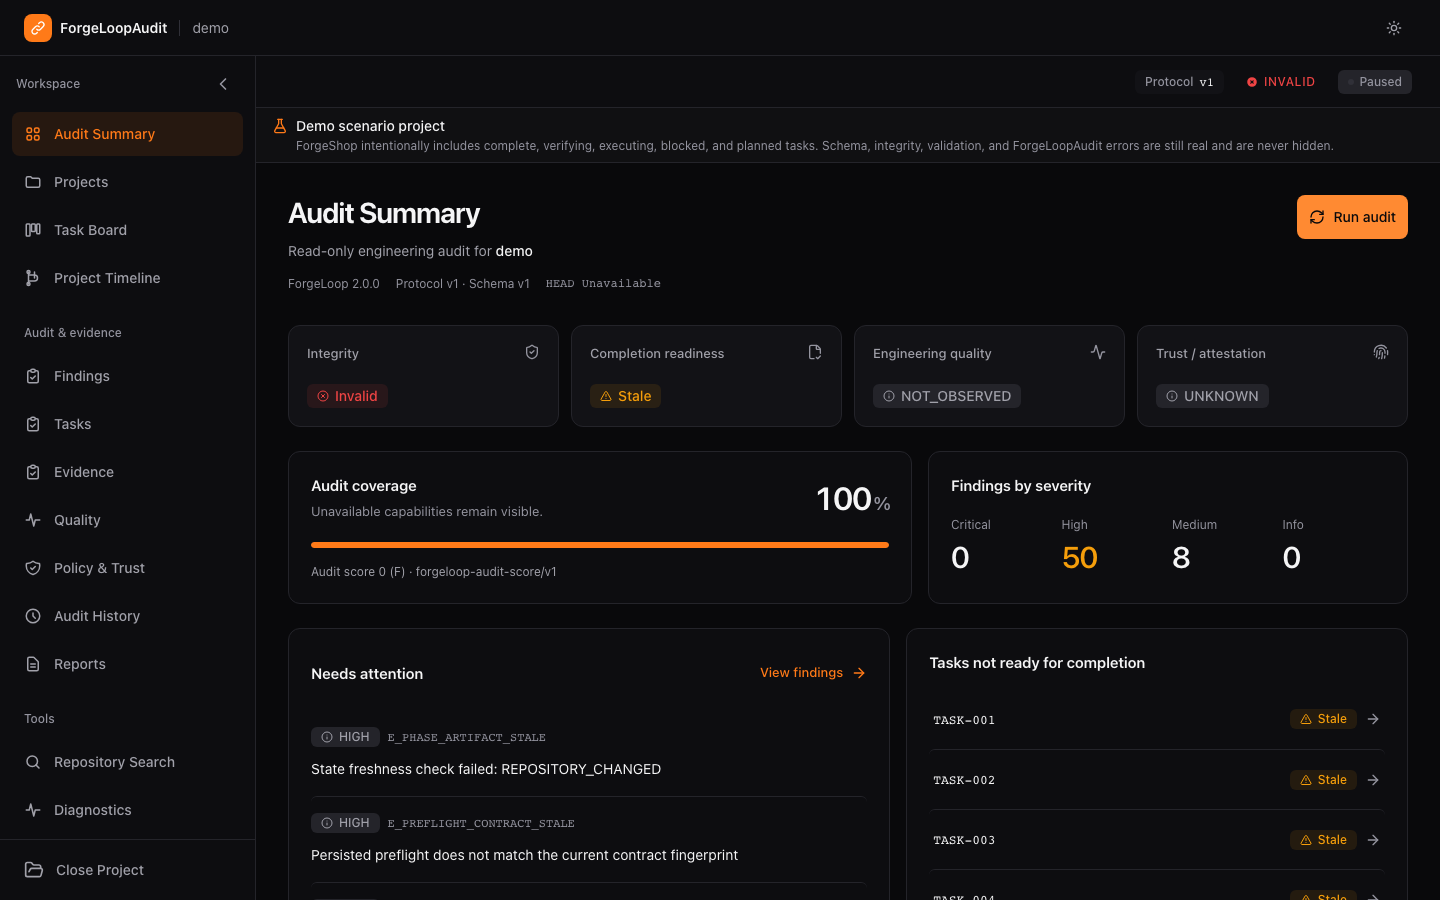
1. Open **Audit Summary** for integrity, completion readiness, quality and trust
|
|
40
|
+
verdicts. Use **Run audit** to refresh the read-only assessment.
|
|
41
|
+
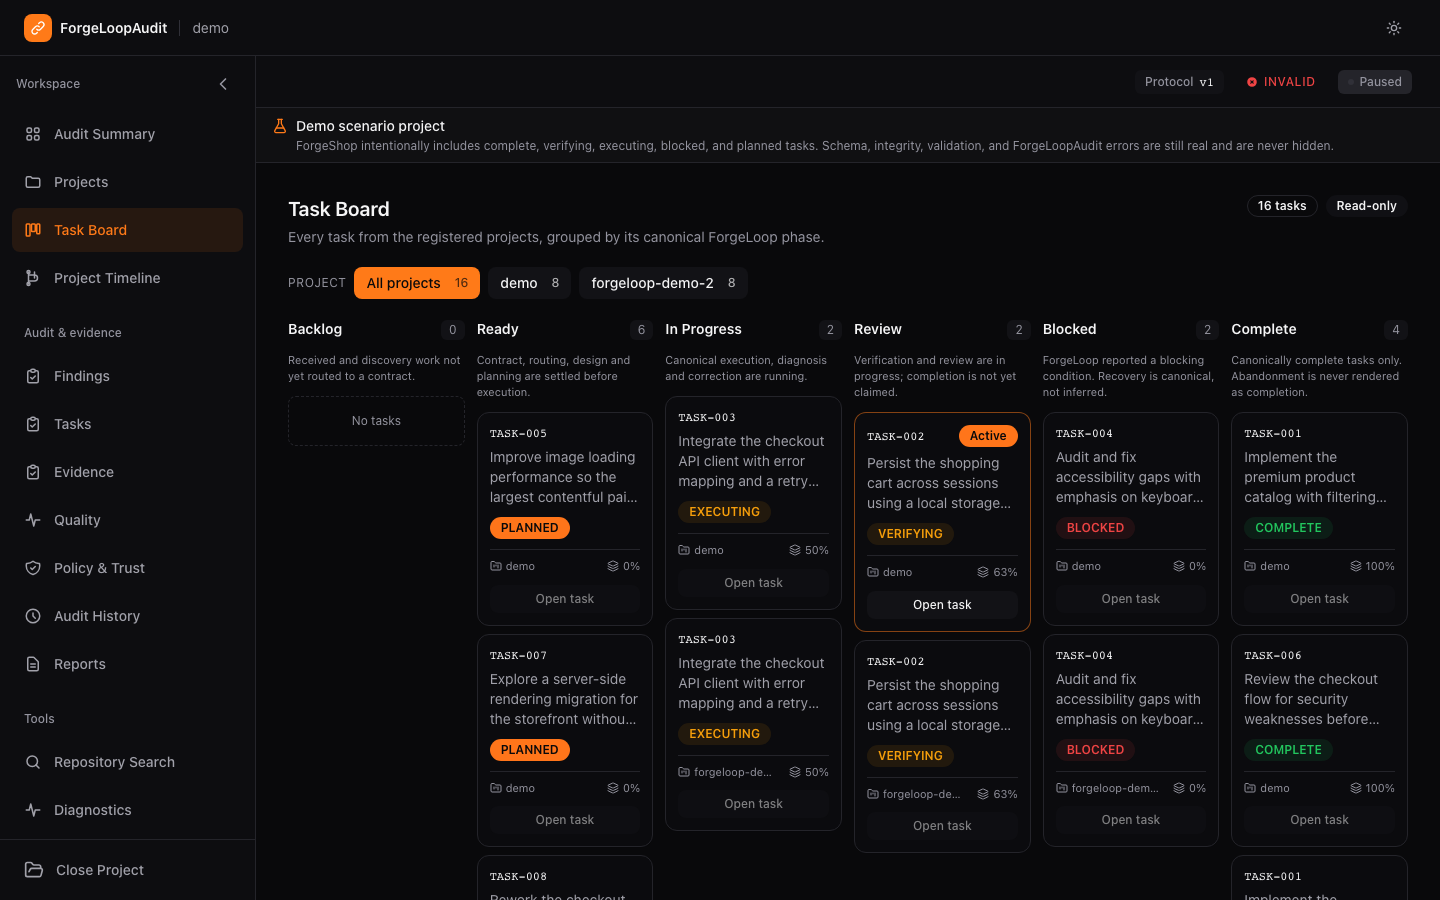
2. Use **Projects** and **Task Board** to navigate registered projects and tasks
|
|
42
|
+
by canonical lifecycle phase; open **Tasks** for a task's detailed audit.
|
|
43
|
+
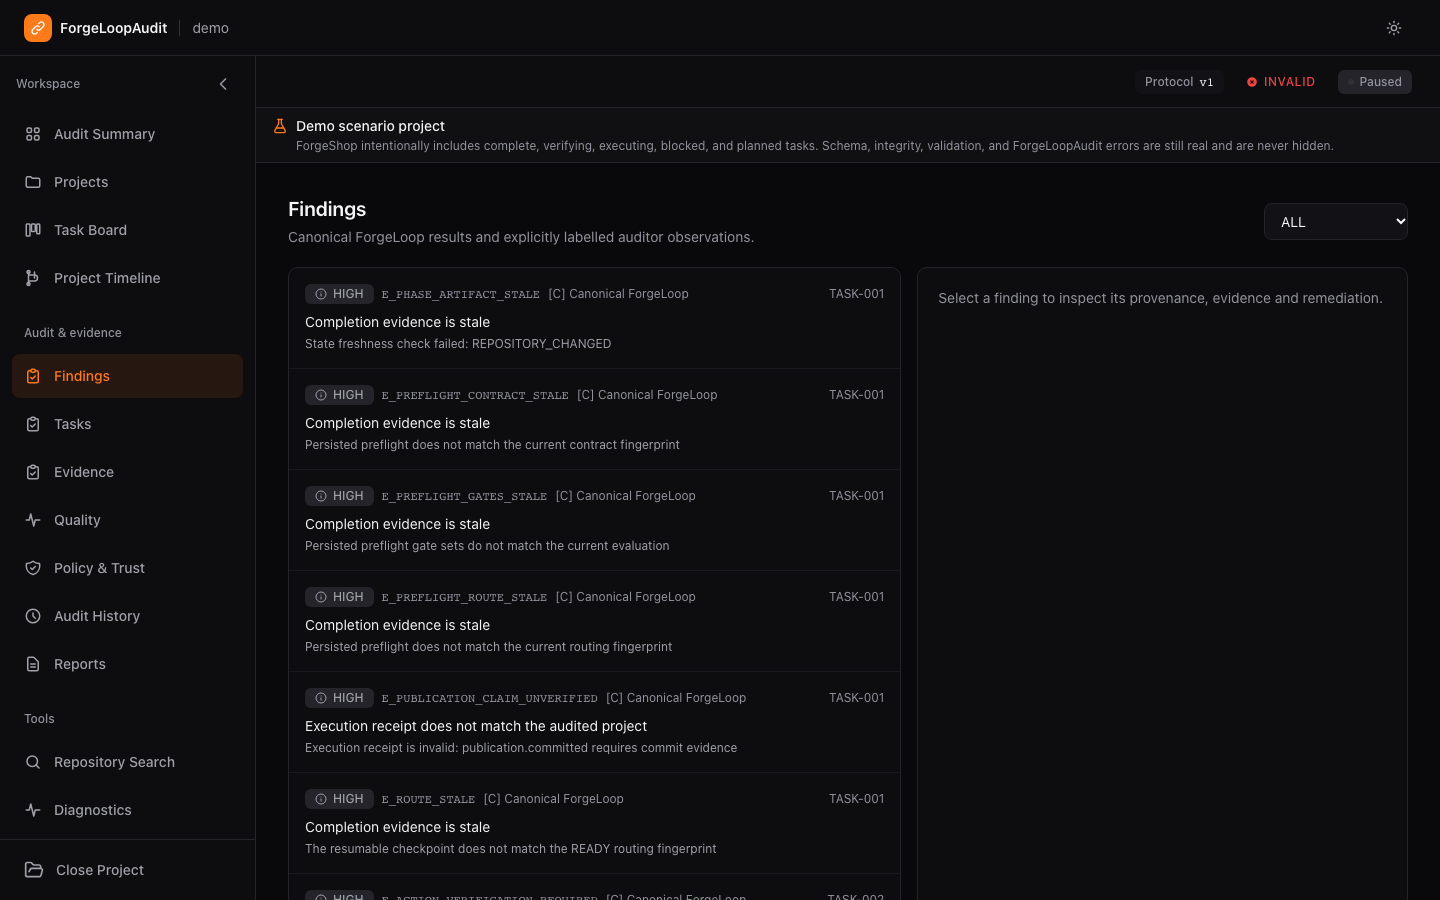
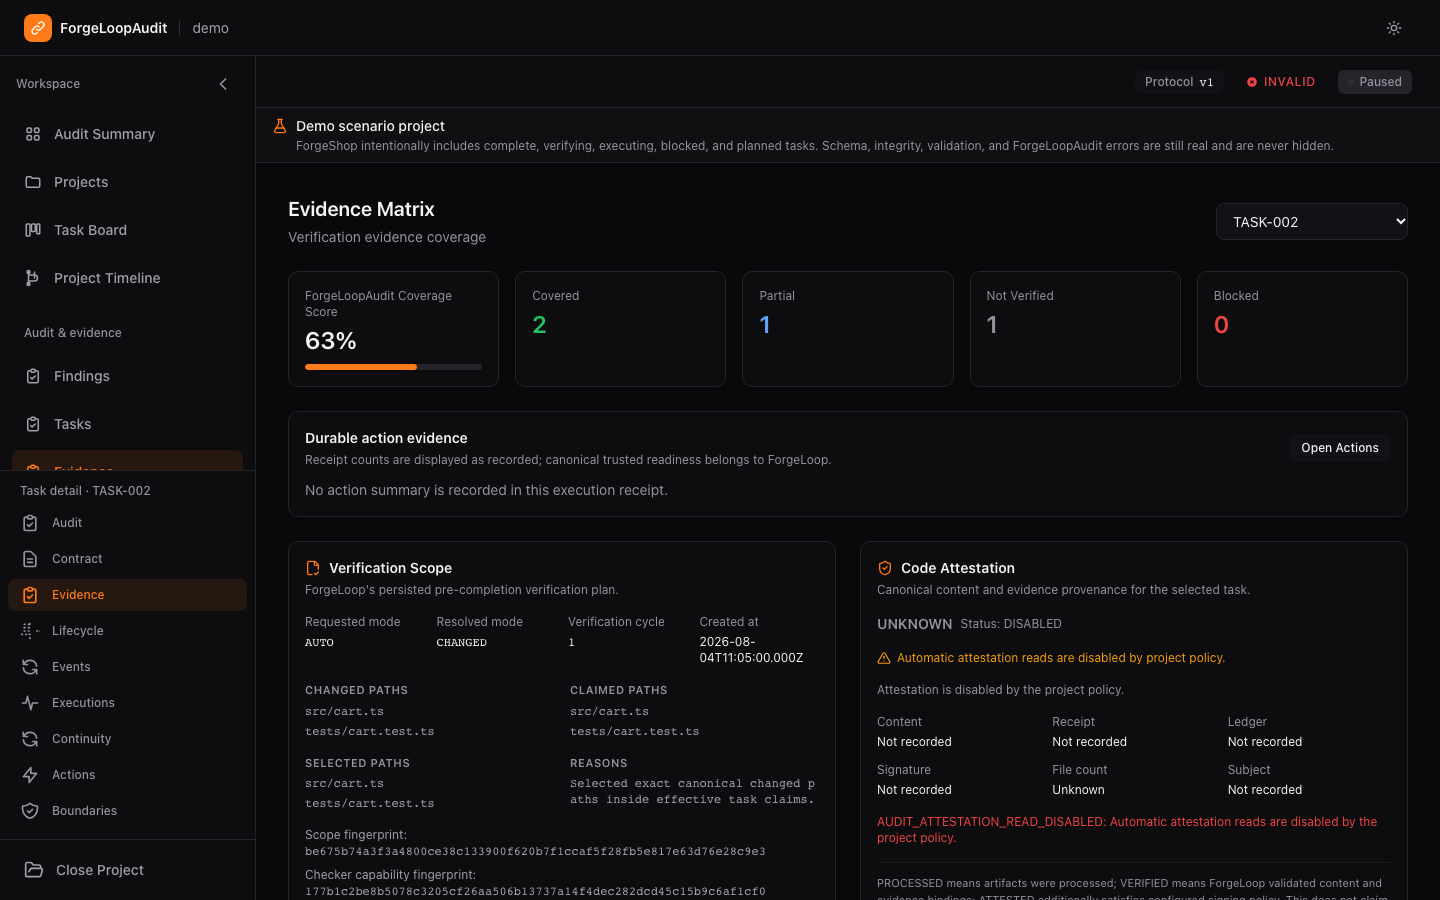
3. Review **Findings** and **Evidence** to trace warnings and verification gaps.
|
|
44
|
+
Coverage, attestation and completion are separate signals.
|
|
45
|
+
4. Inspect **Quality**, **Policy & Trust**, **Audit History** and **Diagnostics**
|
|
46
|
+
for supporting context. Use **Reports** for exports to managed local storage.
|
|
47
|
+
**Repository Search** is discovery only, not verification evidence.
|
|
48
|
+
|
|
49
|
+
## Screenshots
|
|
50
|
+
|
|
51
|
+
These are existing captures of the ForgeShop demo, taken from the production
|
|
52
|
+
renderer at 1440 × 900 in the dark theme, aligned to Audit `0.3.0-rc.3` and
|
|
53
|
+
ForgeLoop `2.0.0-rc.4`. The demo deliberately includes invalid, stale, blocked and
|
|
54
|
+
unverified scenarios. Its warnings and coverage values do not establish
|
|
55
|
+
completion or production readiness for your project.
|
|
56
|
+
|
|
57
|
+
| Audit Summary | Task Board |
|
|
58
|
+
| --- | --- |
|
|
59
|
+
|  |  |
|
|
60
|
+
| Findings | Evidence |
|
|
61
|
+
|  |  |
|
|
62
|
+
|
|
63
|
+
See the [complete screenshot gallery](https://github.com/cassiomc1/forgeloop/blob/main/ForgeLoopAudit/README.md#screenshots)
|
|
64
|
+
and [capture provenance](https://github.com/cassiomc1/forgeloop/blob/main/ForgeLoopAudit/screen/README.md) for the full set.
|
|
65
|
+
For development, verification and command-root details, see the
|
|
66
|
+
[Audit README](https://github.com/cassiomc1/forgeloop/blob/main/ForgeLoopAudit/README.md),
|
|
67
|
+
[Audit documentation index](https://github.com/cassiomc1/forgeloop/blob/main/ForgeLoopAudit/docs/README.md) and
|
|
68
|
+
[workspace guidance](./AGENT_SKILL.md#forgeloopaudit-workspace-guidance).
|
|
69
|
+
Audit has its own dependencies, build and verification commands. Its application
|
|
70
|
+
source and screenshots are excluded from the core npm package; npm users can
|
|
71
|
+
[read this section and its images on GitHub](https://github.com/cassiomc1/forgeloop#forgeloopaudit-workspace).
|
package/docs/GETTING_STARTED.md
CHANGED
|
@@ -117,6 +117,12 @@ and numeric limits.
|
|
|
117
117
|
|
|
118
118
|
### Global installation
|
|
119
119
|
|
|
120
|
+
The public core package is available without organization access. As of
|
|
121
|
+
2026-10-14, both npm `latest` and `next` resolve to `2.0.0-rc.4`. The default
|
|
122
|
+
installation below uses `latest`; use `@cassiomc1/forgeloop@2.0.0-rc.4` when an
|
|
123
|
+
exact reproducible version is required. RC4 remains a release candidate;
|
|
124
|
+
its passing new-user checks do not establish stable SQLite acceptance.
|
|
125
|
+
|
|
120
126
|
Install the ForgeLoop CLI globally to make the `forgeloop` command available
|
|
121
127
|
in your terminal:
|
|
122
128
|
|