tenuo-claude-code 0.2.2__tar.gz → 0.4.0__tar.gz
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/CONTRIBUTING.md +6 -1
- tenuo_claude_code-0.4.0/PKG-INFO +292 -0
- tenuo_claude_code-0.4.0/README.md +262 -0
- tenuo_claude_code-0.4.0/demo/README.md +86 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/tenuo.yaml +15 -8
- tenuo_claude_code-0.4.0/docs/DETAILS.md +186 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/docs/TROUBLESHOOTING.md +1 -1
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/examples/policies/README.md +1 -1
- tenuo_claude_code-0.2.2/examples/policies/audit-rollout.yaml → tenuo_claude_code-0.4.0/examples/policies/dry-run-rollout.yaml +3 -3
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/pyproject.toml +1 -1
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/__init__.py +1 -1
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/admin.py +91 -37
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/cli.py +773 -100
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/data/harness_tools.yaml +3 -3
- tenuo_claude_code-0.4.0/src/tenuo_claude_code/templates/tenuo.yaml.example +27 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/verify.py +10 -8
- tenuo_claude_code-0.4.0/templates/tenuo.yaml.advanced.example +61 -0
- tenuo_claude_code-0.4.0/templates/tenuo.yaml.example +18 -0
- tenuo_claude_code-0.4.0/tests/test_admin.py +436 -0
- tenuo_claude_code-0.4.0/tests/test_check.py +178 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_constraints.py +34 -1
- tenuo_claude_code-0.4.0/tests/test_dx_improvements.py +110 -0
- tenuo_claude_code-0.4.0/tests/test_mcp_proxy.py +53 -0
- tenuo_claude_code-0.4.0/tests/test_posture.py +261 -0
- tenuo_claude_code-0.4.0/tests/test_routing.py +322 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_scaffold.py +70 -0
- tenuo_claude_code-0.2.2/PKG-INFO +0 -598
- tenuo_claude_code-0.2.2/README.md +0 -568
- tenuo_claude_code-0.2.2/demo/README.md +0 -113
- tenuo_claude_code-0.2.2/docs/DETAILS.md +0 -302
- tenuo_claude_code-0.2.2/docs/images/README.md +0 -22
- tenuo_claude_code-0.2.2/src/tenuo_claude_code/templates/tenuo.yaml.example +0 -11
- tenuo_claude_code-0.2.2/templates/tenuo.yaml.advanced.example +0 -34
- tenuo_claude_code-0.2.2/templates/tenuo.yaml.example +0 -13
- tenuo_claude_code-0.2.2/tests/test_admin.py +0 -253
- tenuo_claude_code-0.2.2/tests/test_check.py +0 -74
- tenuo_claude_code-0.2.2/tests/test_routing.py +0 -199
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/.gitignore +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/LICENSE +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/.claude/agents/researcher.md +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/.mcp.json +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/docs/README.md +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/fake-secrets.env +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/ops_server.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/sandbox/incident-report.md +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/sandbox/notes.txt +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/demo/tenuo_demo.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/docs/images/cloud-audit-stream.png +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/docs/images/cloud-receipt-approval-detail.png +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/docs/images/tenuo_claude_code_architecture.png +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/docs/images/tenuo_claude_code_architecture.svg +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/examples/policies/enforce-with-mcp.yaml +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/examples/policies/read-only-research.yaml +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/authorizer_runtime.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/src/tenuo_claude_code/paths.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/templates/README.md +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/templates/admin.env.example +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/templates/cloud.env.example +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/templates/tenuo.yaml.cloud.example +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/conftest.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_approvals.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_authorize_call.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_authorizer_runtime.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_cloud_bindings.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_permissions.py +0 -0
- {tenuo_claude_code-0.2.2 → tenuo_claude_code-0.4.0}/tests/test_subagents.py +0 -0
|
@@ -58,7 +58,12 @@ PyPI package: **`tenuo-claude-code`**. Tag `v*` triggers
|
|
|
58
58
|
[`.github/workflows/release.yml`](.github/workflows/release.yml) (trusted publishing
|
|
59
59
|
or `PYPI_TOKEN` secret).
|
|
60
60
|
|
|
61
|
-
|
|
61
|
+
Release steps:
|
|
62
|
+
|
|
63
|
+
1. Bump `version` in `pyproject.toml`, `src/tenuo_claude_code/__init__.py`, and `uv.lock`.
|
|
64
|
+
2. Commit (`Release X.Y.Z`) and push the `vX.Y.Z` tag (this triggers the PyPI publish).
|
|
65
|
+
3. Always publish brief release notes:
|
|
66
|
+
`gh release create vX.Y.Z --verify-tag --title vX.Y.Z --notes "<one short paragraph or a few bullets>"`.
|
|
62
67
|
|
|
63
68
|
## Policy templates
|
|
64
69
|
|
|
@@ -0,0 +1,292 @@
|
|
|
1
|
+
Metadata-Version: 2.4
|
|
2
|
+
Name: tenuo-claude-code
|
|
3
|
+
Version: 0.4.0
|
|
4
|
+
Summary: Tenuo governance for Claude Code — warrants, hooks, MCP proxy, and Cloud lifecycle
|
|
5
|
+
Project-URL: Homepage, https://tenuo.ai
|
|
6
|
+
Project-URL: Repository, https://github.com/tenuo-ai/claude-governance
|
|
7
|
+
Project-URL: Documentation, https://github.com/tenuo-ai/claude-governance#readme
|
|
8
|
+
Project-URL: Issues, https://github.com/tenuo-ai/claude-governance/issues
|
|
9
|
+
Author: Tenuo Contributors
|
|
10
|
+
License-Expression: Apache-2.0
|
|
11
|
+
License-File: LICENSE
|
|
12
|
+
Keywords: agents,claude-code,governance,mcp,security,warrants
|
|
13
|
+
Classifier: Development Status :: 4 - Beta
|
|
14
|
+
Classifier: Intended Audience :: Developers
|
|
15
|
+
Classifier: License :: OSI Approved :: Apache Software License
|
|
16
|
+
Classifier: Operating System :: OS Independent
|
|
17
|
+
Classifier: Programming Language :: Python :: 3
|
|
18
|
+
Classifier: Programming Language :: Python :: 3.10
|
|
19
|
+
Classifier: Programming Language :: Python :: 3.11
|
|
20
|
+
Classifier: Programming Language :: Python :: 3.12
|
|
21
|
+
Classifier: Programming Language :: Python :: 3.13
|
|
22
|
+
Classifier: Topic :: Security
|
|
23
|
+
Classifier: Topic :: Software Development :: Libraries :: Python Modules
|
|
24
|
+
Requires-Python: >=3.10
|
|
25
|
+
Requires-Dist: certifi>=2024.0
|
|
26
|
+
Requires-Dist: mcp>=1.0
|
|
27
|
+
Requires-Dist: pyyaml>=6.0
|
|
28
|
+
Requires-Dist: tenuo==0.1.0b24
|
|
29
|
+
Description-Content-Type: text/markdown
|
|
30
|
+
|
|
31
|
+
# Tenuo for Claude Code
|
|
32
|
+
|
|
33
|
+
[](https://pypi.org/project/tenuo-claude-code/)
|
|
34
|
+
[](https://pypi.org/project/tenuo-claude-code/)
|
|
35
|
+
[](https://github.com/tenuo-ai/claude-governance/actions/workflows/ci.yml)
|
|
36
|
+
[](LICENSE)
|
|
37
|
+
|
|
38
|
+
Claude Code can read files, run shell commands, fetch URLs, and call MCP tools.
|
|
39
|
+
Tenuo lets you write a `tenuo.yaml` policy for which of those calls are allowed,
|
|
40
|
+
then checks every model-invoked tool call before it runs.
|
|
41
|
+
|
|
42
|
+
That policy is compiled into a signed, expiring credential called a warrant. A
|
|
43
|
+
local authorizer checks each tool call against it and logs the decision. The
|
|
44
|
+
same policy is applied no matter why the model tried the call: prompt injection,
|
|
45
|
+
hallucination, poisoned tool output, or an unsafe request.
|
|
46
|
+
|
|
47
|
+
Start with the local quickstart below. Optional Cloud control-plane setup is in
|
|
48
|
+
[Cloud mode](#cloud-mode).
|
|
49
|
+
|
|
50
|
+
## Quickstart
|
|
51
|
+
|
|
52
|
+
Requires Python 3.10+. Uses Docker if it's running; otherwise a native authorizer binary, installed automatically. On Windows, run these commands from WSL.
|
|
53
|
+
|
|
54
|
+
```bash
|
|
55
|
+
pip install tenuo-claude-code
|
|
56
|
+
mkdir my-project && cd my-project
|
|
57
|
+
tenuo-claude bootstrap
|
|
58
|
+
```
|
|
59
|
+
|
|
60
|
+
`bootstrap` writes a starter `tenuo.yaml`, starts the authorizer, and runs a self-test (`verify`). It runs non-interactively, ideal for a fresh folder. For a guided wizard with prompts, run `tenuo-claude onboard` instead; it's the same flow with a preflight `check`. The starter policy is deliberately strict:
|
|
61
|
+
|
|
62
|
+
```yaml
|
|
63
|
+
name: my-project
|
|
64
|
+
sandbox: ./workspace
|
|
65
|
+
mode: enforce
|
|
66
|
+
enforce:
|
|
67
|
+
Read: "subpath:{sandbox}" # Read only files under ./workspace
|
|
68
|
+
Bash: "shlex:ls,pwd,echo,date" # Bash only these commands
|
|
69
|
+
default: deny # every other tool call is denied
|
|
70
|
+
```
|
|
71
|
+
|
|
72
|
+
Now open Claude Code in `my-project/`:
|
|
73
|
+
|
|
74
|
+
```bash
|
|
75
|
+
claude
|
|
76
|
+
```
|
|
77
|
+
|
|
78
|
+
The agent is governed: `Read ./workspace/notes.txt` is allowed; `Read /etc/passwd`, `Bash(curl …)`, or any tool not listed is denied and logged. After Claude runs a few tools, run `tenuo-claude audit` to see the decisions. Edit `tenuo.yaml` to fit your project (see [Policy](#policy)), then `tenuo-claude refresh`.
|
|
79
|
+
|
|
80
|
+
For an example with MCP and subagents, see the [reference demo](demo/).
|
|
81
|
+
|
|
82
|
+
| Next | Go to |
|
|
83
|
+
|------|-------|
|
|
84
|
+
| Write the policy | [Policy](#policy) |
|
|
85
|
+
| Day-to-day commands | [Commands](#commands) |
|
|
86
|
+
| Org root, receipts, approvals, revocation | [Cloud mode](#cloud-mode) |
|
|
87
|
+
| Security model and limits | [Security](#security) |
|
|
88
|
+
| Something broke | [Troubleshooting](docs/TROUBLESHOOTING.md) · deep dive [docs/DETAILS.md](docs/DETAILS.md) |
|
|
89
|
+
|
|
90
|
+
## Policy
|
|
91
|
+
|
|
92
|
+
`tenuo.yaml` is the whole configuration: it drives the warrant, the authorizer, the hooks, and the MCP proxy. You list tools under `enforce:` and give each a constraint on its key argument.
|
|
93
|
+
|
|
94
|
+
```yaml
|
|
95
|
+
name: acme-backend
|
|
96
|
+
sandbox: ./workspace # a directory; {sandbox} expands to its absolute path
|
|
97
|
+
ttl_seconds: 3600 # optional: session warrant lifetime (default 3600 = 1h)
|
|
98
|
+
mode: enforce # block out-of-scope calls. 'dry-run' = log only, don't block
|
|
99
|
+
|
|
100
|
+
enforce:
|
|
101
|
+
Read: "subpath:{sandbox}"
|
|
102
|
+
Write: "subpath:{sandbox}"
|
|
103
|
+
Bash: "shlex:ls,pwd,echo,cat,grep"
|
|
104
|
+
WebFetch:
|
|
105
|
+
domains: ["api.github.com", "*.githubusercontent.com"]
|
|
106
|
+
|
|
107
|
+
default: deny # anything not listed above is denied
|
|
108
|
+
|
|
109
|
+
subagents: # optional: each role runs under a narrower warrant
|
|
110
|
+
analyst:
|
|
111
|
+
tools: [Read, Grep, Glob]
|
|
112
|
+
|
|
113
|
+
mcp: # optional: govern a downstream MCP server's tools
|
|
114
|
+
downstream: ./your_mcp_server.py
|
|
115
|
+
enforce:
|
|
116
|
+
read_file: "subpath:{sandbox}" # bare string constrains the `path` arg
|
|
117
|
+
run_query: # constrain a differently-named arg
|
|
118
|
+
arg: sql
|
|
119
|
+
constraint: "regex:^SELECT "
|
|
120
|
+
http_call: # constrain several args at once
|
|
121
|
+
args:
|
|
122
|
+
url: "urlpattern:https://api.example.com/*"
|
|
123
|
+
method: "oneof:GET,HEAD"
|
|
124
|
+
```
|
|
125
|
+
|
|
126
|
+
### Constraints
|
|
127
|
+
|
|
128
|
+
| Constraint | Applies to | What it checks |
|
|
129
|
+
|------------|------------|----------------|
|
|
130
|
+
| `subpath:DIR` | path tools (Read, Write, Edit, Glob, Grep) | the path argument must resolve to a location **inside `DIR`**. Symlinks are resolved first, so a link planted in the directory can't point outside it. |
|
|
131
|
+
| `shlex:a,b,c` | Bash, Monitor | the command's **executable** must be one of `a,b,c`, and the command must be a single simple command: pipes, `&&`/`;` chaining, subshells, and shell expansion are rejected. (This allowlists the *verb*, not file paths: `cat /etc/passwd` passes if `cat` is allowed. Use `Read`/`Write` to scope files; drop `Bash` for a hard lock.) |
|
|
132
|
+
| `domains` / `cidrs` / `schemes` / `ports` | WebFetch | the URL's host must match an allowed domain (`*` matches one label) or CIDR range, **and** pass SSRF hygiene: https-only by default (override with `schemes`), optional `ports` allowlist, with loopback, cloud-metadata IPs, encoded-IP tricks, and spoofed hosts (`api.github.com.evil.com`) blocked. |
|
|
133
|
+
| `oneof:a,b` · `notoneof:a,b` · `exact:v` · `pattern:glob` · `regex:re` · `range:min,max` · `urlpattern:url` · `cidr:n/m` | any tool argument | the value must be in the set / not in the set / equal / glob-match / regex-match / fall in the numeric range (either bound may be blank) / match the URL glob / fall inside the IP range (for any IP-based tool, not just WebFetch). |
|
|
134
|
+
|
|
135
|
+
The keys above are the `tenuo.yaml` DSL's convenient subset. The underlying tenuo engine supports more (set operations, numeric ranges, negation, boolean composition, and CEL expressions) for programmatic policies — see [tenuo](https://github.com/tenuo-ai/tenuo).
|
|
136
|
+
|
|
137
|
+
`{sandbox}` is a convenience variable for the directory in `sandbox:`; you can point `subpath:` at any path. Tools you don't list aren't governed individually; they're caught by `default`.
|
|
138
|
+
|
|
139
|
+
For internal egress, `WebFetch` also accepts `cidrs:` to allow hosts by IP range (e.g. `cidrs: ["10.0.0.0/8"]` alongside `domains:`). It's off by default and reaches past public domains and SSRF private-network defaults, so add it deliberately.
|
|
140
|
+
|
|
141
|
+
**Command-execution tools.** `Bash`, `PowerShell`, and `Monitor` all execute commands and are each governed independently (their own constraint on the `command` argument). `Monitor` runs the same shell commands as `Bash` in the background; `PowerShell` is a different dialect, so prefer `oneof`/`pattern`/`regex` over `shlex` (which parses POSIX syntax) for it. If your team enables `PowerShell` or `Monitor` in Claude Code, list them under `enforce:` too. Left unlisted they fall to `default: deny` and are blocked. Never put a shell in `allow:` — that grants it **unconstrained**; governed shells belong under `enforce:`.
|
|
142
|
+
|
|
143
|
+
**MCP tool arguments.** Under `mcp.enforce:`, a bare constraint string targets the `path` argument. To constrain a differently-named argument use `arg: NAME` + `constraint:`, and to constrain several at once use `args: {NAME: constraint, …}`. This works for any downstream MCP tool and any constraint kind, locally and on Cloud. Tools you don't list are still allowed/denied by `default` and can be human-approval gated (`approval:`); they just aren't argument-constrained.
|
|
144
|
+
|
|
145
|
+
- **`mode: enforce`** blocks denied calls. **`mode: dry-run`** computes and logs the same decisions but blocks nothing; use it to roll out a policy, then switch to `enforce`. (`mode: audit` is a deprecated alias for `dry-run`.)
|
|
146
|
+
- **`allow:`** lists extra tools permitted without constraints. Inert Claude harness tools (plan mode, TodoWrite, AskUserQuestion, …) are bundled in by default; set `allow_bundled: false` to opt out.
|
|
147
|
+
- **`default:`** is the fallback for any tool in neither `enforce` nor `allow`: **`deny`** blocks it (recommended) or **`approve`** requires human sign-off (Tenuo Cloud). There is no allow-everything fallback — enforce never fails open; use `mode: dry-run` to observe instead.
|
|
148
|
+
- **`subagents:`** declares roles; spawning is gated to those roles, and each runs under the session warrant **attenuated** to its `tools` (it can only ever do less than the session). [Details](docs/DETAILS.md#subagents).
|
|
149
|
+
- **`ttl_seconds:`** sets the session warrant lifetime in seconds (positive integer; default `3600` = 1h). `up` re-mints before expiry. Enterprise rollouts pin it centrally through Claude Code managed settings / MDM (the policy file is what managed settings pins); local dev sets it directly. A shorter TTL shrinks the blast radius of a leaked warrant.
|
|
150
|
+
|
|
151
|
+
Ready-made policies: [examples/policies/](examples/policies/). After any edit, run `tenuo-claude refresh`.
|
|
152
|
+
|
|
153
|
+
## Commands
|
|
154
|
+
|
|
155
|
+
Day to day, you mostly need `up` (start), `audit` (review), and `refresh` (after editing policy).
|
|
156
|
+
|
|
157
|
+
| Command | What it does |
|
|
158
|
+
|---------|--------------|
|
|
159
|
+
| `onboard` | Interactive first-run wizard (`--local` / `--cloud`); same flow as `bootstrap` but prompts and runs a preflight `check`. Scaffolds an example policy if you don't have one. |
|
|
160
|
+
| `bootstrap` | First-run quickstart (used above): non-interactive scaffold starter policy (if none) → `init` → `up` → `verify`. `--cloud` for Cloud. |
|
|
161
|
+
| `init` | Compile an **existing** `tenuo.yaml`: mint the warrant, wire the PreToolUse hook and MCP proxy. Pass `--scaffold` to write an example if none exists (it no longer does so automatically). |
|
|
162
|
+
| `up` / `down` | Start / stop the authorizer (auto-selects Docker or native; `--native` to force). |
|
|
163
|
+
| `refresh` | Recompile after editing `tenuo.yaml` (restarts the authorizer if running). In Cloud mode, warns if capability rules drifted from the last `tenuo-admin setup`. |
|
|
164
|
+
| `verify [--deep]` | Self-test the live policy against the authorizer (no Claude session needed). `--deep` adds an SSRF / encoded-IP matrix and extra Bash deny cases — a reproducible artifact for security review; when the local Claude CLI can load project settings, it also runs a live PreToolUse exit-code harness. |
|
|
165
|
+
| `audit [--tail N]` | Show the decision log (`.state/receipts.jsonl`). |
|
|
166
|
+
| `check` | Preflight: dependencies, wiring, audit-sink health, leaked admin keys, and (Cloud) control-plane bindings. |
|
|
167
|
+
| `status` | Warrant, mode, audit-sink health, and Cloud summary. |
|
|
168
|
+
| `install-authorizer` | Install the native authorizer to `~/.tenuo/bin` (no Docker, no Cargo). |
|
|
169
|
+
| `bench [--json]` | Measure per-call overhead on your machine (PoP sign, authorizer round-trip, full hook path). |
|
|
170
|
+
| `revoke` | Revoke the current session warrant. |
|
|
171
|
+
|
|
172
|
+
The warrant is short-lived (1h TTL by default, configurable via `ttl_seconds:` in `tenuo.yaml`); `up` refreshes it. The authorizer listens on `127.0.0.1:9090`; change it with `TENUO_AUTHORIZER_PORT` before `bootstrap`. Generated files (don't commit): `.state/` (keys, warrant, credentials), `.claude/settings.json` (hooks), `.mcp.json` (MCP wiring).
|
|
173
|
+
|
|
174
|
+
Working from a git clone instead of PyPI? See [Build from source](#build-from-source).
|
|
175
|
+
|
|
176
|
+
## How enforcement works
|
|
177
|
+
|
|
178
|
+
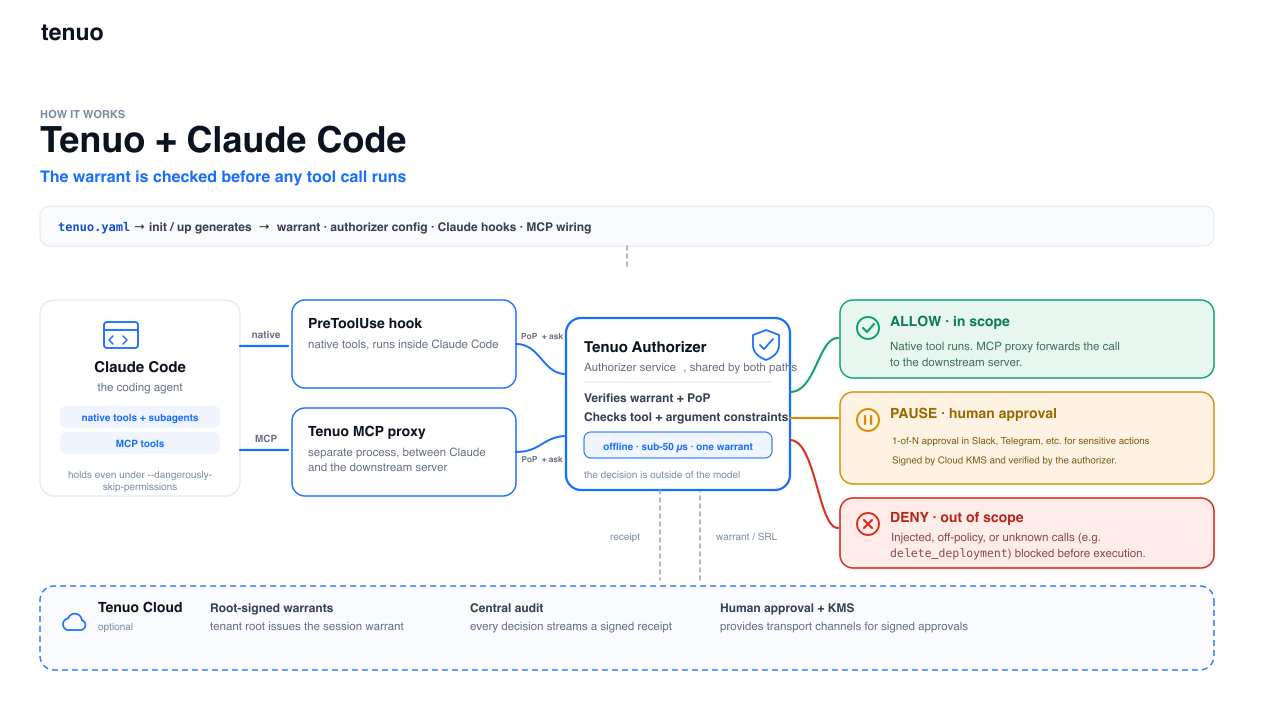
`init` compiles `tenuo.yaml` into a signed warrant and wires two interception points; both check the **same** warrant against the **same** local authorizer:
|
|
179
|
+
|
|
180
|
+
- **Native tools** (Read, Bash, WebFetch, …) → a Claude Code **PreToolUse hook** intercepts the call, signs a proof-of-possession with the session key, and asks the authorizer.
|
|
181
|
+
- **MCP tools** → Claude is pointed at a **proxy** that stands in for the downstream MCP server; the proxy authorizes, then forwards only if allowed.
|
|
182
|
+
|
|
183
|
+
|
|
184
|
+
|
|
185
|
+
The authorizer (a small local service, ~1–3 ms/call) verifies the warrant's signature, proof-of-possession, and expiry, then checks the call's arguments against the warrant's constraints → allow, deny, or (Cloud) approval-required. Full detail in [docs/DETAILS.md](docs/DETAILS.md).
|
|
186
|
+
|
|
187
|
+
## Cloud mode
|
|
188
|
+
|
|
189
|
+
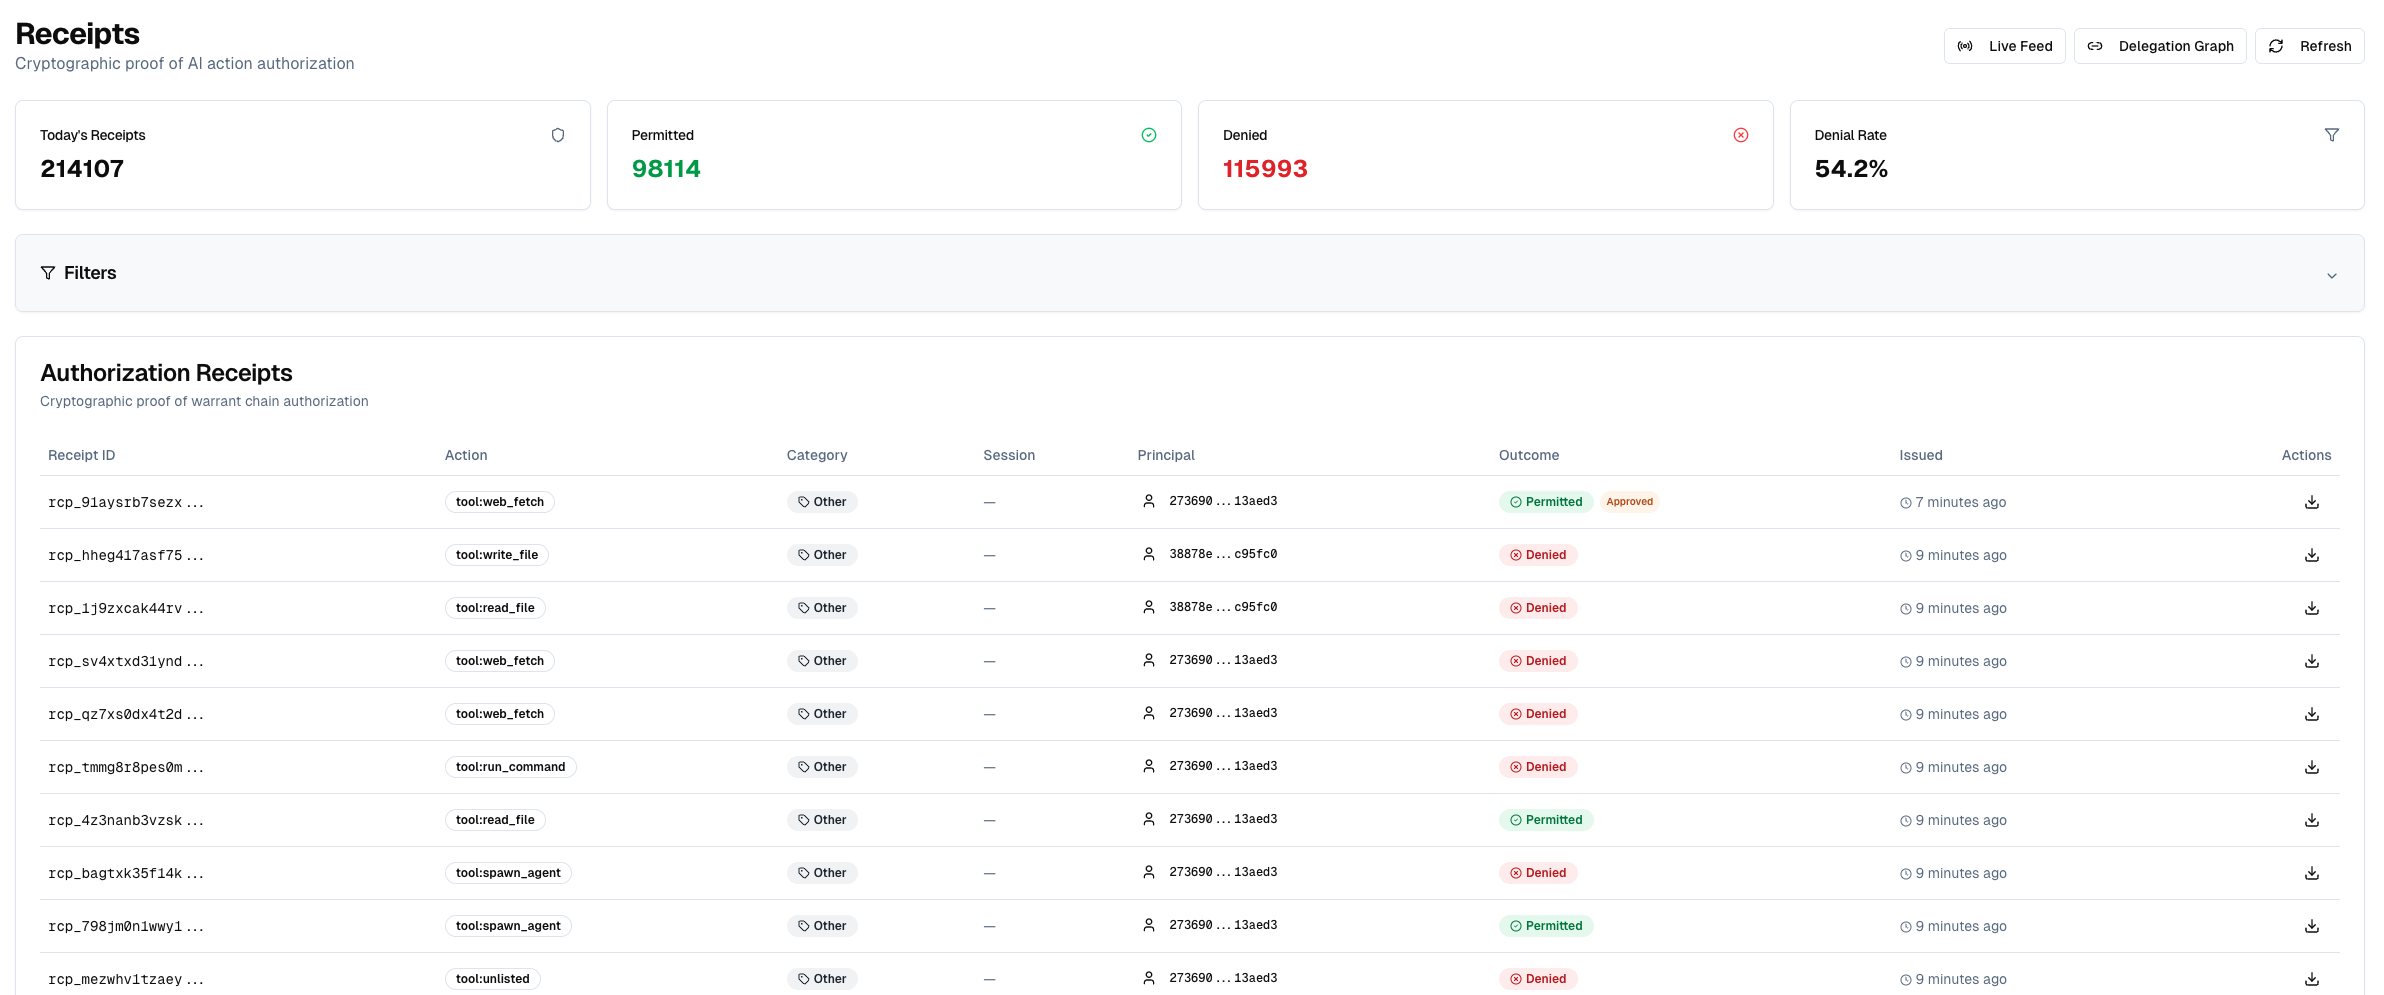
Local mode is enough to evaluate Tenuo on one project. Connect [cloud.tenuo.ai](https://cloud.tenuo.ai) for organization-scale governance:
|
|
190
|
+
|
|
191
|
+
- **Tenant-root warrants**: sessions chain to your org root, not a key on the laptop.
|
|
192
|
+
- **Signed receipts**: one verifiable allow/deny/approval audit stream (Ed25519 over CBOR).
|
|
193
|
+
- **Fleet revocation**: revoke a warrant id; authorizers pick it up within ~30s.
|
|
194
|
+
- **Human approval gates**: specific calls pause for a person instead of allow/deny ([below](#human-approval-cloud)).
|
|
195
|
+
- **Managed rollout**: push hook/MCP wiring through Claude Code managed settings instead of per-project local settings.
|
|
196
|
+
|
|
197
|
+
|
|
198
|
+
|
|
199
|
+
### Setup
|
|
200
|
+
|
|
201
|
+
Two keys, kept apart; the runtime never sees the admin key:
|
|
202
|
+
|
|
203
|
+
| Key | From | Goes in | Used by |
|
|
204
|
+
|-----|------|---------|---------|
|
|
205
|
+
| **Runtime** (`tenuo_ct_…`) | cloud.tenuo.ai → Agents → Quick Connect → **Authorizer Only** | `.state/cloud.env` | `tenuo-claude up`, hooks |
|
|
206
|
+
| **Tenant-admin** (`tc_…`) | Settings → API Keys → Create (admin role) | `~/.tenuo/admin.env` | `tenuo-admin setup` (once) |
|
|
207
|
+
|
|
208
|
+
```bash
|
|
209
|
+
mkdir my-project && cd my-project
|
|
210
|
+
tenuo-claude bootstrap --cloud # runtime token from --connect-token/env, or prompts if missing; then sets up + verifies
|
|
211
|
+
```
|
|
212
|
+
|
|
213
|
+
Every session after that:
|
|
214
|
+
|
|
215
|
+
```bash
|
|
216
|
+
tenuo-claude check && tenuo-claude up
|
|
217
|
+
```
|
|
218
|
+
|
|
219
|
+
If `check` reports a **cloud bindings** failure, run `tenuo-admin setup` and retry.
|
|
220
|
+
|
|
221
|
+
> `tenuo-claude up` refuses to start if a tenant-admin key is in the environment; keep it only in `~/.tenuo/admin.env`. And once a project is on Cloud, don't re-run plain `bootstrap`: it reverts the project to local mode and moves your Cloud files aside. Use `check && up`.
|
|
222
|
+
|
|
223
|
+
CI / non-interactive and manual step-by-step setup: [docs/DETAILS.md § Tenuo Cloud](docs/DETAILS.md#tenuo-cloud-extended). After changing `enforce`/`mcp`/`subagents`/approvals on Cloud, re-run `tenuo-admin setup`; for `mode`-only changes, `refresh` suffices.
|
|
224
|
+
|
|
225
|
+
### Human approval (Cloud)
|
|
226
|
+
|
|
227
|
+
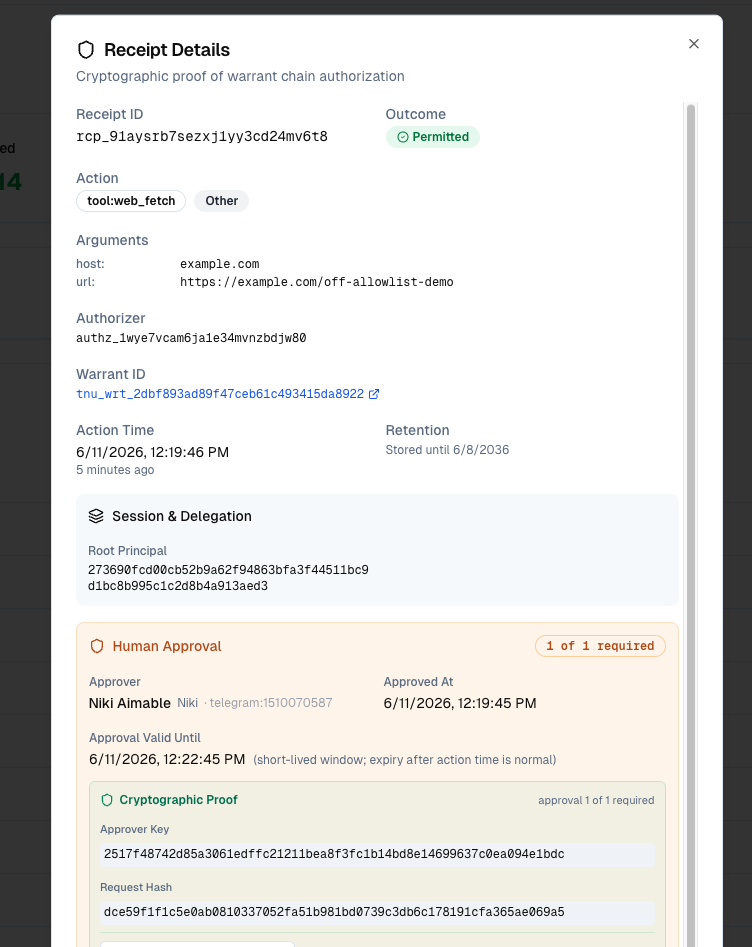
A gated capability returns a third outcome, `approval-required`, instead of allow/deny. The hook opens a Cloud approval request, waits for an approver on their notification channel (Slack, Telegram, console, …), then re-authorizes with their **signed, identity-bound** approval — so the receipt records *who* approved. Add an `approval:` block to **any enforced native tool** (e.g. `Bash`), **any `mcp.enforce` tool**, or `WebFetch`; an optional `exempt:` lets safe argument values skip the gate. `default: approve` gates every unlisted tool.
|
|
228
|
+
|
|
229
|
+
**Human approval requires Tenuo Cloud — anywhere (native hook, MCP proxy, or catch-all).** The gate lives in the Cloud-issued warrant, so without Cloud an approval-gated tool falls back to **deny** (fail-closed); `tenuo-claude check` warns when a gate is configured but Cloud isn't. Setup and policy shape: [docs/DETAILS.md § Human approval](docs/DETAILS.md#human-approval-cloud).
|
|
230
|
+
|
|
231
|
+
|
|
232
|
+
|
|
233
|
+
## Security
|
|
234
|
+
|
|
235
|
+
Tenuo runs **alongside** Claude Code permissions; it doesn't replace managed settings. The difference is where and how policy is enforced:
|
|
236
|
+
|
|
237
|
+
| | Claude Code permissions | Tenuo warrant |
|
|
238
|
+
|---|---|---|
|
|
239
|
+
| Form | Allow/ask/deny rules in settings | Signed, expiring capability token; Cloud chains to your org root |
|
|
240
|
+
| Enforcement point | Claude's permission UI | PreToolUse hook + MCP proxy, checked by the authorizer |
|
|
241
|
+
| `--dangerously-skip-permissions` | Skips the prompts | Does not disable installed Tenuo hook/proxy checks |
|
|
242
|
+
| Expiry | Until edited | Session TTL (1h default, set via `ttl_seconds:`); `up` refreshes |
|
|
243
|
+
| Revocation | Edit rules (live sessions may keep allowances) | Revoke warrant id → ~30s fleet sync (Cloud) |
|
|
244
|
+
| Evidence | Optional hook logs | Local JSONL; signed receipt stream in Cloud |
|
|
245
|
+
| Org deployment | Per-user settings, locally editable | Managed-settings hooks + shared policy |
|
|
246
|
+
|
|
247
|
+
Admins can also block the bypass flag entirely in managed settings (`disableBypassPermissionsMode`).
|
|
248
|
+
|
|
249
|
+
**What's in scope.** Tenuo governs **model-invoked tool calls** (Read, Bash, WebFetch, MCP tools, subagent spawns) on the PreToolUse path, including the agent's own Bash. The TUI `!` shell (a command the *operator* types) is not a tool call and is out of scope; the model can't invoke it. ([details](docs/DETAILS.md#agent-tools-vs-operator-shell))
|
|
250
|
+
|
|
251
|
+
**Fail-closed.** A missing or broken `tenuo.yaml` denies every governed call until it's restored. Keys under `.state/` must be owner-only (`0600`).
|
|
252
|
+
|
|
253
|
+
**Receipts.** Every governed call carries a proof-of-possession signature the authorizer verifies. Locally, the hook appends a JSON line to `.state/receipts.jsonl` (read with `tenuo-claude audit`; in `mode: dry-run`, denials show as `WOULD-DENY`):
|
|
254
|
+
|
|
255
|
+
```json
|
|
256
|
+
{"phase":"pre","decision":"deny","claude_tool":"Read","governed":true,
|
|
257
|
+
"args":{"file_path":"/etc/passwd"},"reason":"Constraint not satisfied"}
|
|
258
|
+
```
|
|
259
|
+
|
|
260
|
+
Connected to Cloud, the authorizer also emits **signed** receipts to your tenant, the verifiable record for compliance and fleet audit.
|
|
261
|
+
|
|
262
|
+
**Rolling out to a team.** Keep `tenuo.yaml` in version control, push the hook/MCP wiring through Claude Code **managed settings** (not per-developer `settings.local.json`), and use Cloud for org-root warrants, central audit, and revocation. Start in `mode: dry-run`, review the `WOULD-DENY` rows, then switch to `enforce`. [Talk to us](https://tenuo.ai/early-access.html) about managed-settings rollout. Report issues: [SECURITY.md](SECURITY.md).
|
|
263
|
+
|
|
264
|
+
## Build from source
|
|
265
|
+
|
|
266
|
+
For development, running the demo from a checkout, or using `./bin/tenuo-claude`:
|
|
267
|
+
|
|
268
|
+
```bash
|
|
269
|
+
git clone https://github.com/tenuo-ai/claude-governance.git
|
|
270
|
+
cd claude-governance
|
|
271
|
+
uv venv && uv sync && source .venv/bin/activate # Windows: .venv\Scripts\activate
|
|
272
|
+
chmod +x bin/tenuo-claude
|
|
273
|
+
uv run tenuo-claude install-authorizer # only if you don't use Docker
|
|
274
|
+
```
|
|
275
|
+
|
|
276
|
+
Run via `./bin/tenuo-claude --help`, `uv run tenuo-claude --help`, or `pip install -e .`. Re-run `tenuo-claude init` (or `refresh`) after moving the repo or reinstalling. The hooks pin the launcher path at wiring time. Contributors: [CONTRIBUTING.md](CONTRIBUTING.md).
|
|
277
|
+
|
|
278
|
+
## Performance
|
|
279
|
+
|
|
280
|
+
Authorization is ~1–3 ms per call; the command hook adds ~100–200 ms (mostly process startup). Measure on your machine with `tenuo-claude bench` after `up`.
|
|
281
|
+
|
|
282
|
+
## This repo
|
|
283
|
+
|
|
284
|
+
GitHub: [`tenuo-ai/claude-governance`](https://github.com/tenuo-ai/claude-governance) · PyPI: [`tenuo-claude-code`](https://pypi.org/project/tenuo-claude-code/)
|
|
285
|
+
|
|
286
|
+
| Path | Contents |
|
|
287
|
+
|------|----------|
|
|
288
|
+
| `src/tenuo_claude_code/` | Package source |
|
|
289
|
+
| `templates/` | Starter `tenuo.yaml` and credential examples |
|
|
290
|
+
| `examples/policies/` | Ready-made policy templates |
|
|
291
|
+
| `demo/` | Reference project and scripted tour |
|
|
292
|
+
| `docs/` | [Implementation details](docs/DETAILS.md) · [Troubleshooting](docs/TROUBLESHOOTING.md) |
|
|
@@ -0,0 +1,262 @@
|
|
|
1
|
+
# Tenuo for Claude Code
|
|
2
|
+
|
|
3
|
+
[](https://pypi.org/project/tenuo-claude-code/)
|
|
4
|
+
[](https://pypi.org/project/tenuo-claude-code/)
|
|
5
|
+
[](https://github.com/tenuo-ai/claude-governance/actions/workflows/ci.yml)
|
|
6
|
+
[](LICENSE)
|
|
7
|
+
|
|
8
|
+
Claude Code can read files, run shell commands, fetch URLs, and call MCP tools.
|
|
9
|
+
Tenuo lets you write a `tenuo.yaml` policy for which of those calls are allowed,
|
|
10
|
+
then checks every model-invoked tool call before it runs.
|
|
11
|
+
|
|
12
|
+
That policy is compiled into a signed, expiring credential called a warrant. A
|
|
13
|
+
local authorizer checks each tool call against it and logs the decision. The
|
|
14
|
+
same policy is applied no matter why the model tried the call: prompt injection,
|
|
15
|
+
hallucination, poisoned tool output, or an unsafe request.
|
|
16
|
+
|
|
17
|
+
Start with the local quickstart below. Optional Cloud control-plane setup is in
|
|
18
|
+
[Cloud mode](#cloud-mode).
|
|
19
|
+
|
|
20
|
+
## Quickstart
|
|
21
|
+
|
|
22
|
+
Requires Python 3.10+. Uses Docker if it's running; otherwise a native authorizer binary, installed automatically. On Windows, run these commands from WSL.
|
|
23
|
+
|
|
24
|
+
```bash
|
|
25
|
+
pip install tenuo-claude-code
|
|
26
|
+
mkdir my-project && cd my-project
|
|
27
|
+
tenuo-claude bootstrap
|
|
28
|
+
```
|
|
29
|
+
|
|
30
|
+
`bootstrap` writes a starter `tenuo.yaml`, starts the authorizer, and runs a self-test (`verify`). It runs non-interactively, ideal for a fresh folder. For a guided wizard with prompts, run `tenuo-claude onboard` instead; it's the same flow with a preflight `check`. The starter policy is deliberately strict:
|
|
31
|
+
|
|
32
|
+
```yaml
|
|
33
|
+
name: my-project
|
|
34
|
+
sandbox: ./workspace
|
|
35
|
+
mode: enforce
|
|
36
|
+
enforce:
|
|
37
|
+
Read: "subpath:{sandbox}" # Read only files under ./workspace
|
|
38
|
+
Bash: "shlex:ls,pwd,echo,date" # Bash only these commands
|
|
39
|
+
default: deny # every other tool call is denied
|
|
40
|
+
```
|
|
41
|
+
|
|
42
|
+
Now open Claude Code in `my-project/`:
|
|
43
|
+
|
|
44
|
+
```bash
|
|
45
|
+
claude
|
|
46
|
+
```
|
|
47
|
+
|
|
48
|
+
The agent is governed: `Read ./workspace/notes.txt` is allowed; `Read /etc/passwd`, `Bash(curl …)`, or any tool not listed is denied and logged. After Claude runs a few tools, run `tenuo-claude audit` to see the decisions. Edit `tenuo.yaml` to fit your project (see [Policy](#policy)), then `tenuo-claude refresh`.
|
|
49
|
+
|
|
50
|
+
For an example with MCP and subagents, see the [reference demo](demo/).
|
|
51
|
+
|
|
52
|
+
| Next | Go to |
|
|
53
|
+
|------|-------|
|
|
54
|
+
| Write the policy | [Policy](#policy) |
|
|
55
|
+
| Day-to-day commands | [Commands](#commands) |
|
|
56
|
+
| Org root, receipts, approvals, revocation | [Cloud mode](#cloud-mode) |
|
|
57
|
+
| Security model and limits | [Security](#security) |
|
|
58
|
+
| Something broke | [Troubleshooting](docs/TROUBLESHOOTING.md) · deep dive [docs/DETAILS.md](docs/DETAILS.md) |
|
|
59
|
+
|
|
60
|
+
## Policy
|
|
61
|
+
|
|
62
|
+
`tenuo.yaml` is the whole configuration: it drives the warrant, the authorizer, the hooks, and the MCP proxy. You list tools under `enforce:` and give each a constraint on its key argument.
|
|
63
|
+
|
|
64
|
+
```yaml
|
|
65
|
+
name: acme-backend
|
|
66
|
+
sandbox: ./workspace # a directory; {sandbox} expands to its absolute path
|
|
67
|
+
ttl_seconds: 3600 # optional: session warrant lifetime (default 3600 = 1h)
|
|
68
|
+
mode: enforce # block out-of-scope calls. 'dry-run' = log only, don't block
|
|
69
|
+
|
|
70
|
+
enforce:
|
|
71
|
+
Read: "subpath:{sandbox}"
|
|
72
|
+
Write: "subpath:{sandbox}"
|
|
73
|
+
Bash: "shlex:ls,pwd,echo,cat,grep"
|
|
74
|
+
WebFetch:
|
|
75
|
+
domains: ["api.github.com", "*.githubusercontent.com"]
|
|
76
|
+
|
|
77
|
+
default: deny # anything not listed above is denied
|
|
78
|
+
|
|
79
|
+
subagents: # optional: each role runs under a narrower warrant
|
|
80
|
+
analyst:
|
|
81
|
+
tools: [Read, Grep, Glob]
|
|
82
|
+
|
|
83
|
+
mcp: # optional: govern a downstream MCP server's tools
|
|
84
|
+
downstream: ./your_mcp_server.py
|
|
85
|
+
enforce:
|
|
86
|
+
read_file: "subpath:{sandbox}" # bare string constrains the `path` arg
|
|
87
|
+
run_query: # constrain a differently-named arg
|
|
88
|
+
arg: sql
|
|
89
|
+
constraint: "regex:^SELECT "
|
|
90
|
+
http_call: # constrain several args at once
|
|
91
|
+
args:
|
|
92
|
+
url: "urlpattern:https://api.example.com/*"
|
|
93
|
+
method: "oneof:GET,HEAD"
|
|
94
|
+
```
|
|
95
|
+
|
|
96
|
+
### Constraints
|
|
97
|
+
|
|
98
|
+
| Constraint | Applies to | What it checks |
|
|
99
|
+
|------------|------------|----------------|
|
|
100
|
+
| `subpath:DIR` | path tools (Read, Write, Edit, Glob, Grep) | the path argument must resolve to a location **inside `DIR`**. Symlinks are resolved first, so a link planted in the directory can't point outside it. |
|
|
101
|
+
| `shlex:a,b,c` | Bash, Monitor | the command's **executable** must be one of `a,b,c`, and the command must be a single simple command: pipes, `&&`/`;` chaining, subshells, and shell expansion are rejected. (This allowlists the *verb*, not file paths: `cat /etc/passwd` passes if `cat` is allowed. Use `Read`/`Write` to scope files; drop `Bash` for a hard lock.) |
|
|
102
|
+
| `domains` / `cidrs` / `schemes` / `ports` | WebFetch | the URL's host must match an allowed domain (`*` matches one label) or CIDR range, **and** pass SSRF hygiene: https-only by default (override with `schemes`), optional `ports` allowlist, with loopback, cloud-metadata IPs, encoded-IP tricks, and spoofed hosts (`api.github.com.evil.com`) blocked. |
|
|
103
|
+
| `oneof:a,b` · `notoneof:a,b` · `exact:v` · `pattern:glob` · `regex:re` · `range:min,max` · `urlpattern:url` · `cidr:n/m` | any tool argument | the value must be in the set / not in the set / equal / glob-match / regex-match / fall in the numeric range (either bound may be blank) / match the URL glob / fall inside the IP range (for any IP-based tool, not just WebFetch). |
|
|
104
|
+
|
|
105
|
+
The keys above are the `tenuo.yaml` DSL's convenient subset. The underlying tenuo engine supports more (set operations, numeric ranges, negation, boolean composition, and CEL expressions) for programmatic policies — see [tenuo](https://github.com/tenuo-ai/tenuo).
|
|
106
|
+
|
|
107
|
+
`{sandbox}` is a convenience variable for the directory in `sandbox:`; you can point `subpath:` at any path. Tools you don't list aren't governed individually; they're caught by `default`.
|
|
108
|
+
|
|
109
|
+
For internal egress, `WebFetch` also accepts `cidrs:` to allow hosts by IP range (e.g. `cidrs: ["10.0.0.0/8"]` alongside `domains:`). It's off by default and reaches past public domains and SSRF private-network defaults, so add it deliberately.
|
|
110
|
+
|
|
111
|
+
**Command-execution tools.** `Bash`, `PowerShell`, and `Monitor` all execute commands and are each governed independently (their own constraint on the `command` argument). `Monitor` runs the same shell commands as `Bash` in the background; `PowerShell` is a different dialect, so prefer `oneof`/`pattern`/`regex` over `shlex` (which parses POSIX syntax) for it. If your team enables `PowerShell` or `Monitor` in Claude Code, list them under `enforce:` too. Left unlisted they fall to `default: deny` and are blocked. Never put a shell in `allow:` — that grants it **unconstrained**; governed shells belong under `enforce:`.
|
|
112
|
+
|
|
113
|
+
**MCP tool arguments.** Under `mcp.enforce:`, a bare constraint string targets the `path` argument. To constrain a differently-named argument use `arg: NAME` + `constraint:`, and to constrain several at once use `args: {NAME: constraint, …}`. This works for any downstream MCP tool and any constraint kind, locally and on Cloud. Tools you don't list are still allowed/denied by `default` and can be human-approval gated (`approval:`); they just aren't argument-constrained.
|
|
114
|
+
|
|
115
|
+
- **`mode: enforce`** blocks denied calls. **`mode: dry-run`** computes and logs the same decisions but blocks nothing; use it to roll out a policy, then switch to `enforce`. (`mode: audit` is a deprecated alias for `dry-run`.)
|
|
116
|
+
- **`allow:`** lists extra tools permitted without constraints. Inert Claude harness tools (plan mode, TodoWrite, AskUserQuestion, …) are bundled in by default; set `allow_bundled: false` to opt out.
|
|
117
|
+
- **`default:`** is the fallback for any tool in neither `enforce` nor `allow`: **`deny`** blocks it (recommended) or **`approve`** requires human sign-off (Tenuo Cloud). There is no allow-everything fallback — enforce never fails open; use `mode: dry-run` to observe instead.
|
|
118
|
+
- **`subagents:`** declares roles; spawning is gated to those roles, and each runs under the session warrant **attenuated** to its `tools` (it can only ever do less than the session). [Details](docs/DETAILS.md#subagents).
|
|
119
|
+
- **`ttl_seconds:`** sets the session warrant lifetime in seconds (positive integer; default `3600` = 1h). `up` re-mints before expiry. Enterprise rollouts pin it centrally through Claude Code managed settings / MDM (the policy file is what managed settings pins); local dev sets it directly. A shorter TTL shrinks the blast radius of a leaked warrant.
|
|
120
|
+
|
|
121
|
+
Ready-made policies: [examples/policies/](examples/policies/). After any edit, run `tenuo-claude refresh`.
|
|
122
|
+
|
|
123
|
+
## Commands
|
|
124
|
+
|
|
125
|
+
Day to day, you mostly need `up` (start), `audit` (review), and `refresh` (after editing policy).
|
|
126
|
+
|
|
127
|
+
| Command | What it does |
|
|
128
|
+
|---------|--------------|
|
|
129
|
+
| `onboard` | Interactive first-run wizard (`--local` / `--cloud`); same flow as `bootstrap` but prompts and runs a preflight `check`. Scaffolds an example policy if you don't have one. |
|
|
130
|
+
| `bootstrap` | First-run quickstart (used above): non-interactive scaffold starter policy (if none) → `init` → `up` → `verify`. `--cloud` for Cloud. |
|
|
131
|
+
| `init` | Compile an **existing** `tenuo.yaml`: mint the warrant, wire the PreToolUse hook and MCP proxy. Pass `--scaffold` to write an example if none exists (it no longer does so automatically). |
|
|
132
|
+
| `up` / `down` | Start / stop the authorizer (auto-selects Docker or native; `--native` to force). |
|
|
133
|
+
| `refresh` | Recompile after editing `tenuo.yaml` (restarts the authorizer if running). In Cloud mode, warns if capability rules drifted from the last `tenuo-admin setup`. |
|
|
134
|
+
| `verify [--deep]` | Self-test the live policy against the authorizer (no Claude session needed). `--deep` adds an SSRF / encoded-IP matrix and extra Bash deny cases — a reproducible artifact for security review; when the local Claude CLI can load project settings, it also runs a live PreToolUse exit-code harness. |
|
|
135
|
+
| `audit [--tail N]` | Show the decision log (`.state/receipts.jsonl`). |
|
|
136
|
+
| `check` | Preflight: dependencies, wiring, audit-sink health, leaked admin keys, and (Cloud) control-plane bindings. |
|
|
137
|
+
| `status` | Warrant, mode, audit-sink health, and Cloud summary. |
|
|
138
|
+
| `install-authorizer` | Install the native authorizer to `~/.tenuo/bin` (no Docker, no Cargo). |
|
|
139
|
+
| `bench [--json]` | Measure per-call overhead on your machine (PoP sign, authorizer round-trip, full hook path). |
|
|
140
|
+
| `revoke` | Revoke the current session warrant. |
|
|
141
|
+
|
|
142
|
+
The warrant is short-lived (1h TTL by default, configurable via `ttl_seconds:` in `tenuo.yaml`); `up` refreshes it. The authorizer listens on `127.0.0.1:9090`; change it with `TENUO_AUTHORIZER_PORT` before `bootstrap`. Generated files (don't commit): `.state/` (keys, warrant, credentials), `.claude/settings.json` (hooks), `.mcp.json` (MCP wiring).
|
|
143
|
+
|
|
144
|
+
Working from a git clone instead of PyPI? See [Build from source](#build-from-source).
|
|
145
|
+
|
|
146
|
+
## How enforcement works
|
|
147
|
+
|
|
148
|
+
`init` compiles `tenuo.yaml` into a signed warrant and wires two interception points; both check the **same** warrant against the **same** local authorizer:
|
|
149
|
+
|
|
150
|
+
- **Native tools** (Read, Bash, WebFetch, …) → a Claude Code **PreToolUse hook** intercepts the call, signs a proof-of-possession with the session key, and asks the authorizer.
|
|
151
|
+
- **MCP tools** → Claude is pointed at a **proxy** that stands in for the downstream MCP server; the proxy authorizes, then forwards only if allowed.
|
|
152
|
+
|
|
153
|
+

|
|
154
|
+
|
|
155
|
+
The authorizer (a small local service, ~1–3 ms/call) verifies the warrant's signature, proof-of-possession, and expiry, then checks the call's arguments against the warrant's constraints → allow, deny, or (Cloud) approval-required. Full detail in [docs/DETAILS.md](docs/DETAILS.md).
|
|
156
|
+
|
|
157
|
+
## Cloud mode
|
|
158
|
+
|
|
159
|
+
Local mode is enough to evaluate Tenuo on one project. Connect [cloud.tenuo.ai](https://cloud.tenuo.ai) for organization-scale governance:
|
|
160
|
+
|
|
161
|
+
- **Tenant-root warrants**: sessions chain to your org root, not a key on the laptop.
|
|
162
|
+
- **Signed receipts**: one verifiable allow/deny/approval audit stream (Ed25519 over CBOR).
|
|
163
|
+
- **Fleet revocation**: revoke a warrant id; authorizers pick it up within ~30s.
|
|
164
|
+
- **Human approval gates**: specific calls pause for a person instead of allow/deny ([below](#human-approval-cloud)).
|
|
165
|
+
- **Managed rollout**: push hook/MCP wiring through Claude Code managed settings instead of per-project local settings.
|
|
166
|
+
|
|
167
|
+

|
|
168
|
+
|
|
169
|
+
### Setup
|
|
170
|
+
|
|
171
|
+
Two keys, kept apart; the runtime never sees the admin key:
|
|
172
|
+
|
|
173
|
+
| Key | From | Goes in | Used by |
|
|
174
|
+
|-----|------|---------|---------|
|
|
175
|
+
| **Runtime** (`tenuo_ct_…`) | cloud.tenuo.ai → Agents → Quick Connect → **Authorizer Only** | `.state/cloud.env` | `tenuo-claude up`, hooks |
|
|
176
|
+
| **Tenant-admin** (`tc_…`) | Settings → API Keys → Create (admin role) | `~/.tenuo/admin.env` | `tenuo-admin setup` (once) |
|
|
177
|
+
|
|
178
|
+
```bash
|
|
179
|
+
mkdir my-project && cd my-project
|
|
180
|
+
tenuo-claude bootstrap --cloud # runtime token from --connect-token/env, or prompts if missing; then sets up + verifies
|
|
181
|
+
```
|
|
182
|
+
|
|
183
|
+
Every session after that:
|
|
184
|
+
|
|
185
|
+
```bash
|
|
186
|
+
tenuo-claude check && tenuo-claude up
|
|
187
|
+
```
|
|
188
|
+
|
|
189
|
+
If `check` reports a **cloud bindings** failure, run `tenuo-admin setup` and retry.
|
|
190
|
+
|
|
191
|
+
> `tenuo-claude up` refuses to start if a tenant-admin key is in the environment; keep it only in `~/.tenuo/admin.env`. And once a project is on Cloud, don't re-run plain `bootstrap`: it reverts the project to local mode and moves your Cloud files aside. Use `check && up`.
|
|
192
|
+
|
|
193
|
+
CI / non-interactive and manual step-by-step setup: [docs/DETAILS.md § Tenuo Cloud](docs/DETAILS.md#tenuo-cloud-extended). After changing `enforce`/`mcp`/`subagents`/approvals on Cloud, re-run `tenuo-admin setup`; for `mode`-only changes, `refresh` suffices.
|
|
194
|
+
|
|
195
|
+
### Human approval (Cloud)
|
|
196
|
+
|
|
197
|
+
A gated capability returns a third outcome, `approval-required`, instead of allow/deny. The hook opens a Cloud approval request, waits for an approver on their notification channel (Slack, Telegram, console, …), then re-authorizes with their **signed, identity-bound** approval — so the receipt records *who* approved. Add an `approval:` block to **any enforced native tool** (e.g. `Bash`), **any `mcp.enforce` tool**, or `WebFetch`; an optional `exempt:` lets safe argument values skip the gate. `default: approve` gates every unlisted tool.
|
|
198
|
+
|
|
199
|
+
**Human approval requires Tenuo Cloud — anywhere (native hook, MCP proxy, or catch-all).** The gate lives in the Cloud-issued warrant, so without Cloud an approval-gated tool falls back to **deny** (fail-closed); `tenuo-claude check` warns when a gate is configured but Cloud isn't. Setup and policy shape: [docs/DETAILS.md § Human approval](docs/DETAILS.md#human-approval-cloud).
|
|
200
|
+
|
|
201
|
+

|
|
202
|
+
|
|
203
|
+
## Security
|
|
204
|
+
|
|
205
|
+
Tenuo runs **alongside** Claude Code permissions; it doesn't replace managed settings. The difference is where and how policy is enforced:
|
|
206
|
+
|
|
207
|
+
| | Claude Code permissions | Tenuo warrant |
|
|
208
|
+
|---|---|---|
|
|
209
|
+
| Form | Allow/ask/deny rules in settings | Signed, expiring capability token; Cloud chains to your org root |
|
|
210
|
+
| Enforcement point | Claude's permission UI | PreToolUse hook + MCP proxy, checked by the authorizer |
|
|
211
|
+
| `--dangerously-skip-permissions` | Skips the prompts | Does not disable installed Tenuo hook/proxy checks |
|
|
212
|
+
| Expiry | Until edited | Session TTL (1h default, set via `ttl_seconds:`); `up` refreshes |
|
|
213
|
+
| Revocation | Edit rules (live sessions may keep allowances) | Revoke warrant id → ~30s fleet sync (Cloud) |
|
|
214
|
+
| Evidence | Optional hook logs | Local JSONL; signed receipt stream in Cloud |
|
|
215
|
+
| Org deployment | Per-user settings, locally editable | Managed-settings hooks + shared policy |
|
|
216
|
+
|
|
217
|
+
Admins can also block the bypass flag entirely in managed settings (`disableBypassPermissionsMode`).
|
|
218
|
+
|
|
219
|
+
**What's in scope.** Tenuo governs **model-invoked tool calls** (Read, Bash, WebFetch, MCP tools, subagent spawns) on the PreToolUse path, including the agent's own Bash. The TUI `!` shell (a command the *operator* types) is not a tool call and is out of scope; the model can't invoke it. ([details](docs/DETAILS.md#agent-tools-vs-operator-shell))
|
|
220
|
+
|
|
221
|
+
**Fail-closed.** A missing or broken `tenuo.yaml` denies every governed call until it's restored. Keys under `.state/` must be owner-only (`0600`).
|
|
222
|
+
|
|
223
|
+
**Receipts.** Every governed call carries a proof-of-possession signature the authorizer verifies. Locally, the hook appends a JSON line to `.state/receipts.jsonl` (read with `tenuo-claude audit`; in `mode: dry-run`, denials show as `WOULD-DENY`):
|
|
224
|
+
|
|
225
|
+
```json
|
|
226
|
+
{"phase":"pre","decision":"deny","claude_tool":"Read","governed":true,
|
|
227
|
+
"args":{"file_path":"/etc/passwd"},"reason":"Constraint not satisfied"}
|
|
228
|
+
```
|
|
229
|
+
|
|
230
|
+
Connected to Cloud, the authorizer also emits **signed** receipts to your tenant, the verifiable record for compliance and fleet audit.
|
|
231
|
+
|
|
232
|
+
**Rolling out to a team.** Keep `tenuo.yaml` in version control, push the hook/MCP wiring through Claude Code **managed settings** (not per-developer `settings.local.json`), and use Cloud for org-root warrants, central audit, and revocation. Start in `mode: dry-run`, review the `WOULD-DENY` rows, then switch to `enforce`. [Talk to us](https://tenuo.ai/early-access.html) about managed-settings rollout. Report issues: [SECURITY.md](SECURITY.md).
|
|
233
|
+
|
|
234
|
+
## Build from source
|
|
235
|
+
|
|
236
|
+
For development, running the demo from a checkout, or using `./bin/tenuo-claude`:
|
|
237
|
+
|
|
238
|
+
```bash
|
|
239
|
+
git clone https://github.com/tenuo-ai/claude-governance.git
|
|
240
|
+
cd claude-governance
|
|
241
|
+
uv venv && uv sync && source .venv/bin/activate # Windows: .venv\Scripts\activate
|
|
242
|
+
chmod +x bin/tenuo-claude
|
|
243
|
+
uv run tenuo-claude install-authorizer # only if you don't use Docker
|
|
244
|
+
```
|
|
245
|
+
|
|
246
|
+
Run via `./bin/tenuo-claude --help`, `uv run tenuo-claude --help`, or `pip install -e .`. Re-run `tenuo-claude init` (or `refresh`) after moving the repo or reinstalling. The hooks pin the launcher path at wiring time. Contributors: [CONTRIBUTING.md](CONTRIBUTING.md).
|
|
247
|
+
|
|
248
|
+
## Performance
|
|
249
|
+
|
|
250
|
+
Authorization is ~1–3 ms per call; the command hook adds ~100–200 ms (mostly process startup). Measure on your machine with `tenuo-claude bench` after `up`.
|
|
251
|
+
|
|
252
|
+
## This repo
|
|
253
|
+
|
|
254
|
+
GitHub: [`tenuo-ai/claude-governance`](https://github.com/tenuo-ai/claude-governance) · PyPI: [`tenuo-claude-code`](https://pypi.org/project/tenuo-claude-code/)
|
|
255
|
+
|
|
256
|
+
| Path | Contents |
|
|
257
|
+
|------|----------|
|
|
258
|
+
| `src/tenuo_claude_code/` | Package source |
|
|
259
|
+
| `templates/` | Starter `tenuo.yaml` and credential examples |
|
|
260
|
+
| `examples/policies/` | Ready-made policy templates |
|
|
261
|
+
| `demo/` | Reference project and scripted tour |
|
|
262
|
+
| `docs/` | [Implementation details](docs/DETAILS.md) · [Troubleshooting](docs/TROUBLESHOOTING.md) |
|