attackmap 0.6.4__tar.gz
This diff represents the content of publicly available package versions that have been released to one of the supported registries. The information contained in this diff is provided for informational purposes only and reflects changes between package versions as they appear in their respective public registries.
- attackmap-0.6.4/LICENSE +21 -0
- attackmap-0.6.4/PKG-INFO +226 -0
- attackmap-0.6.4/README.md +161 -0
- attackmap-0.6.4/pyproject.toml +122 -0
- attackmap-0.6.4/setup.cfg +4 -0
- attackmap-0.6.4/src/attackmap/__init__.py +2 -0
- attackmap-0.6.4/src/attackmap/analyzer.py +449 -0
- attackmap-0.6.4/src/attackmap/analyzer_contracts.py +194 -0
- attackmap-0.6.4/src/attackmap/analyzers.py +1003 -0
- attackmap-0.6.4/src/attackmap/anomalies.py +612 -0
- attackmap-0.6.4/src/attackmap/asset_model.py +245 -0
- attackmap-0.6.4/src/attackmap/attack_taxonomy.py +133 -0
- attackmap-0.6.4/src/attackmap/auth_protocol.py +702 -0
- attackmap-0.6.4/src/attackmap/authz.py +1695 -0
- attackmap-0.6.4/src/attackmap/bench.py +467 -0
- attackmap-0.6.4/src/attackmap/cli.py +1474 -0
- attackmap-0.6.4/src/attackmap/config_scanner.py +389 -0
- attackmap-0.6.4/src/attackmap/context_pack.py +82 -0
- attackmap-0.6.4/src/attackmap/contracts.py +201 -0
- attackmap-0.6.4/src/attackmap/control_model.py +280 -0
- attackmap-0.6.4/src/attackmap/crossrepo.py +356 -0
- attackmap-0.6.4/src/attackmap/crypto.py +240 -0
- attackmap-0.6.4/src/attackmap/cve.py +717 -0
- attackmap-0.6.4/src/attackmap/defensive_review.py +647 -0
- attackmap-0.6.4/src/attackmap/detection_opportunities.py +1221 -0
- attackmap-0.6.4/src/attackmap/detections/__init__.py +491 -0
- attackmap-0.6.4/src/attackmap/detections/bola.yml +57 -0
- attackmap-0.6.4/src/attackmap/detections/cloud.yml +609 -0
- attackmap-0.6.4/src/attackmap/detections/injection.yml +167 -0
- attackmap-0.6.4/src/attackmap/detections/secrets.yml +48 -0
- attackmap-0.6.4/src/attackmap/detections/sigma.py +511 -0
- attackmap-0.6.4/src/attackmap/detections/ssrf.yml +98 -0
- attackmap-0.6.4/src/attackmap/detections/weakness.yml +62 -0
- attackmap-0.6.4/src/attackmap/detections/webhook.yml +45 -0
- attackmap-0.6.4/src/attackmap/detections/workflow.yml +121 -0
- attackmap-0.6.4/src/attackmap/diagrams.py +237 -0
- attackmap-0.6.4/src/attackmap/diff.py +301 -0
- attackmap-0.6.4/src/attackmap/exploitability.py +493 -0
- attackmap-0.6.4/src/attackmap/fingerprint.py +91 -0
- attackmap-0.6.4/src/attackmap/fleet.py +370 -0
- attackmap-0.6.4/src/attackmap/gitref.py +129 -0
- attackmap-0.6.4/src/attackmap/graph.py +26 -0
- attackmap-0.6.4/src/attackmap/handler_auth.py +639 -0
- attackmap-0.6.4/src/attackmap/handler_span.py +62 -0
- attackmap-0.6.4/src/attackmap/hunt_harness.py +505 -0
- attackmap-0.6.4/src/attackmap/insights.py +701 -0
- attackmap-0.6.4/src/attackmap/llm_review.py +846 -0
- attackmap-0.6.4/src/attackmap/lockfiles.py +521 -0
- attackmap-0.6.4/src/attackmap/mass_assignment.py +543 -0
- attackmap-0.6.4/src/attackmap/md.py +175 -0
- attackmap-0.6.4/src/attackmap/merge.py +333 -0
- attackmap-0.6.4/src/attackmap/models.py +1284 -0
- attackmap-0.6.4/src/attackmap/plugins_lock.py +114 -0
- attackmap-0.6.4/src/attackmap/popular_packages.py +193 -0
- attackmap-0.6.4/src/attackmap/progress.py +258 -0
- attackmap-0.6.4/src/attackmap/recon_models.py +31 -0
- attackmap-0.6.4/src/attackmap/recon_to_analysis.py +149 -0
- attackmap-0.6.4/src/attackmap/redact.py +220 -0
- attackmap-0.6.4/src/attackmap/report.py +424 -0
- attackmap-0.6.4/src/attackmap/review_eval.py +335 -0
- attackmap-0.6.4/src/attackmap/review_json.py +308 -0
- attackmap-0.6.4/src/attackmap/review_prompts.py +796 -0
- attackmap-0.6.4/src/attackmap/route_auth_fusion.py +474 -0
- attackmap-0.6.4/src/attackmap/safe_fs.py +285 -0
- attackmap-0.6.4/src/attackmap/sarif.py +373 -0
- attackmap-0.6.4/src/attackmap/sbom.py +418 -0
- attackmap-0.6.4/src/attackmap/scanner.py +1379 -0
- attackmap-0.6.4/src/attackmap/sdk/__init__.py +278 -0
- attackmap-0.6.4/src/attackmap/sdk/contracts.py +17 -0
- attackmap-0.6.4/src/attackmap/sdk/fs.py +156 -0
- attackmap-0.6.4/src/attackmap/sdk/models.py +59 -0
- attackmap-0.6.4/src/attackmap/secrets_history.py +161 -0
- attackmap-0.6.4/src/attackmap/security_overlay.py +71 -0
- attackmap-0.6.4/src/attackmap/srcpaths.py +301 -0
- attackmap-0.6.4/src/attackmap/suggest.py +394 -0
- attackmap-0.6.4/src/attackmap/supply_chain.py +688 -0
- attackmap-0.6.4/src/attackmap/suppress.py +740 -0
- attackmap-0.6.4/src/attackmap/taint.py +1540 -0
- attackmap-0.6.4/src/attackmap/taint_flow.py +1419 -0
- attackmap-0.6.4/src/attackmap/taint_sinks.py +431 -0
- attackmap-0.6.4/src/attackmap/taint_sinks.yaml +308 -0
- attackmap-0.6.4/src/attackmap/taint_sources.py +396 -0
- attackmap-0.6.4/src/attackmap/taxonomy.py +465 -0
- attackmap-0.6.4/src/attackmap/threat_model.py +3441 -0
- attackmap-0.6.4/src/attackmap/topology.py +316 -0
- attackmap-0.6.4/src/attackmap/triage.py +151 -0
- attackmap-0.6.4/src/attackmap/weaknesses.py +365 -0
- attackmap-0.6.4/src/attackmap/webhardening.py +479 -0
- attackmap-0.6.4/src/attackmap/webhook_verification.py +1067 -0
- attackmap-0.6.4/src/attackmap/workflow_scanner.py +964 -0
- attackmap-0.6.4/src/attackmap.egg-info/PKG-INFO +226 -0
- attackmap-0.6.4/src/attackmap.egg-info/SOURCES.txt +210 -0
- attackmap-0.6.4/src/attackmap.egg-info/dependency_links.txt +1 -0
- attackmap-0.6.4/src/attackmap.egg-info/entry_points.txt +2 -0
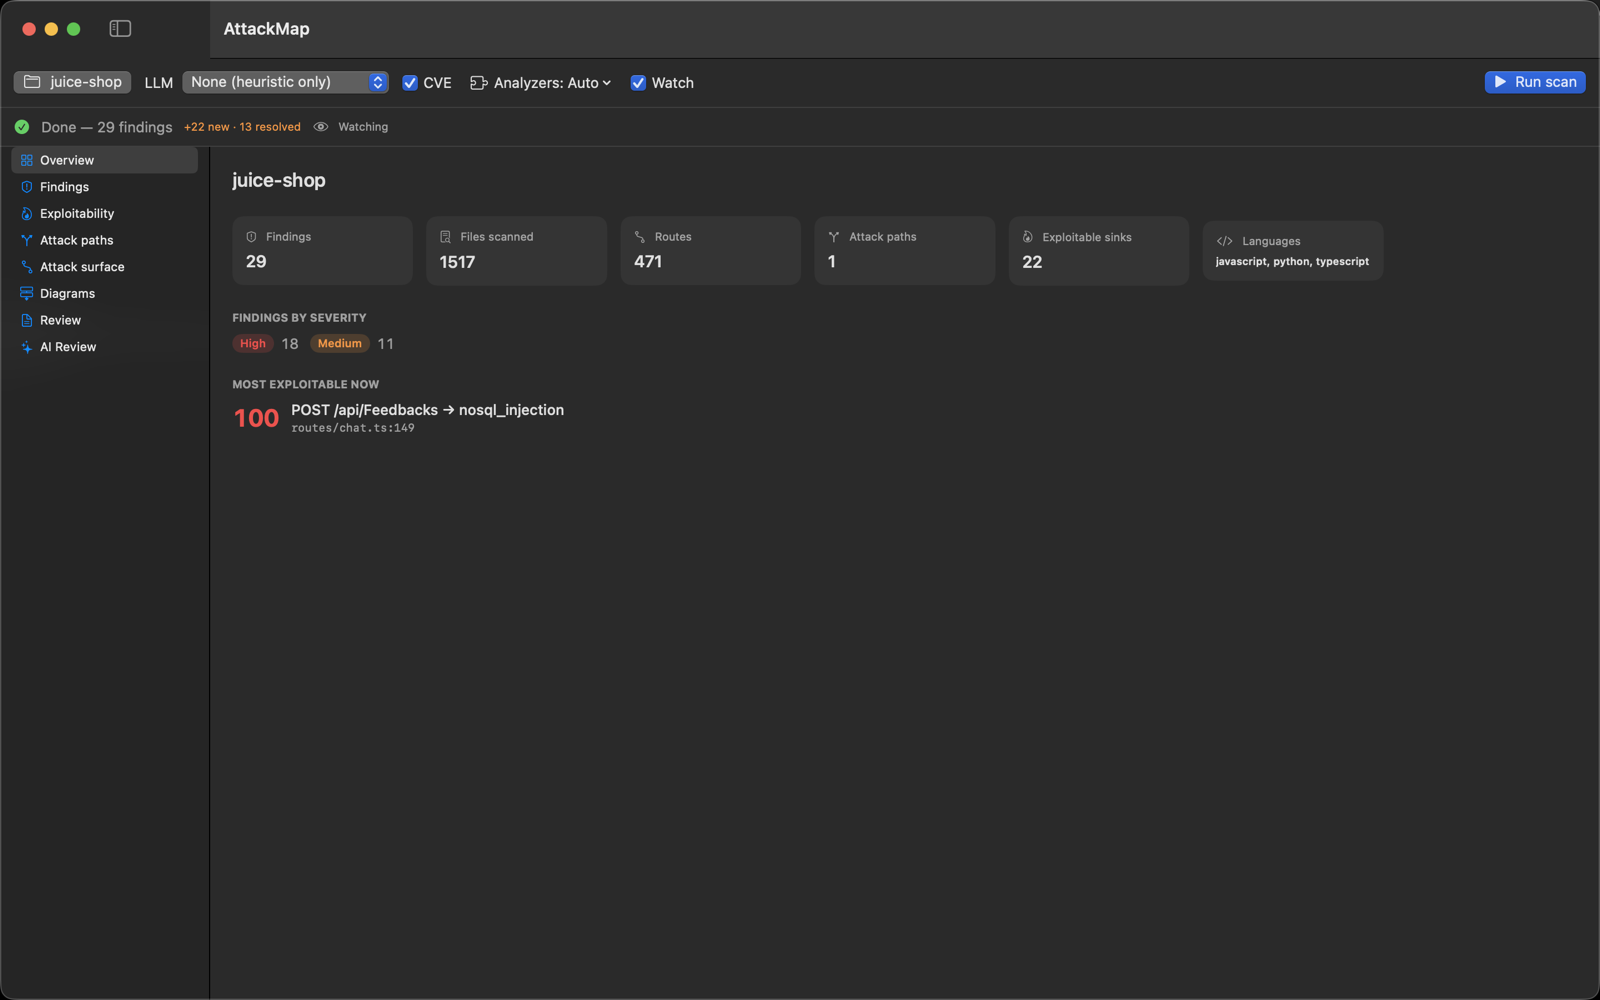
- attackmap-0.6.4/src/attackmap.egg-info/requires.txt +33 -0
- attackmap-0.6.4/src/attackmap.egg-info/top_level.txt +1 -0
- attackmap-0.6.4/tests/test_analyzer.py +297 -0
- attackmap-0.6.4/tests/test_analyzer_isolation.py +94 -0
- attackmap-0.6.4/tests/test_analyzer_metadata_schema.py +194 -0
- attackmap-0.6.4/tests/test_analyzer_order.py +92 -0
- attackmap-0.6.4/tests/test_analyzers.py +816 -0
- attackmap-0.6.4/tests/test_anomalies.py +663 -0
- attackmap-0.6.4/tests/test_app_surface.py +192 -0
- attackmap-0.6.4/tests/test_artifact_schemas.py +39 -0
- attackmap-0.6.4/tests/test_auth_protocol.py +259 -0
- attackmap-0.6.4/tests/test_auth_route_category.py +62 -0
- attackmap-0.6.4/tests/test_authz.py +1701 -0
- attackmap-0.6.4/tests/test_bench.py +249 -0
- attackmap-0.6.4/tests/test_capabilities.py +26 -0
- attackmap-0.6.4/tests/test_cli_validation.py +84 -0
- attackmap-0.6.4/tests/test_cloud_misconfig.py +407 -0
- attackmap-0.6.4/tests/test_config_scanner.py +305 -0
- attackmap-0.6.4/tests/test_context_pack.py +46 -0
- attackmap-0.6.4/tests/test_contracts.py +194 -0
- attackmap-0.6.4/tests/test_crossrepo.py +328 -0
- attackmap-0.6.4/tests/test_crypto.py +285 -0
- attackmap-0.6.4/tests/test_cve.py +779 -0
- attackmap-0.6.4/tests/test_defensive_review.py +360 -0
- attackmap-0.6.4/tests/test_detection_rules.py +683 -0
- attackmap-0.6.4/tests/test_detection_rules_cloud.py +278 -0
- attackmap-0.6.4/tests/test_detection_rules_part2.py +419 -0
- attackmap-0.6.4/tests/test_determinism.py +94 -0
- attackmap-0.6.4/tests/test_diagrams.py +256 -0
- attackmap-0.6.4/tests/test_diff.py +369 -0
- attackmap-0.6.4/tests/test_exploitability.py +329 -0
- attackmap-0.6.4/tests/test_finding_locations.py +149 -0
- attackmap-0.6.4/tests/test_fleet.py +319 -0
- attackmap-0.6.4/tests/test_gitref_hardening.py +54 -0
- attackmap-0.6.4/tests/test_graph.py +16 -0
- attackmap-0.6.4/tests/test_handler_session_gate.py +603 -0
- attackmap-0.6.4/tests/test_handler_span.py +53 -0
- attackmap-0.6.4/tests/test_hunt.py +206 -0
- attackmap-0.6.4/tests/test_hunt_harness.py +559 -0
- attackmap-0.6.4/tests/test_injection_sinks.py +310 -0
- attackmap-0.6.4/tests/test_inline_scope.py +103 -0
- attackmap-0.6.4/tests/test_install_isolation.py +73 -0
- attackmap-0.6.4/tests/test_instance_diff.py +114 -0
- attackmap-0.6.4/tests/test_js_suffixes.py +26 -0
- attackmap-0.6.4/tests/test_llm_cli_isolation.py +186 -0
- attackmap-0.6.4/tests/test_llm_markdown_sanitizer.py +51 -0
- attackmap-0.6.4/tests/test_llm_review.py +697 -0
- attackmap-0.6.4/tests/test_lockfiles.py +479 -0
- attackmap-0.6.4/tests/test_markdown_escaping.py +279 -0
- attackmap-0.6.4/tests/test_mass_assignment.py +332 -0
- attackmap-0.6.4/tests/test_merge.py +196 -0
- attackmap-0.6.4/tests/test_modules_cli.py +44 -0
- attackmap-0.6.4/tests/test_native_weaknesses.py +237 -0
- attackmap-0.6.4/tests/test_oauth_session.py +213 -0
- attackmap-0.6.4/tests/test_output_exclusion.py +199 -0
- attackmap-0.6.4/tests/test_output_format.py +159 -0
- attackmap-0.6.4/tests/test_pr_comment.py +49 -0
- attackmap-0.6.4/tests/test_progress.py +183 -0
- attackmap-0.6.4/tests/test_prompt_injection.py +140 -0
- attackmap-0.6.4/tests/test_provenance.py +208 -0
- attackmap-0.6.4/tests/test_recall.py +310 -0
- attackmap-0.6.4/tests/test_recon_to_analysis.py +126 -0
- attackmap-0.6.4/tests/test_redact.py +172 -0
- attackmap-0.6.4/tests/test_regex_budget.py +97 -0
- attackmap-0.6.4/tests/test_remediate.py +65 -0
- attackmap-0.6.4/tests/test_report.py +52 -0
- attackmap-0.6.4/tests/test_review_eval.py +165 -0
- attackmap-0.6.4/tests/test_review_json.py +92 -0
- attackmap-0.6.4/tests/test_review_prompts.py +96 -0
- attackmap-0.6.4/tests/test_route_auth_contract.py +82 -0
- attackmap-0.6.4/tests/test_route_auth_fusion.py +355 -0
- attackmap-0.6.4/tests/test_route_twins.py +315 -0
- attackmap-0.6.4/tests/test_rule_ids.py +95 -0
- attackmap-0.6.4/tests/test_safe_fs.py +216 -0
- attackmap-0.6.4/tests/test_sarif.py +221 -0
- attackmap-0.6.4/tests/test_sarif_identity.py +96 -0
- attackmap-0.6.4/tests/test_sbom.py +250 -0
- attackmap-0.6.4/tests/test_scan_limits.py +227 -0
- attackmap-0.6.4/tests/test_scanner.py +1294 -0
- attackmap-0.6.4/tests/test_sdk_fs.py +130 -0
- attackmap-0.6.4/tests/test_secret_precision.py +80 -0
- attackmap-0.6.4/tests/test_secrets_deep.py +267 -0
- attackmap-0.6.4/tests/test_security_overlay.py +353 -0
- attackmap-0.6.4/tests/test_severity_tiers.py +138 -0
- attackmap-0.6.4/tests/test_shared_contract_imports.py +66 -0
- attackmap-0.6.4/tests/test_signal_v2.py +207 -0
- attackmap-0.6.4/tests/test_signal_v2_core.py +75 -0
- attackmap-0.6.4/tests/test_single_pass.py +70 -0
- attackmap-0.6.4/tests/test_sink_args.py +106 -0
- attackmap-0.6.4/tests/test_skip_dirs.py +66 -0
- attackmap-0.6.4/tests/test_srcpaths.py +246 -0
- attackmap-0.6.4/tests/test_suggest.py +281 -0
- attackmap-0.6.4/tests/test_supply_chain.py +220 -0
- attackmap-0.6.4/tests/test_supply_chain_risk.py +250 -0
- attackmap-0.6.4/tests/test_suppress.py +355 -0
- attackmap-0.6.4/tests/test_suppress_file_validation.py +86 -0
- attackmap-0.6.4/tests/test_suppression_governance.py +283 -0
- attackmap-0.6.4/tests/test_taint.py +694 -0
- attackmap-0.6.4/tests/test_taint_flow.py +568 -0
- attackmap-0.6.4/tests/test_taint_sanitizer.py +122 -0
- attackmap-0.6.4/tests/test_taint_sinks.py +263 -0
- attackmap-0.6.4/tests/test_taint_urlconf.py +247 -0
- attackmap-0.6.4/tests/test_taxonomy.py +250 -0
- attackmap-0.6.4/tests/test_threat_intel.py +272 -0
- attackmap-0.6.4/tests/test_threat_model.py +740 -0
- attackmap-0.6.4/tests/test_topology.py +220 -0
- attackmap-0.6.4/tests/test_triage.py +201 -0
- attackmap-0.6.4/tests/test_type_hints.py +41 -0
- attackmap-0.6.4/tests/test_unreadable_and_fleet_failures.py +79 -0
- attackmap-0.6.4/tests/test_weaknesses.py +276 -0
- attackmap-0.6.4/tests/test_web_api_hardening.py +286 -0
- attackmap-0.6.4/tests/test_webhardening.py +467 -0
- attackmap-0.6.4/tests/test_webhook_management.py +286 -0
- attackmap-0.6.4/tests/test_webhook_reach.py +269 -0
- attackmap-0.6.4/tests/test_webhook_reach_frameworks.py +509 -0
- attackmap-0.6.4/tests/test_webhook_verification.py +263 -0
- attackmap-0.6.4/tests/test_workflow_rules.py +384 -0
- attackmap-0.6.4/tests/test_workflow_scanner.py +463 -0
attackmap-0.6.4/LICENSE
ADDED
|
@@ -0,0 +1,21 @@
|
|
|
1
|
+
MIT License
|
|
2
|
+
|
|
3
|
+
Copyright (c) 2026 Matthew Davis and AttackMap Contributors
|
|
4
|
+
|
|
5
|
+
Permission is hereby granted, free of charge, to any person obtaining a copy
|
|
6
|
+
of this software and associated documentation files (the "Software"), to deal
|
|
7
|
+
in the Software without restriction, including without limitation the rights
|
|
8
|
+
to use, copy, modify, merge, publish, distribute, sublicense, and/or sell
|
|
9
|
+
copies of the Software, and to permit persons to whom the Software is
|
|
10
|
+
furnished to do so, subject to the following conditions:
|
|
11
|
+
|
|
12
|
+
The above copyright notice and this permission notice shall be included in all
|
|
13
|
+
copies or substantial portions of the Software.
|
|
14
|
+
|
|
15
|
+
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR
|
|
16
|
+
IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY,
|
|
17
|
+
FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE
|
|
18
|
+
AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER
|
|
19
|
+
LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM,
|
|
20
|
+
OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE
|
|
21
|
+
SOFTWARE.
|
attackmap-0.6.4/PKG-INFO
ADDED
|
@@ -0,0 +1,226 @@
|
|
|
1
|
+
Metadata-Version: 2.4
|
|
2
|
+
Name: attackmap
|
|
3
|
+
Version: 0.6.4
|
|
4
|
+
Summary: AI-assisted defensive security analyzer for codebases — scans a repository, models assets and controls, finds cross-cutting weaknesses, and generates an evidence-grounded review with MITRE ATT&CK mappings and detection-engineering hints.
|
|
5
|
+
Author: AttackMap Contributors
|
|
6
|
+
Author-email: Matthew Davis <mlaify@mlaify.io>
|
|
7
|
+
Maintainer-email: Matthew Davis <mlaify@mlaify.io>
|
|
8
|
+
License: MIT
|
|
9
|
+
Project-URL: Homepage, https://github.com/mlaify/AttackMap
|
|
10
|
+
Project-URL: Documentation, https://github.com/mlaify/AttackMap/wiki
|
|
11
|
+
Project-URL: Repository, https://github.com/mlaify/AttackMap
|
|
12
|
+
Project-URL: Issues, https://github.com/mlaify/AttackMap/issues
|
|
13
|
+
Project-URL: Changelog, https://github.com/mlaify/AttackMap/blob/main/CHANGELOG.md
|
|
14
|
+
Keywords: security,static-analysis,appsec,defensive-security,threat-modeling,attack-surface,mitre-attack,detection-engineering,code-review,llm,claude
|
|
15
|
+
Classifier: Development Status :: 4 - Beta
|
|
16
|
+
Classifier: Environment :: Console
|
|
17
|
+
Classifier: Intended Audience :: Developers
|
|
18
|
+
Classifier: Intended Audience :: Information Technology
|
|
19
|
+
Classifier: Intended Audience :: System Administrators
|
|
20
|
+
Classifier: License :: OSI Approved :: MIT License
|
|
21
|
+
Classifier: Operating System :: OS Independent
|
|
22
|
+
Classifier: Programming Language :: Python :: 3
|
|
23
|
+
Classifier: Programming Language :: Python :: 3.11
|
|
24
|
+
Classifier: Programming Language :: Python :: 3.12
|
|
25
|
+
Classifier: Programming Language :: Python :: 3.13
|
|
26
|
+
Classifier: Programming Language :: Python :: 3 :: Only
|
|
27
|
+
Classifier: Topic :: Security
|
|
28
|
+
Classifier: Topic :: Software Development :: Quality Assurance
|
|
29
|
+
Classifier: Topic :: Software Development :: Testing
|
|
30
|
+
Classifier: Typing :: Typed
|
|
31
|
+
Requires-Python: >=3.11
|
|
32
|
+
Description-Content-Type: text/markdown
|
|
33
|
+
License-File: LICENSE
|
|
34
|
+
Requires-Dist: typer>=0.12.3
|
|
35
|
+
Requires-Dist: pydantic>=2.7.0
|
|
36
|
+
Requires-Dist: networkx>=3.3
|
|
37
|
+
Requires-Dist: PyYAML>=6.0
|
|
38
|
+
Provides-Extra: llm
|
|
39
|
+
Requires-Dist: anthropic>=0.40.0; extra == "llm"
|
|
40
|
+
Requires-Dist: openai>=1.60.0; extra == "llm"
|
|
41
|
+
Provides-Extra: all
|
|
42
|
+
Requires-Dist: attackmap[llm]; extra == "all"
|
|
43
|
+
Requires-Dist: attackmap-analyzer-python==0.2.0; extra == "all"
|
|
44
|
+
Requires-Dist: attackmap-analyzer-rust==0.2.0; extra == "all"
|
|
45
|
+
Requires-Dist: attackmap-analyzer-go==0.2.0; extra == "all"
|
|
46
|
+
Requires-Dist: attackmap-analyzer-java-spring==0.2.0; extra == "all"
|
|
47
|
+
Requires-Dist: attackmap-analyzer-dotnet==0.2.0; extra == "all"
|
|
48
|
+
Requires-Dist: attackmap-analyzer-terraform==0.2.1; extra == "all"
|
|
49
|
+
Requires-Dist: attackmap-analyzer-c==0.2.0; extra == "all"
|
|
50
|
+
Requires-Dist: attackmap-analyzer-cpp==0.2.0; extra == "all"
|
|
51
|
+
Requires-Dist: attackmap-analyzer-swift==0.2.0; extra == "all"
|
|
52
|
+
Requires-Dist: attackmap-analyzer-node-service==0.3.0; extra == "all"
|
|
53
|
+
Requires-Dist: attackmap-analyzer-atproto==0.2.0; extra == "all"
|
|
54
|
+
Requires-Dist: attackmap-analyzer-php-web==0.2.0; extra == "all"
|
|
55
|
+
Requires-Dist: attackmap-analyzer-php-laminas==0.2.0; extra == "all"
|
|
56
|
+
Requires-Dist: attackmap-analyzer-omeka-s==0.2.0; extra == "all"
|
|
57
|
+
Requires-Dist: attackmap-analyzer-iac==0.2.0; extra == "all"
|
|
58
|
+
Provides-Extra: dev
|
|
59
|
+
Requires-Dist: pytest>=8.0.0; extra == "dev"
|
|
60
|
+
Requires-Dist: build>=1.2.0; extra == "dev"
|
|
61
|
+
Requires-Dist: jsonschema>=4.0; extra == "dev"
|
|
62
|
+
Requires-Dist: pysigma>=2.0; extra == "dev"
|
|
63
|
+
Requires-Dist: ruff>=0.6; extra == "dev"
|
|
64
|
+
Dynamic: license-file
|
|
65
|
+
|
|
66
|
+
# AttackMap
|
|
67
|
+
|
|
68
|
+
> [!IMPORTANT]
|
|
69
|
+
> **Active development, slow pace.** AttackMap is under active development, but
|
|
70
|
+
> progress may be slow until more contributors or co-maintainers join. Help is
|
|
71
|
+
> very welcome with the core engine, an analyzer, the macOS app, or the docs —
|
|
72
|
+
> see [CONTRIBUTING.md](https://github.com/mlaify/AttackMap/blob/main/CONTRIBUTING.md) or open an issue on
|
|
73
|
+
> [mlaify/AttackMap](https://github.com/mlaify/AttackMap/issues) to say hello.
|
|
74
|
+
> Security reports are still welcome at [security@mlaify.io](mailto:security@mlaify.io).
|
|
75
|
+
|
|
76
|
+
**Local-first, AI-assisted defensive security analysis for codebases.** AttackMap
|
|
77
|
+
reads a repository (or a whole fleet of them), reconstructs the attack surface —
|
|
78
|
+
routes, data stores, external calls, auth signals, trust boundaries — traces
|
|
79
|
+
request-to-sink data flow, and produces an evidence-grounded, prioritized security
|
|
80
|
+
review. It finds the cross-cutting weaknesses single-file scanners miss, and never
|
|
81
|
+
sends your code anywhere.
|
|
82
|
+
|
|
83
|
+
[](https://github.com/mlaify/AttackMap/blob/main/LICENSE)
|
|
84
|
+
[](https://www.python.org/)
|
|
85
|
+
|
|
86
|
+
> **Status: beta (v0.6.4).** Core engine + 15 analyzer plugins, published on
|
|
87
|
+
> [PyPI](https://pypi.org/project/attackmap/) and validated on real codebases. AttackMap is heuristic by
|
|
88
|
+
> design — findings are confidence-tiered evidence, not proof. Roadmap to 1.0:
|
|
89
|
+
> [issue #209](https://github.com/mlaify/AttackMap/issues/209).
|
|
90
|
+
|
|
91
|
+
Full documentation: **[docs.mlaify.io](https://docs.mlaify.io)** ·
|
|
92
|
+
architecture & internals: **[wiki](https://github.com/mlaify/AttackMap/wiki)**.
|
|
93
|
+
|
|
94
|
+
### The macOS app
|
|
95
|
+
|
|
96
|
+
Prefer a GUI? A native macOS front-end drives this CLI and renders every result
|
|
97
|
+
view. Install it with Homebrew (this also installs the CLI), or build it from
|
|
98
|
+
source at [mlaify/AttackMap-mac](https://github.com/mlaify/AttackMap-mac):
|
|
99
|
+
|
|
100
|
+
```bash
|
|
101
|
+
brew install --cask mlaify/tap/attackmap-app
|
|
102
|
+
```
|
|
103
|
+
|
|
104
|
+
| Overview | Exploitability |
|
|
105
|
+
|---|---|
|
|
106
|
+
| [](https://docs.mlaify.io/gui/) | [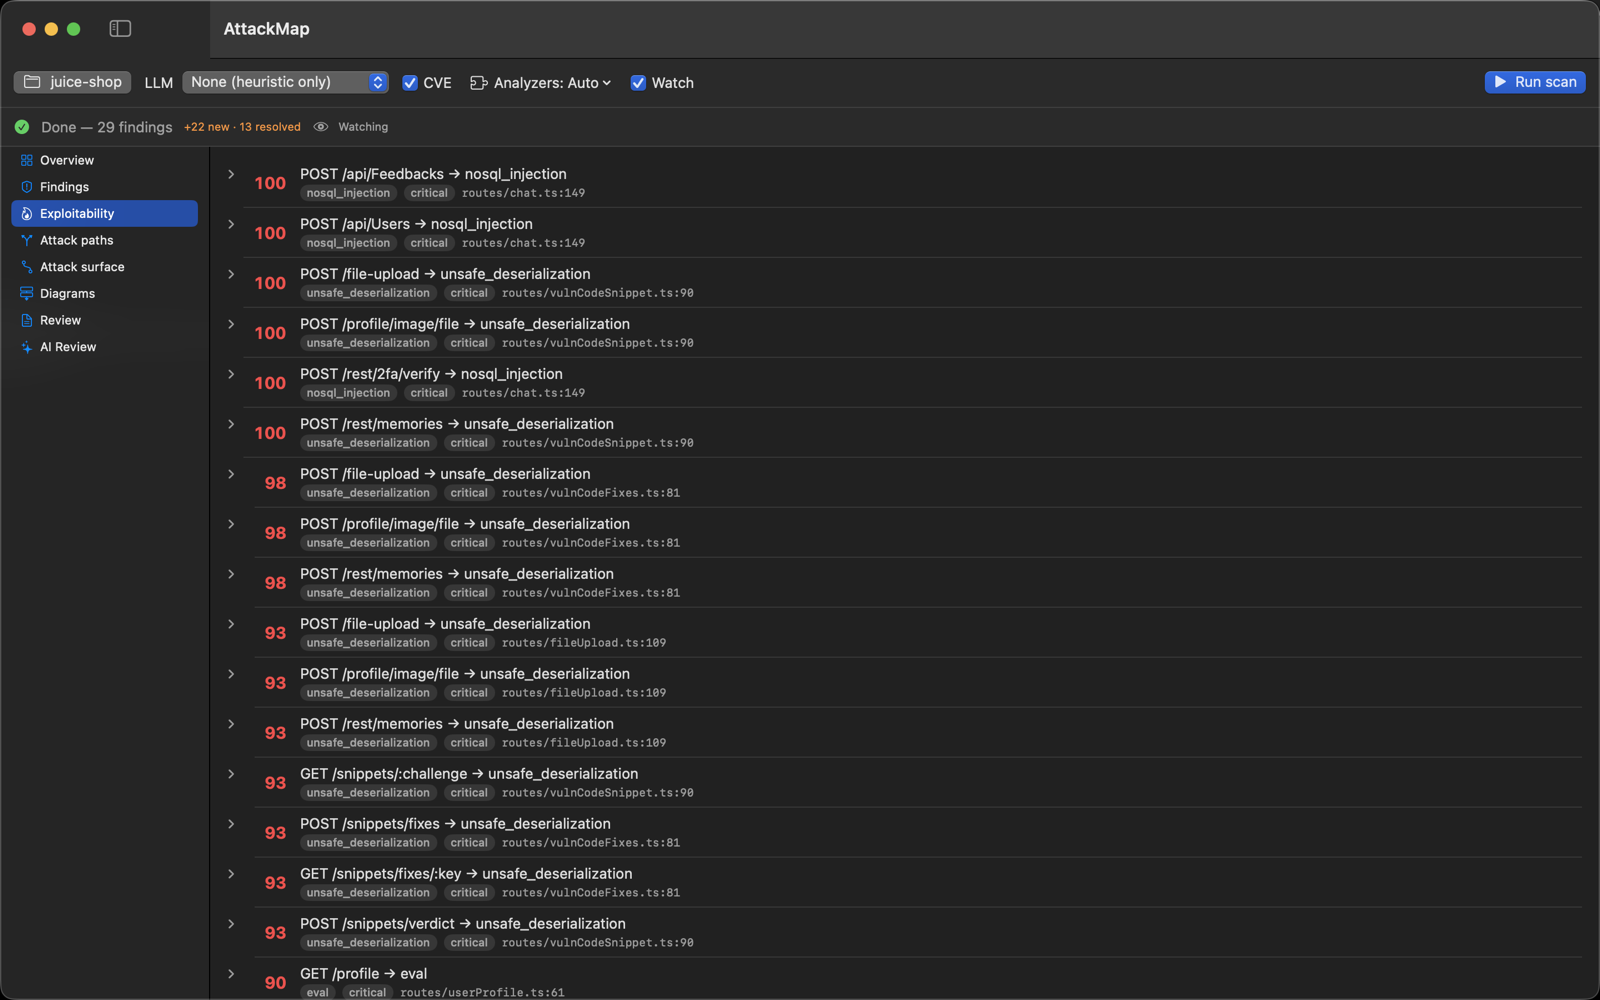](https://docs.mlaify.io/gui/) |
|
|
107
|
+
|
|
108
|
+
*Scanning OWASP Juice Shop. Walkthrough in the [macOS app docs](https://docs.mlaify.io/gui/); source at [mlaify/AttackMap-mac](https://github.com/mlaify/AttackMap-mac).*
|
|
109
|
+
|
|
110
|
+
## Quickstart
|
|
111
|
+
|
|
112
|
+
```bash
|
|
113
|
+
brew install mlaify/tap/attackmap # Homebrew: CLI + all 15 analyzer plugins
|
|
114
|
+
# or, from PyPI: uv tool install "attackmap[all]" (or pipx install "attackmap[all]")
|
|
115
|
+
attackmap analyze /path/to/repo # heuristic review → reports/
|
|
116
|
+
attackmap analyze /path/to/repo --llm # + AI-narrated review (Claude or OpenAI)
|
|
117
|
+
attackmap analyze ./svc-a ./svc-b ./gw # cross-repo / fleet scan
|
|
118
|
+
```
|
|
119
|
+
|
|
120
|
+
Read `reports/defensive-review.md` for the heuristic review, and (with `--llm`)
|
|
121
|
+
`reports/defensive-review-llm.md` for the AI narration. `--llm` resolves auth
|
|
122
|
+
automatically (`ANTHROPIC_API_KEY`, or your Claude/`codex` CLI subscription); add
|
|
123
|
+
`--llm-provider openai` for OpenAI/Codex.
|
|
124
|
+
|
|
125
|
+
Other install paths: `pip install git+https://github.com/mlaify/AttackMap.git` (core
|
|
126
|
+
only), or the `[llm]` extra for AI narration. Not sure
|
|
127
|
+
which analyzer plugins a repo needs? `attackmap suggest ./repo`. Full install and
|
|
128
|
+
CI setup: **[install guide](https://docs.mlaify.io/install/)**.
|
|
129
|
+
|
|
130
|
+
## What it finds
|
|
131
|
+
|
|
132
|
+
- **Attack-surface recon** — routes, data stores, external calls, auth signals,
|
|
133
|
+
secrets, frameworks, entrypoints; every signal carries a `file:line` citation,
|
|
134
|
+
evidence snippet, and confidence.
|
|
135
|
+
- **Data-flow / injection taint** (Python, JS/TS, Go, PHP, Java, C#, Ruby) —
|
|
136
|
+
SQL, shell, eval/code and expression (SpEL/OGNL) injection, JNDI, SSRF, SSTI,
|
|
137
|
+
NoSQL, LDAP, XPath, path traversal and zip-slip, deserialization, open
|
|
138
|
+
redirect, header and regex injection — traced source → variable → sink
|
|
139
|
+
inside each handler, with flow-bound sanitizers, SARIF `codeFlows`, a
|
|
140
|
+
plugin-extensible sink registry (`taint_sinks.yaml`), and a deterministic
|
|
141
|
+
0–100 **exploitability score**.
|
|
142
|
+
- **Novel vuln classes** — prototype pollution, mass assignment, JWT, XXE, ReDoS,
|
|
143
|
+
insecure upload, GraphQL exposure; **BOLA/IDOR** authorization; insecure-crypto
|
|
144
|
+
& web-hardening; anomaly/outlier + signature-free **invariant mining**.
|
|
145
|
+
- **Dependency CVEs** (`--cve`) — SBOM + lockfile resolution against OSV.dev,
|
|
146
|
+
folded into the exploitability score.
|
|
147
|
+
- **Unknown-bug discovery** — `--hunt --verify` (a multi-pass, majority-vote LLM
|
|
148
|
+
jury), verifier-gated `--recall`, and **cross-repo / fleet** analysis:
|
|
149
|
+
confused-deputy flows, trust-assumption gaps, and the sibling service that omits
|
|
150
|
+
a control its peers enforce.
|
|
151
|
+
- **Workflow** — `--triage`, `--remediate`, finding suppression, baseline diff
|
|
152
|
+
gating, SARIF + Mermaid/Graphviz output, and a GitHub **Action + PR bot**.
|
|
153
|
+
|
|
154
|
+
Each run writes Markdown, JSON (`attackmap-report.json`), **SARIF 2.1.0**, and
|
|
155
|
+
diagram artifacts; fleet runs add `fleet-summary.{md,json}` + `fleet-graph.md`.
|
|
156
|
+
See the [outputs reference](https://docs.mlaify.io/scanning/) for the full list.
|
|
157
|
+
|
|
158
|
+
## Supported ecosystems
|
|
159
|
+
|
|
160
|
+
Fourteen analyzer plugins (each installable on its own; `[all]` installs every one):
|
|
161
|
+
**Python**, **JavaScript/TypeScript** (Node services), **Go**, **Java/Kotlin**
|
|
162
|
+
(Spring), **C#** (ASP.NET Core), **Rust**, **PHP** (web / Laminas / Omeka-S),
|
|
163
|
+
**C**, **C++**, **Terraform**, **IaC** (Docker / compose / GitHub Actions),
|
|
164
|
+
**AT Protocol**. Specialty and experimental analyzers are opt-in: when one
|
|
165
|
+
matches a repo, `analyze` says so, and `-m <name>` runs it (`attackmap modules`
|
|
166
|
+
shows which). Details: [analyzers reference](https://docs.mlaify.io/analyzers/).
|
|
167
|
+
Write your own against the documented [analyzer SDK](https://github.com/mlaify/AttackMap/blob/main/docs/external-analyzers.md).
|
|
168
|
+
|
|
169
|
+
## CLI cheat-sheet
|
|
170
|
+
|
|
171
|
+
```bash
|
|
172
|
+
attackmap analyze <path> # review a repo (--output dir, --format all|json|markdown)
|
|
173
|
+
attackmap analyze repoA repoB … # multi-repo fleet scan
|
|
174
|
+
attackmap analyze <path> --cve # dependency CVEs (OSV.dev)
|
|
175
|
+
attackmap analyze <path> --recall # widen taint discovery (extra reach = SPECULATIVE)
|
|
176
|
+
attackmap analyze <path> --llm # AI narrative (--llm-provider claude|openai)
|
|
177
|
+
attackmap analyze <path> --hunt --verify # LLM exploit-hypothesis hunt, adjudicated vs. source
|
|
178
|
+
attackmap analyze <path> --triage # cluster/dedupe/rank existing findings
|
|
179
|
+
attackmap analyze <path> --remediate # review-first fix suggestions
|
|
180
|
+
attackmap analyze <path> --baseline prev.json --fail-on-new-high # PR gate
|
|
181
|
+
attackmap suggest ./repo # recommend analyzer plugins · attackmap modules # list installed
|
|
182
|
+
```
|
|
183
|
+
|
|
184
|
+
Verify-jury knobs (`--verify-votes` / `--hunt-lenses` / `--hunt-rounds` /
|
|
185
|
+
`--hunt-budget`) and suppression (`--no-suppress` / `--suppress-file`) are
|
|
186
|
+
documented in the [CLI reference](https://docs.mlaify.io/cli/).
|
|
187
|
+
|
|
188
|
+
## What AttackMap is *not*
|
|
189
|
+
|
|
190
|
+
- **Not a runtime detector.** It's static; its detection hints are leads for your
|
|
191
|
+
SIEM team, not deployable rules.
|
|
192
|
+
- **Not a replacement for dedicated SCA.** `--cve` folds CVE signal into an
|
|
193
|
+
architecture-aware narrative; Trivy/Grype/Dependabot go deeper on resolution.
|
|
194
|
+
- **Not a sound taint engine.** Taint follows local assignments *within* one
|
|
195
|
+
function (intra-procedural def-use) and a call-graph-refined import walk
|
|
196
|
+
*across* files; it does not follow a value into a helper it is passed to, and
|
|
197
|
+
branches are not distinguished. Precision over recall; findings are evidence,
|
|
198
|
+
not proof. See the limits in `src/attackmap/taint_flow.py`.
|
|
199
|
+
- **Not exhaustive.** Heuristic by design, with explicit confidence tiers and
|
|
200
|
+
guardrails for stale signals.
|
|
201
|
+
|
|
202
|
+
## Documentation & links
|
|
203
|
+
|
|
204
|
+
- **[docs.mlaify.io](https://docs.mlaify.io)** — user guide, install, CLI,
|
|
205
|
+
analyzers, SDK
|
|
206
|
+
- **[Wiki](https://github.com/mlaify/AttackMap/wiki)** — architecture, roadmap,
|
|
207
|
+
contributor references
|
|
208
|
+
- **[Roadmap / Bug Triage / Kanban](https://github.com/orgs/mlaify/projects)** —
|
|
209
|
+
project boards · [Road to 1.0](https://github.com/mlaify/AttackMap/issues/209)
|
|
210
|
+
- [`CHANGELOG.md`](https://github.com/mlaify/AttackMap/blob/main/CHANGELOG.md) · [`CONTRIBUTING.md`](https://github.com/mlaify/AttackMap/blob/main/CONTRIBUTING.md) ·
|
|
211
|
+
[`SECURITY.md`](https://github.com/mlaify/AttackMap/blob/main/SECURITY.md) · [`VISION.md`](https://github.com/mlaify/AttackMap/blob/main/VISION.md)
|
|
212
|
+
|
|
213
|
+
## Special thanks
|
|
214
|
+
|
|
215
|
+
AttackMap is built by its contributors.
|
|
216
|
+
|
|
217
|
+
<a href="https://github.com/mlaify/AttackMap/graphs/contributors"><img src="https://contrib.rocks/image?repo=mlaify/AttackMap" alt="AttackMap contributors" /></a>
|
|
218
|
+
|
|
219
|
+
## Contributing
|
|
220
|
+
|
|
221
|
+
Issues and PRs welcome — see [CONTRIBUTING.md](https://github.com/mlaify/AttackMap/blob/main/CONTRIBUTING.md). By contributing
|
|
222
|
+
you agree your contributions will be MIT-licensed.
|
|
223
|
+
|
|
224
|
+
## License
|
|
225
|
+
|
|
226
|
+
[MIT](https://github.com/mlaify/AttackMap/blob/main/LICENSE). Copyright (c) 2026 Matthew Davis and AttackMap Contributors.
|
|
@@ -0,0 +1,161 @@
|
|
|
1
|
+
# AttackMap
|
|
2
|
+
|
|
3
|
+
> [!IMPORTANT]
|
|
4
|
+
> **Active development, slow pace.** AttackMap is under active development, but
|
|
5
|
+
> progress may be slow until more contributors or co-maintainers join. Help is
|
|
6
|
+
> very welcome with the core engine, an analyzer, the macOS app, or the docs —
|
|
7
|
+
> see [CONTRIBUTING.md](https://github.com/mlaify/AttackMap/blob/main/CONTRIBUTING.md) or open an issue on
|
|
8
|
+
> [mlaify/AttackMap](https://github.com/mlaify/AttackMap/issues) to say hello.
|
|
9
|
+
> Security reports are still welcome at [security@mlaify.io](mailto:security@mlaify.io).
|
|
10
|
+
|
|
11
|
+
**Local-first, AI-assisted defensive security analysis for codebases.** AttackMap
|
|
12
|
+
reads a repository (or a whole fleet of them), reconstructs the attack surface —
|
|
13
|
+
routes, data stores, external calls, auth signals, trust boundaries — traces
|
|
14
|
+
request-to-sink data flow, and produces an evidence-grounded, prioritized security
|
|
15
|
+
review. It finds the cross-cutting weaknesses single-file scanners miss, and never
|
|
16
|
+
sends your code anywhere.
|
|
17
|
+
|
|
18
|
+
[](https://github.com/mlaify/AttackMap/blob/main/LICENSE)
|
|
19
|
+
[](https://www.python.org/)
|
|
20
|
+
|
|
21
|
+
> **Status: beta (v0.6.4).** Core engine + 15 analyzer plugins, published on
|
|
22
|
+
> [PyPI](https://pypi.org/project/attackmap/) and validated on real codebases. AttackMap is heuristic by
|
|
23
|
+
> design — findings are confidence-tiered evidence, not proof. Roadmap to 1.0:
|
|
24
|
+
> [issue #209](https://github.com/mlaify/AttackMap/issues/209).
|
|
25
|
+
|
|
26
|
+
Full documentation: **[docs.mlaify.io](https://docs.mlaify.io)** ·
|
|
27
|
+
architecture & internals: **[wiki](https://github.com/mlaify/AttackMap/wiki)**.
|
|
28
|
+
|
|
29
|
+
### The macOS app
|
|
30
|
+
|
|
31
|
+
Prefer a GUI? A native macOS front-end drives this CLI and renders every result
|
|
32
|
+
view. Install it with Homebrew (this also installs the CLI), or build it from
|
|
33
|
+
source at [mlaify/AttackMap-mac](https://github.com/mlaify/AttackMap-mac):
|
|
34
|
+
|
|
35
|
+
```bash
|
|
36
|
+
brew install --cask mlaify/tap/attackmap-app
|
|
37
|
+
```
|
|
38
|
+
|
|
39
|
+
| Overview | Exploitability |
|
|
40
|
+
|---|---|
|
|
41
|
+
| [](https://docs.mlaify.io/gui/) | [](https://docs.mlaify.io/gui/) |
|
|
42
|
+
|
|
43
|
+
*Scanning OWASP Juice Shop. Walkthrough in the [macOS app docs](https://docs.mlaify.io/gui/); source at [mlaify/AttackMap-mac](https://github.com/mlaify/AttackMap-mac).*
|
|
44
|
+
|
|
45
|
+
## Quickstart
|
|
46
|
+
|
|
47
|
+
```bash
|
|
48
|
+
brew install mlaify/tap/attackmap # Homebrew: CLI + all 15 analyzer plugins
|
|
49
|
+
# or, from PyPI: uv tool install "attackmap[all]" (or pipx install "attackmap[all]")
|
|
50
|
+
attackmap analyze /path/to/repo # heuristic review → reports/
|
|
51
|
+
attackmap analyze /path/to/repo --llm # + AI-narrated review (Claude or OpenAI)
|
|
52
|
+
attackmap analyze ./svc-a ./svc-b ./gw # cross-repo / fleet scan
|
|
53
|
+
```
|
|
54
|
+
|
|
55
|
+
Read `reports/defensive-review.md` for the heuristic review, and (with `--llm`)
|
|
56
|
+
`reports/defensive-review-llm.md` for the AI narration. `--llm` resolves auth
|
|
57
|
+
automatically (`ANTHROPIC_API_KEY`, or your Claude/`codex` CLI subscription); add
|
|
58
|
+
`--llm-provider openai` for OpenAI/Codex.
|
|
59
|
+
|
|
60
|
+
Other install paths: `pip install git+https://github.com/mlaify/AttackMap.git` (core
|
|
61
|
+
only), or the `[llm]` extra for AI narration. Not sure
|
|
62
|
+
which analyzer plugins a repo needs? `attackmap suggest ./repo`. Full install and
|
|
63
|
+
CI setup: **[install guide](https://docs.mlaify.io/install/)**.
|
|
64
|
+
|
|
65
|
+
## What it finds
|
|
66
|
+
|
|
67
|
+
- **Attack-surface recon** — routes, data stores, external calls, auth signals,
|
|
68
|
+
secrets, frameworks, entrypoints; every signal carries a `file:line` citation,
|
|
69
|
+
evidence snippet, and confidence.
|
|
70
|
+
- **Data-flow / injection taint** (Python, JS/TS, Go, PHP, Java, C#, Ruby) —
|
|
71
|
+
SQL, shell, eval/code and expression (SpEL/OGNL) injection, JNDI, SSRF, SSTI,
|
|
72
|
+
NoSQL, LDAP, XPath, path traversal and zip-slip, deserialization, open
|
|
73
|
+
redirect, header and regex injection — traced source → variable → sink
|
|
74
|
+
inside each handler, with flow-bound sanitizers, SARIF `codeFlows`, a
|
|
75
|
+
plugin-extensible sink registry (`taint_sinks.yaml`), and a deterministic
|
|
76
|
+
0–100 **exploitability score**.
|
|
77
|
+
- **Novel vuln classes** — prototype pollution, mass assignment, JWT, XXE, ReDoS,
|
|
78
|
+
insecure upload, GraphQL exposure; **BOLA/IDOR** authorization; insecure-crypto
|
|
79
|
+
& web-hardening; anomaly/outlier + signature-free **invariant mining**.
|
|
80
|
+
- **Dependency CVEs** (`--cve`) — SBOM + lockfile resolution against OSV.dev,
|
|
81
|
+
folded into the exploitability score.
|
|
82
|
+
- **Unknown-bug discovery** — `--hunt --verify` (a multi-pass, majority-vote LLM
|
|
83
|
+
jury), verifier-gated `--recall`, and **cross-repo / fleet** analysis:
|
|
84
|
+
confused-deputy flows, trust-assumption gaps, and the sibling service that omits
|
|
85
|
+
a control its peers enforce.
|
|
86
|
+
- **Workflow** — `--triage`, `--remediate`, finding suppression, baseline diff
|
|
87
|
+
gating, SARIF + Mermaid/Graphviz output, and a GitHub **Action + PR bot**.
|
|
88
|
+
|
|
89
|
+
Each run writes Markdown, JSON (`attackmap-report.json`), **SARIF 2.1.0**, and
|
|
90
|
+
diagram artifacts; fleet runs add `fleet-summary.{md,json}` + `fleet-graph.md`.
|
|
91
|
+
See the [outputs reference](https://docs.mlaify.io/scanning/) for the full list.
|
|
92
|
+
|
|
93
|
+
## Supported ecosystems
|
|
94
|
+
|
|
95
|
+
Fourteen analyzer plugins (each installable on its own; `[all]` installs every one):
|
|
96
|
+
**Python**, **JavaScript/TypeScript** (Node services), **Go**, **Java/Kotlin**
|
|
97
|
+
(Spring), **C#** (ASP.NET Core), **Rust**, **PHP** (web / Laminas / Omeka-S),
|
|
98
|
+
**C**, **C++**, **Terraform**, **IaC** (Docker / compose / GitHub Actions),
|
|
99
|
+
**AT Protocol**. Specialty and experimental analyzers are opt-in: when one
|
|
100
|
+
matches a repo, `analyze` says so, and `-m <name>` runs it (`attackmap modules`
|
|
101
|
+
shows which). Details: [analyzers reference](https://docs.mlaify.io/analyzers/).
|
|
102
|
+
Write your own against the documented [analyzer SDK](https://github.com/mlaify/AttackMap/blob/main/docs/external-analyzers.md).
|
|
103
|
+
|
|
104
|
+
## CLI cheat-sheet
|
|
105
|
+
|
|
106
|
+
```bash
|
|
107
|
+
attackmap analyze <path> # review a repo (--output dir, --format all|json|markdown)
|
|
108
|
+
attackmap analyze repoA repoB … # multi-repo fleet scan
|
|
109
|
+
attackmap analyze <path> --cve # dependency CVEs (OSV.dev)
|
|
110
|
+
attackmap analyze <path> --recall # widen taint discovery (extra reach = SPECULATIVE)
|
|
111
|
+
attackmap analyze <path> --llm # AI narrative (--llm-provider claude|openai)
|
|
112
|
+
attackmap analyze <path> --hunt --verify # LLM exploit-hypothesis hunt, adjudicated vs. source
|
|
113
|
+
attackmap analyze <path> --triage # cluster/dedupe/rank existing findings
|
|
114
|
+
attackmap analyze <path> --remediate # review-first fix suggestions
|
|
115
|
+
attackmap analyze <path> --baseline prev.json --fail-on-new-high # PR gate
|
|
116
|
+
attackmap suggest ./repo # recommend analyzer plugins · attackmap modules # list installed
|
|
117
|
+
```
|
|
118
|
+
|
|
119
|
+
Verify-jury knobs (`--verify-votes` / `--hunt-lenses` / `--hunt-rounds` /
|
|
120
|
+
`--hunt-budget`) and suppression (`--no-suppress` / `--suppress-file`) are
|
|
121
|
+
documented in the [CLI reference](https://docs.mlaify.io/cli/).
|
|
122
|
+
|
|
123
|
+
## What AttackMap is *not*
|
|
124
|
+
|
|
125
|
+
- **Not a runtime detector.** It's static; its detection hints are leads for your
|
|
126
|
+
SIEM team, not deployable rules.
|
|
127
|
+
- **Not a replacement for dedicated SCA.** `--cve` folds CVE signal into an
|
|
128
|
+
architecture-aware narrative; Trivy/Grype/Dependabot go deeper on resolution.
|
|
129
|
+
- **Not a sound taint engine.** Taint follows local assignments *within* one
|
|
130
|
+
function (intra-procedural def-use) and a call-graph-refined import walk
|
|
131
|
+
*across* files; it does not follow a value into a helper it is passed to, and
|
|
132
|
+
branches are not distinguished. Precision over recall; findings are evidence,
|
|
133
|
+
not proof. See the limits in `src/attackmap/taint_flow.py`.
|
|
134
|
+
- **Not exhaustive.** Heuristic by design, with explicit confidence tiers and
|
|
135
|
+
guardrails for stale signals.
|
|
136
|
+
|
|
137
|
+
## Documentation & links
|
|
138
|
+
|
|
139
|
+
- **[docs.mlaify.io](https://docs.mlaify.io)** — user guide, install, CLI,
|
|
140
|
+
analyzers, SDK
|
|
141
|
+
- **[Wiki](https://github.com/mlaify/AttackMap/wiki)** — architecture, roadmap,
|
|
142
|
+
contributor references
|
|
143
|
+
- **[Roadmap / Bug Triage / Kanban](https://github.com/orgs/mlaify/projects)** —
|
|
144
|
+
project boards · [Road to 1.0](https://github.com/mlaify/AttackMap/issues/209)
|
|
145
|
+
- [`CHANGELOG.md`](https://github.com/mlaify/AttackMap/blob/main/CHANGELOG.md) · [`CONTRIBUTING.md`](https://github.com/mlaify/AttackMap/blob/main/CONTRIBUTING.md) ·
|
|
146
|
+
[`SECURITY.md`](https://github.com/mlaify/AttackMap/blob/main/SECURITY.md) · [`VISION.md`](https://github.com/mlaify/AttackMap/blob/main/VISION.md)
|
|
147
|
+
|
|
148
|
+
## Special thanks
|
|
149
|
+
|
|
150
|
+
AttackMap is built by its contributors.
|
|
151
|
+
|
|
152
|
+
<a href="https://github.com/mlaify/AttackMap/graphs/contributors"><img src="https://contrib.rocks/image?repo=mlaify/AttackMap" alt="AttackMap contributors" /></a>
|
|
153
|
+
|
|
154
|
+
## Contributing
|
|
155
|
+
|
|
156
|
+
Issues and PRs welcome — see [CONTRIBUTING.md](https://github.com/mlaify/AttackMap/blob/main/CONTRIBUTING.md). By contributing
|
|
157
|
+
you agree your contributions will be MIT-licensed.
|
|
158
|
+
|
|
159
|
+
## License
|
|
160
|
+
|
|
161
|
+
[MIT](https://github.com/mlaify/AttackMap/blob/main/LICENSE). Copyright (c) 2026 Matthew Davis and AttackMap Contributors.
|
|
@@ -0,0 +1,122 @@
|
|
|
1
|
+
[build-system]
|
|
2
|
+
requires = ["setuptools>=68", "wheel"]
|
|
3
|
+
build-backend = "setuptools.build_meta"
|
|
4
|
+
|
|
5
|
+
[project]
|
|
6
|
+
name = "attackmap"
|
|
7
|
+
# Single-sourced from src/attackmap/__init__.py (see [tool.setuptools.dynamic]).
|
|
8
|
+
dynamic = ["version"]
|
|
9
|
+
description = "AI-assisted defensive security analyzer for codebases — scans a repository, models assets and controls, finds cross-cutting weaknesses, and generates an evidence-grounded review with MITRE ATT&CK mappings and detection-engineering hints."
|
|
10
|
+
readme = "README.md"
|
|
11
|
+
requires-python = ">=3.11"
|
|
12
|
+
license = {text = "MIT"}
|
|
13
|
+
authors = [
|
|
14
|
+
{name = "Matthew Davis", email = "mlaify@mlaify.io"},
|
|
15
|
+
{name = "AttackMap Contributors"},
|
|
16
|
+
]
|
|
17
|
+
maintainers = [
|
|
18
|
+
{name = "Matthew Davis", email = "mlaify@mlaify.io"},
|
|
19
|
+
]
|
|
20
|
+
keywords = [
|
|
21
|
+
"security",
|
|
22
|
+
"static-analysis",
|
|
23
|
+
"appsec",
|
|
24
|
+
"defensive-security",
|
|
25
|
+
"threat-modeling",
|
|
26
|
+
"attack-surface",
|
|
27
|
+
"mitre-attack",
|
|
28
|
+
"detection-engineering",
|
|
29
|
+
"code-review",
|
|
30
|
+
"llm",
|
|
31
|
+
"claude",
|
|
32
|
+
]
|
|
33
|
+
classifiers = [
|
|
34
|
+
"Development Status :: 4 - Beta",
|
|
35
|
+
"Environment :: Console",
|
|
36
|
+
"Intended Audience :: Developers",
|
|
37
|
+
"Intended Audience :: Information Technology",
|
|
38
|
+
"Intended Audience :: System Administrators",
|
|
39
|
+
"License :: OSI Approved :: MIT License",
|
|
40
|
+
"Operating System :: OS Independent",
|
|
41
|
+
"Programming Language :: Python :: 3",
|
|
42
|
+
"Programming Language :: Python :: 3.11",
|
|
43
|
+
"Programming Language :: Python :: 3.12",
|
|
44
|
+
"Programming Language :: Python :: 3.13",
|
|
45
|
+
"Programming Language :: Python :: 3 :: Only",
|
|
46
|
+
"Topic :: Security",
|
|
47
|
+
"Topic :: Software Development :: Quality Assurance",
|
|
48
|
+
"Topic :: Software Development :: Testing",
|
|
49
|
+
"Typing :: Typed",
|
|
50
|
+
]
|
|
51
|
+
dependencies = [
|
|
52
|
+
"typer>=0.12.3",
|
|
53
|
+
"pydantic>=2.7.0",
|
|
54
|
+
"networkx>=3.3",
|
|
55
|
+
"PyYAML>=6.0",
|
|
56
|
+
]
|
|
57
|
+
|
|
58
|
+
[project.optional-dependencies]
|
|
59
|
+
llm = [
|
|
60
|
+
"anthropic>=0.40.0",
|
|
61
|
+
"openai>=1.60.0",
|
|
62
|
+
]
|
|
63
|
+
all = [
|
|
64
|
+
"attackmap[llm]",
|
|
65
|
+
"attackmap-analyzer-python==0.2.0",
|
|
66
|
+
"attackmap-analyzer-rust==0.2.0",
|
|
67
|
+
"attackmap-analyzer-go==0.2.0",
|
|
68
|
+
"attackmap-analyzer-java-spring==0.2.0",
|
|
69
|
+
"attackmap-analyzer-dotnet==0.2.0",
|
|
70
|
+
"attackmap-analyzer-terraform==0.2.1",
|
|
71
|
+
"attackmap-analyzer-c==0.2.0",
|
|
72
|
+
"attackmap-analyzer-cpp==0.2.0",
|
|
73
|
+
"attackmap-analyzer-swift==0.2.0",
|
|
74
|
+
"attackmap-analyzer-node-service==0.3.0",
|
|
75
|
+
"attackmap-analyzer-atproto==0.2.0",
|
|
76
|
+
"attackmap-analyzer-php-web==0.2.0",
|
|
77
|
+
"attackmap-analyzer-php-laminas==0.2.0",
|
|
78
|
+
"attackmap-analyzer-omeka-s==0.2.0",
|
|
79
|
+
"attackmap-analyzer-iac==0.2.0",
|
|
80
|
+
]
|
|
81
|
+
dev = [
|
|
82
|
+
"pytest>=8.0.0",
|
|
83
|
+
"build>=1.2.0",
|
|
84
|
+
"jsonschema>=4.0",
|
|
85
|
+
# Validates the generated Sigma rules in tests (#251); not a runtime dependency.
|
|
86
|
+
"pysigma>=2.0",
|
|
87
|
+
"ruff>=0.6",
|
|
88
|
+
]
|
|
89
|
+
|
|
90
|
+
[project.urls]
|
|
91
|
+
Homepage = "https://github.com/mlaify/AttackMap"
|
|
92
|
+
Documentation = "https://github.com/mlaify/AttackMap/wiki"
|
|
93
|
+
Repository = "https://github.com/mlaify/AttackMap"
|
|
94
|
+
Issues = "https://github.com/mlaify/AttackMap/issues"
|
|
95
|
+
Changelog = "https://github.com/mlaify/AttackMap/blob/main/CHANGELOG.md"
|
|
96
|
+
|
|
97
|
+
[project.scripts]
|
|
98
|
+
attackmap = "attackmap.cli:app"
|
|
99
|
+
|
|
100
|
+
[tool.setuptools]
|
|
101
|
+
package-dir = {"" = "src"}
|
|
102
|
+
|
|
103
|
+
[tool.setuptools.packages.find]
|
|
104
|
+
where = ["src"]
|
|
105
|
+
|
|
106
|
+
[tool.setuptools.package-data]
|
|
107
|
+
# Declarative taint sink registry (#240).
|
|
108
|
+
attackmap = ["taint_sinks.yaml"]
|
|
109
|
+
# Sigma rule templates for detection opportunities (#251).
|
|
110
|
+
"attackmap.detections" = ["*.yml"]
|
|
111
|
+
|
|
112
|
+
[tool.setuptools.dynamic]
|
|
113
|
+
version = {attr = "attackmap.__version__"}
|
|
114
|
+
|
|
115
|
+
[tool.pytest.ini_options]
|
|
116
|
+
pythonpath = ["src"]
|
|
117
|
+
testpaths = ["tests"]
|
|
118
|
+
|
|
119
|
+
[tool.ruff.lint]
|
|
120
|
+
# Pyflakes only (#231): undefined names, unused imports/locals. Style rules
|
|
121
|
+
# are out of scope; CI runs this on src/attackmap.
|
|
122
|
+
select = ["F"]
|